
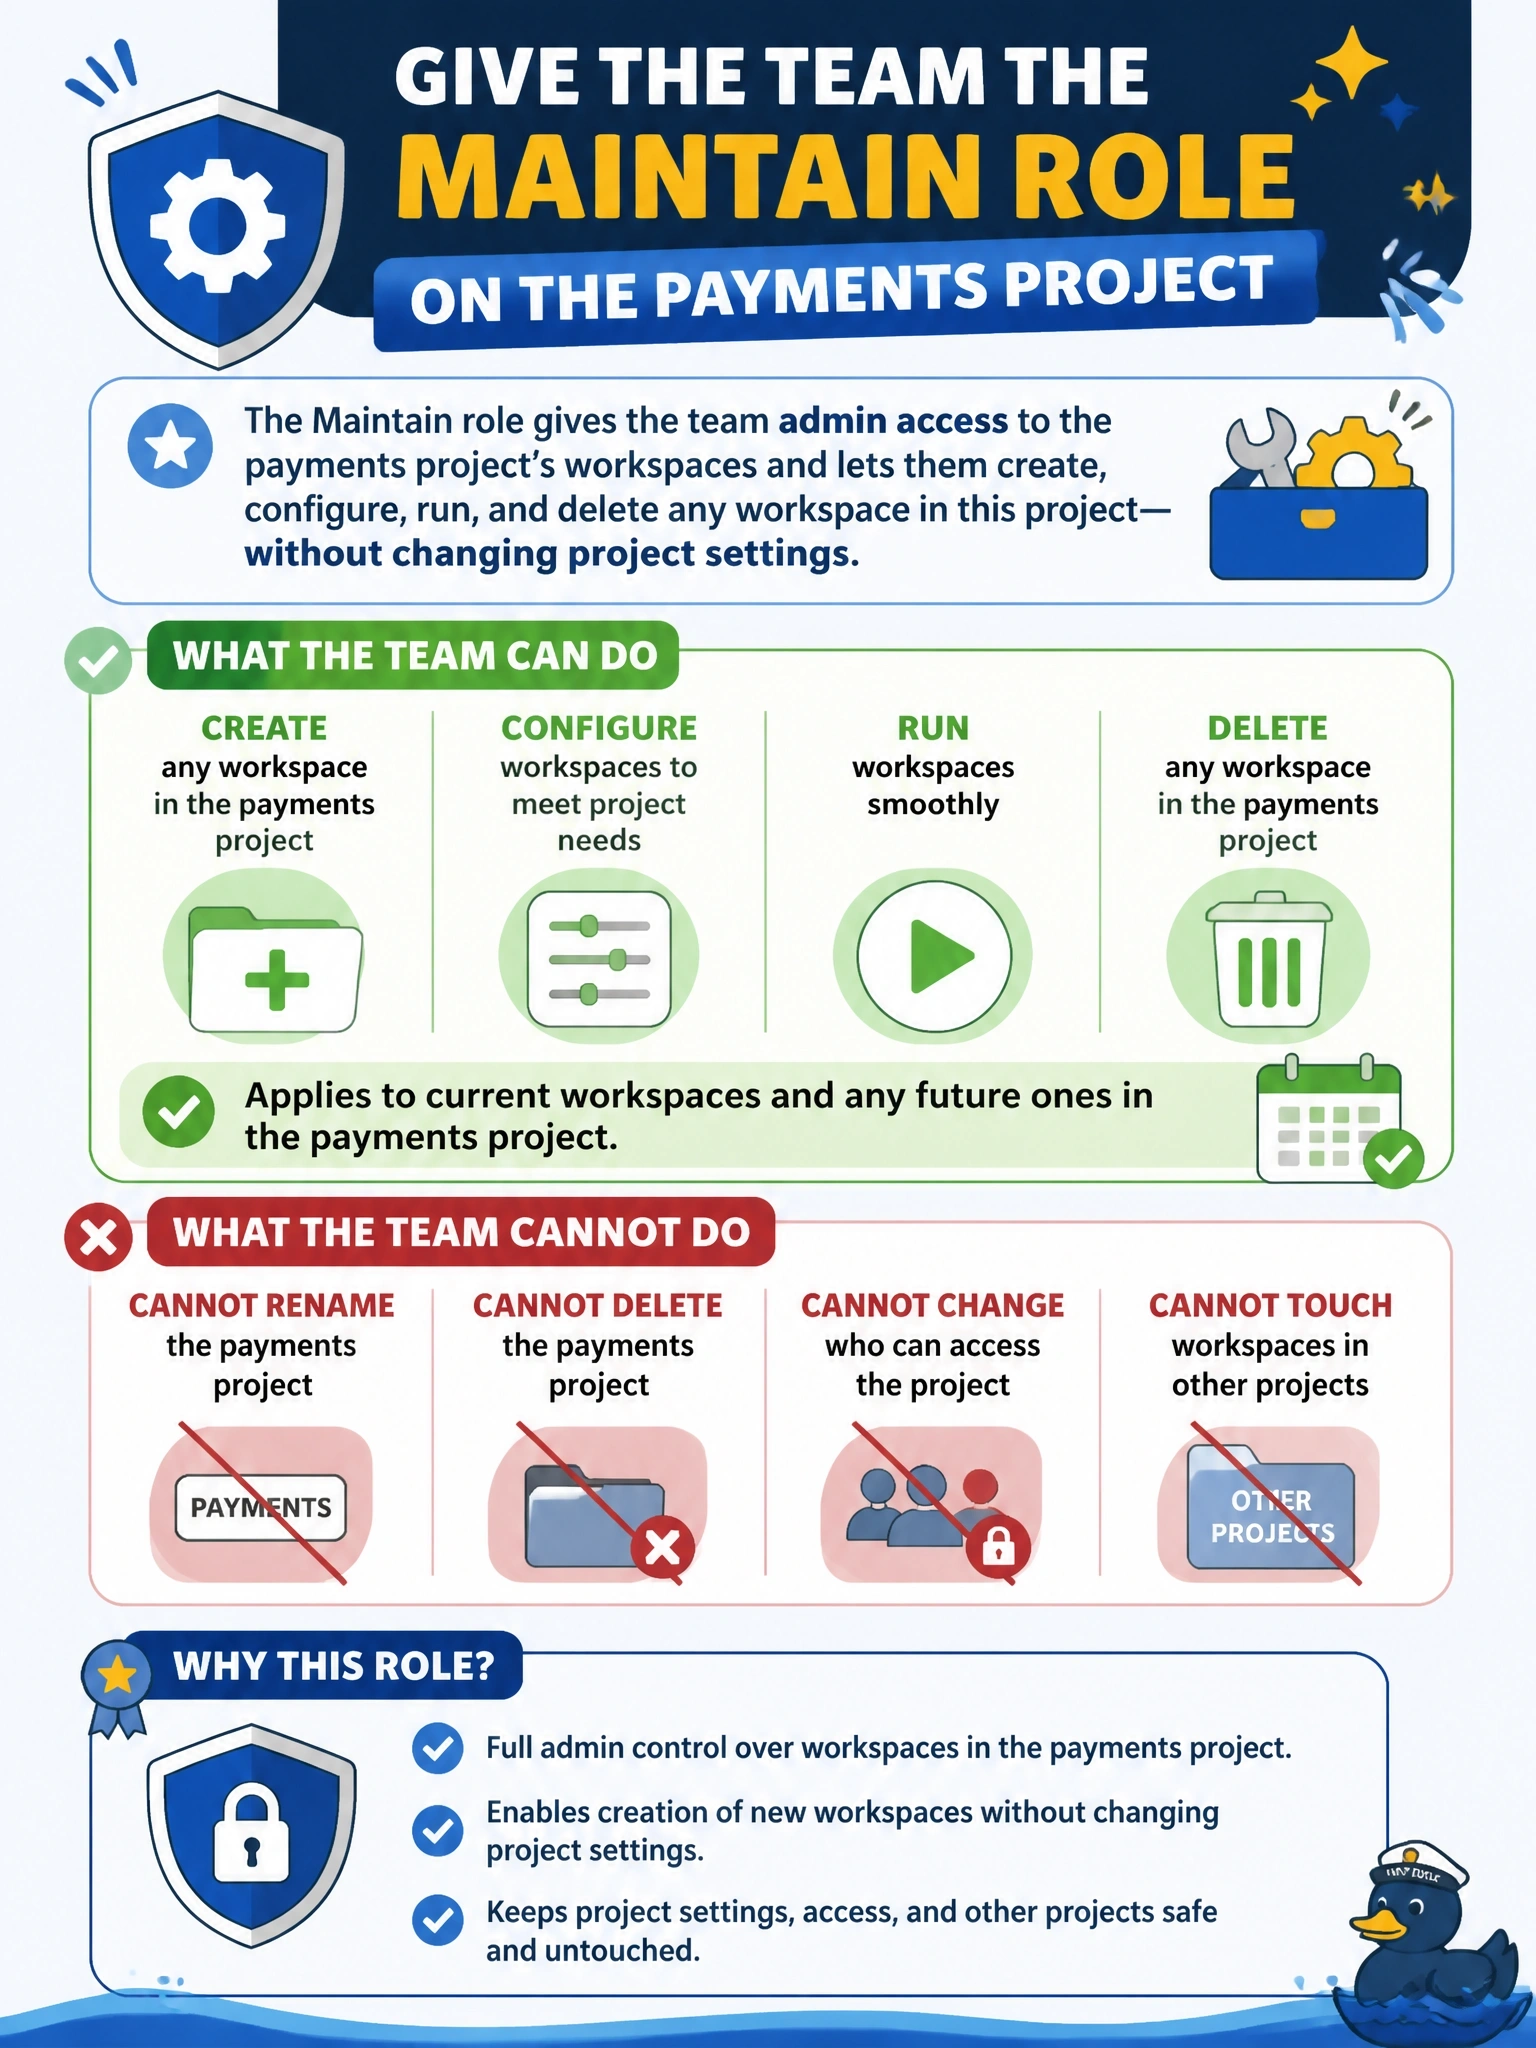
The payments team must be able to create, configure, run and delete any workspace in the payments project, including future ones. It must not rename or delete the project, change which teams can access it, or touch workspaces in other projects. Which permission should the team receive?
Select an answer to reveal the explanation.
Short Explanation
You're handing out keys to one floor of the building, not the master key. Project Maintain lets the team run the whole floor's workspaces, including new ones, without letting them repaint the sign on the door or change who else gets in.
Full Explanation
Project roles in HCP Terraform build on one another: Read, Write, Maintain and Admin. Maintain grants admin access to every workspace in the project and the ability to create and delete workspaces there, which covers current and future workspaces, while leaving project settings untouched. The Admin role adds updating project settings, deleting the project, moving workspaces, and managing team permissions on the project, so it grants exactly the abilities the stem says the team must not have. Write allows reading workspaces and initiating, cancelling and applying runs, and reading and writing variables and state, but it does not allow creating or deleting workspaces, so it fails the stated requirement. Manage all workspaces is an organization permission: it gives admin access to every workspace in the organization and the ability to create workspaces anywhere, which breaks the requirement to stay out of other projects. Because project roles apply to all workspaces in the project, there is no need to grant per-workspace access as workspaces are added. Exam caveat: when a team needs only part of this access, a custom project role can combine individual permissions from the same table. Operational check: as a payments team member, create and delete a test workspace in the project, then confirm the project settings and Team Access pages are not editable.