
A newly formed cloud governance team must enforce the CIS AWS Foundations benchmark in HCP Terraform within weeks and has no Sentinel authors on staff. What is the most direct way to obtain enforceable policies?
Select an answer to reveal the explanation.
Short Explanation
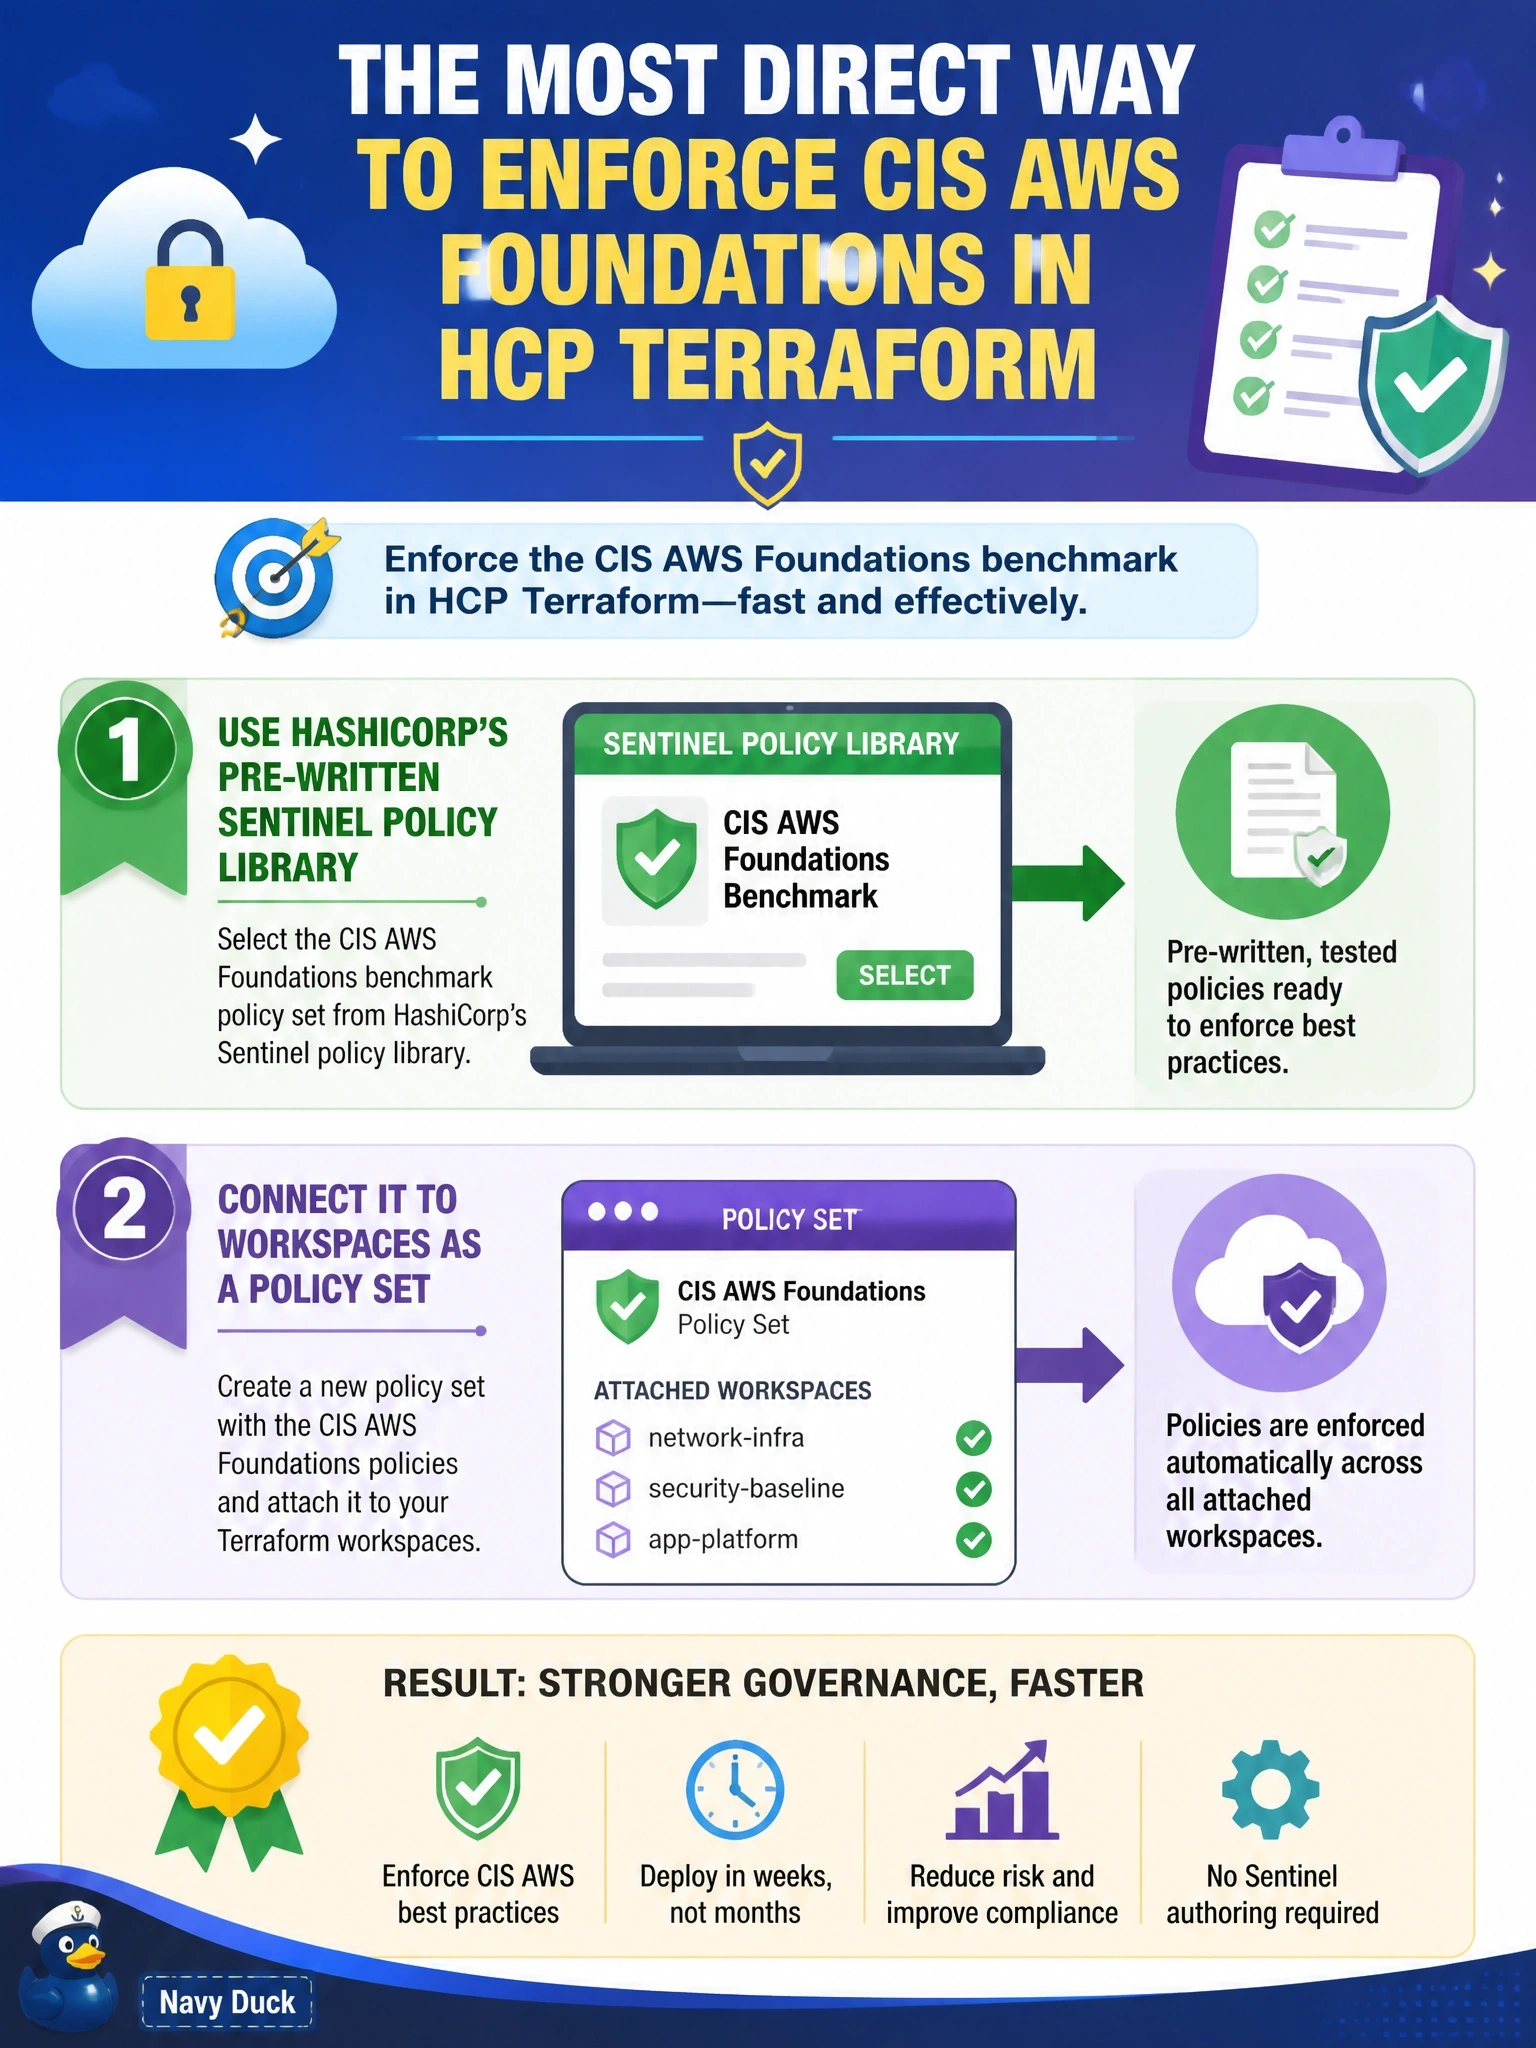
Why would you write a hundred rules from scratch when HashiCorp has already written and tested them? Grab the pre-written CIS library, fork it, and connect it as a policy set. Watch out for check blocks; they warn, they don't block.
Full Explanation
HashiCorp publishes pre-written Sentinel policy libraries for several AWS standards, including CIS AWS Foundations benchmark versions, AWS Foundational Security Best Practices, ISO/IEC 27001 Annex A, PCI DSS and NIST SP 800-53. The documented workflow is to download the policies or fork the HashiCorp repository, then connect them to HCP Terraform or Terraform Enterprise as a policy set, which requires owner-team membership or the Manage Policies permission. The team gets enforceable, maintained policies without writing Sentinel and can still tune enforcement levels and scope. Health assessments detect drift and run continuous validation of checks and conditions; they do not score resources against compliance benchmarks. Check blocks report warnings and never block an apply, so they cannot enforce a benchmark. Cost estimation reports projected monthly cost changes for supported resources; it says nothing about security controls. Exam caveat: pre-written policies are a starting point; review each control's enforcement level before making it mandatory, because some controls may conflict with approved existing designs. Operational check: connect the forked library as a policy set scoped to a pilot project at advisory, review which runs fail which controls, then raise enforcement and widen scope in stages.