
A child module builds a database connection string from a sensitive password variable and exposes it as output conn_string with sensitive = true. The root module declares output "db_conn" { value = module.db.conn_string }, and terraform plan fails with an error saying the output refers to sensitive values. What is the correct fix?
Select an answer to reveal the explanation.
Short Explanation
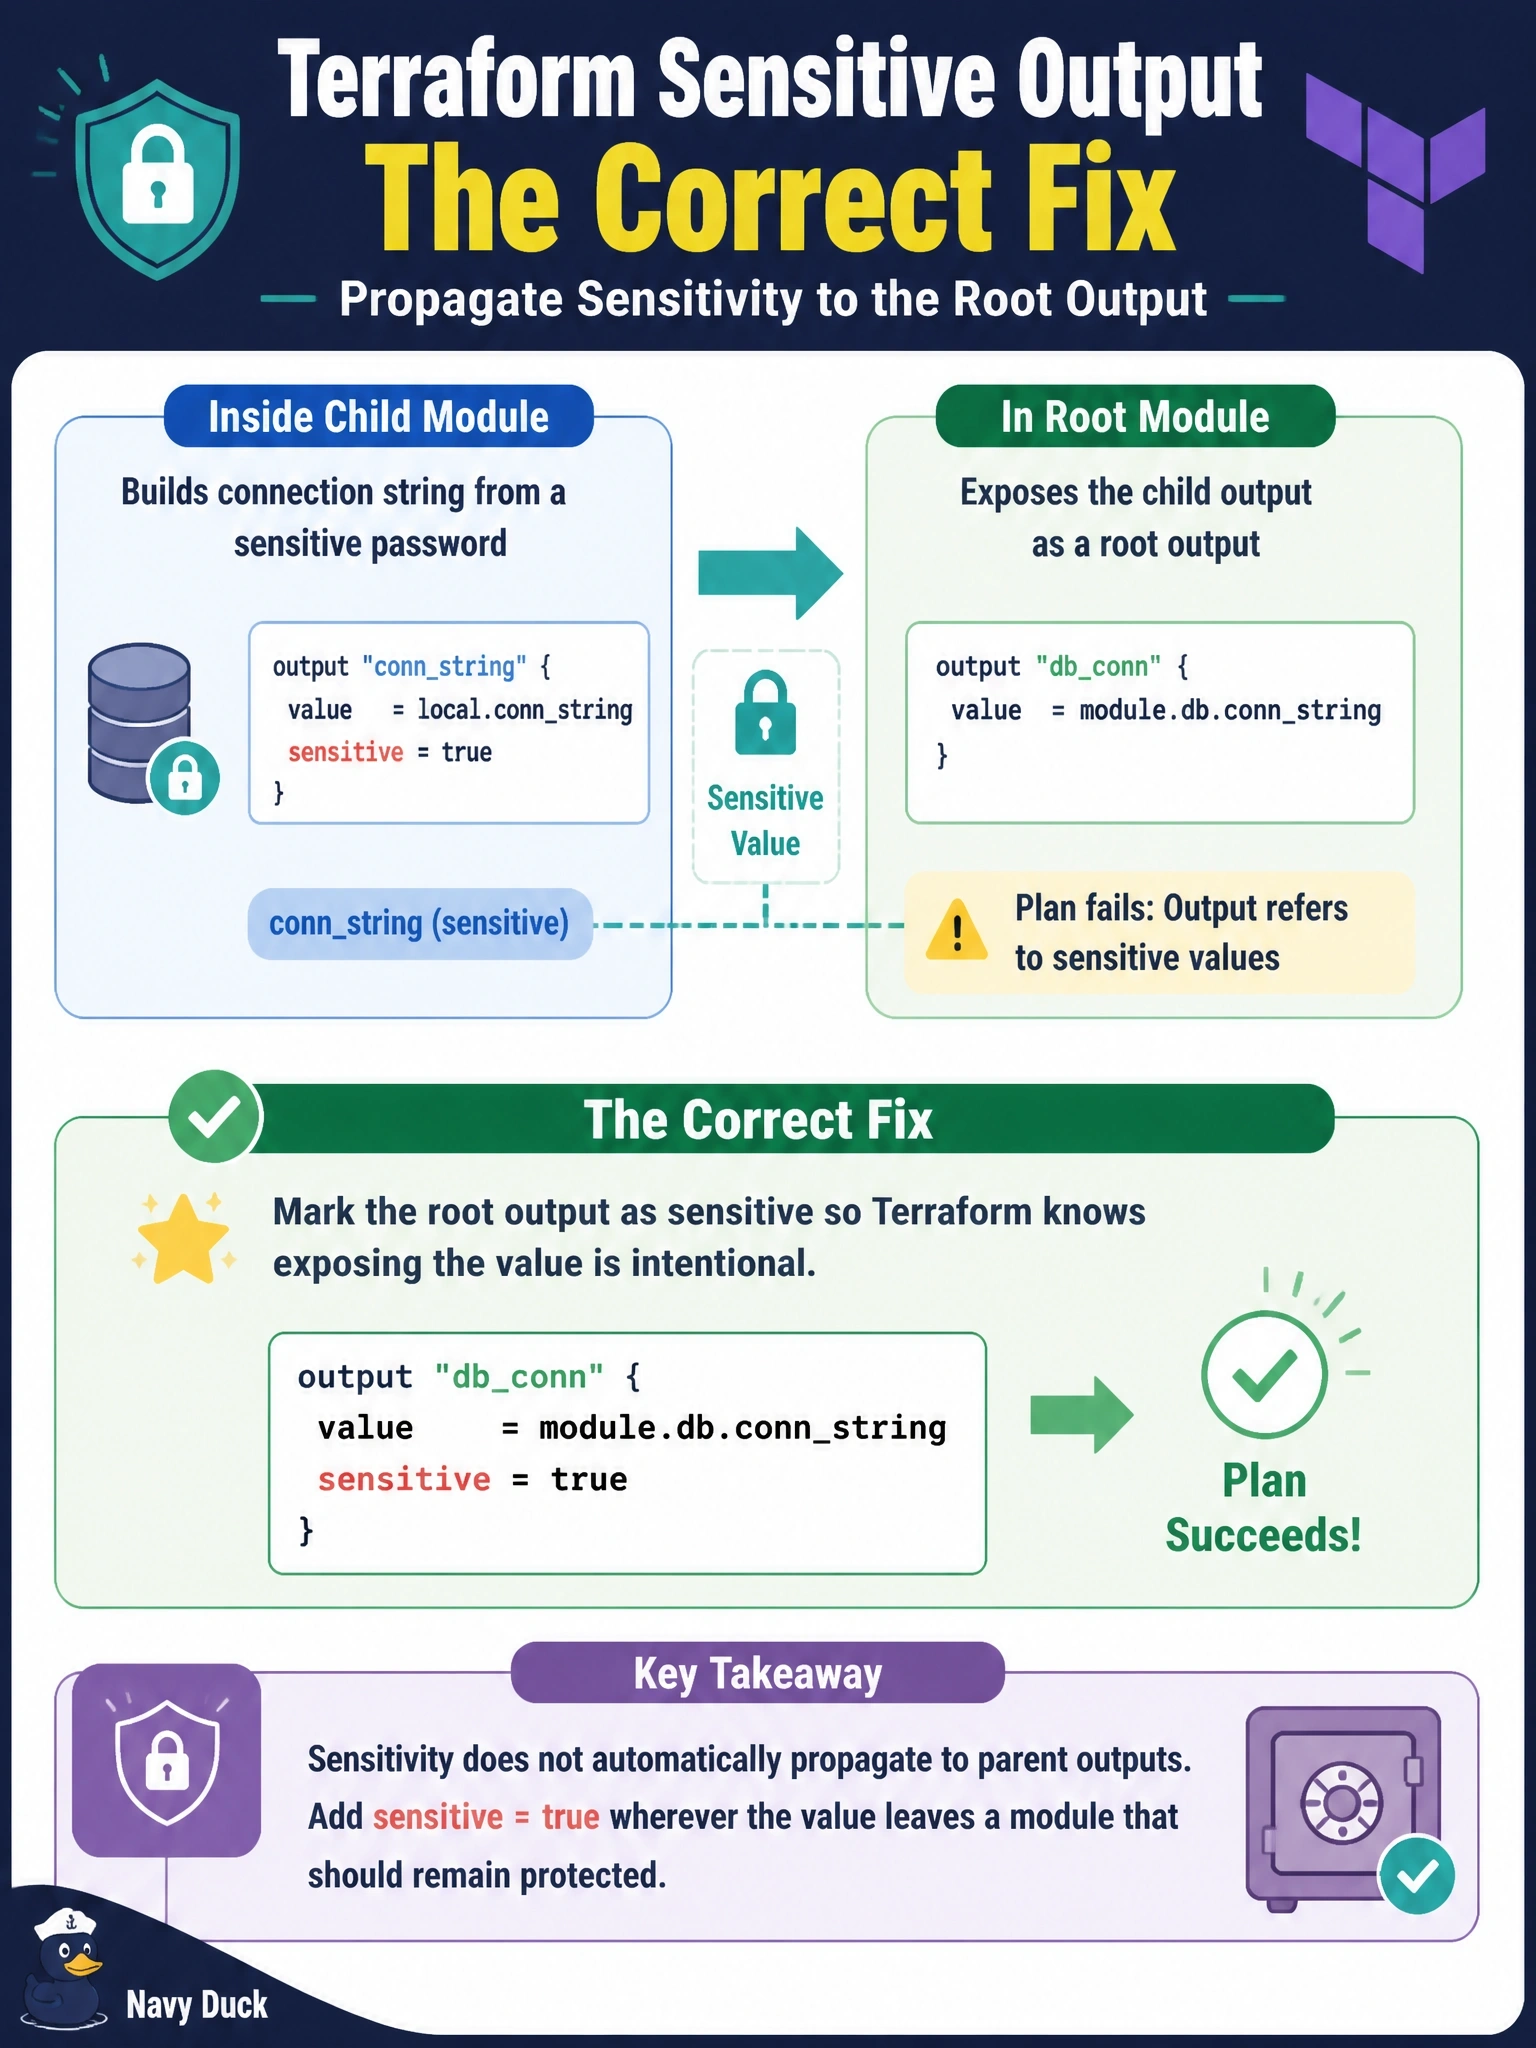
Terraform is double-checking you here: a secret is about to walk out the front door, so it wants the root output to carry the sensitive tag too. Add sensitive = true and the value stays redacted in plan output. Stripping the flag or reaching for nonsensitive() just turns the warning into a leak.
Full Explanation
Terraform propagates sensitivity through expressions. Any value derived from a sensitive variable or sensitive module output is itself sensitive, and a root output that references such a value without declaring sensitive = true causes an error, so that an author never exposes a secret by accident. Adding sensitive = true to the root output acknowledges the exposure and keeps the value redacted in plan and apply output and in the HCP Terraform UI. Wrapping the reference in nonsensitive() removes the marking and prints the connection string, including the password, which the function's documentation warns against unless the derived value is truly free of sensitive content. Removing sensitive from the child output does not fix anything, because the password is still sensitive and the derived string remains marked; it also weakens the module contract. The ephemeral argument on outputs is permitted only in child modules; a root module output cannot be ephemeral, and the value would not reach state for consumers anyway. Exam caveat: sensitive outputs are still written to state, and terraform output -json or -raw prints them in plain text. Operational check: run terraform plan and confirm db_conn shows as sensitive, then review who can read the state that holds it.