
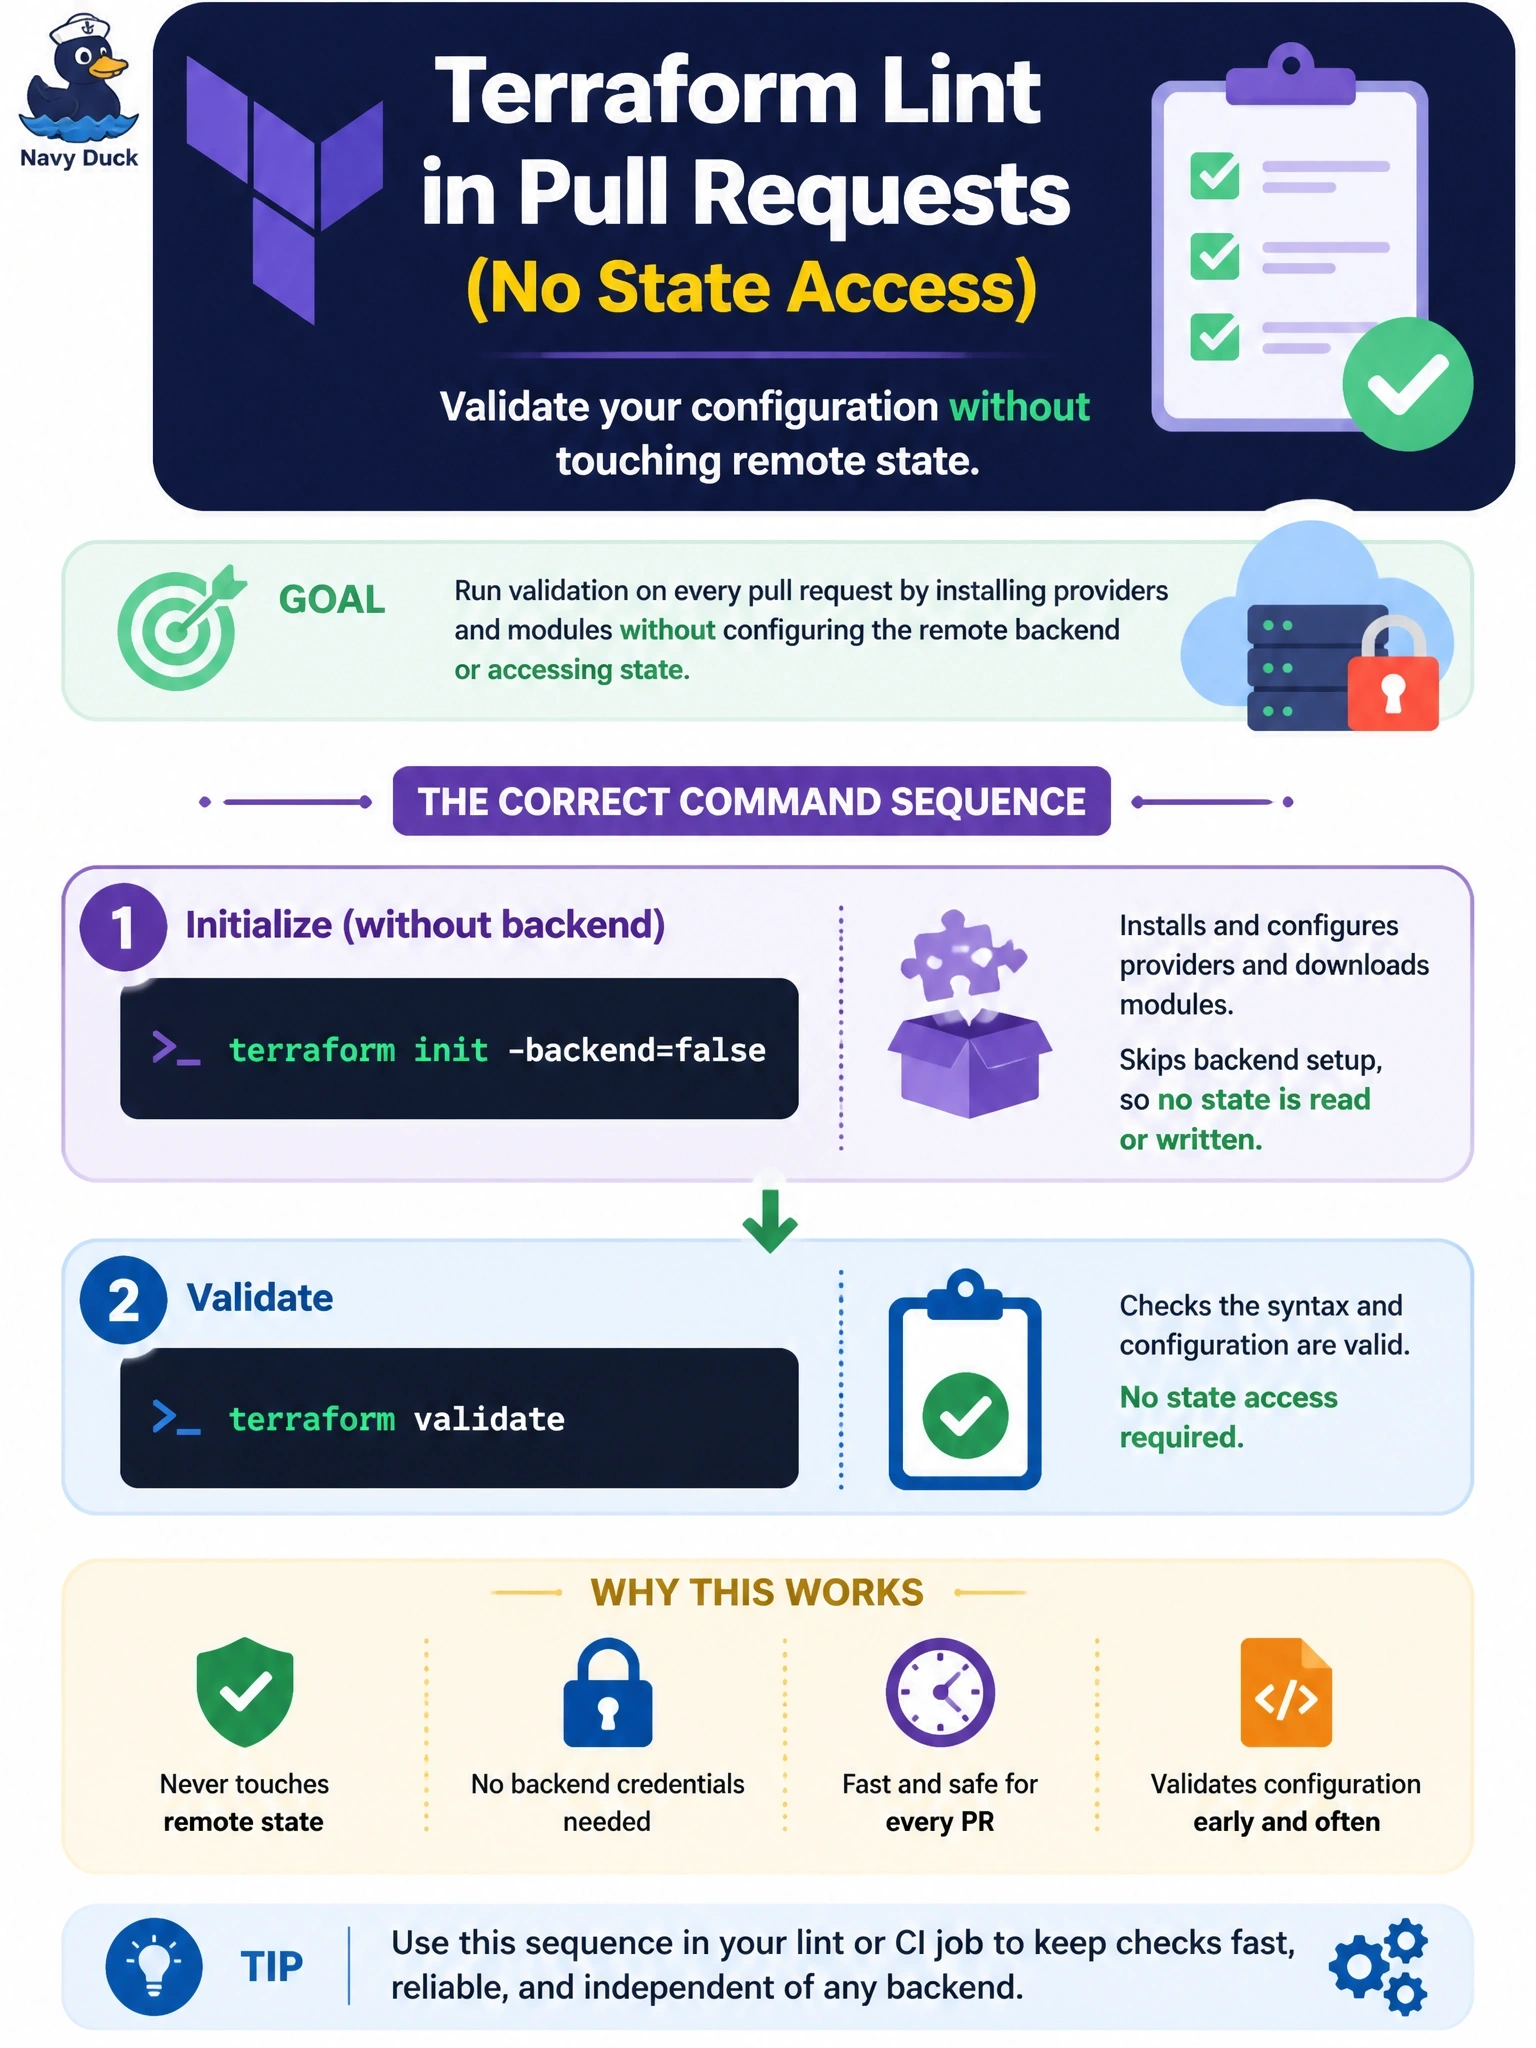
A lint job must run terraform validate on every pull request. The configuration uses a remote backend, but the lint runner has no credentials for that backend and should never touch state. Which command sequence works?
Select an answer to reveal the explanation.
Short Explanation
Validate needs your providers and modules on hand, but it doesn't need the state vault. So you install the toolbox and skip the vault: init with -backend=false, then validate. Plan's no good here because plan always reads state.
Full Explanation
terraform validate checks a configuration's syntax, references and types against provider schemas, which requires providers and modules to be installed in the working directory, so some form of init must run first. terraform init -backend=false performs those installation steps but skips backend configuration, so no backend credentials are needed and state is never read or written. Validate then runs entirely locally. Skipping init leaves providers and modules missing, and validate fails as soon as it needs their schemas. -reconfigure discards any previously saved backend settings but still configures the backend from the configuration, which requires access and credentials. Plan always reads state to compare it with configuration; -lock=false only skips locking, not backend access, and a plan job is not a lint job. Exam caveat: in Terraform 1.15, terraform validate also checks the backend block itself, confirming that the backend type exists and required attributes are present, without connecting to the backend. Operational check: run the lint job on a runner with no cloud or backend credentials and confirm it completes and reports a deliberately introduced reference error.