
During an incident, an engineer needs every attribute Terraform has recorded for one for_each instance, aws_instance.web["api"], including its provider-assigned ID, printed in human-readable form. Which command should they run?
Select an answer to reveal the explanation.
Short Explanation
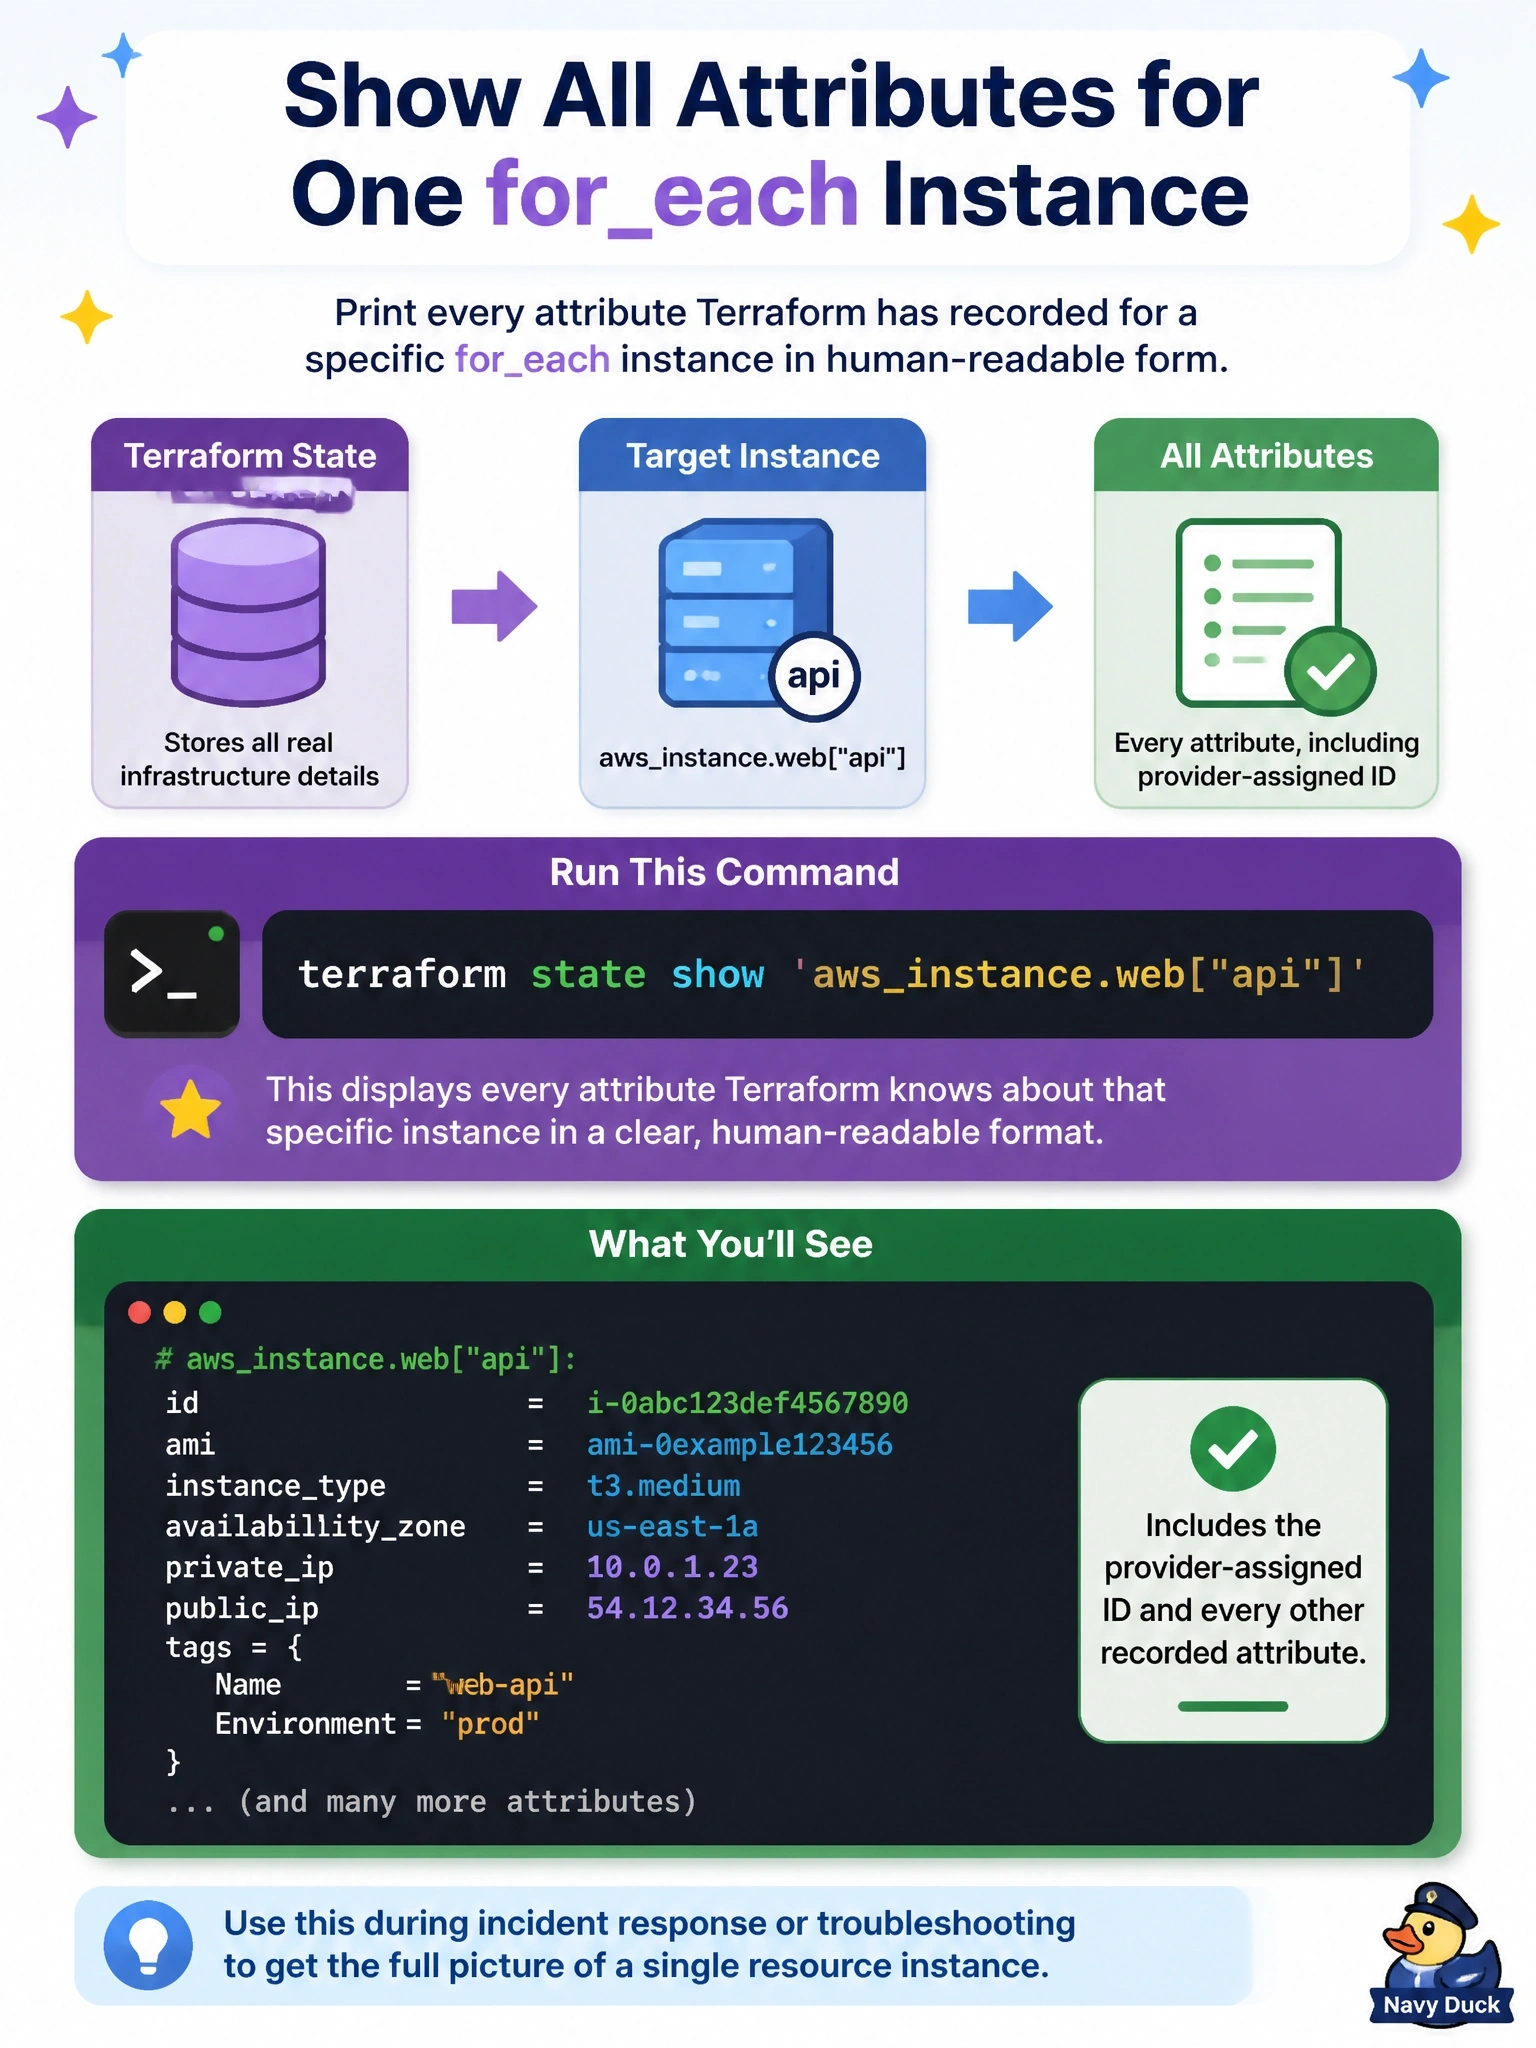
When you need the full file on one suspect, you ask for it by name. terraform state show with the quoted address prints everything Terraform recorded about that single instance, ID included. The trap is state list -id, which works the other way round: give it an ID, it hands you an address.
Full Explanation
The terraform state show command prints the attributes of a single resource instance from state, given its address in resource addressing format. For a for_each instance the address includes the key, so it must be quoted to protect the brackets and inner quotes from the shell. The output includes every recorded attribute, such as the provider-assigned id, network addresses and tags, which is what an engineer usually needs during an incident. The state list command's -id option filters the list to the resource whose remote ID matches the given value; it expects an ID rather than an address and returns an address, so it answers the reverse question. The terraform output command prints root module output values by output name and cannot look up resources by address. The terraform state pull command downloads the entire raw state and writes it to standard output; it takes no address argument, so it cannot narrow the output to one instance and produces machine-oriented JSON rather than the readable view required. Exam caveat: sensitive attributes are redacted in this view but remain in state, so access to state is still access to secrets. Operational check: run terraform state list to copy the exact address, then pass it quoted to terraform state show and confirm the id matches what the cloud console shows.