
A team wants to enable auto-merge for a dependency-update agent's PRs to reduce review overhead. They are debating the right conditions. Which set of auto-merge conditions provides the MOST appropriate balance of automation and safety?
Select an answer to reveal the explanation.
Short Explanation
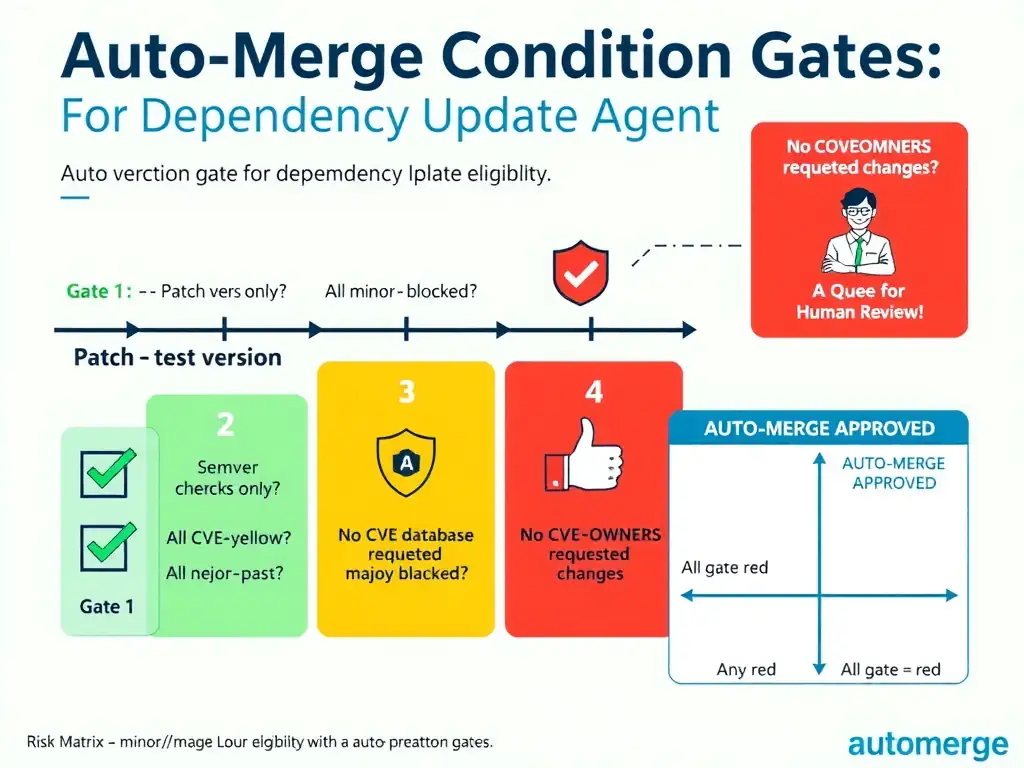
Auto-merge conditions are your fire suppression system — they should activate only when you're confident the situation is safe, not just when nobody said 'stop.' Use them only for patch updates with passing CI, no known CVEs, and no CODEOWNERS change requests. CI alone doesn't catch CVEs, and 'no objections in 48 hours' is just hope wearing the clothes of a policy.
Full Explanation
Auto-merge conditions for agent PRs must be tuned to the specific risk profile of the operation. Dependency updates have three distinct risk categories: patch (low — bug fixes only per semver), minor (medium — new features, possible deprecations), and major (high — breaking changes expected).
The approach that auto-merges when CI passes regardless of patch, minor, or major severity is insufficient because CI tests validate that existing functionality works but do not detect all breakage from API changes, performance regressions, or new security vulnerabilities introduced in the updated package. One package could update its minor or major version in a way that passes tests but introduces subtle incompatibilities.
The patch-plus-CI-plus-CVE-plus-CODEOWNERS approach is correct because it stacks four complementary conditions: patch-only restricts auto-merge to the lowest-risk update category where semver guarantees no breaking changes; CI pass ensures existing functionality is not broken; CVE check ensures the new version doesn't introduce known security vulnerabilities — a package could fix a bug while simultaneously introducing a new dependency with a CVE; and no CODEOWNERS requested changes respects human expert override — if a domain expert has flagged an issue, the auto-merge should not proceed.
The agent-confidence-score approach is circular: the agent is both proposing the change and scoring its own confidence, creating a self-approval dynamic. Confidence scores from LLMs are also unreliable measures of actual code safety. This is a soft guardrail, not a hard one.
The 48-hour no-objection window approach is a weak policy. It assumes humans are actively monitoring PR queues, which is unreliable. Silence is not consent. This condition allows unsafe PRs to auto-merge whenever the team is busy, on vacation, or simply hasn't noticed the PR.