
A Copilot agent helps HR staff draft performance review templates by retrieving historical review examples from a database. The database contains real employee reviews with names, performance ratings, and compensation data. The agent retrieves these as context and occasionally surfaces employee names and salaries in its responses to other users. Which data handling practice should be implemented to address this GDPR and privacy concern?
Select an answer to reveal the explanation.
Short Explanation
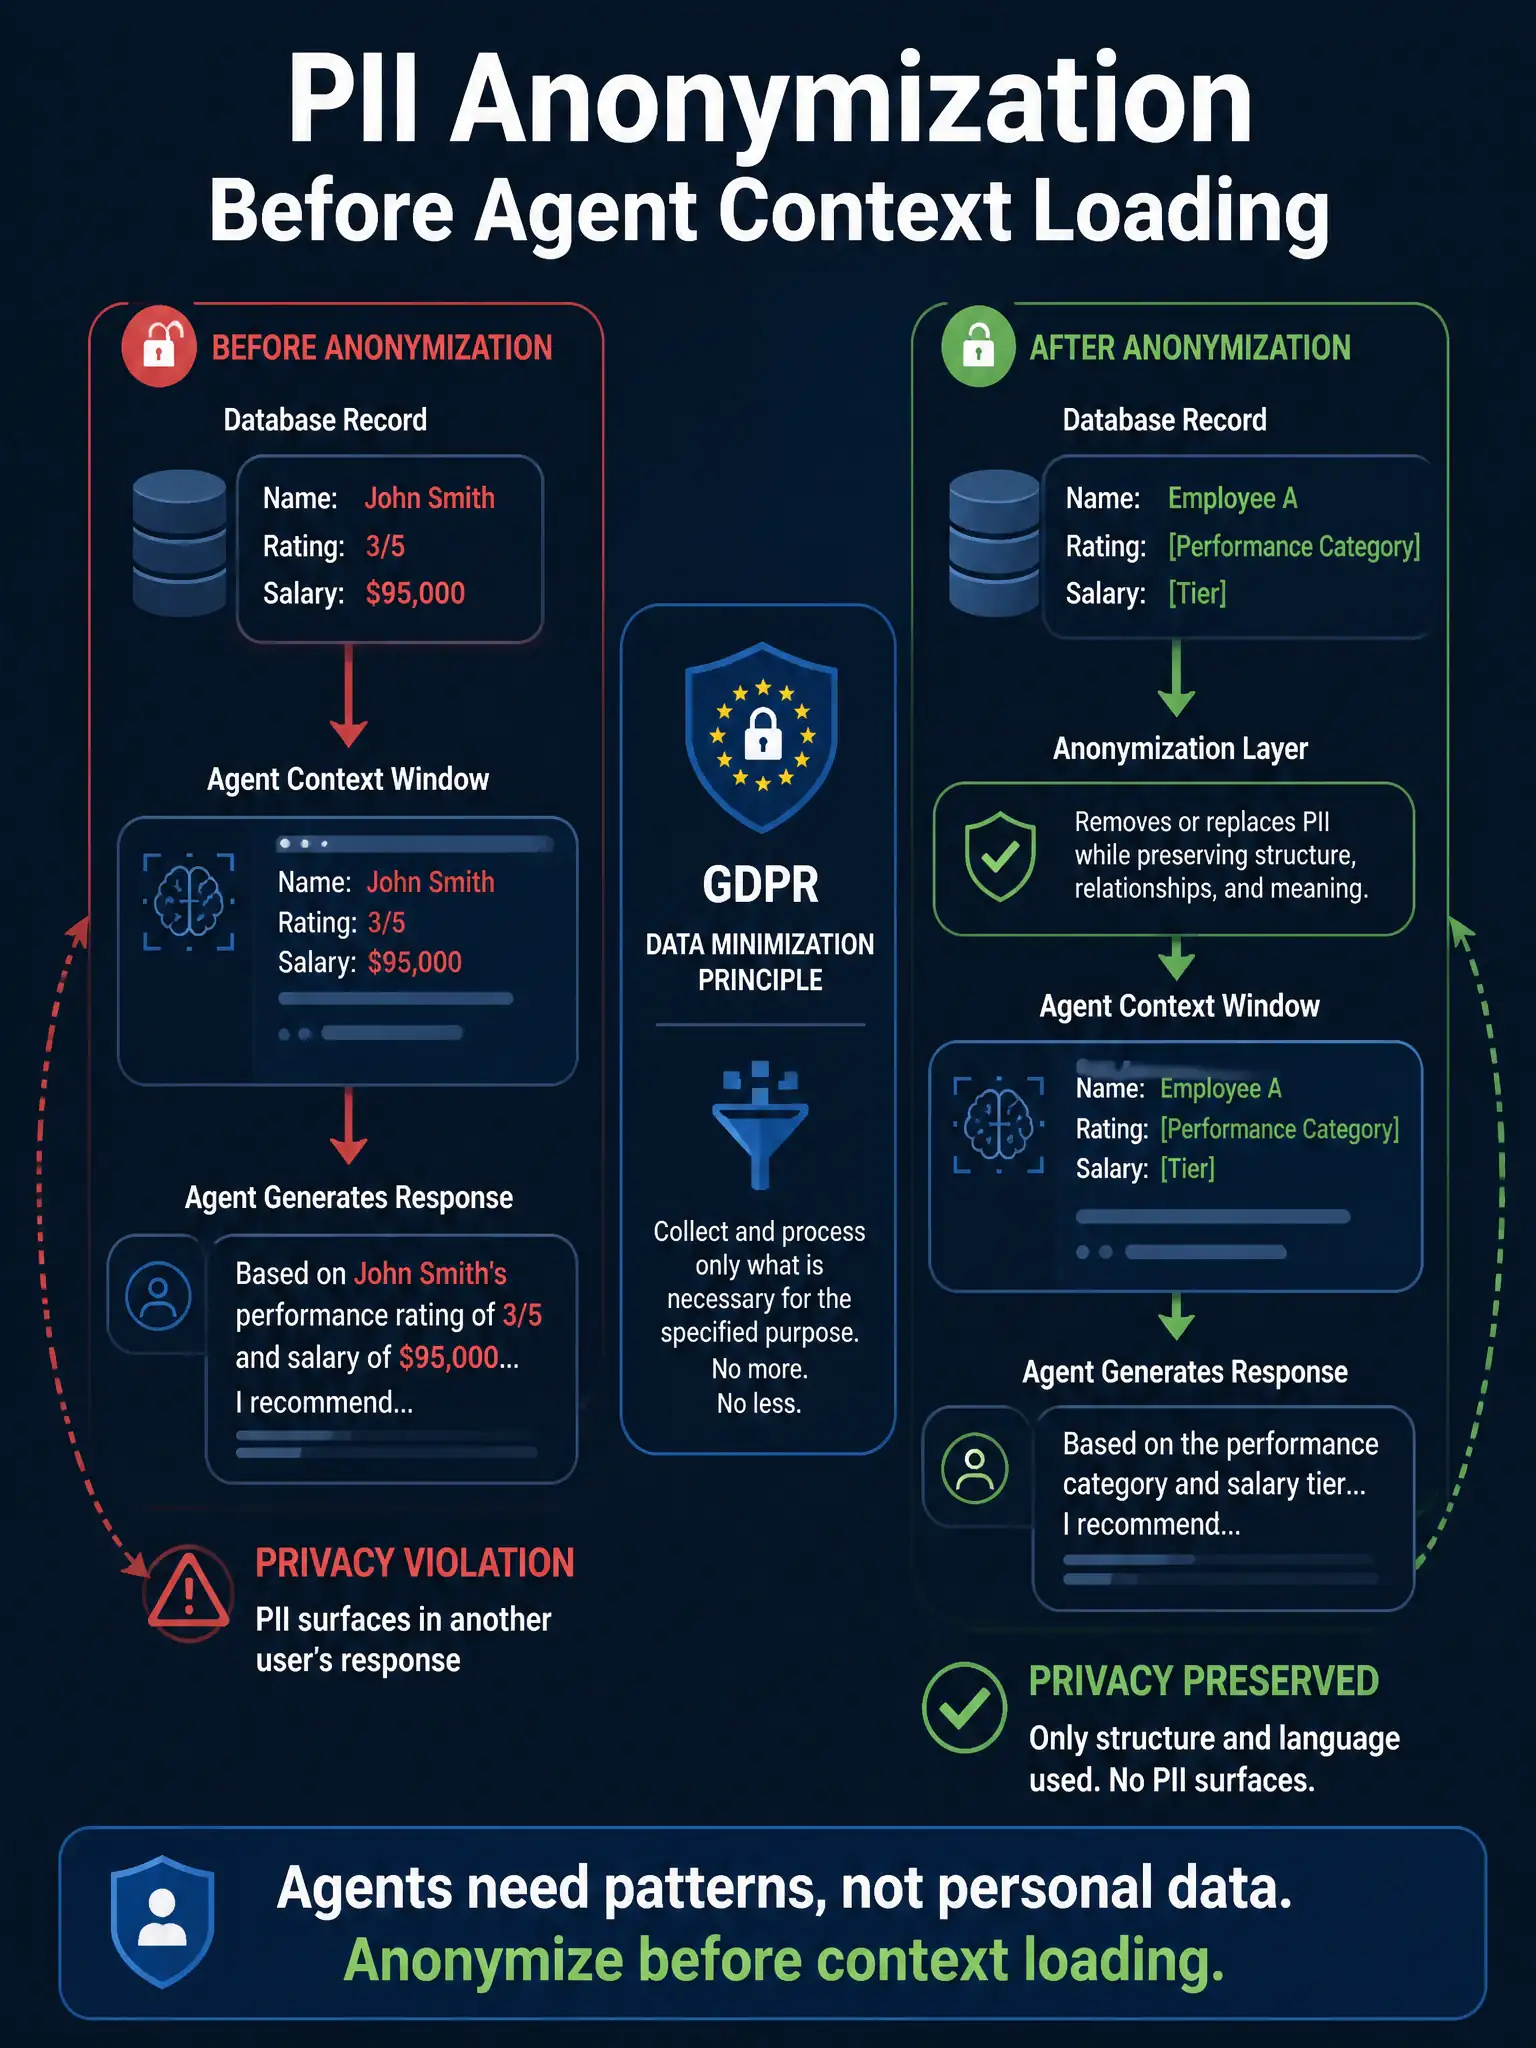
Loading real PII into an AI agent's context is like putting personnel files on a conference table—anyone in the room can see them. You should anonymize and pseudonymize names and compensation before records enter the context, so the agent learns review structure without exposing private data.
Full Explanation
The core privacy principle violated here is data minimization: agents should only process the personal data necessary for their task. To generate a performance review template, the agent needs to understand the structure and language patterns of reviews—it does not need the actual employee names, their specific ratings, or compensation figures.
The correct data handling practice is to anonymize and pseudonymize PII in database records before loading them into the agent's context window, replacing names and compensation figures with generic placeholders. This can include replacing real names with synthetic identifiers such as 'Employee One' or 'Team Member Two', replacing specific compensation figures with ranges or generic placeholders such as '$85,000' becoming '[Compensation Tier 3]', and replacing identifiable project names with generic references such as 'Project Phoenix' becoming '[Major Product Initiative]'. This transformation should happen at the data retrieval layer, before records enter the agent's context window.
GDPR applies because even when HR staff are authorized to access the underlying data, feeding it to a third-party AI model such as GitHub Copilot may constitute a new processing activity that requires its own legal basis, data processing agreement, and data minimization obligations.
The option that restricts the agent to only HR staff with access to the database addresses access control but not data minimization. HR staff using the agent may still inadvertently expose PII to other users if the agent surfaces it in shared contexts. The option that configures the agent to respond only to HR staff members and refuse requests from other roles also doesn't prevent the PII from being in the context; it only limits who sees the responses. If the model routes context across sessions, restriction on responses alone is insufficient. The option that adds a disclaimer to agent responses stating that any personal information provided is subject to GDPR protections is a legal notice, not a technical control, and does nothing to prevent the privacy violation.