
After a security incident where a Copilot agent is suspected of accessing files outside its intended scope, the forensics team cannot determine which specific tool calls were made, with what parameters, or in what order, because no tool-level logging was implemented. What should be added to the MCP server to support future forensic investigations?
Select an answer to reveal the explanation.
Short Explanation
Treat MCP tool-level audit logs like a flight black box: they capture every input and output at the exact point of execution, in sequence, immutably. You need what the agent actually did, not just what it thought it was doing. Don't trust the model's story when the tool log can tell you the truth.
Full Explanation
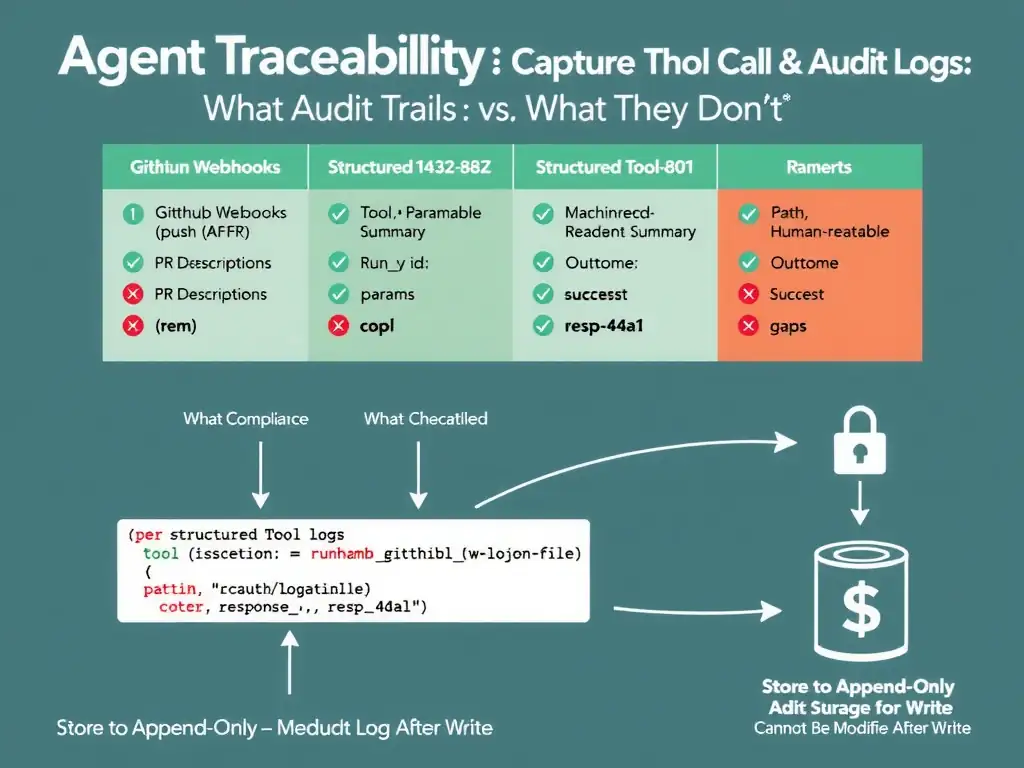
Forensic investigations of agentic AI incidents require logs at the right level of abstraction. GitHub's organization audit log captures platform-level events (API calls to GitHub's APIs), but MCP tool calls may involve internal tools, file system operations, or third-party APIs that are entirely outside GitHub's visibility.
Structured MCP audit logs must capture: - Timestamp (with millisecond precision for ordering) - Agent session ID (to correlate all actions within a single run) - Tool name (which tool was invoked) - Input parameters (the full parameter set passed—critical for understanding what paths, queries, or targets were accessed) - Output summary (what the tool returned—needed to determine what data the agent received) - Outcome (success, error, denied by allow-list)
The logs must be written to an immutable store (append-only, write-once) so that a compromised agent or attacker cannot delete evidence.
The verbose debug logging approach, where the agent's system prompt makes the model output its reasoning before each tool call, captures what the model intended, which is useful context but not a substitute for what actually executed. Prompt injection attacks are often designed to make the model think it's doing one thing while actually doing another, making the model's stated reasoning unreliable as forensic evidence. The approach of enabling GitHub's organization audit log to capture API events with full request bodies only covers GitHub API calls; internal tool calls are invisible to it. The video screen capture approach, such as recording the agent's terminal session for post-incident replay, is impractical, unstructured, and cannot be efficiently queried during an investigation.