
A development team deploys GitHub official remote MCP server to give their Copilot agent access to repository operations. Their security engineer asks: which security controls does the GitHub remote MCP server handle automatically, and which must the team configure themselves? Which statement correctly describes this division of responsibility?
Select an answer to reveal the explanation.
Short Explanation
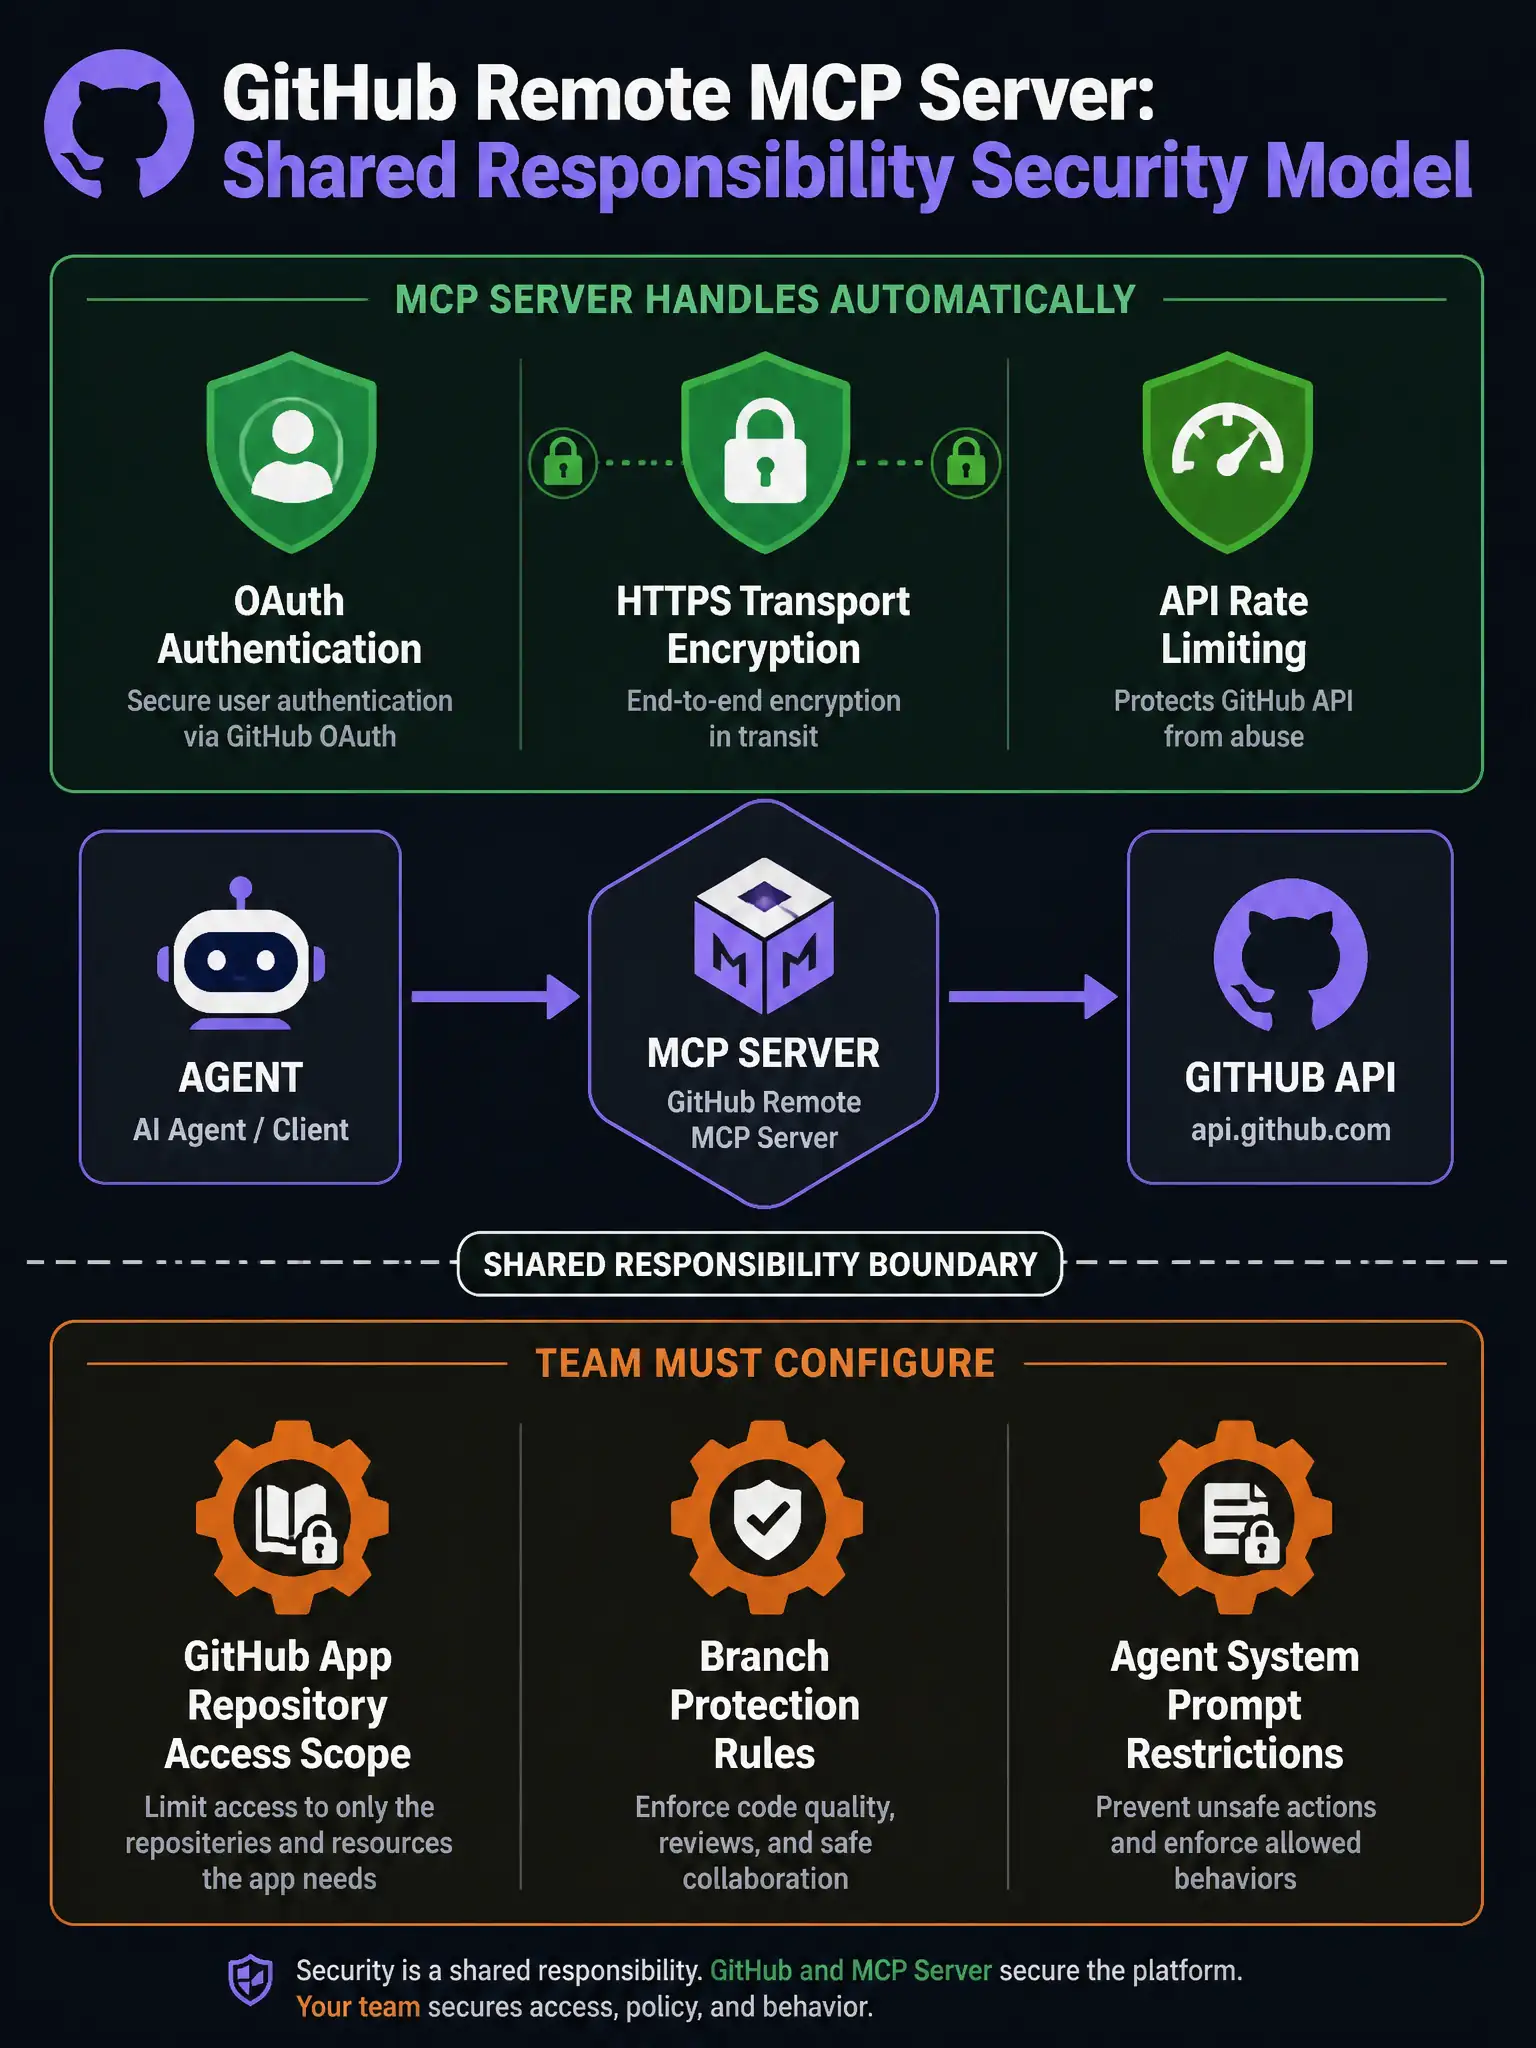
The GitHub remote MCP server handles OAuth, HTTPS, and rate limiting for you. You still own repository scope, branch protection, and the agent system prompt so it doesn't request operations it shouldn't.
Full Explanation
Understanding the shared responsibility model for remote MCP servers is essential for secure agent deployments. The GitHub official remote MCP server handles several security concerns at the infrastructure level: OAuth 2.0 authentication flows, including token exchange and refresh; HTTPS transport encryption for all MCP protocol traffic; and rate limiting aligned with GitHub API limits to prevent the agent from triggering abuse protections. The statement that says the GitHub remote MCP server automatically handles OAuth authentication, HTTPS transport encryption, and API rate limiting, while the team must separately configure repository access, branch protection, and the agent system prompt, correctly describes this boundary. The team retains responsibility for application-layer controls: configuring the GitHub App installation to restrict which repositories are accessible, which is done in GitHub App settings rather than the MCP server; enforcing branch protection rules on target repositories, which is configured in repository settings; and crafting the agent system prompt to restrict what tool calls the agent is permitted to initiate. The MCP server executes whatever tool calls the agent requests within its authenticated scope, and it does not second-guess whether a particular operation fits the agent's intended use case. The statement claiming the server handles all permission enforcement end-to-end, including restricting which repositories the agent can access and enforcing branch protection rules, overstates the server's capabilities. The server does not enforce business-level restrictions like preventing the agent from cloning every repository it has access to, or blocking force-pushes that branch protection rules would catch. Branch protection is a GitHub repository setting, not an MCP server feature. The statement saying the team must implement their own OAuth flow because the server only provides tool definitions and does not handle authentication is wrong in the opposite direction. The GitHub remote MCP server includes a complete OAuth flow, so developers do not need to implement their own OAuth layer; this is one of the key advantages of using the official remote server over running a local MCP server. The statement saying remote MCP servers have no built-in security controls and must sit behind a Web Application Firewall configured by the team is inaccurate. The remote MCP server communicates over HTTPS and implements rate limiting natively. A Web Application Firewall is not required for standard deployments, though it can be added for additional defense-in-depth in high-security environments.