
Your organization's main branch has branch protection enabled requiring two human approvals and passing status checks before merging. A new Copilot agent is configured to auto-approve its own pull requests once its internal confidence score exceeds 95%. During testing, the agent successfully merges a PR to main with only its own approval. What is the most likely cause of this failure?
Select an answer to reveal the explanation.
Short Explanation
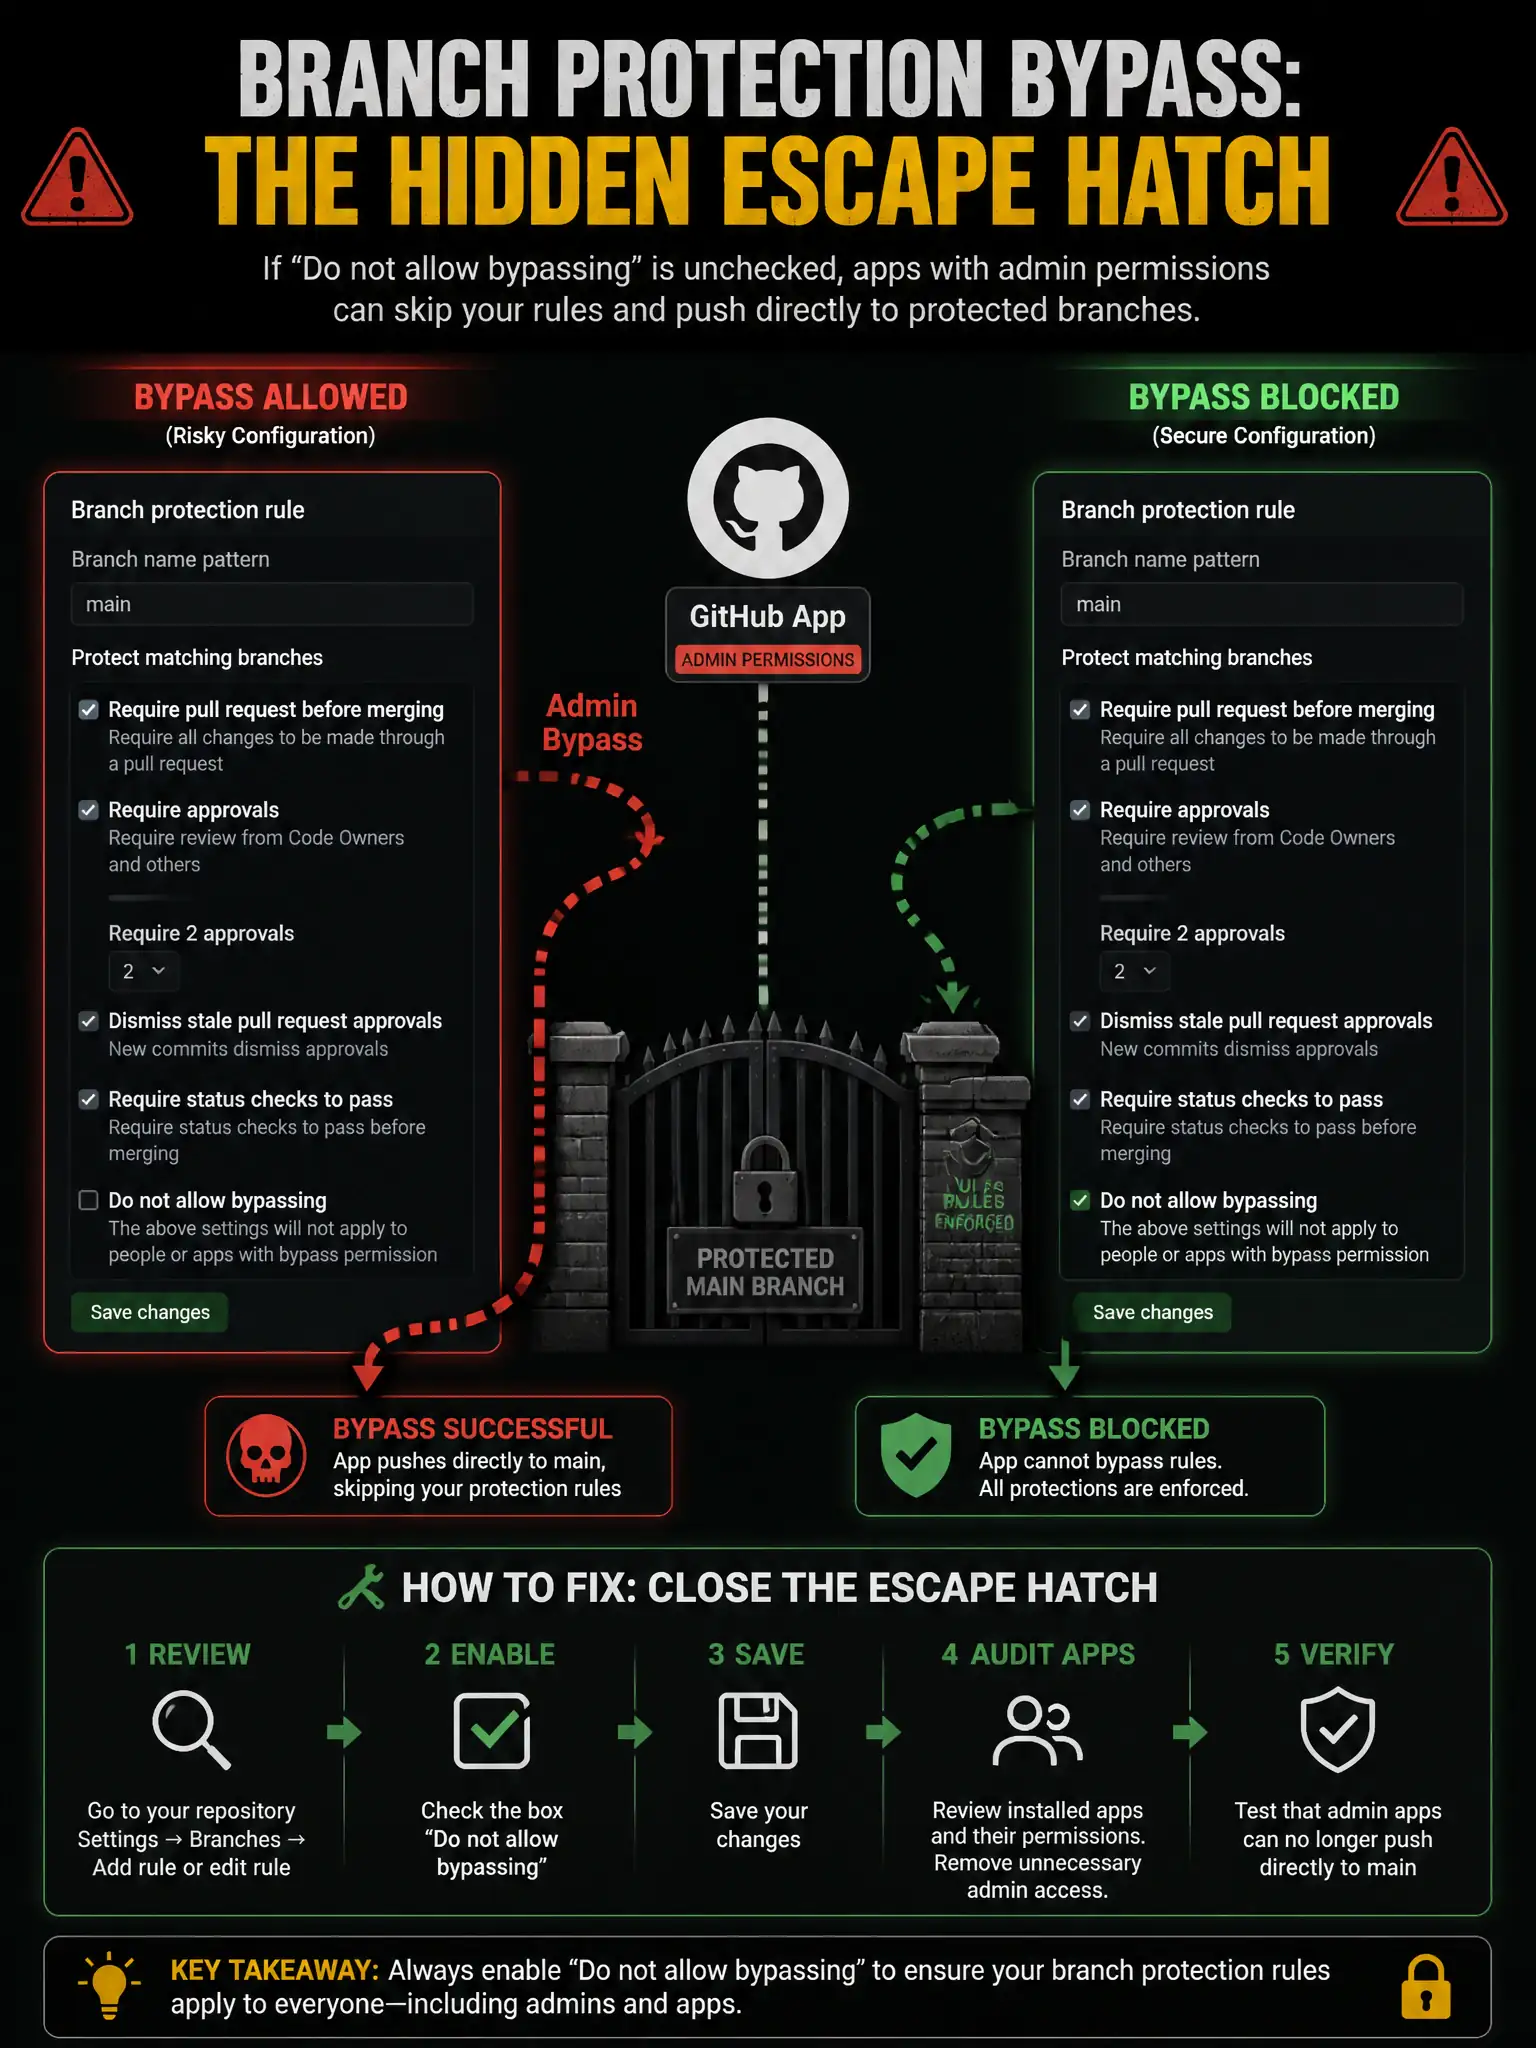
Branch protection has a bypass gap: if 'Do not allow bypassing the above settings' isn't on, a GitHub App with admin rights can walk right through it. That's why your agent merged with only its own approval. Turn on the no-bypass setting and trim the App's permissions.
Full Explanation
GitHub branch protection rules include a critical setting: 'Do not allow bypassing the above settings.' When this setting is off, which is the default, repository administrators and GitHub Apps with admin-level permissions can bypass branch protection rules, including approval requirements and required status checks. That is the most likely explanation for why the agent merged with only its own approval despite the two-approval rule. If the agent's GitHub App was installed with admin permissions, a common but overly permissive configuration, it can bypass branch protection entirely, regardless of the approval count or confidence score. The two-part fix is to enable 'Do not allow bypassing the above settings' in the branch protection configuration and reduce the agent's GitHub App permissions from admin to the minimum required, typically 'pull-requests: write, contents: read'. The suggestion to raise the confidence threshold to 99% addresses the agent's internal logic but not the platform-level bypass; a 99% confident agent with admin bypass can still merge without review. The claim that the two-approval requirement only applies to human contributors, not GitHub App installations, is incorrect because branch protection rules do apply to GitHub Apps, and there is no automatic exemption for Apps. The claim that status checks were not configured so the branch protection rule evaluated as passing by default would mean checks were not enforced, but that is a separate issue from the approval count failure, and the scenario specifies that the agent's own approval satisfied the two-approval requirement, pointing to bypass rather than missing checks.