
After deploying a Copilot agent that automatically closes resolved issues and merges approved PRs, your compliance team reports that the organization's audit log shows actions attributed only to the GitHub App service account, with no indication of which agent run, which user request, or which model decision triggered each action. What is the most important improvement to implement?
Select an answer to reveal the explanation.
Short Explanation
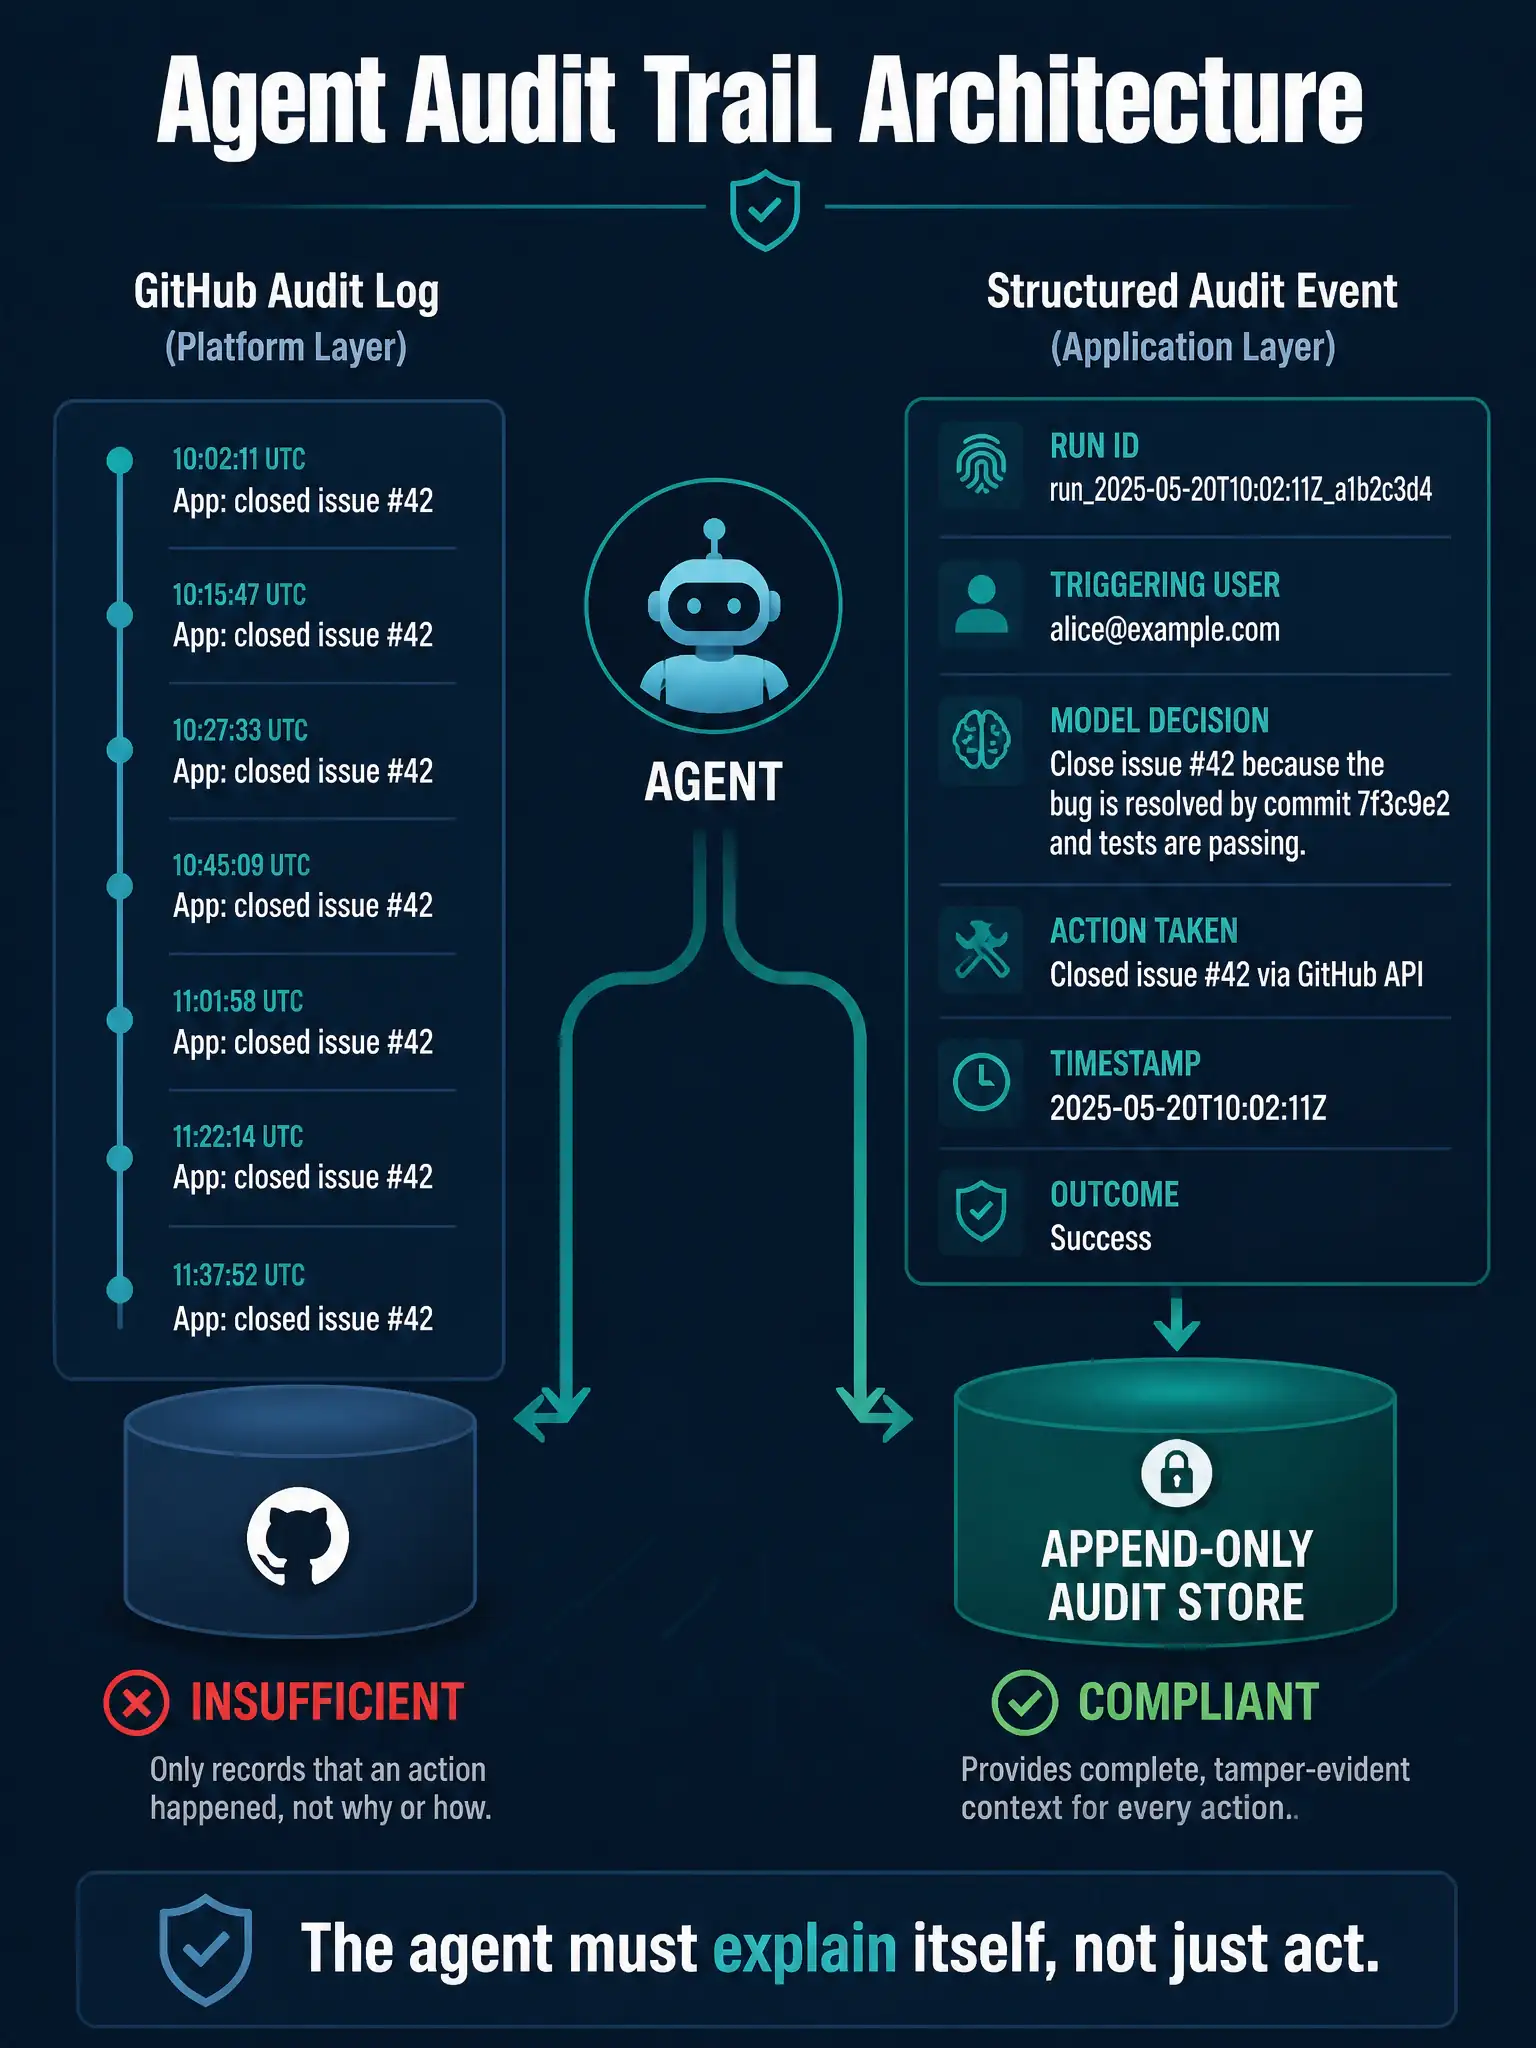
An audit trail is like a flight data recorder: it's useless if it only says 'the plane flew' without capturing what commands were given and why. You need structured pre-action audit events that record the run ID, triggering user, model decision summary, and action taken so compliance can trace each agent action. GitHub's audit log alone does not capture that reasoning chain.
Full Explanation
GitHub's organization audit log captures API calls at the platform level—who, meaning which GitHub App installation, did what action on which resource—but it has no visibility into the agent's internal decision-making process: what prompt triggered the run, which user initiated it, what the model's reasoning was, or which specific condition in the agent logic led to the action. This is the traceability gap the compliance team is identifying.
The correct improvement is to instrument the agent itself to emit structured audit events before each side-effecting action. These events should include the run ID so all actions from a single execution can be correlated, the triggering event such as a user manually triggering the agent or a webhook event starting it, a summary of the model's decision rationale, the specific action about to be taken, and a timestamp. These events should go to an append-only store, such as a dedicated audit log table, a SIEM, or an immutable blob storage location.
The dedicated bot user account option changes the display name but provides no additional traceability about why actions were taken. The GitHub organization audit log streaming option improves platform-level visibility but still captures only the external action, not the agent's internal reasoning. The issue or pull request comment option is a partial measure—it documents the reason but in a mutable, non-structured format that can be deleted and is hard to query for compliance purposes. Pre-action, structured, append-only audit events are the Responsible AI accountability standard.