
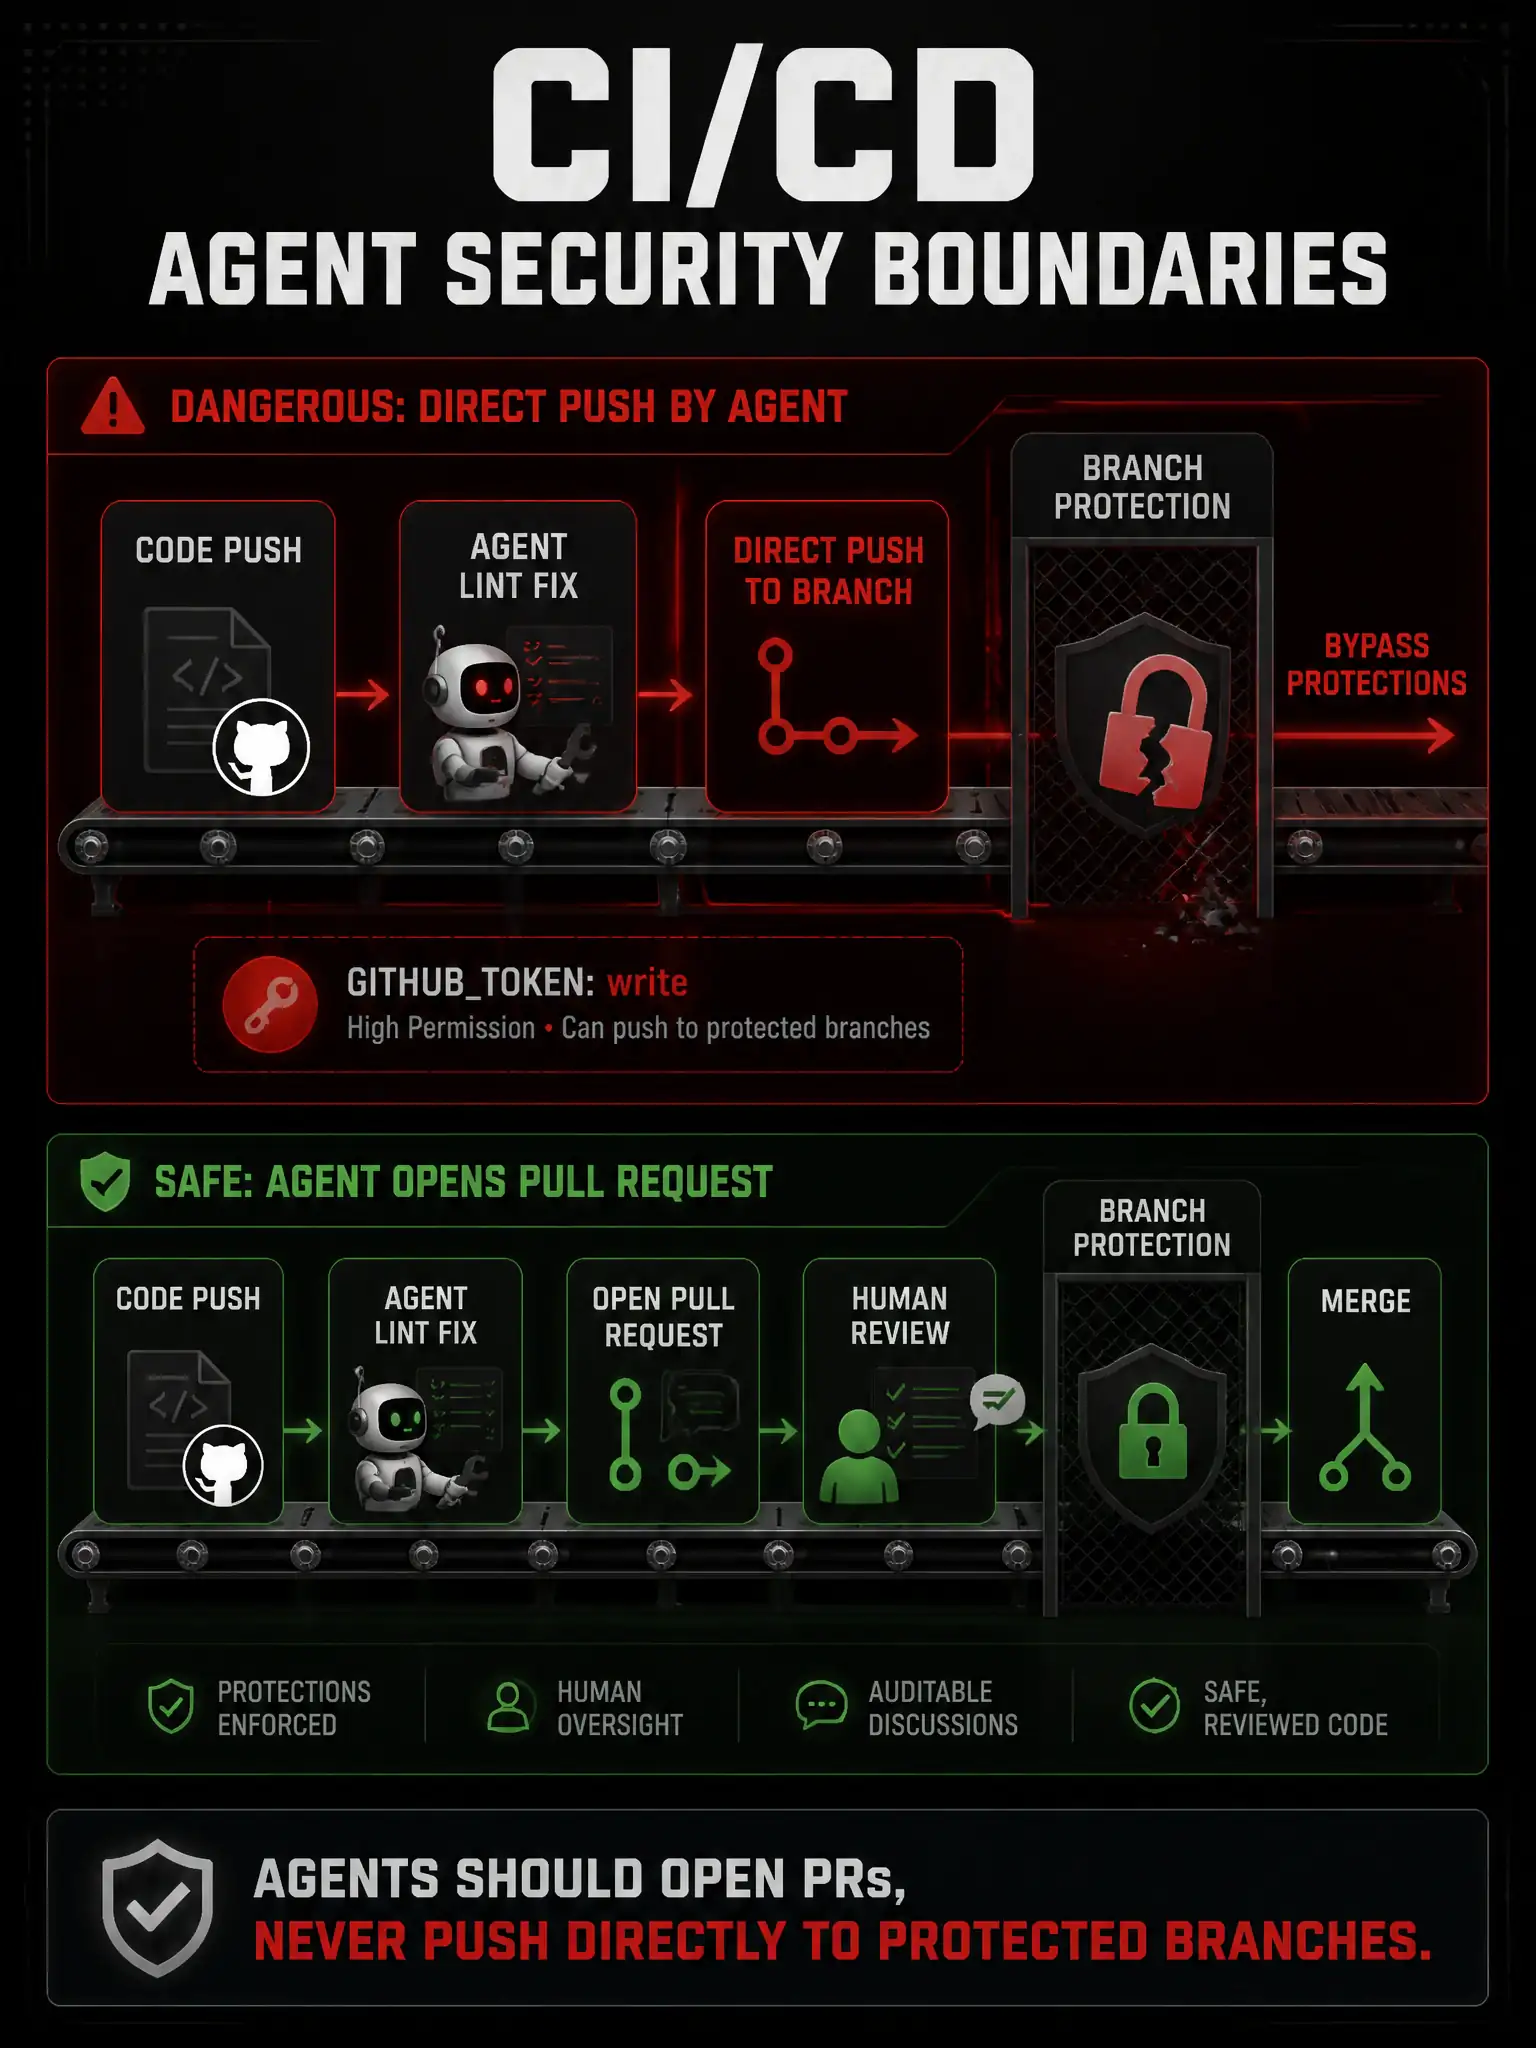
A Copilot agent is embedded in a GitHub Actions CI/CD pipeline to auto-fix linting errors and push corrected code directly to the triggering branch. A security engineer notes that this agent runs with the workflow's default GITHUB_TOKEN. Which security boundary violation does this pattern most clearly represent?
Select an answer to reveal the explanation.
Short Explanation
You've handed the agent a token with write access, so it can push straight to the branch and skip the human review that branch protection is supposed to enforce. That's the boundary violation: the token can do more than the workflow should allow.
Full Explanation
The correct answer is the statement that the default GITHUB_TOKEN has write access to the repository, allowing the agent to push code without human review and bypassing branch protection intent. The core violation is that the agent's use of the default GITHUB_TOKEN with write access allows it to commit and push code directly to branches that are presumably protected. Branch protection rules are designed to ensure that code changes pass through human review, or at least automated checks before merging, but an agent pushing directly to the triggering branch circumvents that intent. In a secure CI/CD architecture, agents should operate with read-only tokens when possible, and write operations should be gated by explicit human approval or restricted to non-protected branches, such as bot/* branches. Auto-fix agents should open pull requests rather than pushing directly, because that preserves the human review step. The retry-logic statement is an operational concern, not a security boundary issue. The statement recommending a PAT instead of GITHUB_TOKEN is actually worse from a security perspective: PATs often have broader scope and longer lifetimes than the GITHUB_TOKEN, which expires after the workflow run. The runner-isolation statement overstates the runner isolation problem; GitHub Actions runners are reasonably isolated, and the problem here is specifically the token permissions and agent authorization model. The correct mitigation is to configure permissions: pull-requests: write, contents: read in the workflow YAML, and have the agent open a PR with its fixes rather than pushing directly.