
An agent has merged a pull request and now needs to trigger a downstream integration test workflow in the same repository. The downstream workflow is defined in .github/workflows/integration-tests.yml and is configured with workflow_dispatch as a trigger. Which MCP tool call and token permission combination is required for the agent to trigger this workflow?
Select an answer to reveal the explanation.
Short Explanation
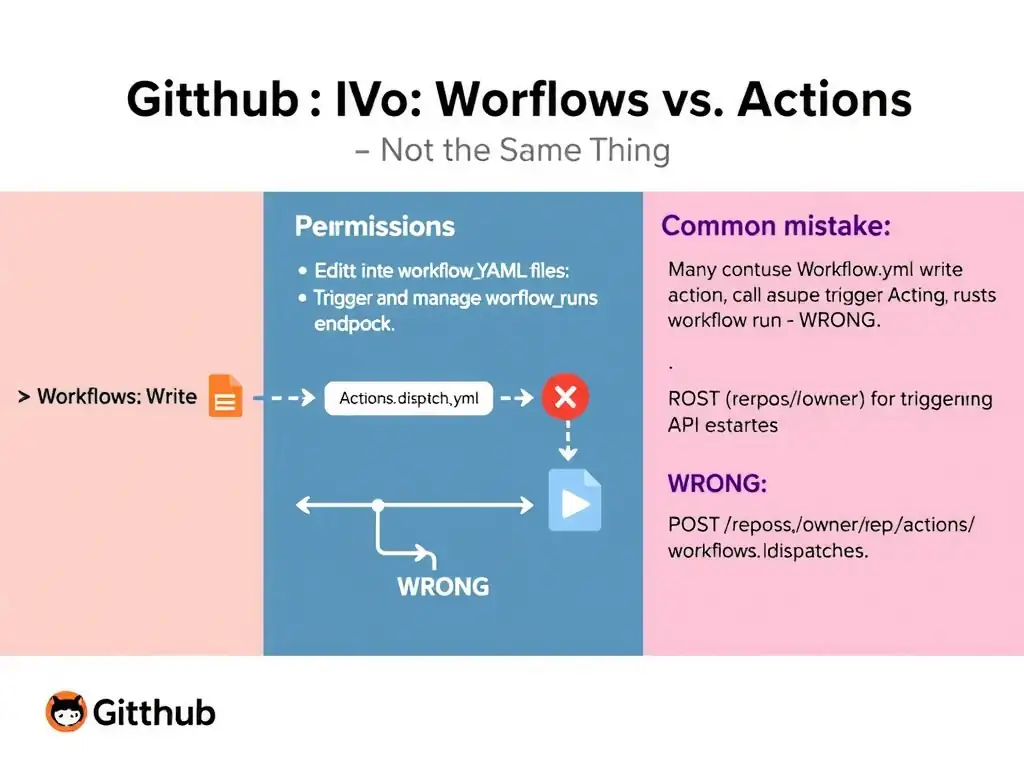
You trigger a workflow_dispatch run through the Actions API, not by editing the workflow file. You need Actions: write because that permission controls starting and managing workflow runs. Workflows: write only lets you edit the YAML recipe, not turn on the oven.
Full Explanation
GitHub's permission model distinguishes between modifying workflow definitions, which are the YAML files, and triggering or managing workflow runs, which are the actual executions. These are controlled by different permission scopes. The create_commit call targeting the workflow file with Contents: write is wrong. Committing a change to the workflow file to force a trigger event is a hack, not a proper invocation method. It would modify the workflow content unnecessarily, generate unwanted git history, potentially break the workflow if the commit introduces any syntax issues, and would trigger the workflow based on the push trigger if configured rather than workflow_dispatch. This is not the appropriate way to programmatically trigger a workflow. The create_check_run call with Checks: write is wrong. The create_check_run tool creates a check run entry in GitHub Checks system. It does not trigger workflow executions. Check runs are status indicators associated with commits. They are created by CI systems reporting their results, not used to initiate workflows. The trigger_workflow or equivalent workflow dispatch call targeting the workflow file name with Workflows: write is subtly wrong in a way the exam specifically tests. A Workflows: write permission grants the ability to create, modify, and delete workflow YAML files in the .github/workflows/ directory. It does not grant the ability to trigger workflow runs. This is a common confusion because the permission sounds like it should cover triggering workflows. The workflow dispatch endpoint call via an MCP HTTP tool or the GitHub MCP server workflow dispatch tool, targeting the workflow ID or filename with Actions: write, is correct. Triggering a workflow_dispatch event via the GitHub REST API, by posting to /repos/{owner}/{repo}/actions/workflows/{workflow_id}/dispatches, requires the Actions: write permission, not Workflows: write. The GitHub MCP server exposes this capability through a workflow dispatch tool, and an MCP HTTP tool can call the same endpoint. This is the correct, intended mechanism for programmatically triggering a workflow_dispatch-enabled workflow from an agent.