
A team reports that their database maintenance agent deleted a production database during a cleanup operation. The agent had been given broad database management permissions and interpreted a 'remove old test databases' instruction as applying to any database matching certain naming patterns. The production database matched the pattern. No authorization was requested before the deletion. What guardrail design failure does this most directly represent?
Select an answer to reveal the explanation.
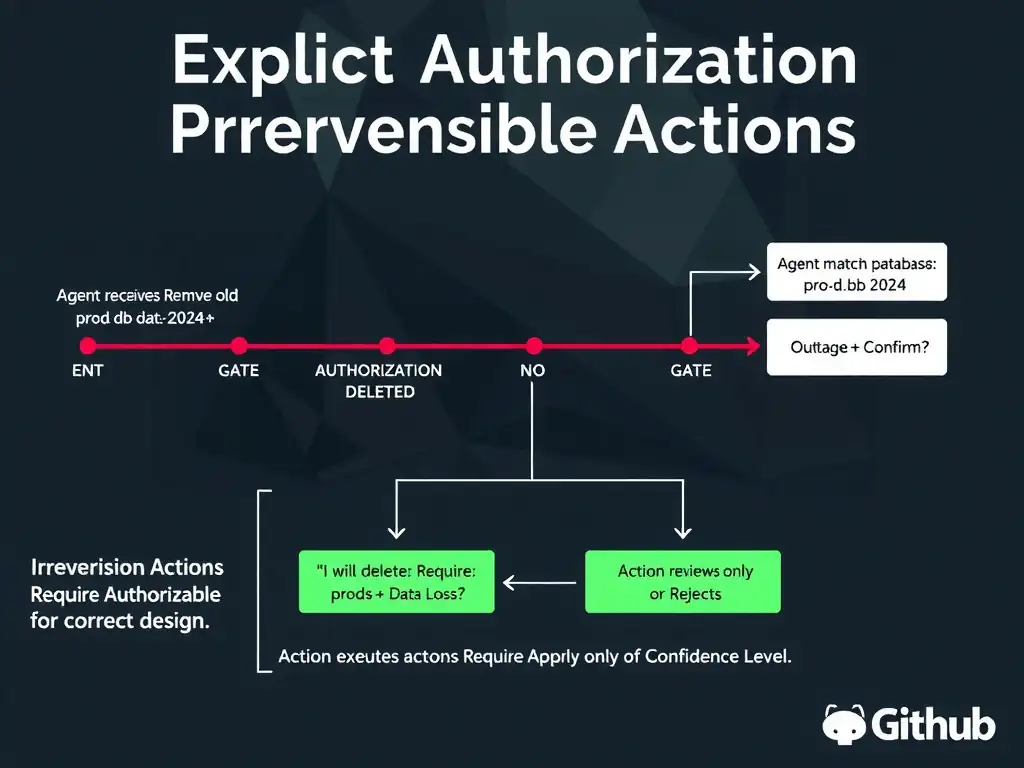
Short Explanation
If an agent can wipe production because it confidently matched a pattern, you've missed the real guardrail. You need explicit human confirmation before irreversible actions, especially production deletions, no matter how sure the agent is.
Full Explanation
This question tests your understanding of explicit authorization requirements for irreversible actions — a core guardrail principle in agentic AI systems.
The correct answer is the one requiring explicit human confirmation before irreversible actions. Irreversible actions — particularly those that destroy data, delete production resources, or make changes that cannot be undone — require explicit human authorization as a categorical requirement, independent of how confident the agent is in its reasoning. This is not a question of whether the agent's pattern matching was correct (it was working as designed) or whether the instruction was ambiguous (it was reasonably clear in context). The fundamental problem is that the agent was permitted to execute a production database deletion without pausing for human confirmation. Guardrail design must include: (1) identifying all irreversible actions; (2) classifying them as high-risk/compliance-level; and (3) requiring explicit authorization before execution, with the agent presenting what it intends to delete, why, and waiting for affirmative human approval.
The pattern-matching fix is incorrect. Improved naming pattern check might reduce the likelihood of this specific false match, but it does not address the root guardrail failure. Improved pattern checks could still produce false matches, and without an authorization gate, those false matches would also be executed automatically. The fix must be architectural (add the authorization gate), not just procedural (improve the pattern).
The more precise instruction is incorrect, though instruction clarity matters. Even with perfectly precise instructions, agents can make reasoning errors or encounter edge cases. Irreversible actions must have authorization gates that activate regardless of instruction clarity, precisely because the consequence of an error is unrecoverable.
Read-only database permissions are incorrect as a complete solution. Read-only access prevents the immediate problem but eliminates the agent's entire utility for database maintenance. The correct approach is to keep write access but gate destructive operations behind explicit authorization, not to remove capability entirely.
The principle: explicit authorization for irreversible changes is non-negotiable, regardless of agent confidence. The exam tests whether you know that confidence level doesn't override the authorization requirement for irreversible changes.