
A compliance audit requires the team to identify all commits made by AI agents versus human developers over the last six months. The agent has been committing code using a shared service account (ci-bot) with no additional metadata in the commit message. The audit team cannot distinguish agent commits from human commits made through the same account. What should have been implemented from the start?
Select an answer to reveal the explanation.
Short Explanation
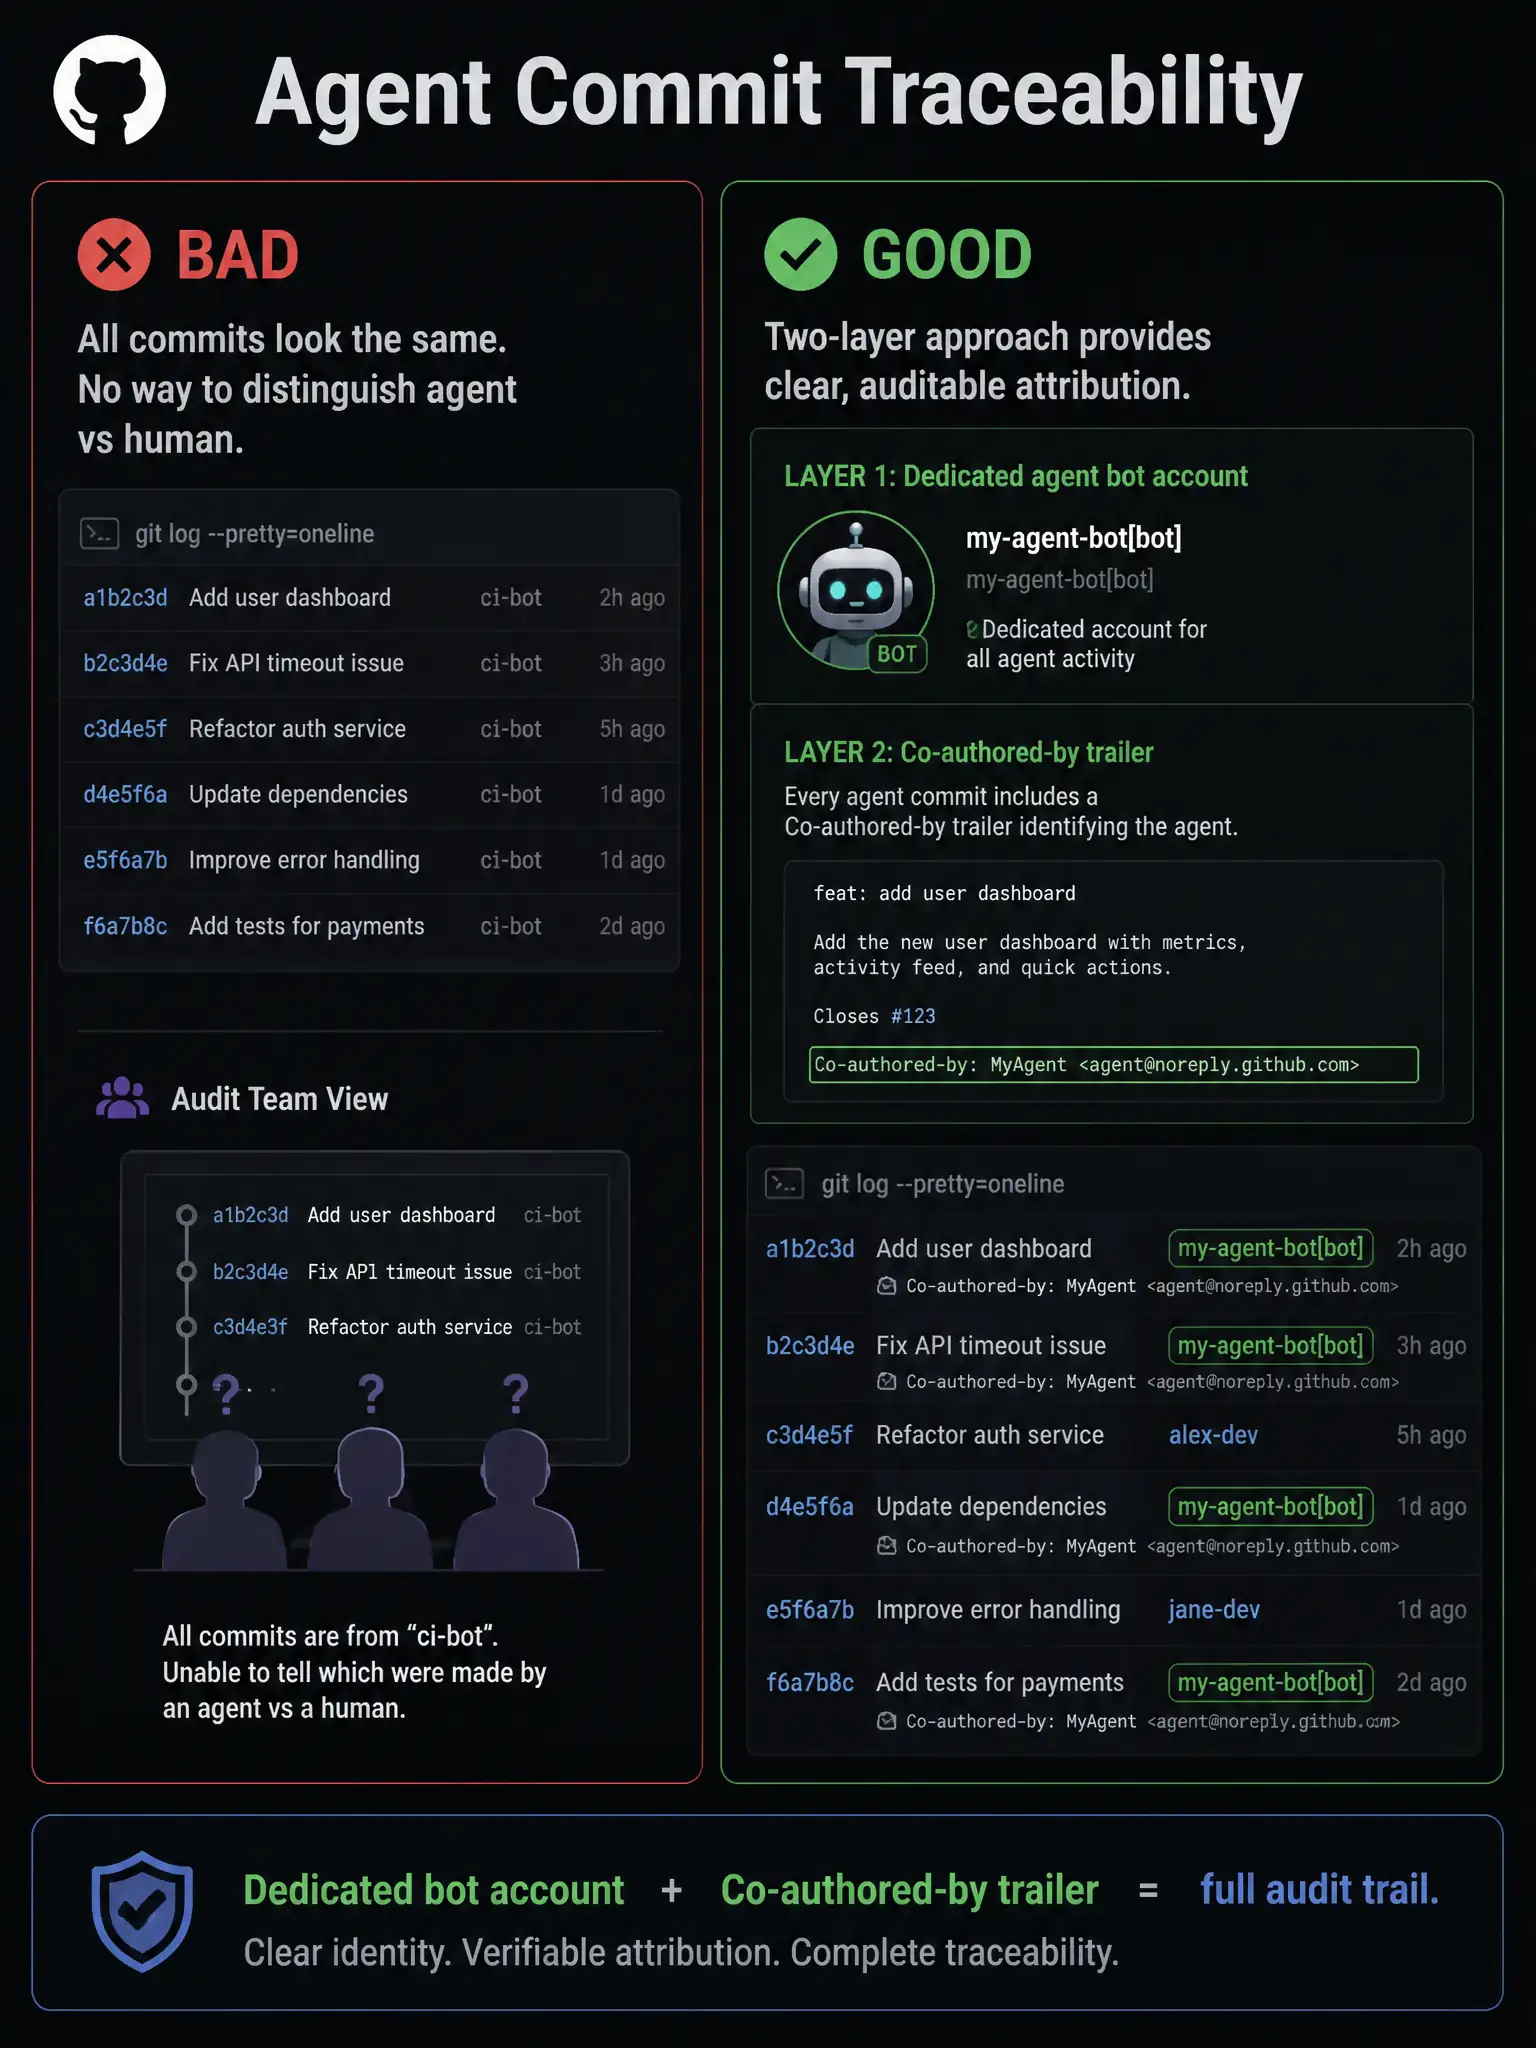
When an AI agent and a human both commit through the same ci-bot account with no labels, they're indistinguishable — like two chefs signing the same dish with 'the kitchen.' You fix this by using a dedicated agent bot account and adding a Co-authored-by: Agent Name <agent@noreply> trailer to every commit message.
Full Explanation
GitHub provides two standard mechanisms for identifying agent-authored commits in the audit trail.
First, the agent should use a dedicated GitHub App or bot account (for example, my-agent-bot[bot]) rather than a shared service account. This makes all agent commits immediately filterable by author in GitHub's search and audit log.
Second, the agent should append a Co-authored-by trailer to every commit message: Co-authored-by: MyAgent <[email protected]>. This trailer is rendered in GitHub's UI, included in git log output, and queryable in the GitHub API, providing a clear signal that an agent participated in the commit.
Together, these two practices make agent commits fully traceable and distinguishable from human commits in any compliance audit.
The separate-branch approach, where agent changes are made to a branch that is never merged to the main branch, would mean agent changes never reach the main codebase and would make agent work invisible to the audit for the wrong reason — traceability requires the commits to be in the main history, just labeled.
The separate CHANGELOG file approach is a supplemental documentation practice that does not make the commits themselves identifiable in git log or GitHub's audit APIs.
The GPG-key approach, where agent commits are signed with a key unique to the agent, is a commit signing approach that verifies the commit was made by a specific key holder. While useful for authenticity, GPG signing alone does not provide the human-readable audit trail or UI-visible labeling that Co-authored-by trailers and dedicated bot accounts provide, and it adds key management overhead.