
After deploying an automated access-provisioning agent in a financial services organization, the compliance team flags it as a violation. The agent independently approves, provisions, and audits all access changes without any human review step. The organization's policy requires segregation of duties for access management. What is the most appropriate remediation?
Select an answer to reveal the explanation.
Short Explanation
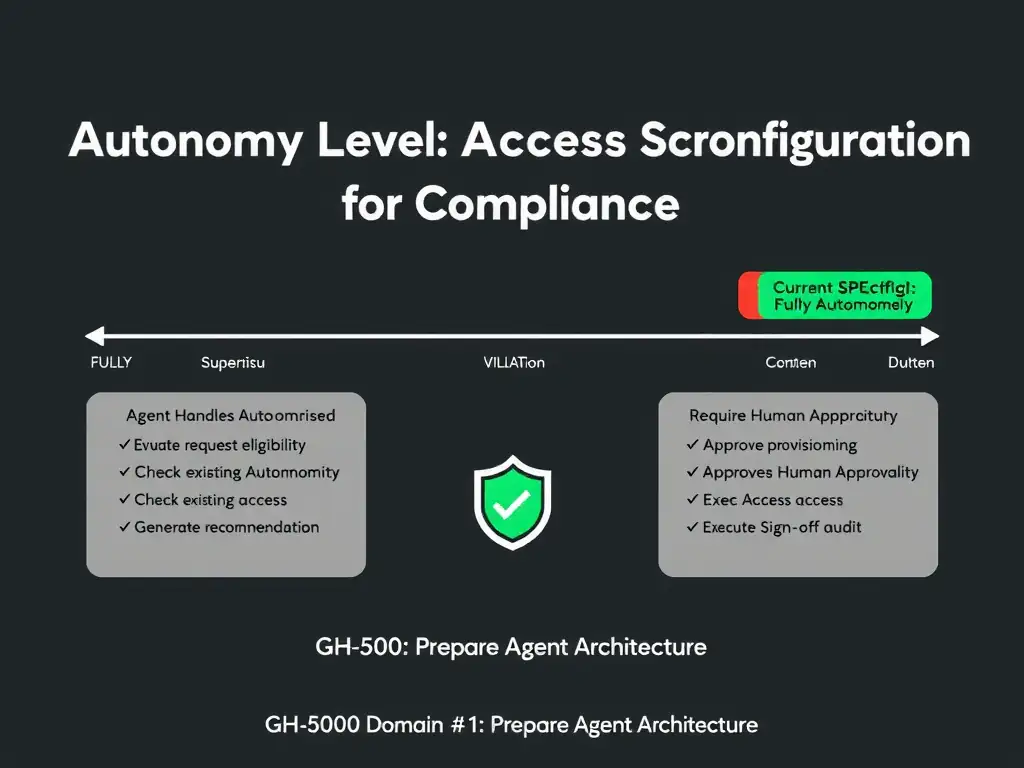
If a bank teller approves their own wire transfers, executes them, and signs off on the audit, that's a compliance nightmare, so banks separate those duties. Your agent was doing all three, so you need to dial back its autonomy level and put humans in charge of approval while the agent handles routine groundwork.
Full Explanation
Autonomy level configuration is a deliberate architectural choice in agentic system design. Agents can operate across a spectrum: fully supervised, where every action requires human approval; partially autonomous, where routine actions are automatic and high-risk or sensitive actions require approval; or fully autonomous, where there are no human checkpoints. The right level depends on the risk profile of the actions involved and the regulatory constraints of the operating environment.
The appropriate remediation is reducing the agent's autonomy level by configuring mandatory human approval checkpoints for provisioning decisions, while reserving fully autonomous operation for low-risk tasks only. In a regulated financial services environment, access provisioning is explicitly governed by segregation-of-duties policies, meaning the same entity cannot approve, execute, and audit access changes. The agent's autonomy level must be reconfigured to insert mandatory human approval checkpoints for provisioning decisions. Routine, low-risk read operations, such as checking whether an account exists, can remain autonomous, but the actual provisioning decision must route through a human approver. This is not a failure of the technology; it is a misconfiguration of the autonomy level for the compliance context.
The rule-based automation replacement, which would remove artificial intelligence entirely because such agents supposedly cannot be compliant in regulated industries, is an overreaction. Artificial-intelligence agents can be compliant in regulated industries; the problem is misconfiguration, not the technology itself. Well-configured agents with appropriate human checkpoints are widely used in financial services.
The detailed logging approach, which lets auditors review what the agent provisioned after the fact, improves post-hoc auditability but does not fix the segregation-of-duties violation. If the agent provisioned access without human approval, logging that fact more thoroughly does not make the provisioning compliant. Compliance requires procedural controls at decision time, not just records after the fact.
The read-only interface scope approach, which lets the agent assess access requests but prevents it from provisioning anything, eliminates the compliance problem by eliminating the agent's usefulness. The goal is a properly configured agent that automates what is safe to automate, not a fully disabled one.
For the exam: 'too much autonomy,' 'no human review,' 'compliance violation,' and 'segregation of duties' all point to autonomy-level misconfiguration. The fix is targeted reduction of autonomy with human checkpoints, not elimination of the agent.