
You want to enable a GitHub Copilot agent to autonomously create a new branch, commit changes to it, and open a pull request — all without human intervention. Which two things must be true for this to work correctly?
Select an answer to reveal the explanation.
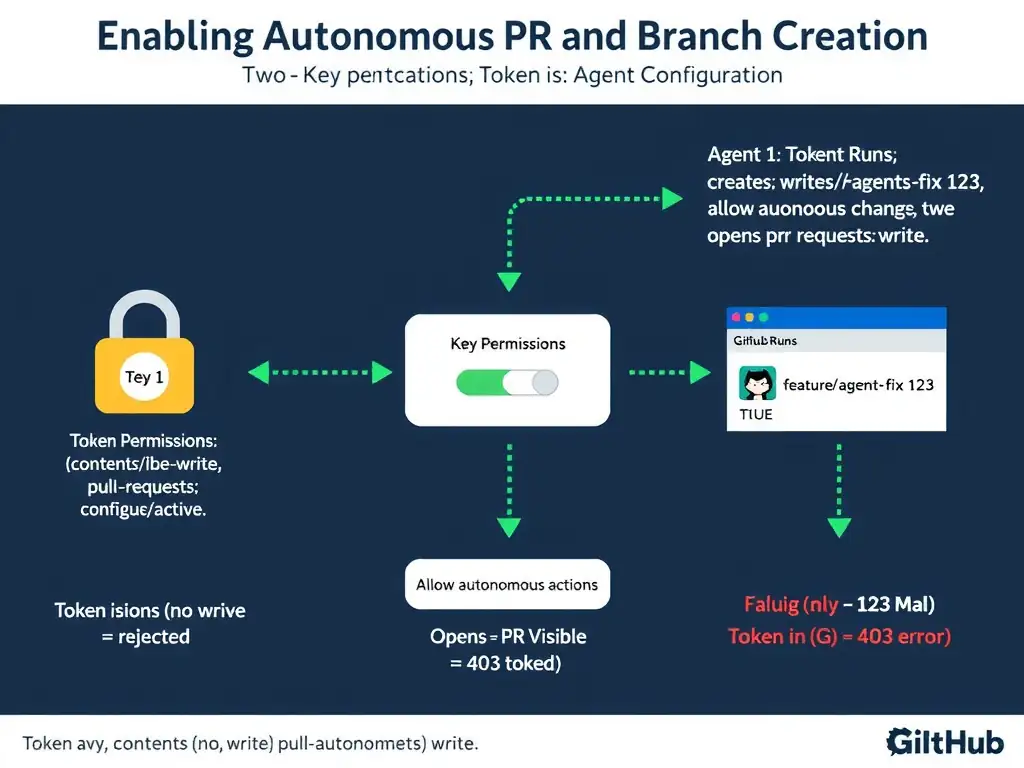
Short Explanation
To let a Copilot agent create a branch, commit, and open a PR on its own, you need both the right token permissions and the agent's own autonomous-action setting. The token needs contents: write and pull-requests: write, and the agent definition must explicitly allow autonomous actions. If either piece is missing, the agent can't finish the job.
Full Explanation
Enabling autonomous branch creation and pull request submission requires satisfying both the authentication layer (correct token permissions) and the agent configuration layer (explicit enablement of autonomous actions).
The choice requiring a service account token with admin:repo scope and disabled branch protection rules on all branches is incorrect. admin:repo scope is a classic OAuth scope for GitHub Apps and PATs that confers broad administrative access. Modern best practice, and the GitHub Copilot agent framework, uses fine-grained permissions specified in the workflow or app installation. More critically, disabling branch protection rules on all branches is not a prerequisite — agents can create new branches, which are not protected by default, without touching protection rules on main.
The correct choice is the one requiring the agent's GitHub token to have contents: write and pull-requests: write permissions, and requiring the agent to be explicitly configured to allow autonomous actions in its definition. The GitHub Actions GITHUB_TOKEN or a GitHub App token requires fine-grained permissions declared in the workflow: contents: write allows creating/updating files, creating branches, and pushing commits via the API; pull-requests: write allows creating and updating pull requests. Beyond the token, the agent definition must explicitly enable autonomous actions. Without this explicit opt-in, the agent may not have the runtime authorization to perform actions that modify repository state, even if the token technically allows them. This two-layer design prevents accidental or unintended autonomous behavior.
The choice requiring the agent to run as an org owner and the workflow to use runs-on: self-hosted to access the git binary for branch creation is incorrect. Running as an org owner is not required for branch creation and PR submission. These are standard repository operations available to users and apps with appropriate repository permissions. The runs-on label, whether self-hosted or GitHub-hosted, relates to the runner infrastructure, not to Git permissions or agent authorization.
The choice requiring the repository owner to approve each branch creation and PR in real time through the GitHub mobile app before the agent can proceed is incorrect. The scenario explicitly calls for autonomous action without human intervention. Requiring real-time approval defeats the purpose of agent autonomy. Some workflows may include human approval gates as a safety measure, but this is optional and configured at the workflow level — it is not a default requirement for agents to create branches and PRs.
Key point: autonomous actions need both the right token permissions and explicit agent-level configuration enabling autonomous behavior.