
Why do many enterprises set the default GITHUB_TOKEN workflow permissions to read-only at the organization or enterprise level?
Select an answer to reveal the explanation.
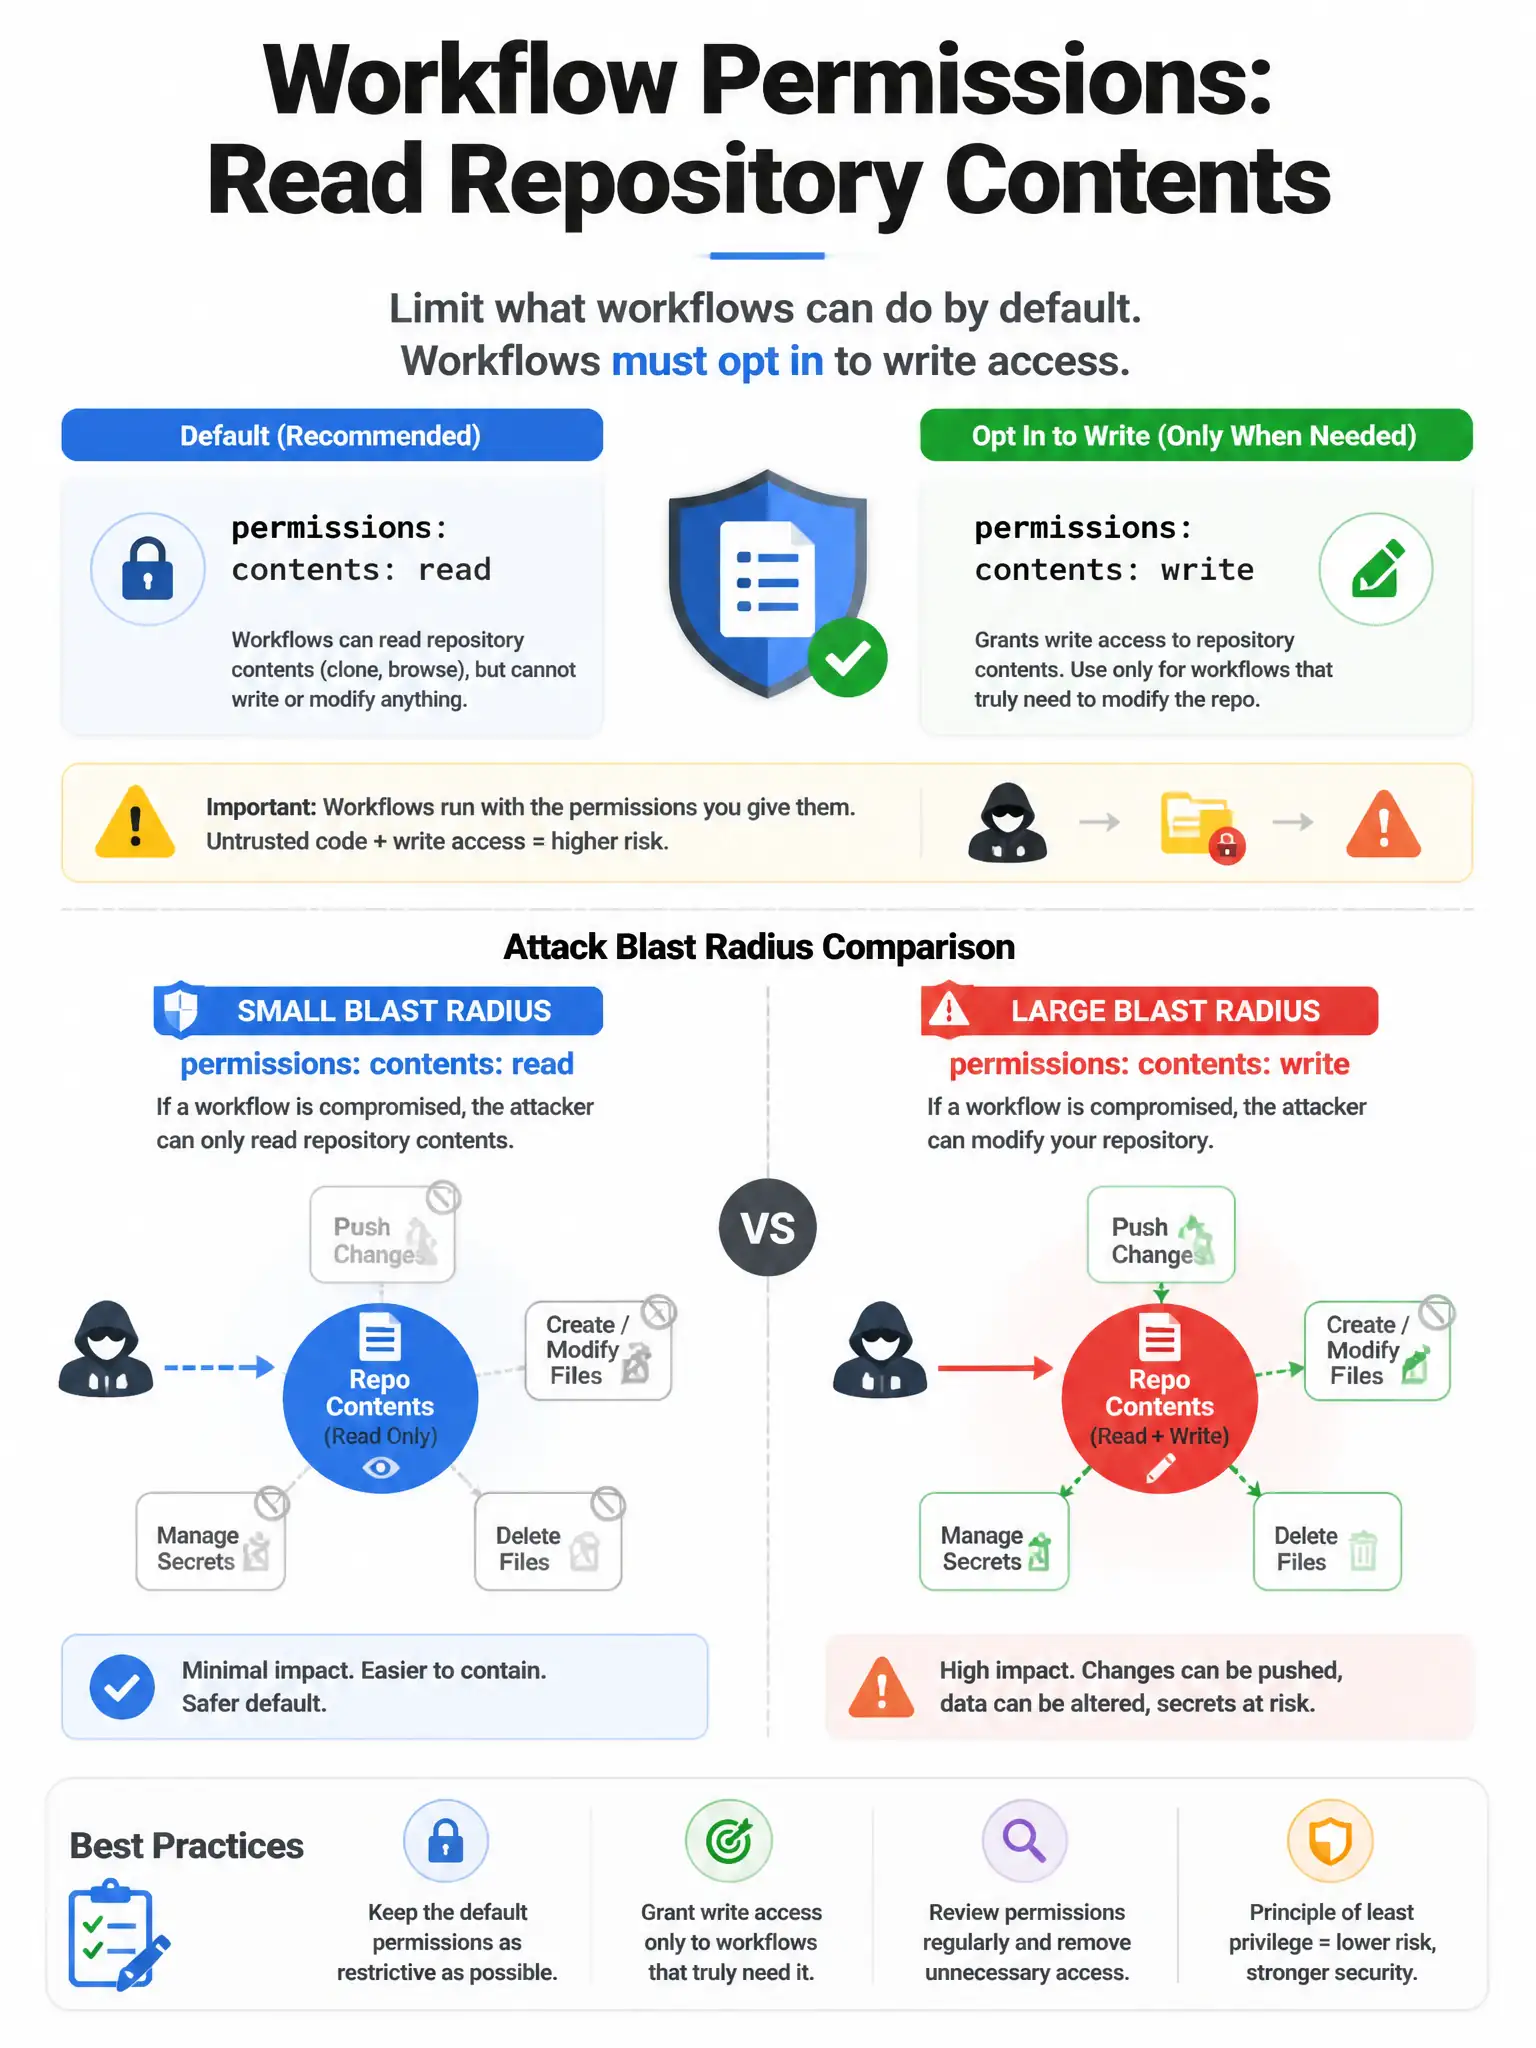
Short Explanation
Default read for GITHUB_TOKEN is least privilege for CI: a random workflow cannot push or rewrite releases unless someone explicitly opts into write permissions. That shrinks damage from poisoned dependencies or bad PRs. It does not replace branch protection and is unrelated to interactive human login tokens.
Full Explanation
Reducing blast radius by requiring explicit write permissions is correct: default read-only GITHUB_TOKEN lets workflows request contents: write only when needed. The force-workflows-to-fail option is not the goal; well-written workflows still succeed. The eliminate-branch-protection option is false. The personal-access-token-for-UI option confuses workflow tokens with user auth. Pair with forbidden fork write patterns, environment gates, and actions allow lists.