
An enterprise enables an IP allow list. Which two statements correctly describe common interactions with GitHub Apps and automation? (Choose two)
Select all correct answers, then click Submit.
Short Explanation
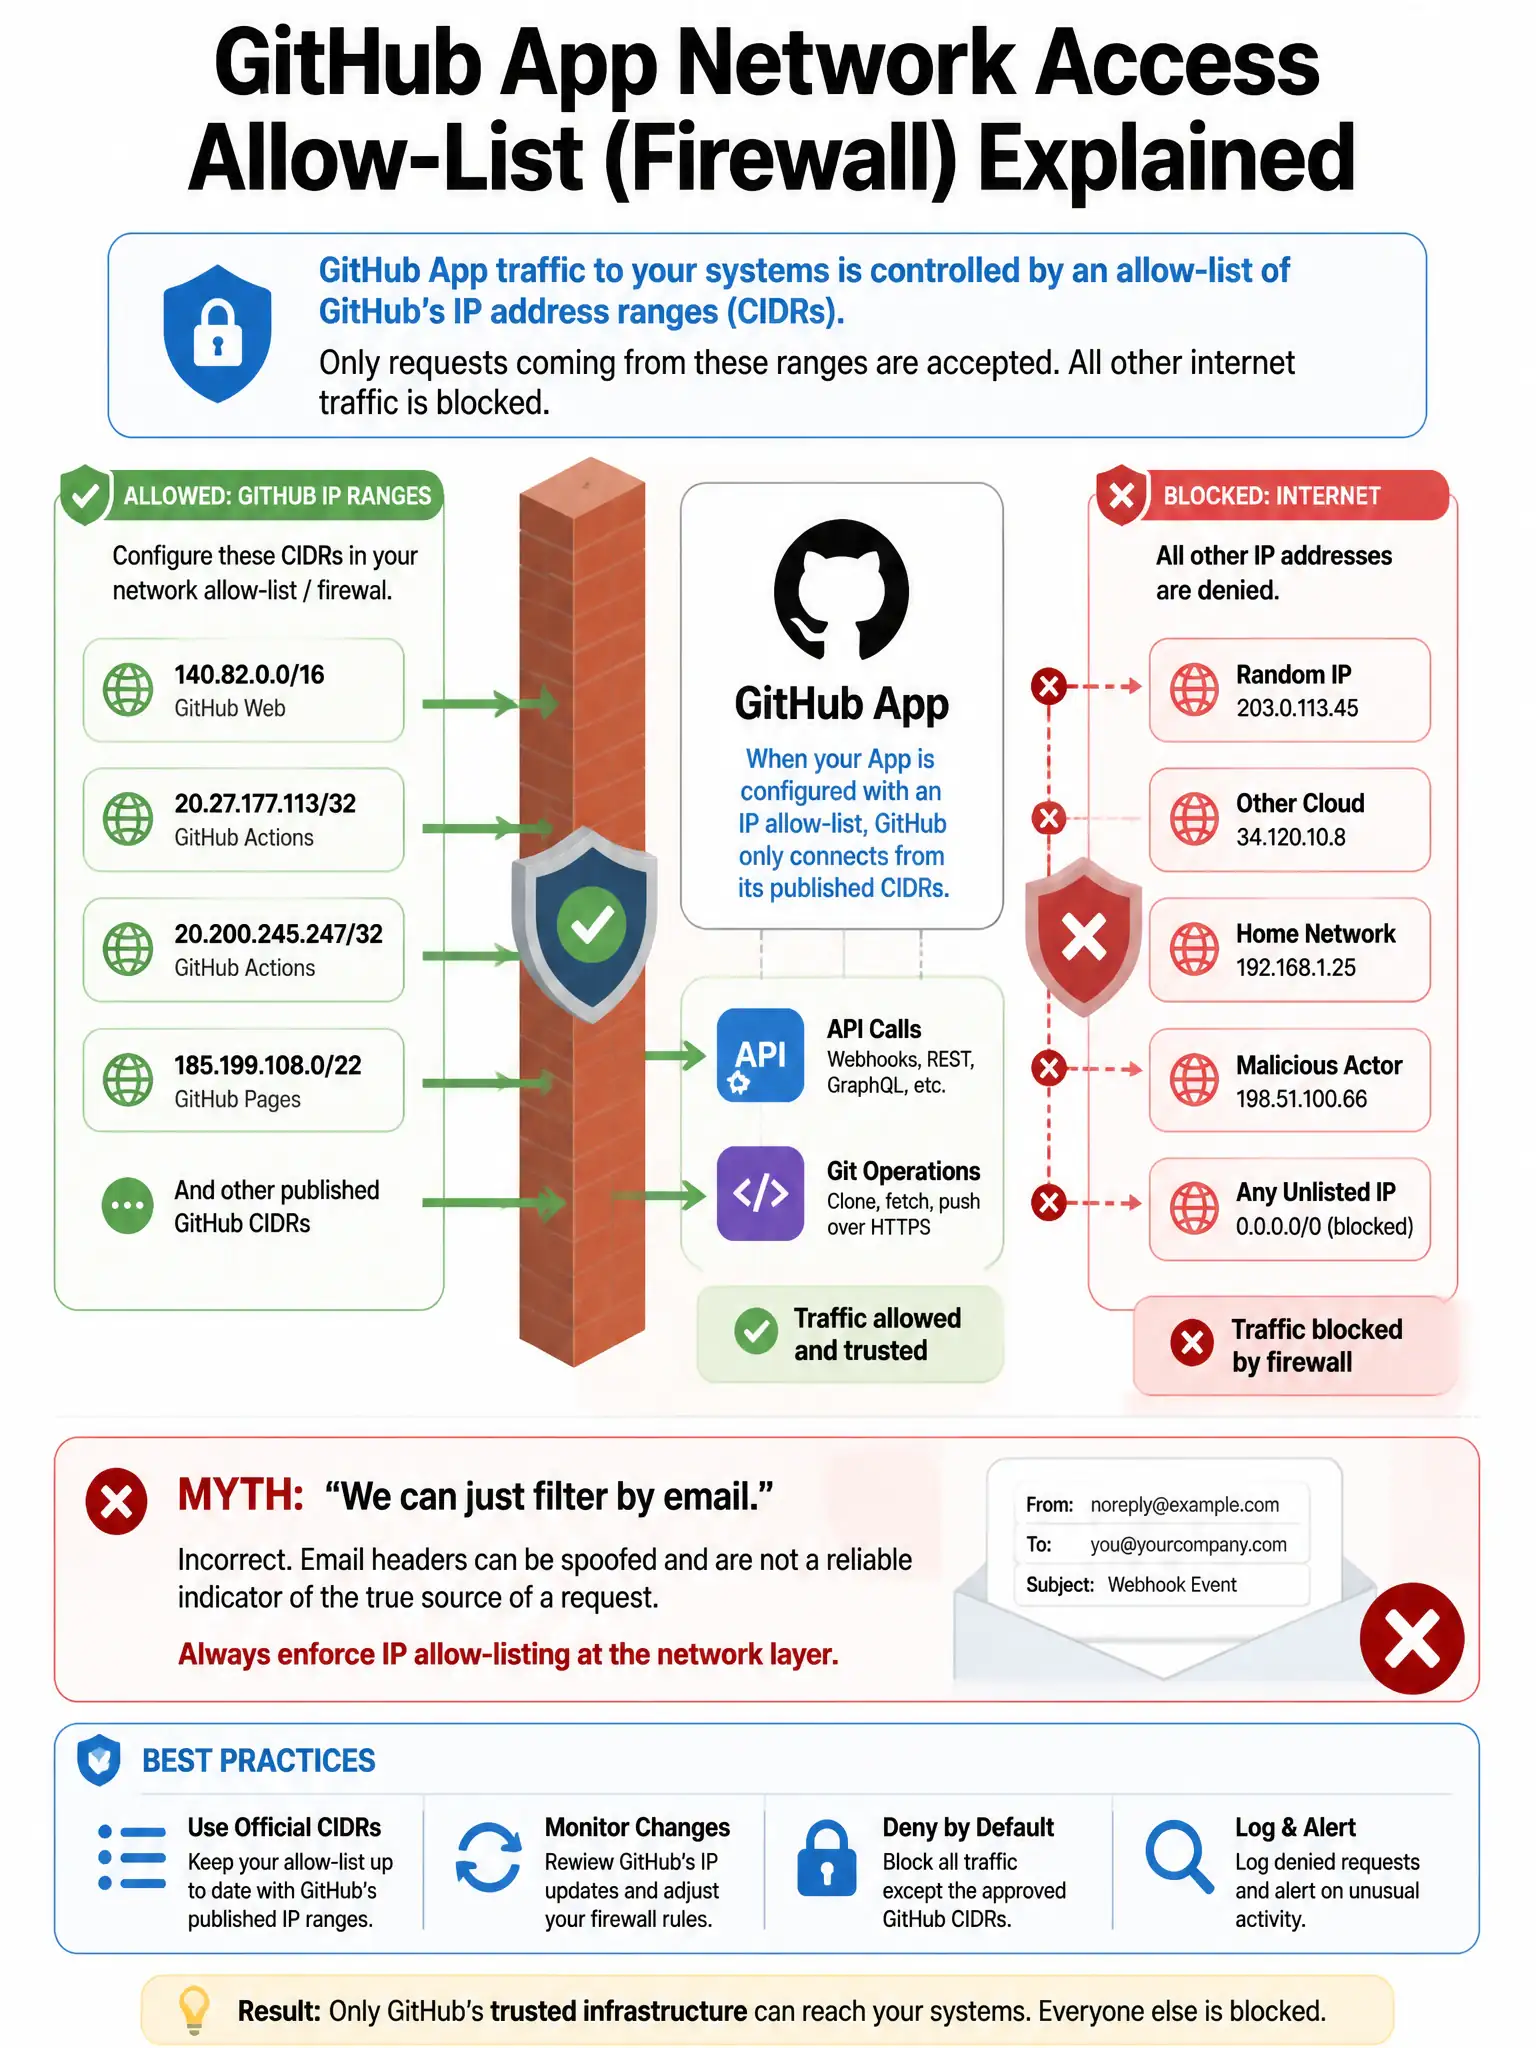
IP allow lists fence who can hit your enterprise/org from the network path. You've got to account for user-to-server traffic that may still need to satisfy those rules depending on how access is made, and admins can configure allow list settings that account for GitHub App access patterns.
Full Explanation
The correct statements are that user-to-server access can still be subject to IP allow list enforcement depending on the access path, and that administrators configure allow list behavior with GitHub App access in mind. IP allow lists restrict access to enterprise/organization resources from non-allowed IPs for web, API, and Git paths as designed. The claim that IP allow lists automatically disable all GitHub Apps enterprise-wide with no exceptions possible is false: Apps are not universally hard-disabled with zero configuration options; enterprises plan allow lists and app installation policies together. The claim that IP allow lists only filter email notifications and never affect API or Git access is false: allow lists are access controls for product access, not merely email filters. Test CI egress IPs, third-party SaaS, and GitHub App architectures before enforcing, and maintain an emergency break-glass process.