
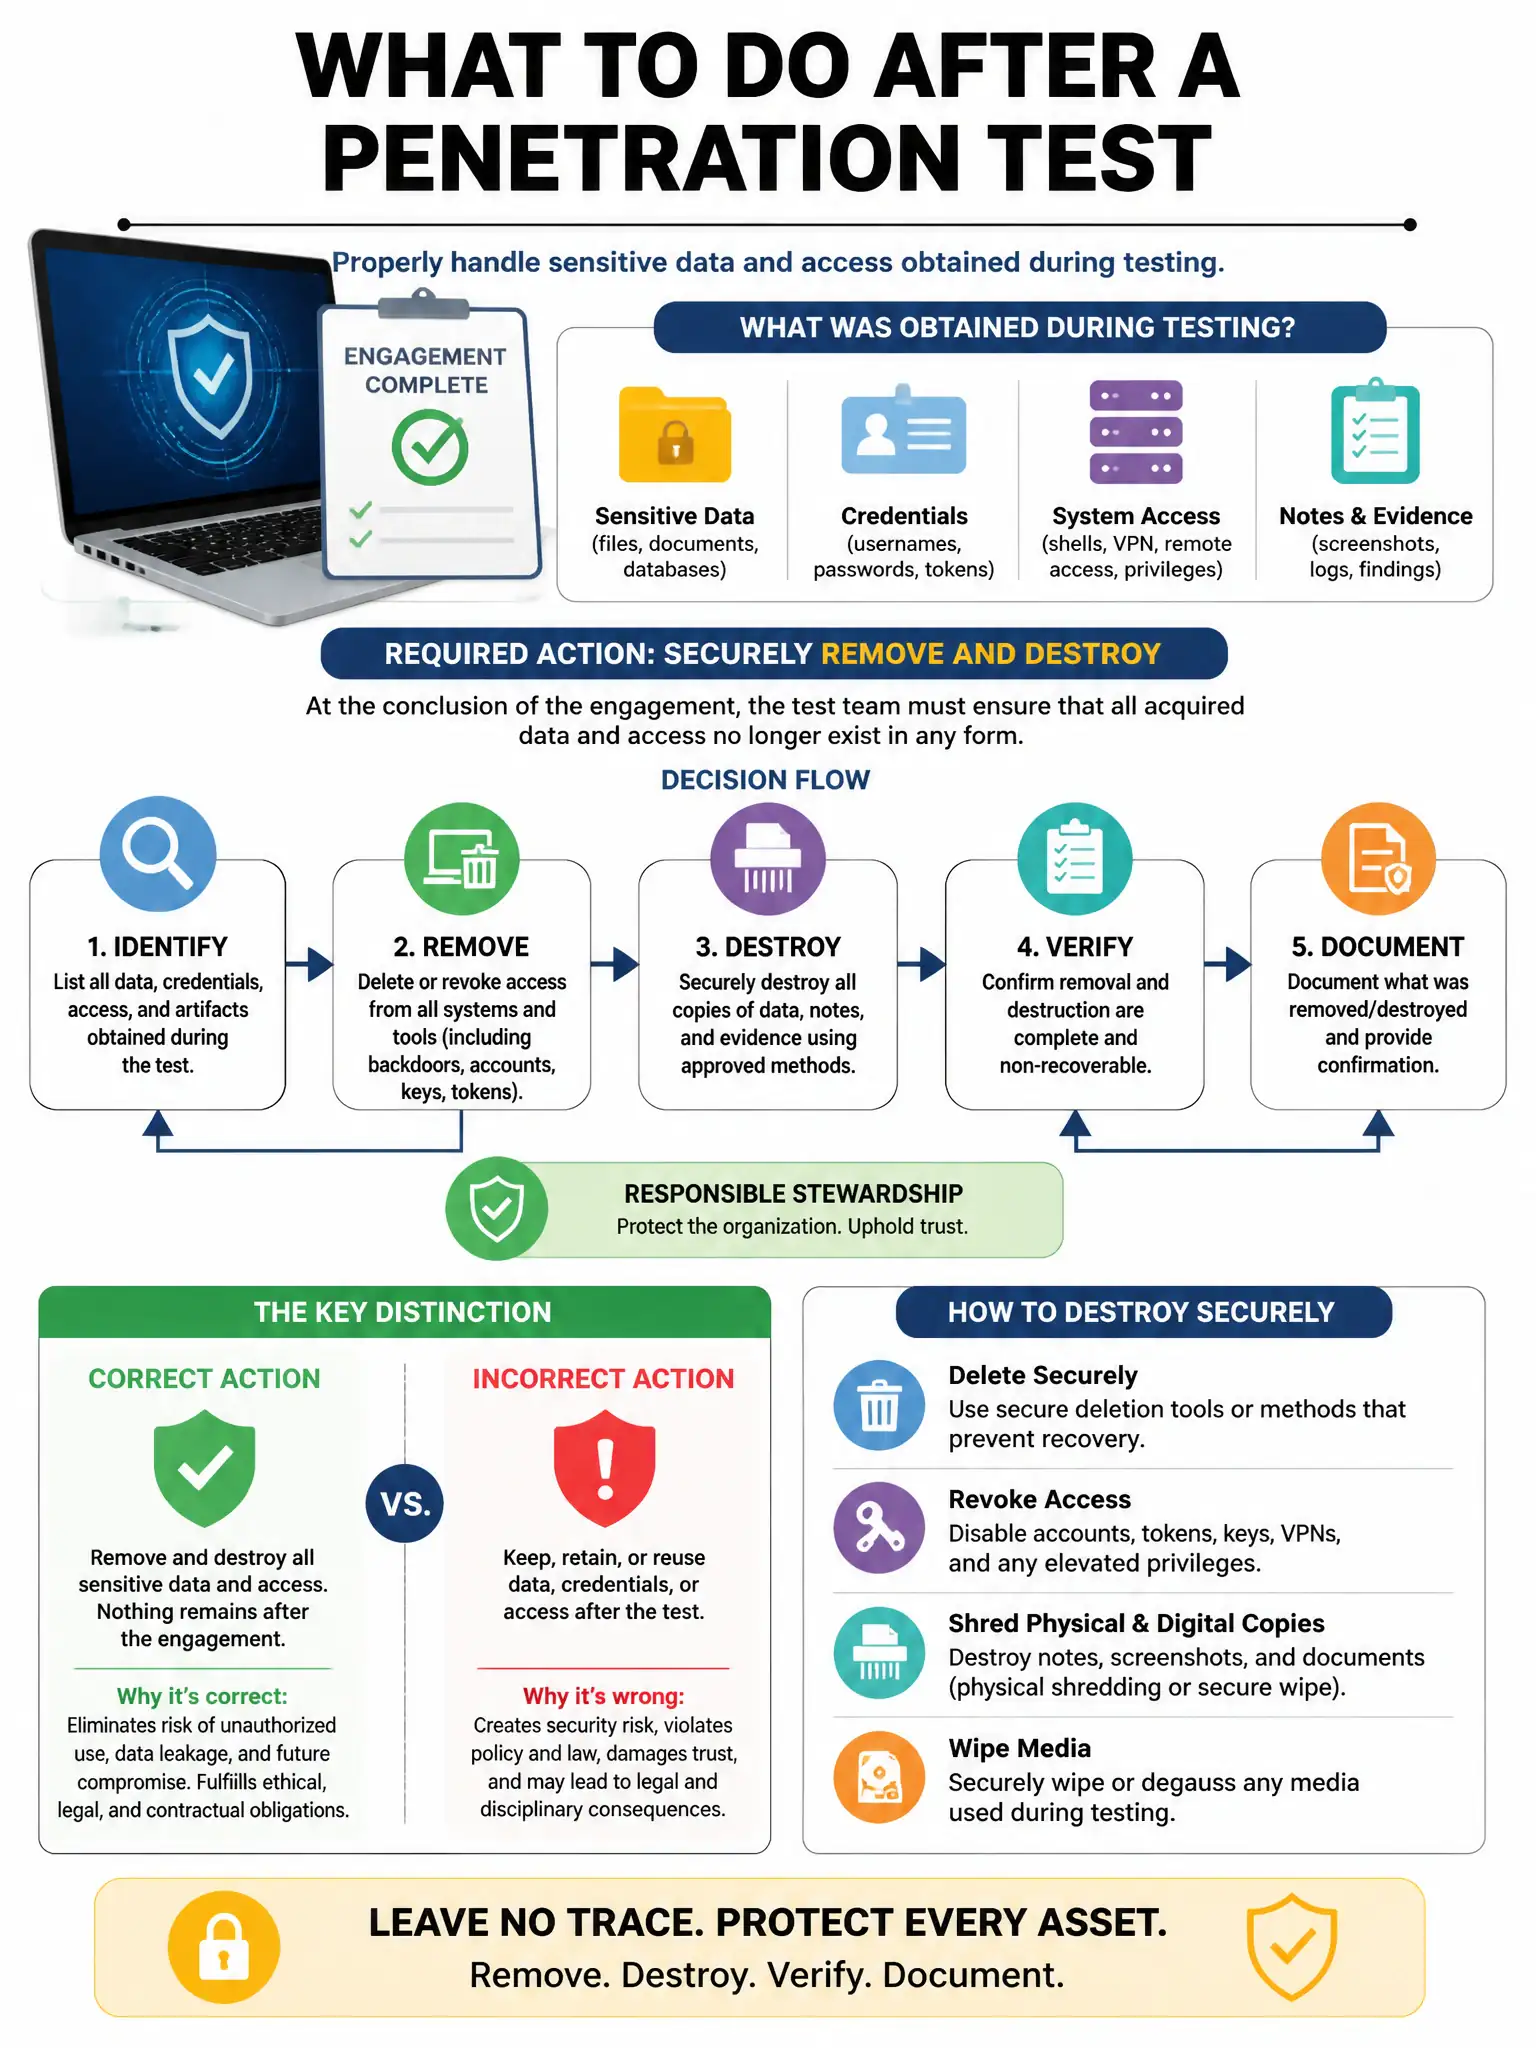
After completing a penetration test, the test team must handle the sensitive data and access obtained during testing. Which action is required at the conclusion of the engagement per professional standards?
Select an answer to reveal the explanation.
Short Explanation
You need to securely destroy all data, credentials, and access obtained during testing according to the cleanup procedures in the Rules of Engagement. That removes test accounts, backdoors, web shells, and client data so no artifacts remain to be exploited or create data protection problems.
Full Explanation
The correct action is to securely destroy all data, credentials, and access obtained during testing according to the cleanup procedures documented in the Rules of Engagement. Professional penetration test engagements require complete cleanup of all access created during testing, including test accounts, backdoors, and web shells, and secure destruction of all client data, including credentials, sensitive files, and network captures, to ensure no test artifacts remain that could be exploited or cause data protection issues. The choice to keep all obtained credentials and data for future reference and comparison with the next test is wrong because retaining client credentials and data beyond the engagement scope violates data protection principles and engagement terms. The choice to transfer all penetration test artifacts to the security team's shared drive for long-term storage is wrong because storing client penetration test data, including credentials, on shared drives creates unnecessary data exposure risk. The choice to publish the findings publicly to improve industry awareness of the organization's vulnerabilities is wrong because publicly disclosing vulnerabilities without client consent violates professional ethics, contractual obligations, and responsible disclosure principles.