
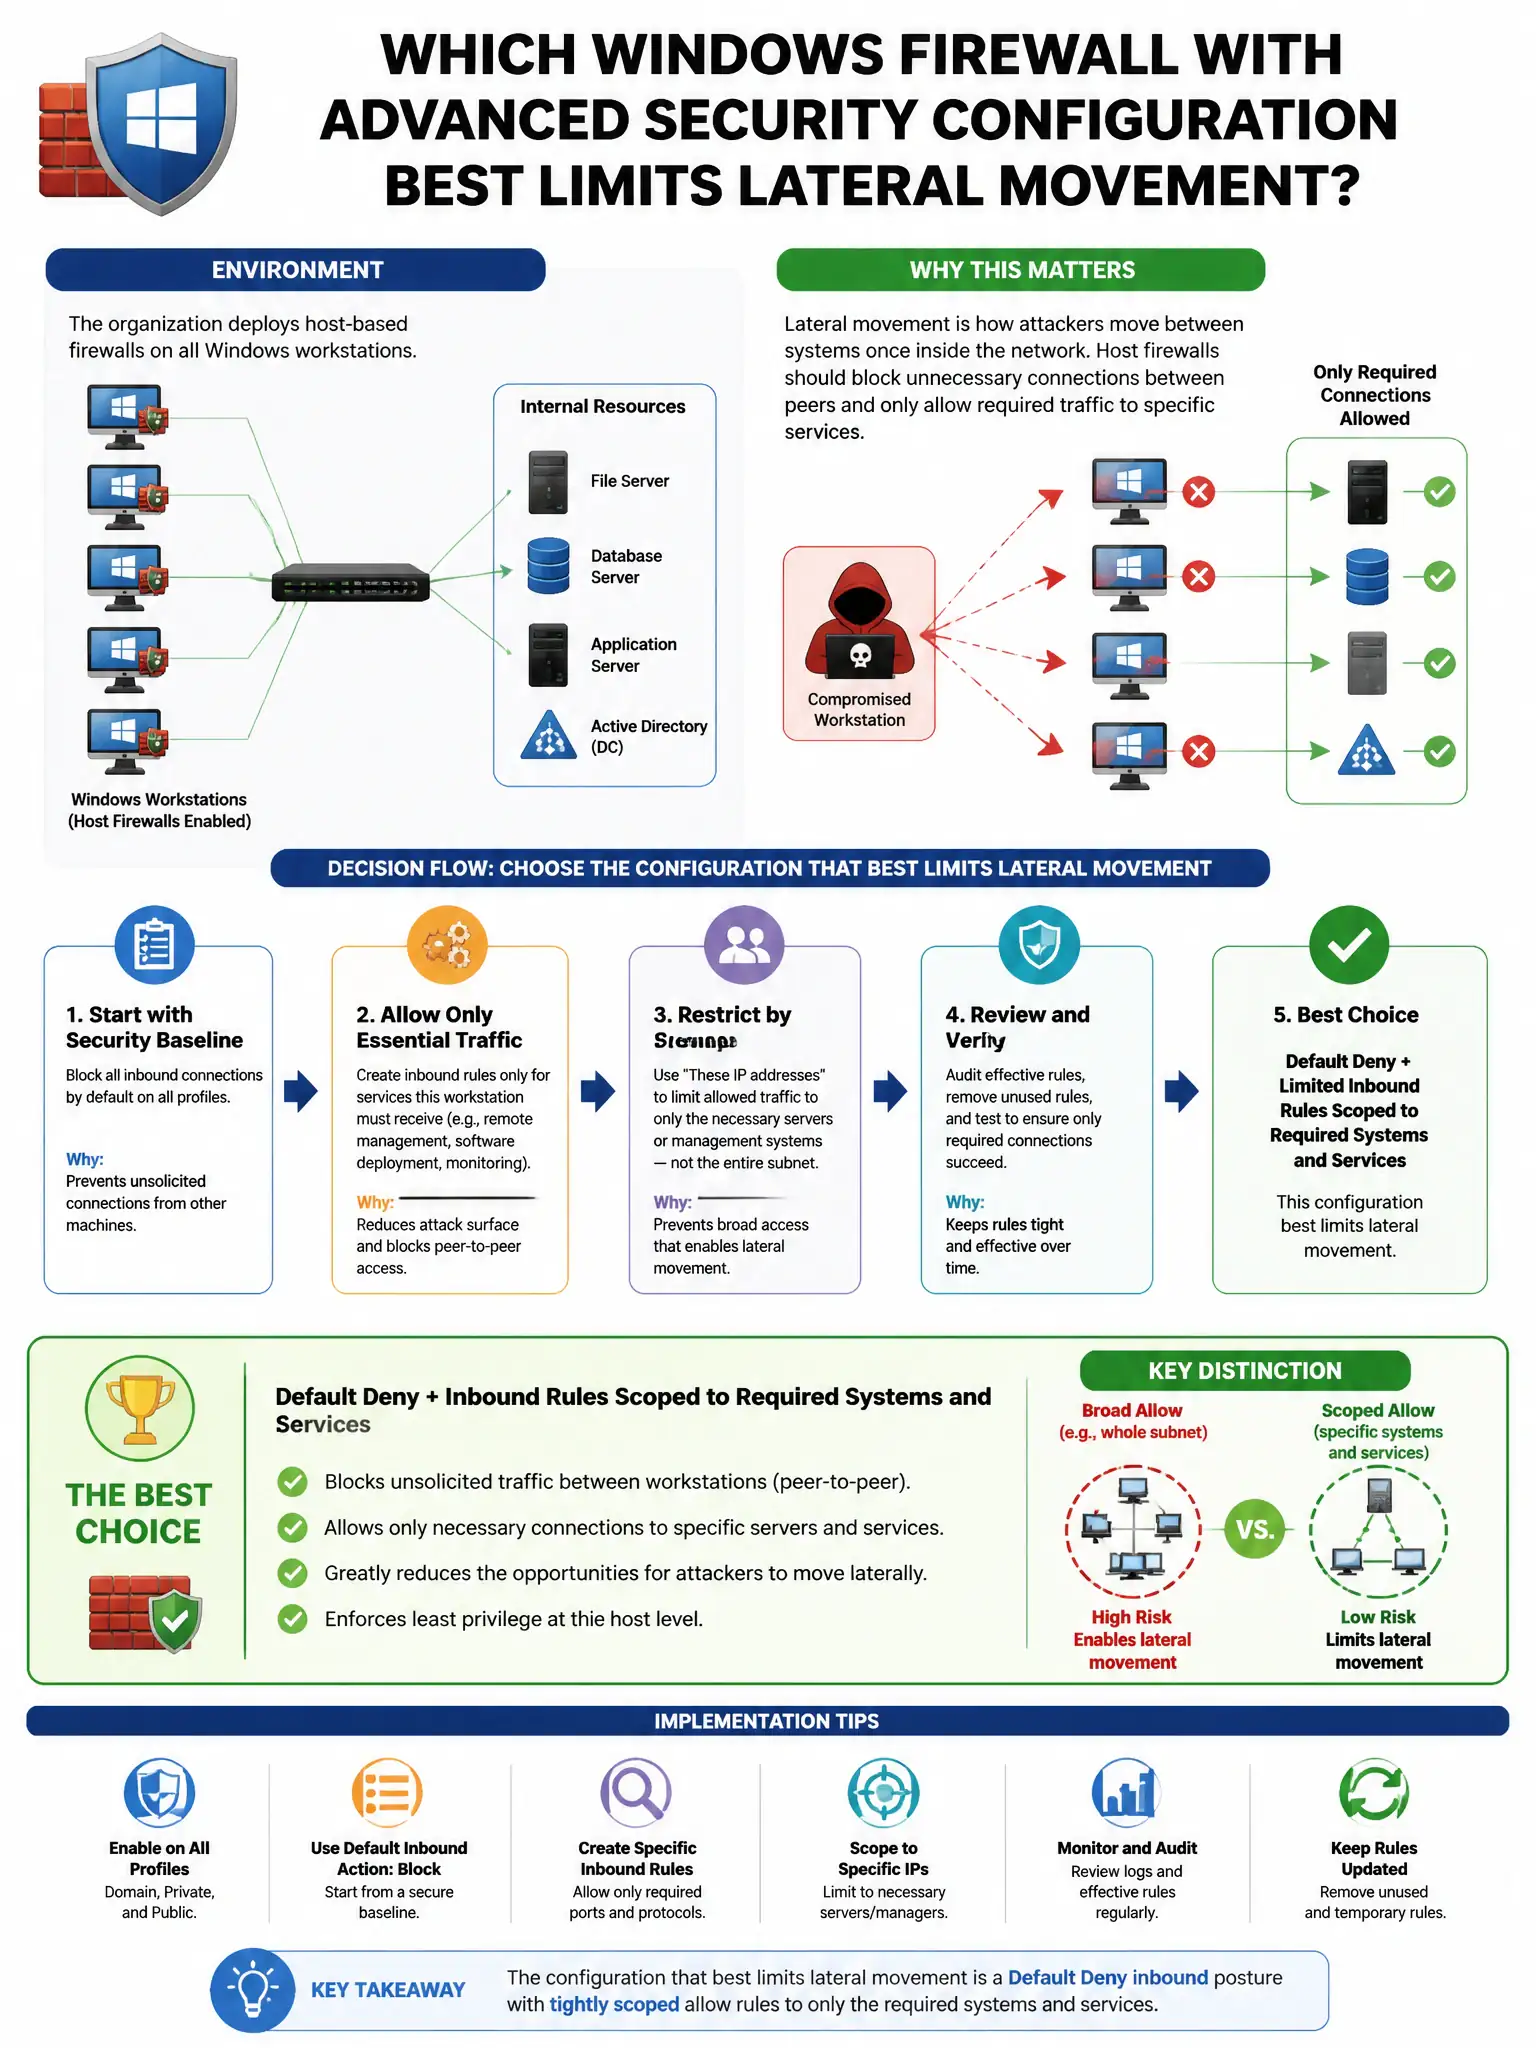
An organization deploys host-based firewalls on all Windows workstations. Which Windows Firewall with Advanced Security configuration best limits lateral movement?
Select an answer to reveal the explanation.
Short Explanation
You block inbound connections from other internal workstations, allow inbound only from management systems and servers, and permit outbound traffic to approved services. That stops peer-to-peer lateral movement like SMB spreading, WMI execution, and RDP, and enforces least-privilege networking at the host level.
Full Explanation
The configuration that blocks all inbound connections from other internal workstations, allows inbound only from management systems and servers, and permits outbound traffic only to approved services is best because it prevents peer-to-peer lateral movement techniques such as SMB spreading, WMI execution, and RDP. It also enforces least-privilege networking at the host level by limiting which internal systems can reach each workstation and which external or internal services the workstation can reach. Allowing all inbound and outbound traffic to simplify management is wrong because it eliminates the security benefit of host-based firewalls. Disabling the host firewall and relying entirely on the network perimeter firewall is wrong because perimeter controls fail once the perimeter is bypassed; host firewalls are a critical defense-in-depth layer for internal east-west traffic. Blocking only inbound connections from internet IP addresses is wrong because it leaves internal lateral movement pathways fully open.