
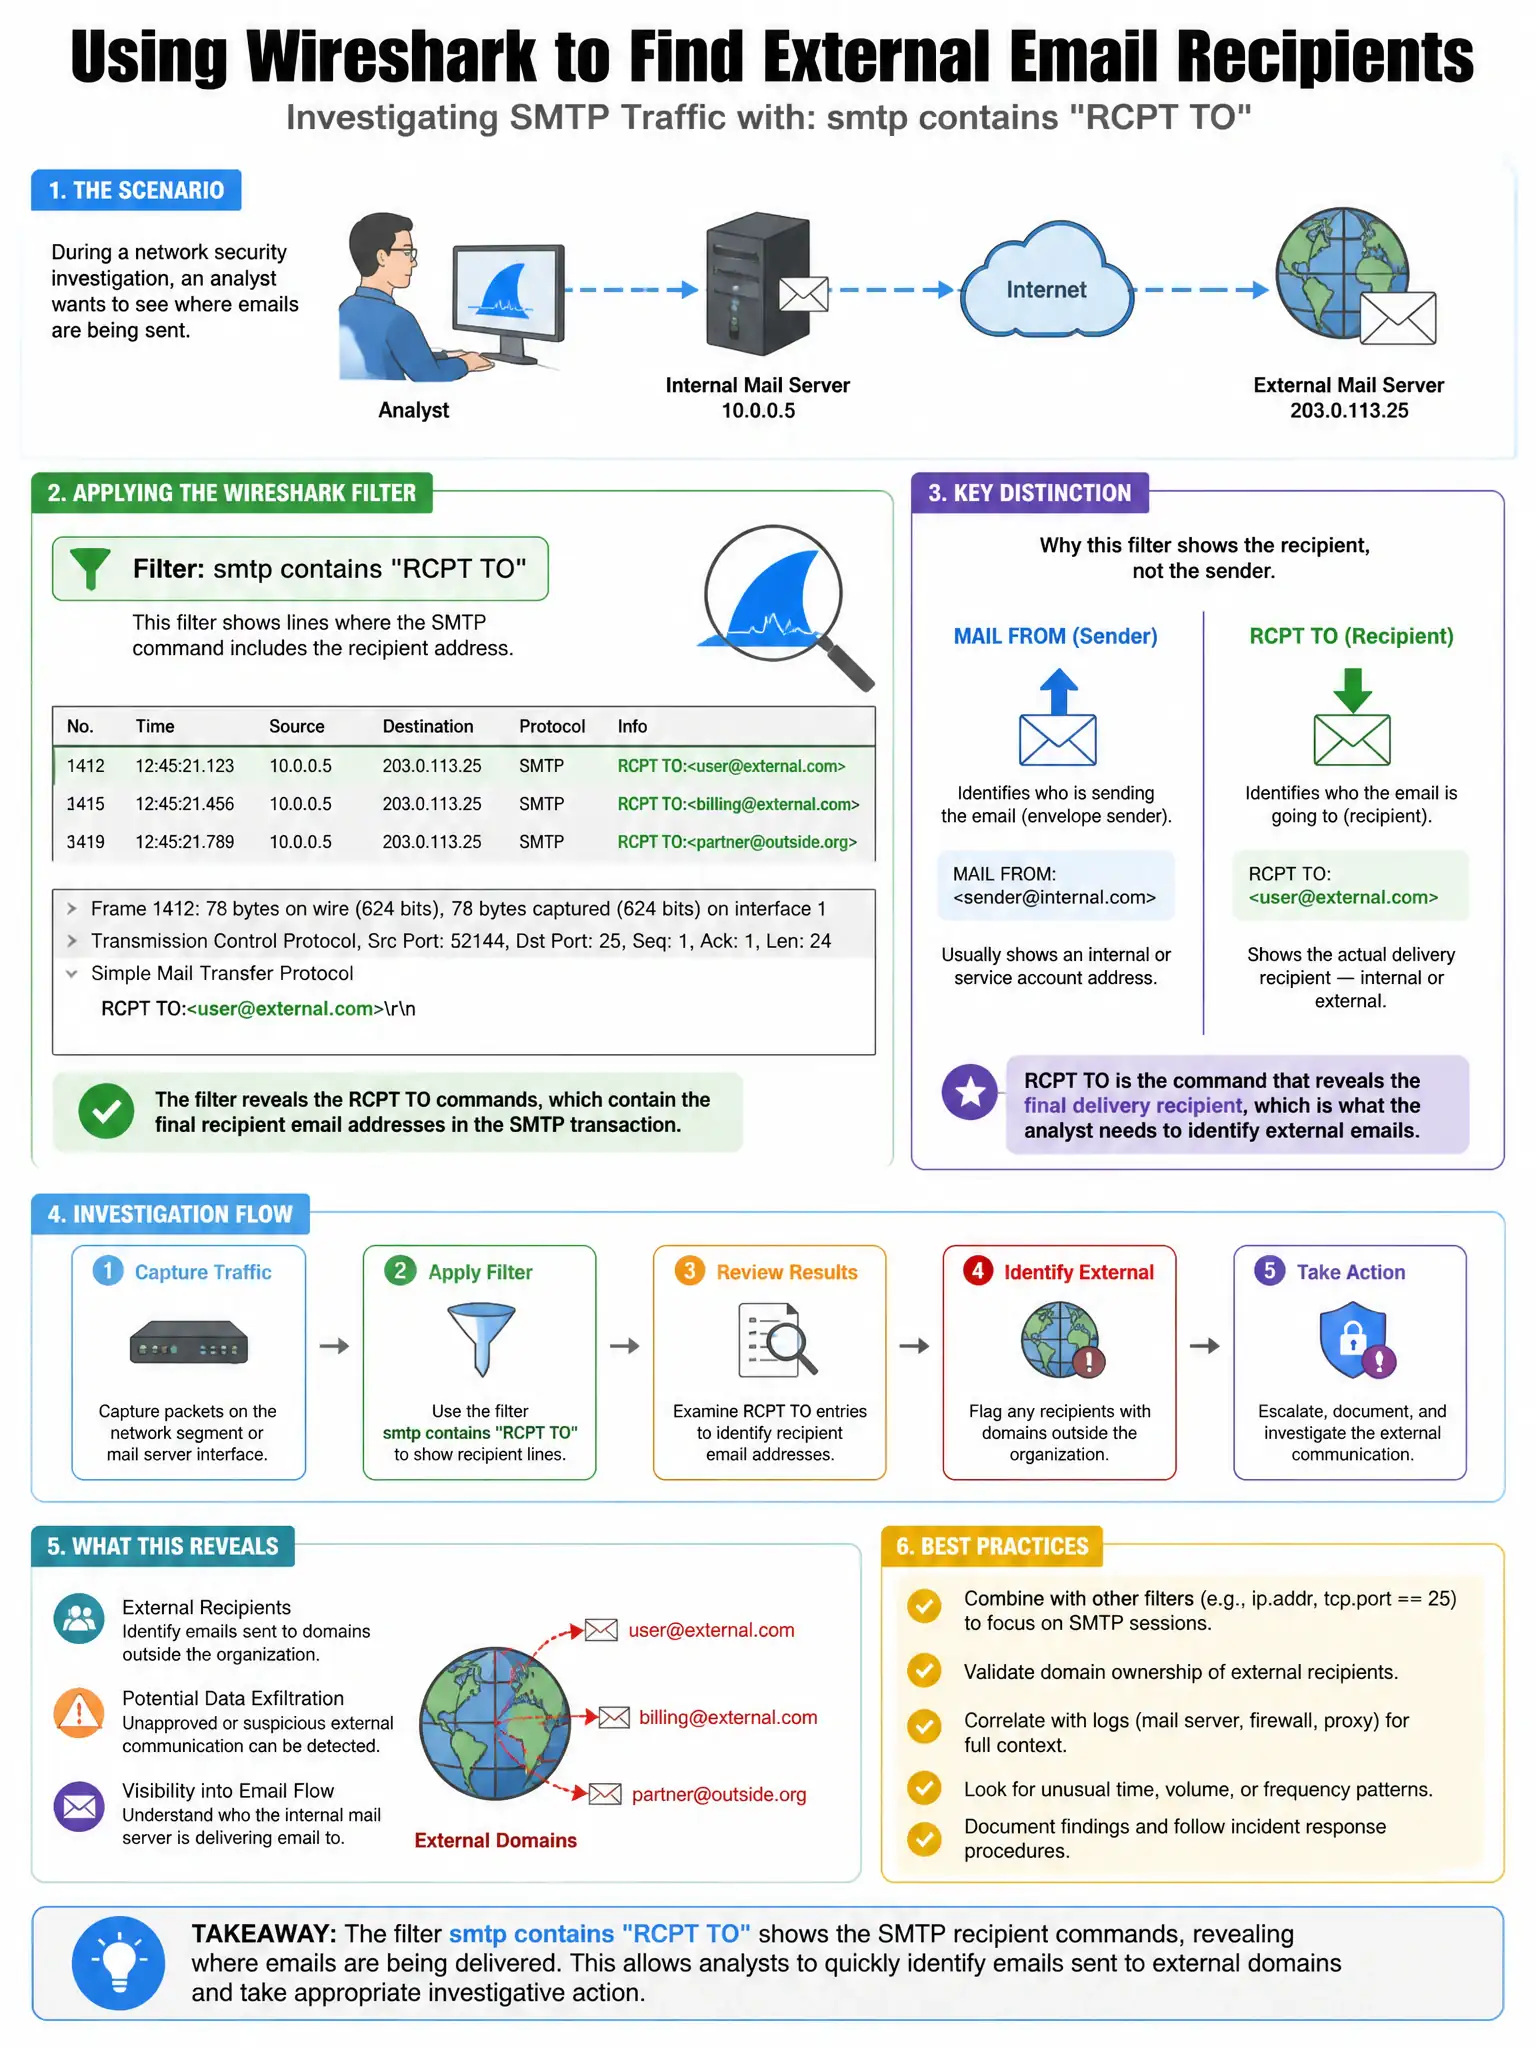
During a network security investigation, an analyst uses the Wireshark filter smtp contains "RCPT TO" to examine email traffic. The analyst finds emails being sent to an external domain with 15 distinct recipients. What should the analyst investigate further?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to check whether an authorized mail gateway sent the messages or a workstation hit an external SMTP server directly. A workstation blasting to 15 external recipients is a red flag for spam-sending malware, phishing, or data exfiltration.
Full Explanation
The correct answer is the option that asks whether the emails were sent by an authorized mail server or by a workstation directly contacting an external SMTP server, because legitimate enterprise email flows through configured mail gateways. A workstation directly connecting to an external SMTP server and sending to many recipients indicates malware using the system as a spam relay, phishing sender, or using email for data exfiltration. The option saying nothing is wrong because the sending source matters; a mail server sending to 15 recipients is normal, but a workstation doing so is anomalous. The option asking whether the recipients are in the corporate global address list is wrong because recipient list membership doesn't address the suspicious sending behavior. The option asking whether TLS encryption was used for the SMTP session is wrong because while TLS encryption is a security concern for eavesdropping, the primary investigative concern is the unauthorized direct SMTP connection from a workstation.