
A penetration tester performs an nmap scan and uses -sV --script=banner flags. What information do these flags collect?
Select an answer to reveal the explanation.
Short Explanation
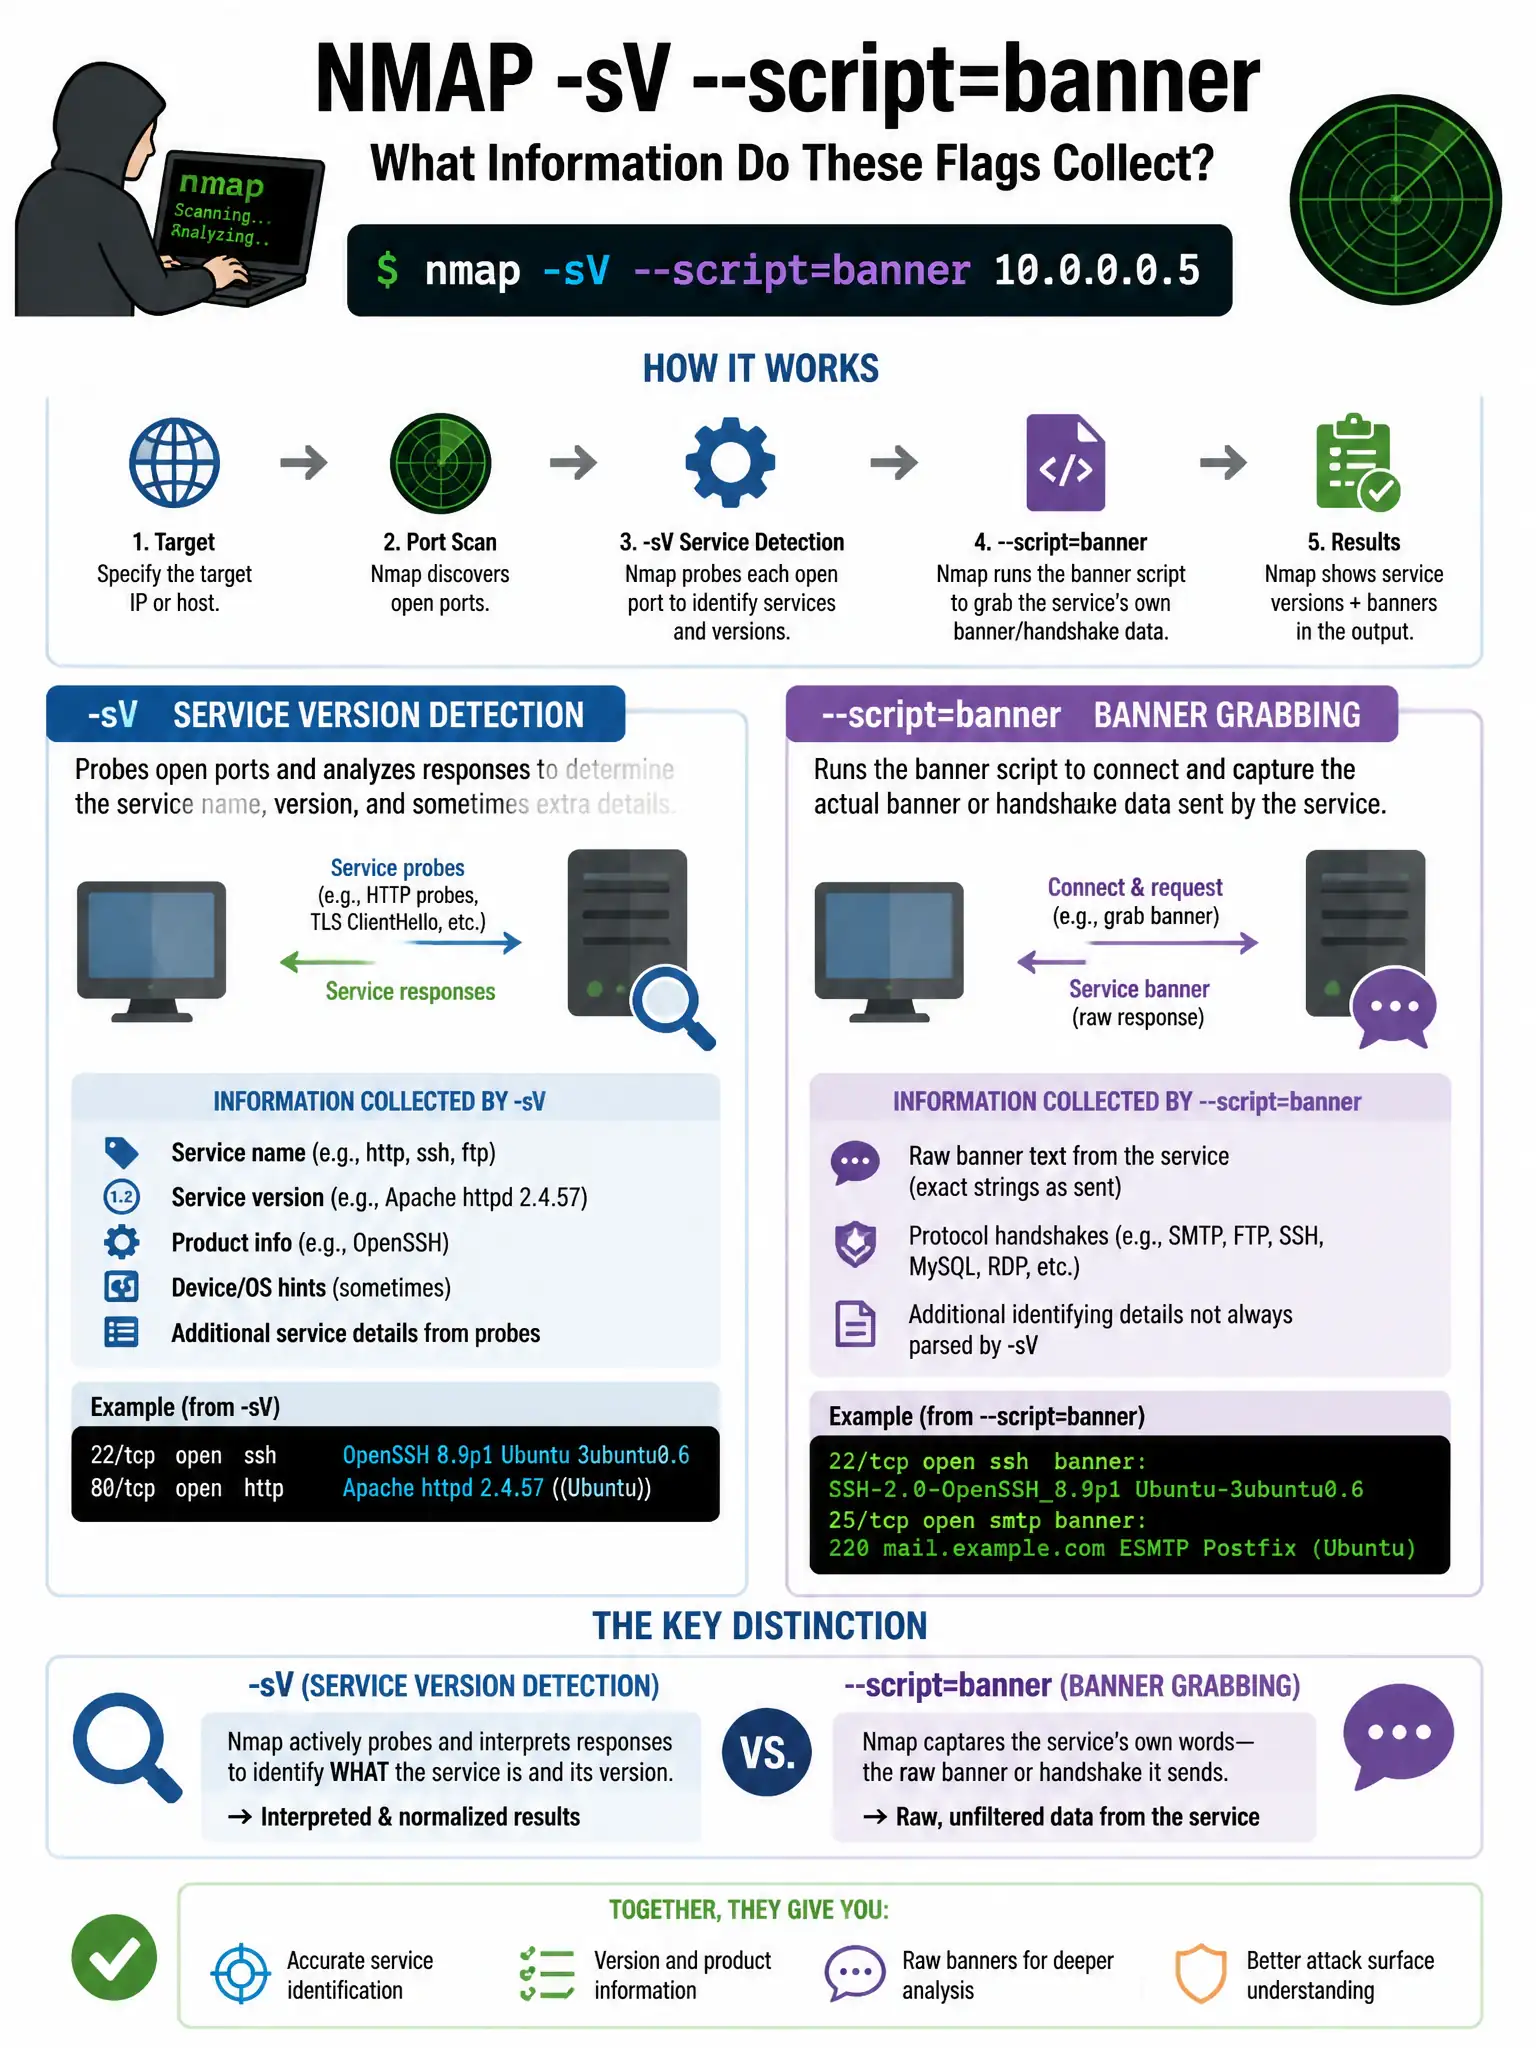
Here's the deal — you're getting service version detection and banner grabbing. -sV probes open ports to identify software versions, and --script=banner captures raw service banners, giving you names, versions, and config details for spotting exploitable vulnerabilities.
Full Explanation
The option describing -sV probing services for version information and --script=banner capturing service banners is correct. -sV sends probes to open ports to identify software versions, while the banner NSE script collects raw service banners, revealing names, versions, and configuration details useful for identifying known CVEs and exploitable vulnerabilities. The UDP port scan with OS fingerprinting option is wrong because UDP scanning uses -sU and OS fingerprinting uses -O. The stealth SYN scan while completely hiding the scanner's identity option is wrong because -sS is the stealth SYN scan flag; -sV detects versions and does not specifically hide the scanner. The OWASP web application vulnerability scan option is wrong because nmap does not implement OWASP's web testing methodology; web application testing requires purpose-built tools like Burp Suite.