
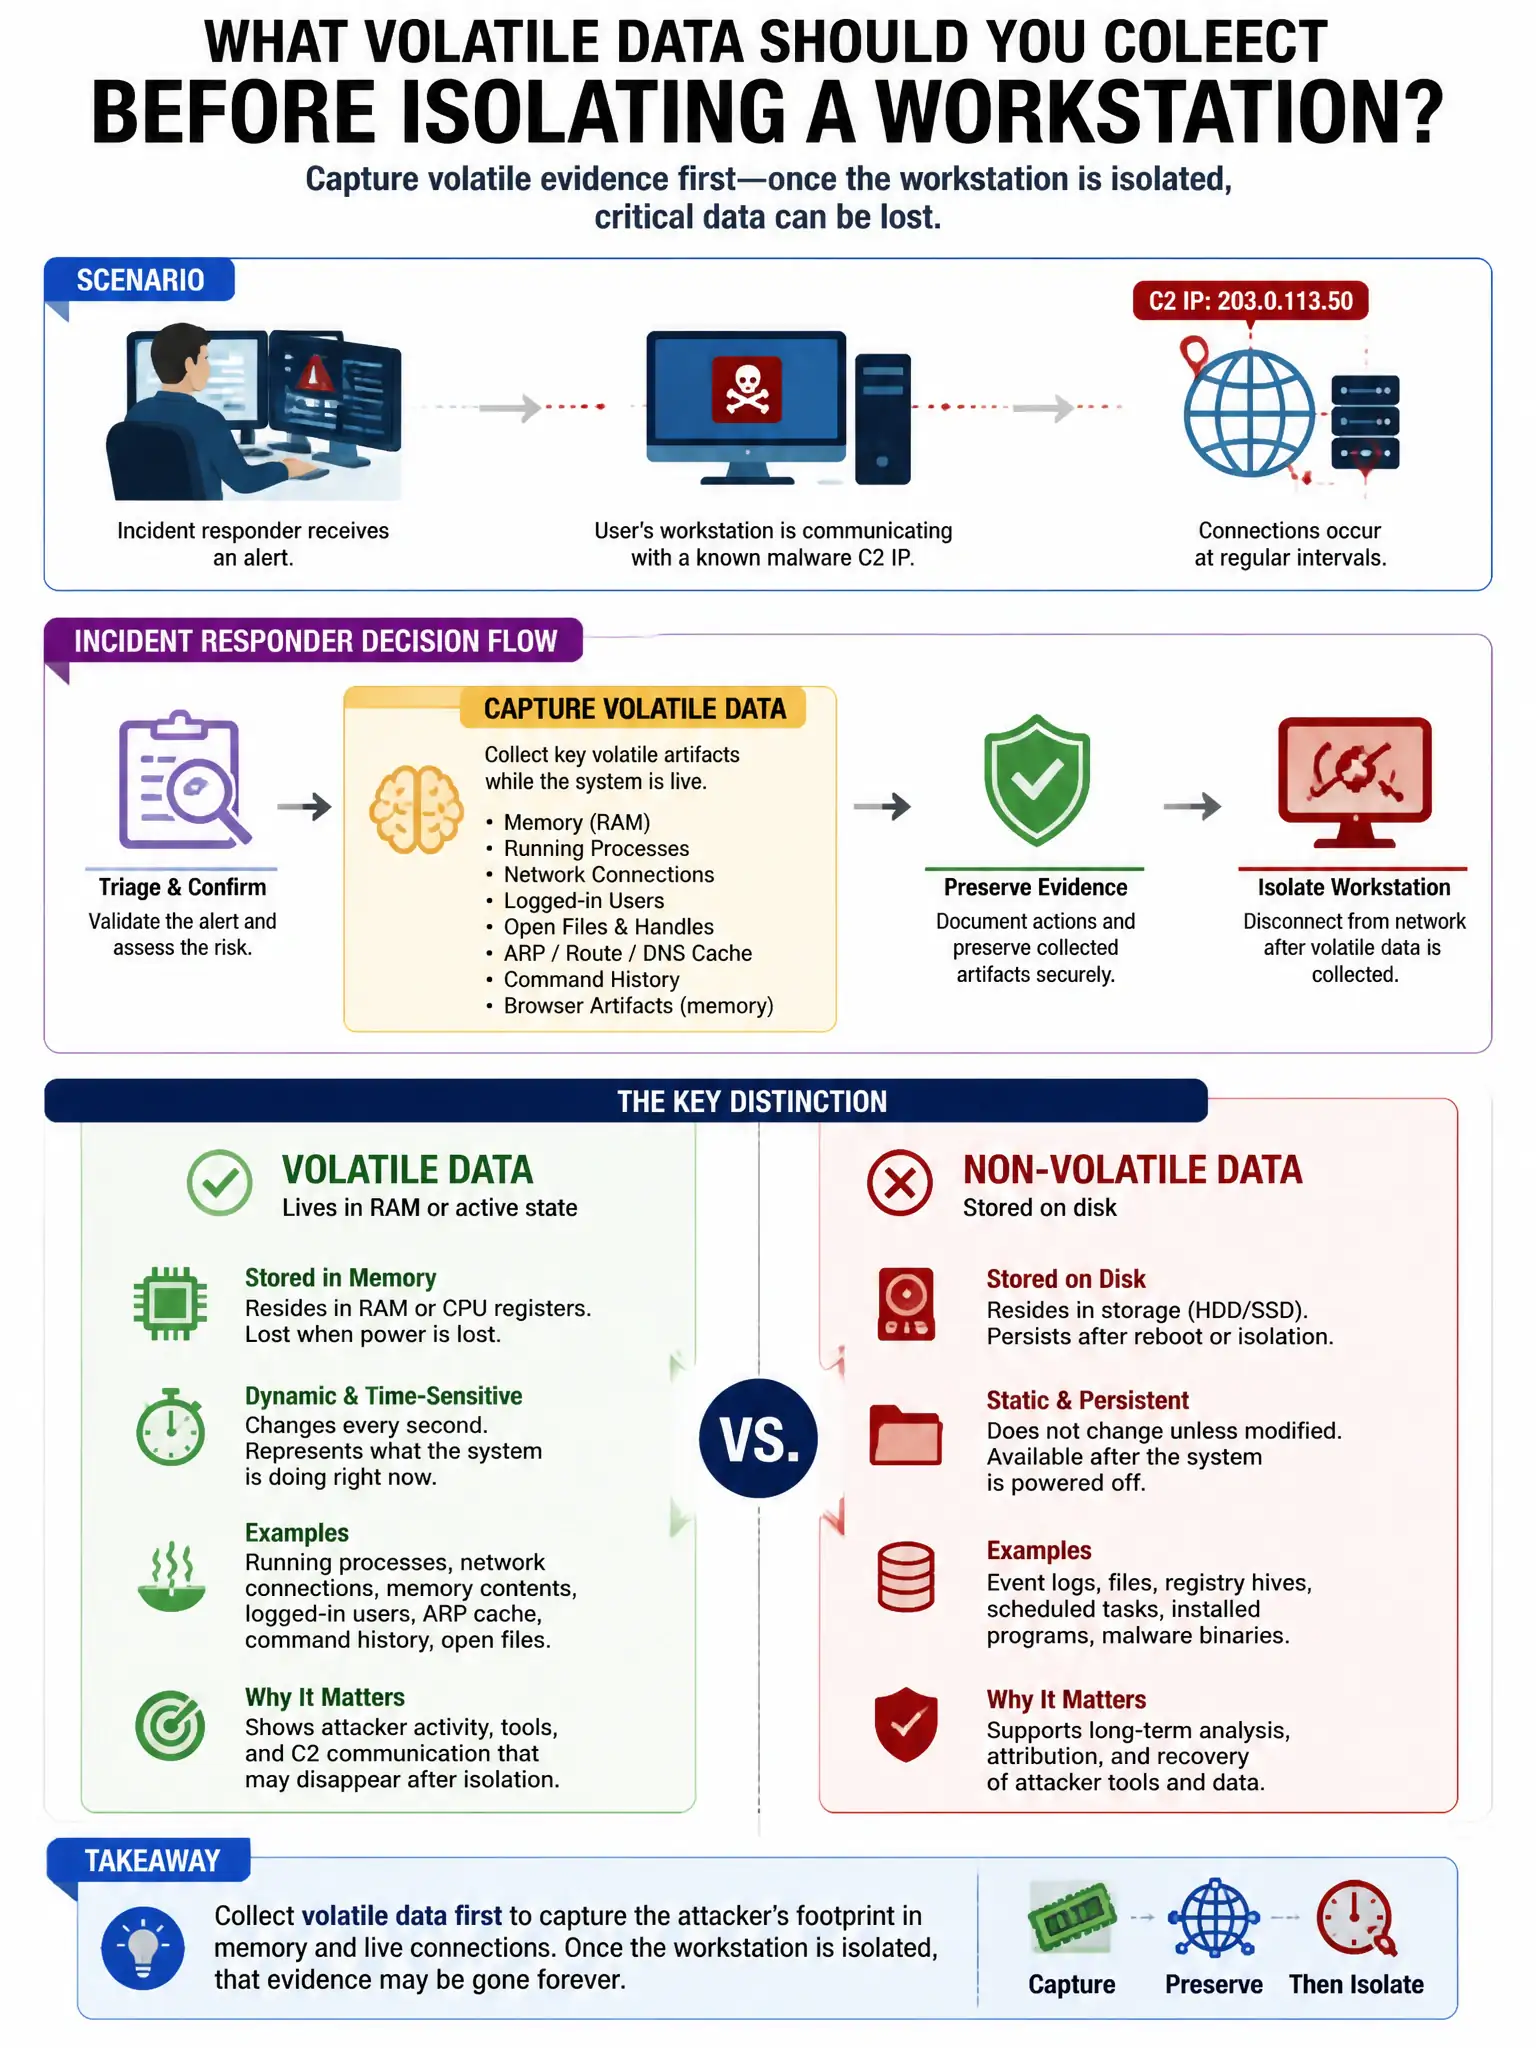
An incident responder receives a report that a user's workstation is communicating with a known malware C2 IP at regular intervals. Before isolating the workstation, what volatile data should be collected first?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — collect the running process list, network connections, logged-in users, and system memory first because that volatile data disappears when you shut down or isolate the workstation. You need it before containment changes the running state.
Full Explanation
The running process list, network connections, logged-in users, and system memory are correct because volatile data is lost when a system is shut down or isolated; this data must be collected before containment actions that disrupt the system's running state. The hard drive image to preserve all files is wrong because disk images can be collected after isolation; they are non-volatile and do not require urgent collection before containment. The Windows Event Log files are wrong because event log files are non-volatile, stored on disk, and can be collected after isolation; they are not the priority volatile data. The list of installed software from the Programs and Features control panel is wrong because installed software lists are available from the registry and file system at any time; they are not volatile data.