
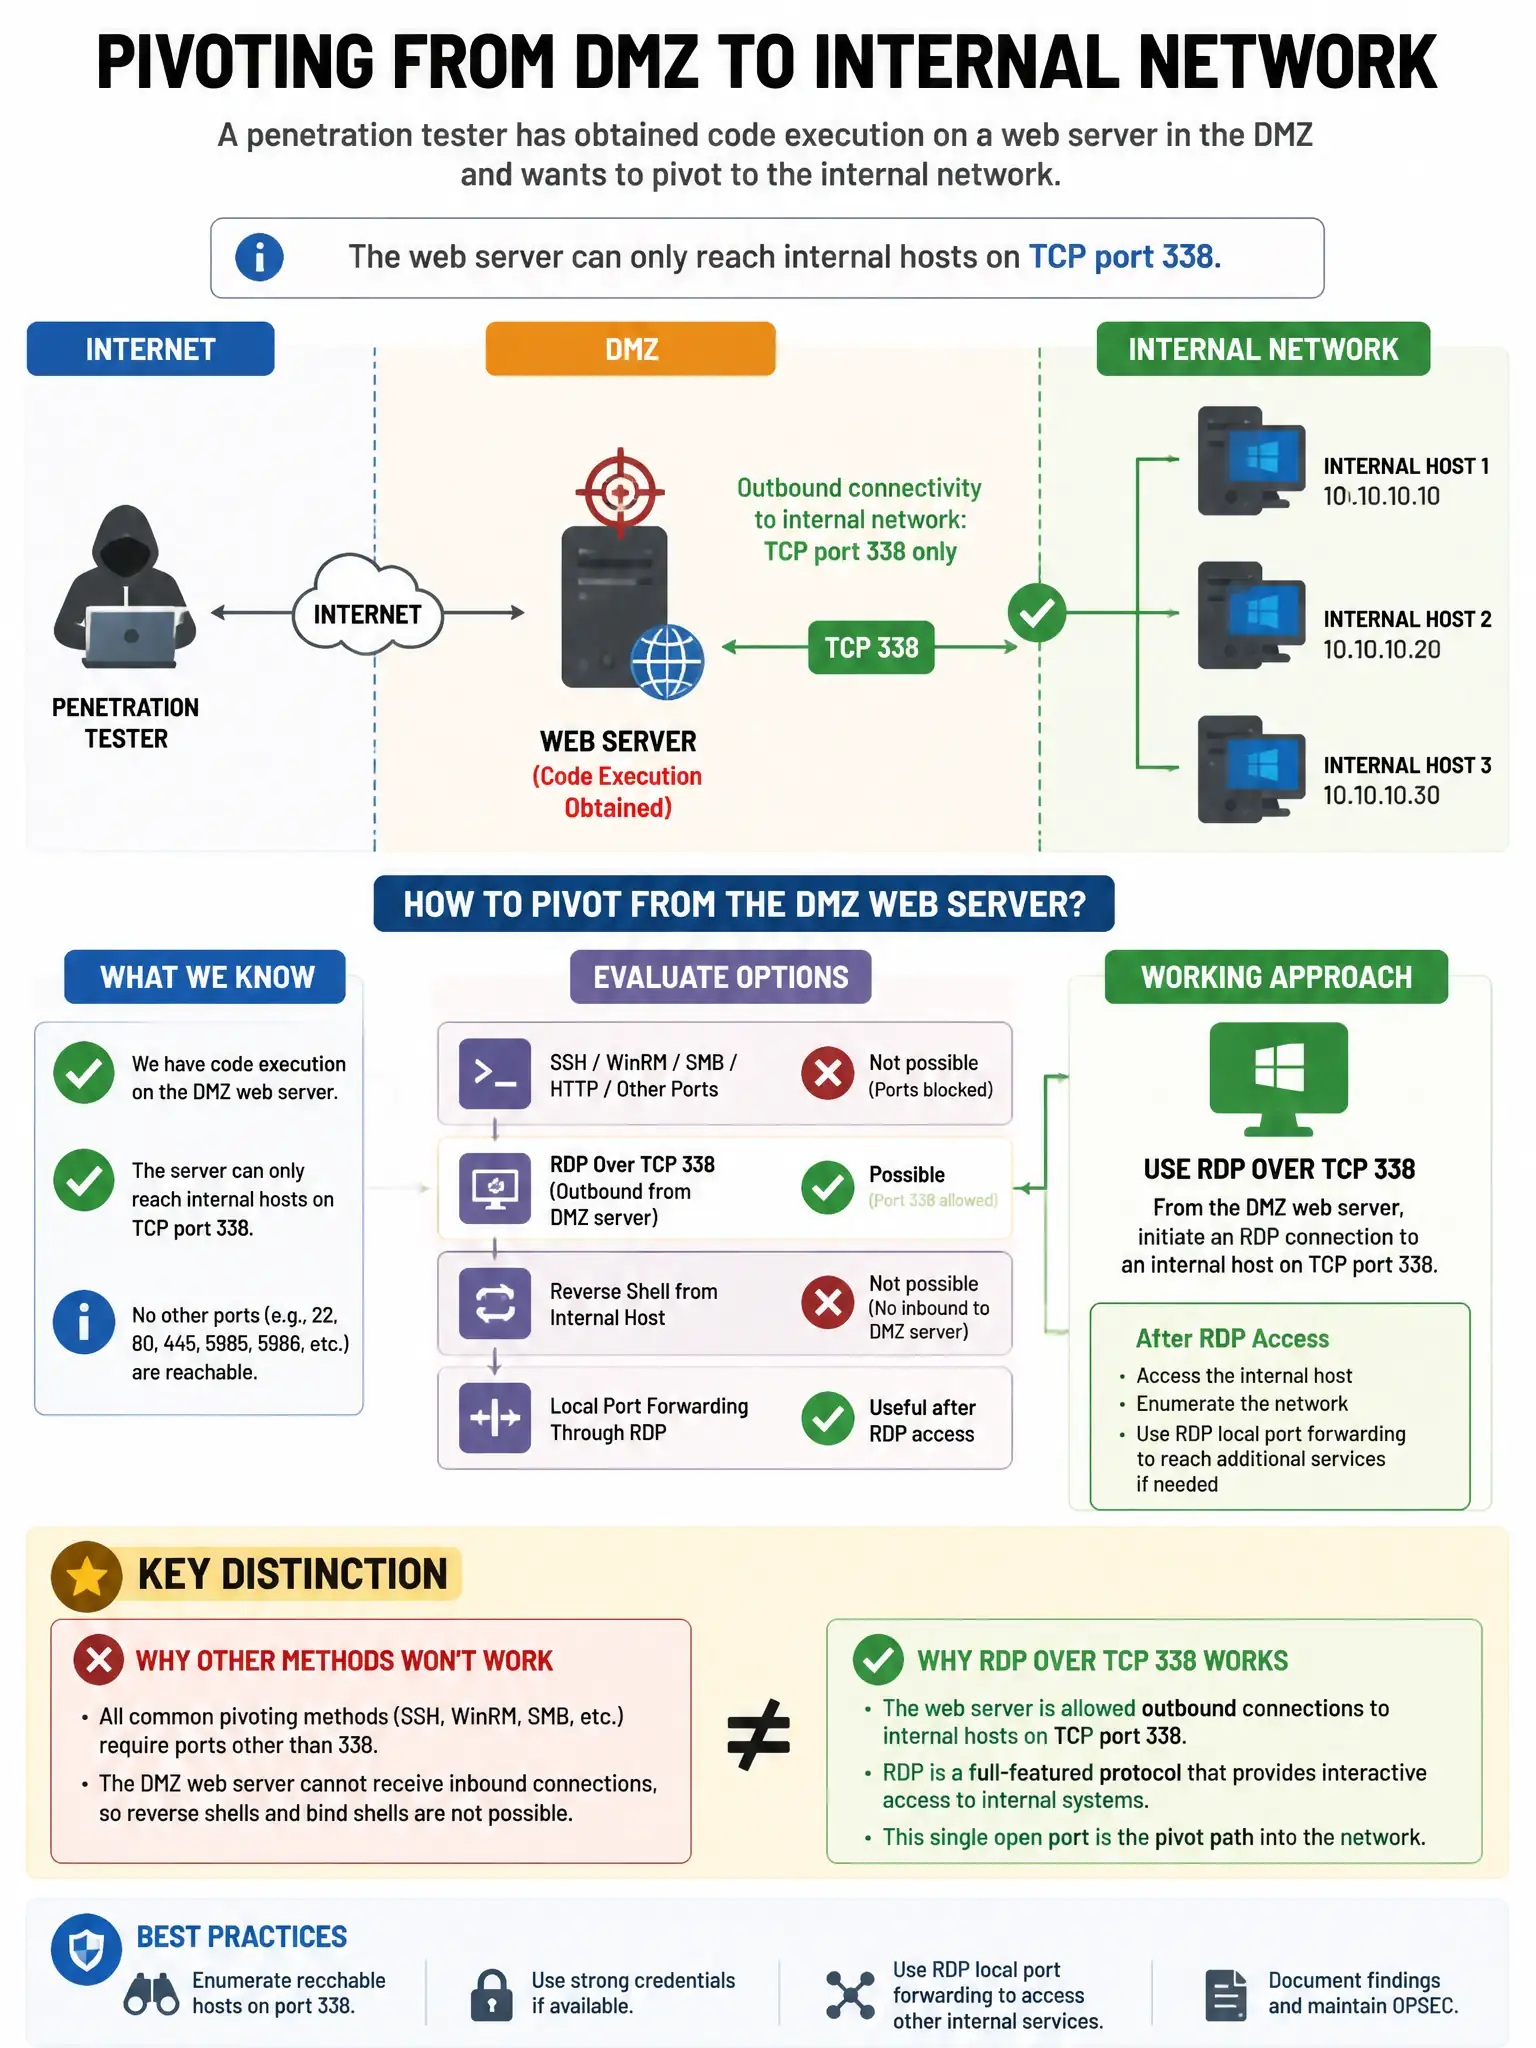
A penetration tester has obtained code execution on a web server in the DMZ and wants to pivot to the internal network. The web server can only reach internal hosts on TCP port 3389. Which technique allows the tester to pivot through this connection?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal: you need a SOCKS proxy or port-forward tunnel through the compromised web server because it routes your attacker traffic to internal hosts over the only allowed path, TCP 3389. That pivots through the network boundary.
Full Explanation
Setting up a SOCKS proxy or port-forward tunnel through the compromised web server is correct because it allows the attacker to route traffic from their attack system to internal hosts via the web server's allowed outbound connection on TCP 3389, effectively pivoting through the network boundary. Exploiting the RDP service on internal hosts using the EternalBlue vulnerability is wrong because EternalBlue exploits SMB (TCP 445), not RDP (TCP 3389), and the web server can only reach internal hosts on 3389. Using ARP spoofing to redirect internal traffic through the compromised server is wrong because ARP spoofing affects traffic within the same Layer 2 segment and would not help pivot from the DMZ to the internal network. Deploying a reverse DNS shell through port 53 to bypass the port restriction is wrong because DNS-based techniques use port 53; the constraint is that only port 3389 is allowed, so DNS shells would be blocked.