
An organization wants to ensure that its egress filtering policy prevents data exfiltration. Which egress filtering strategy is most effective?
Select an answer to reveal the explanation.
Short Explanation
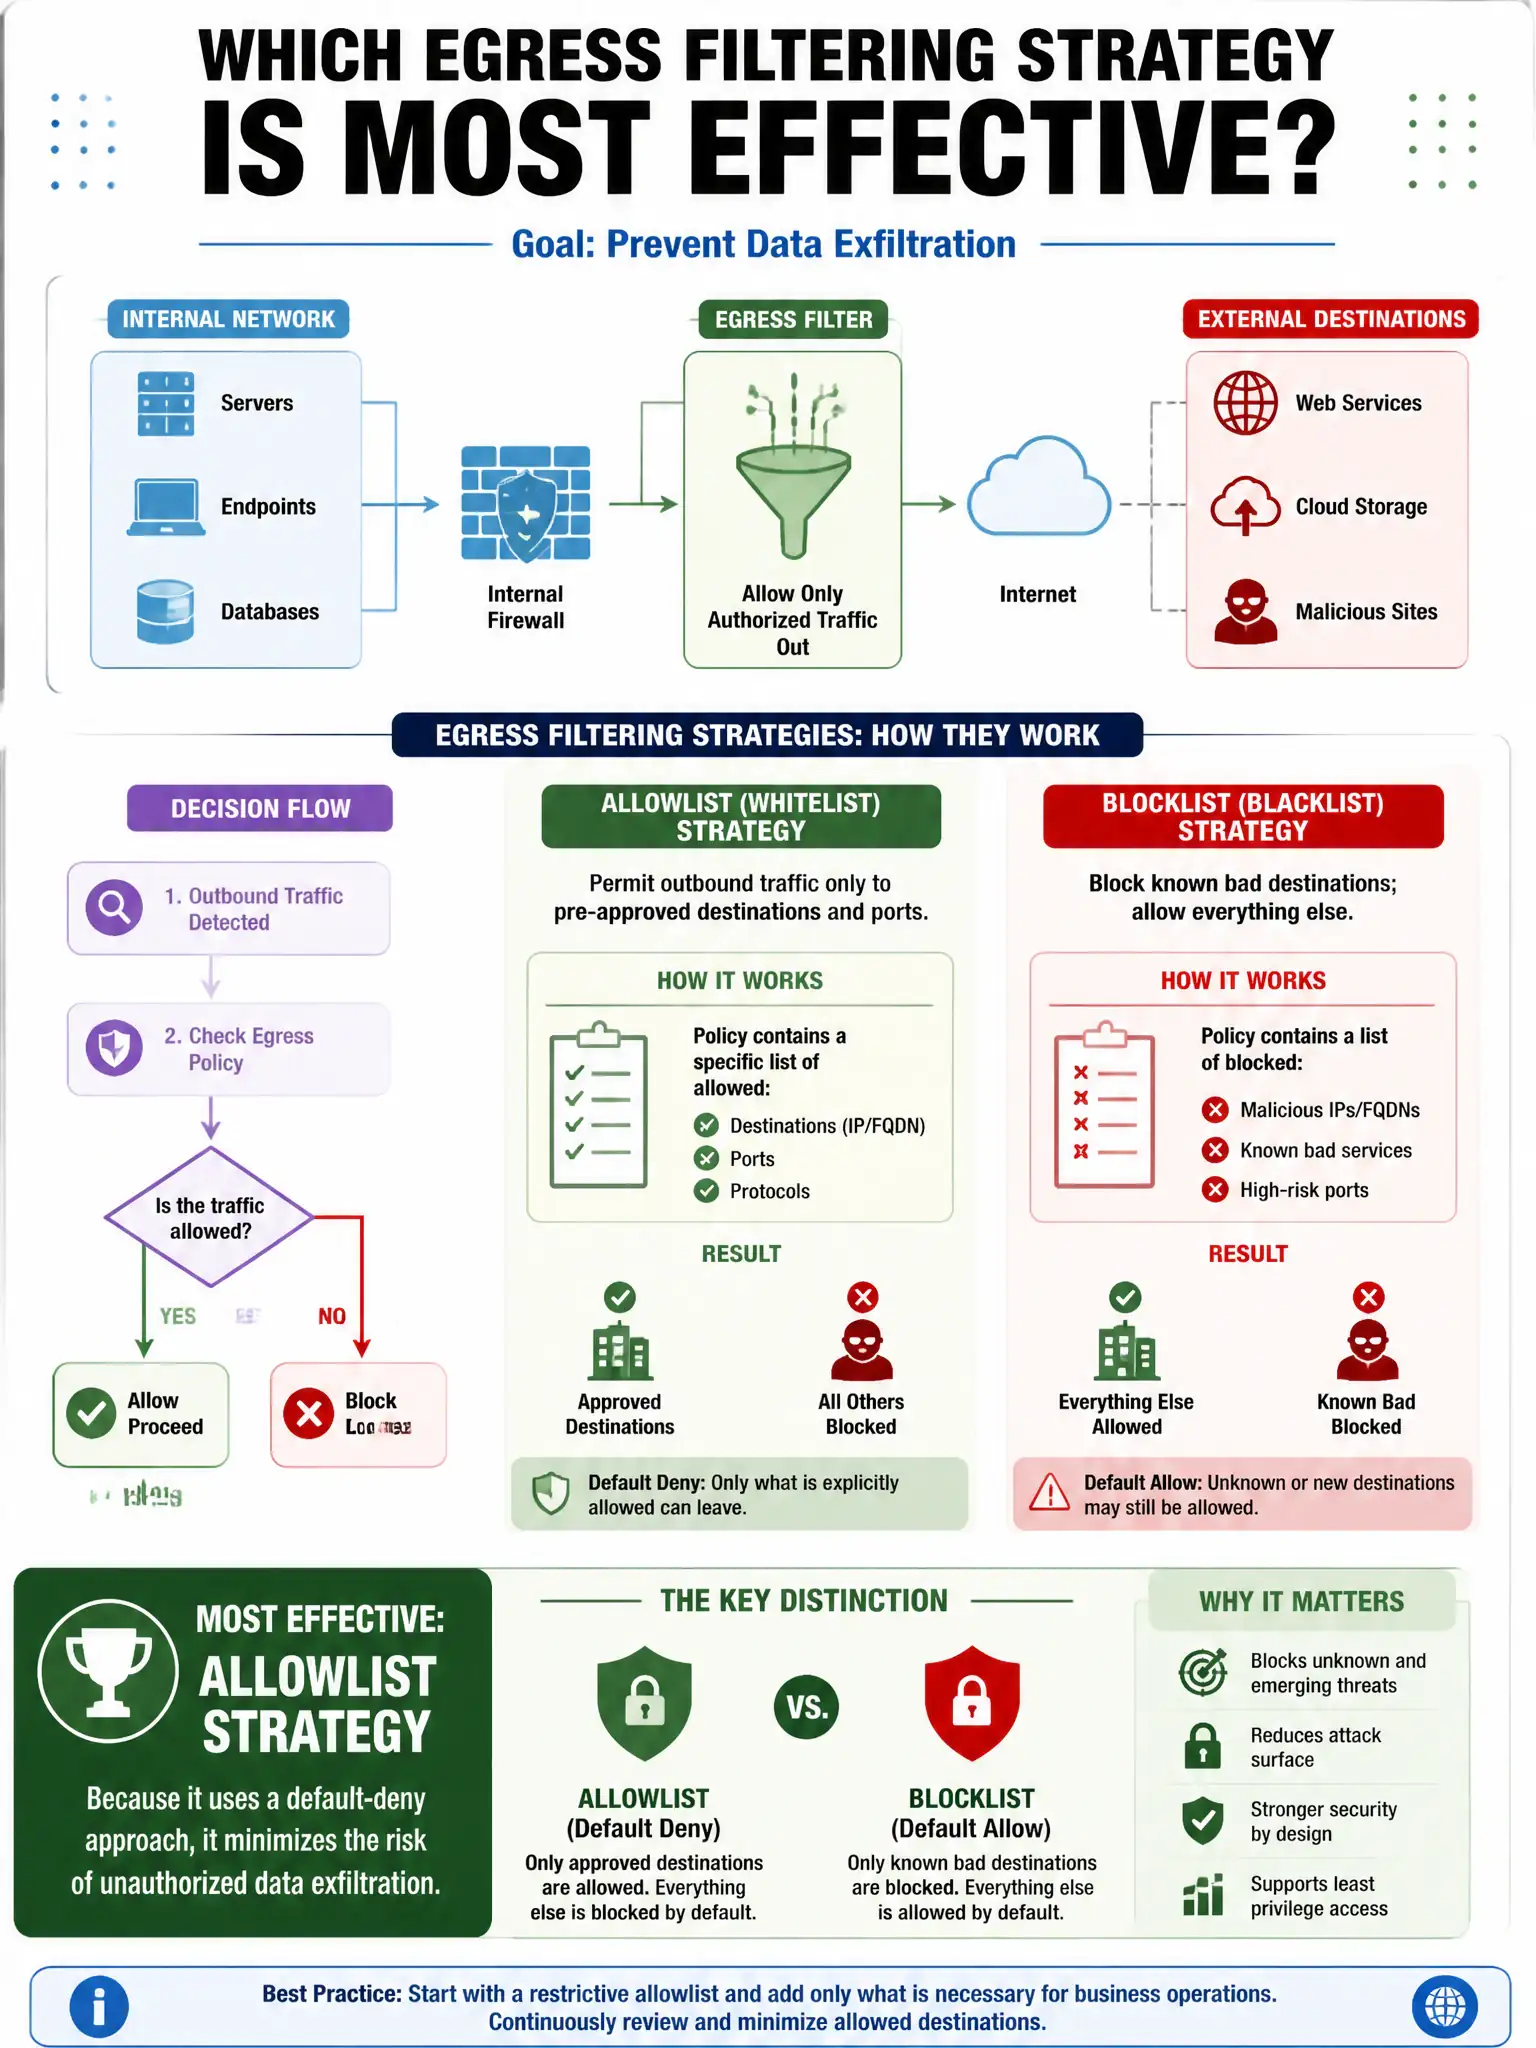
Here's the deal — you want the most effective egress filtering to start with default-deny and only allow the protocols, ports, and destinations your business actually needs. That closes off the unknown channels attackers use to sneak data out.
Full Explanation
The most effective strategy is a default-deny egress policy that allows only explicitly approved protocols, ports, and destinations required for business. This is the most restrictive approach because it limits exfiltration channels to intentionally permitted services. Allowing all outbound traffic except known malicious IP addresses is wrong because it relies on block-listing and fails against unknown attacker infrastructure. Limiting outbound traffic to ports 80 and 443 only is wrong because data can still be sent over HTTP or HTTPS to attacker-controlled servers. Blocking all ICMP outbound traffic is wrong because ping-based exfiltration is rare and attackers have many other channels.