
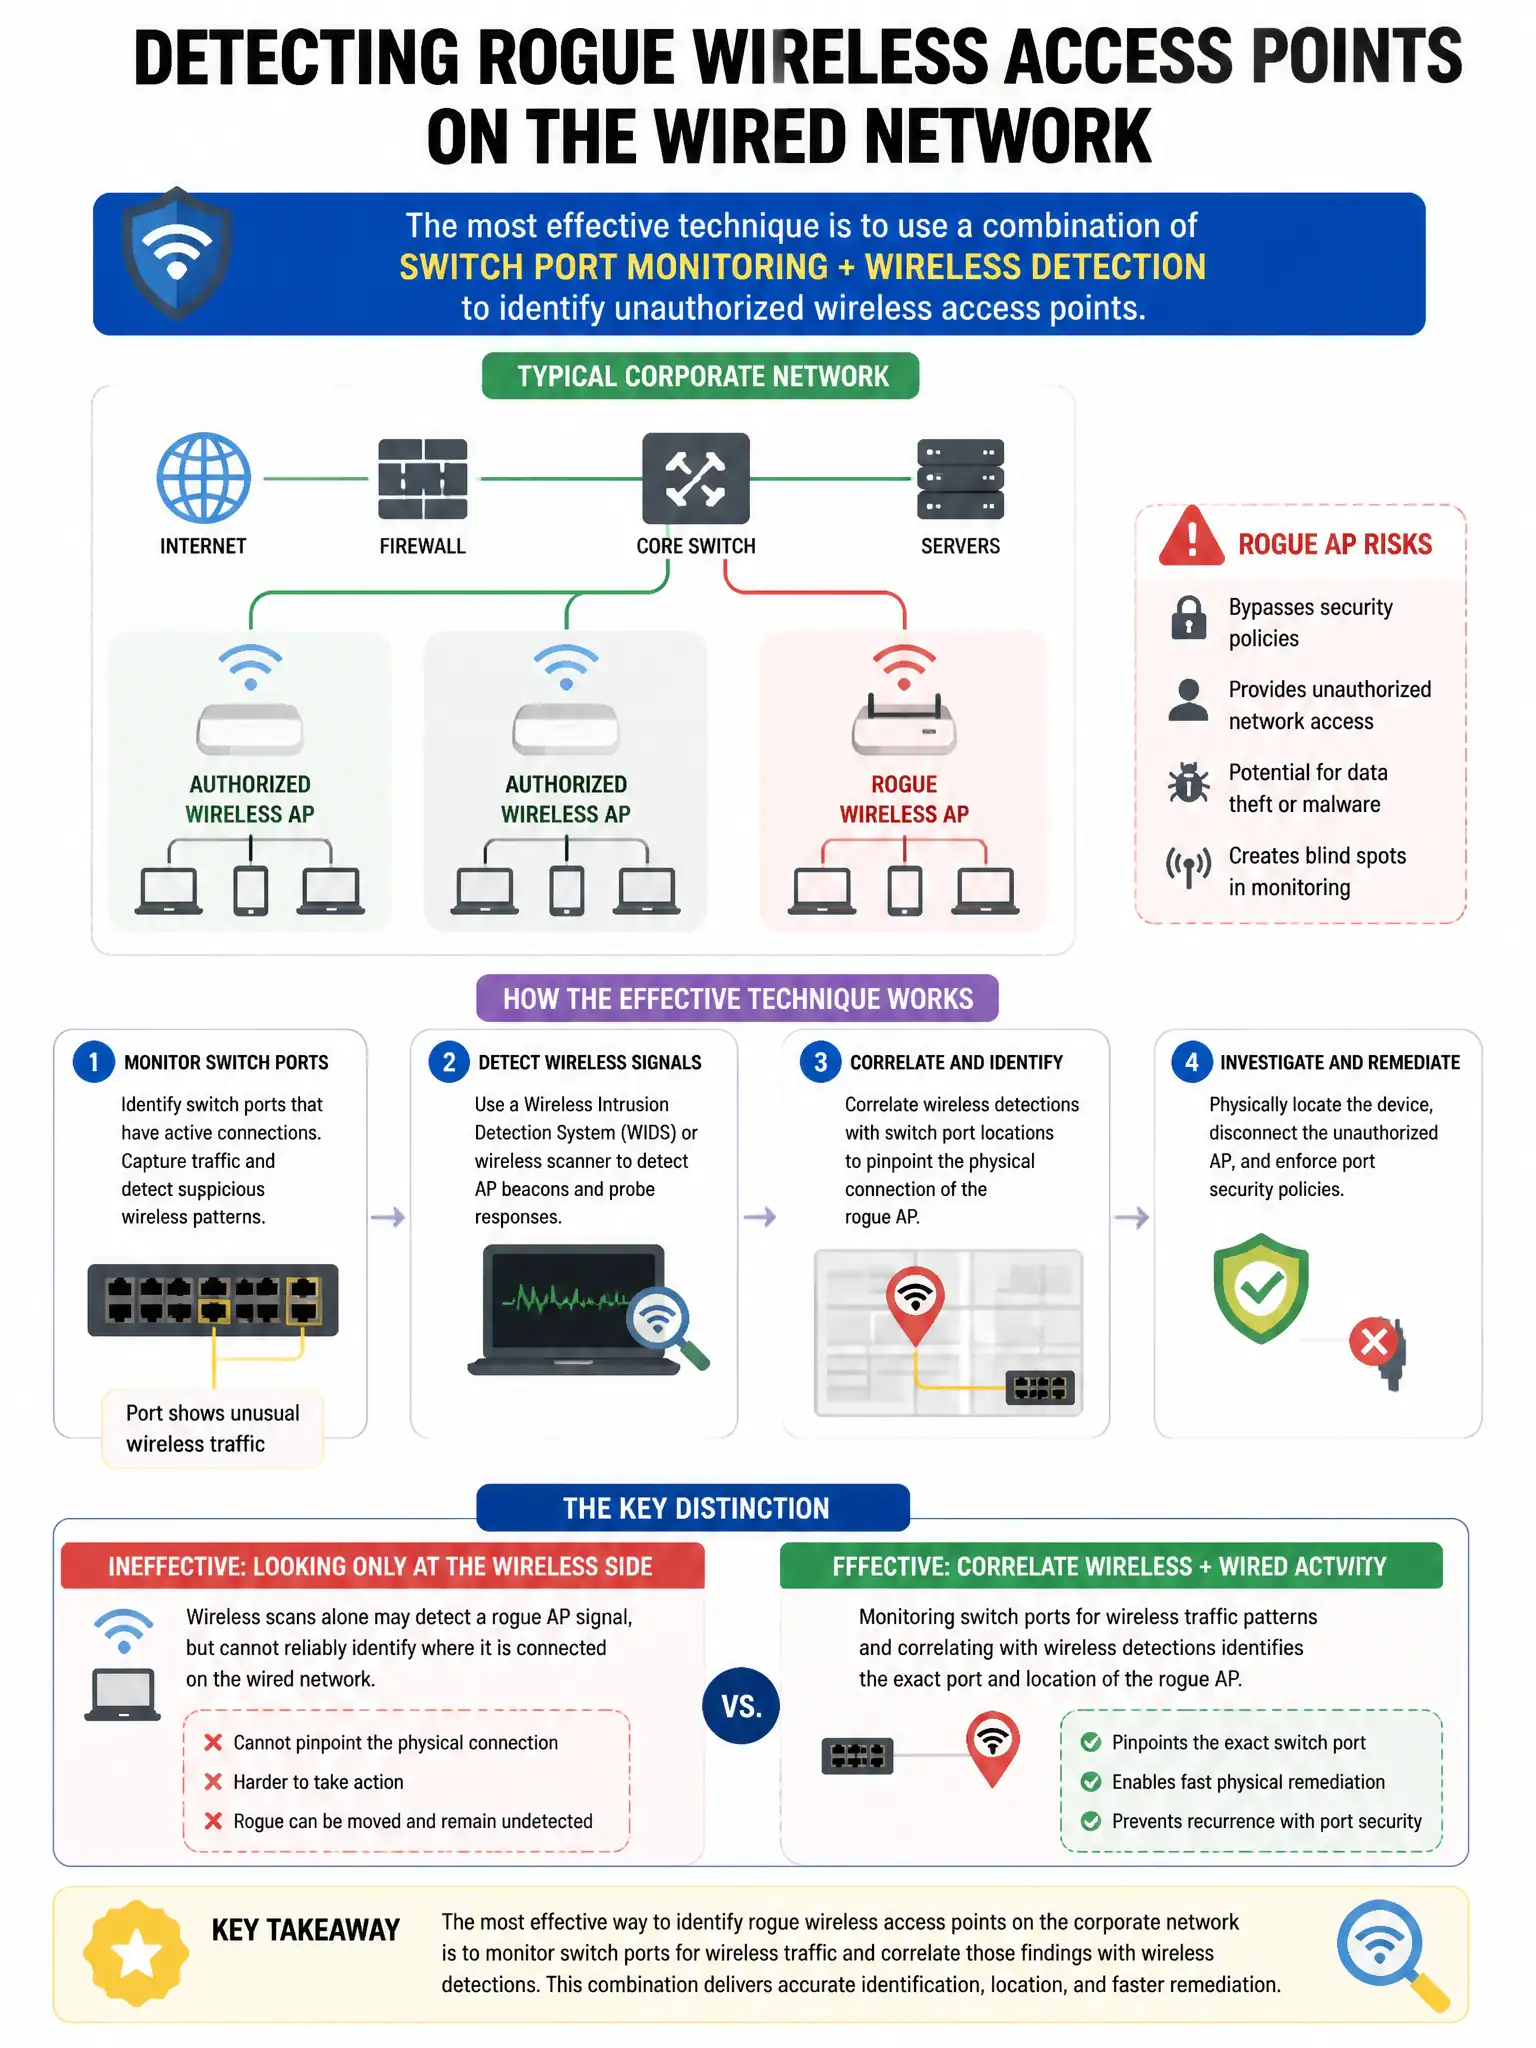
An organization wants to detect rogue wireless access points connected to the corporate wired network. Which technique is most effective at identifying unauthorized wireless devices?
Select an answer to reveal the explanation.
Short Explanation
You want to run authorized wireless surveys with spectrum analyzers, then compare every BSSID/MAC you find against your approved AP inventory. That’s how you spot rogue APs that aren’t registered, and you can even locate them physically.
Full Explanation
Authorized wireless surveys with spectrum analyzers are correct because they detect all wireless signals in the environment, and correlating discovered BSSID/MAC addresses against the authorized AP inventory identifies rogue devices that are not registered; physical surveys also locate rogue AP positions. Scanning all wired switch ports with Nmap for wireless-related services is wrong because rogue APs broadcast wirelessly and do not necessarily expose services detectable from the wired network. Blocking all 2.4GHz and 5GHz RF with physical shielding in the building is wrong because RF shielding is impractical for most environments and prevents legitimate wireless too. Requiring all wireless clients to use WEP encryption to identify rogue devices is wrong because WEP is a deprecated weak encryption standard; requiring it would reduce security for all devices and would not identify rogues.