
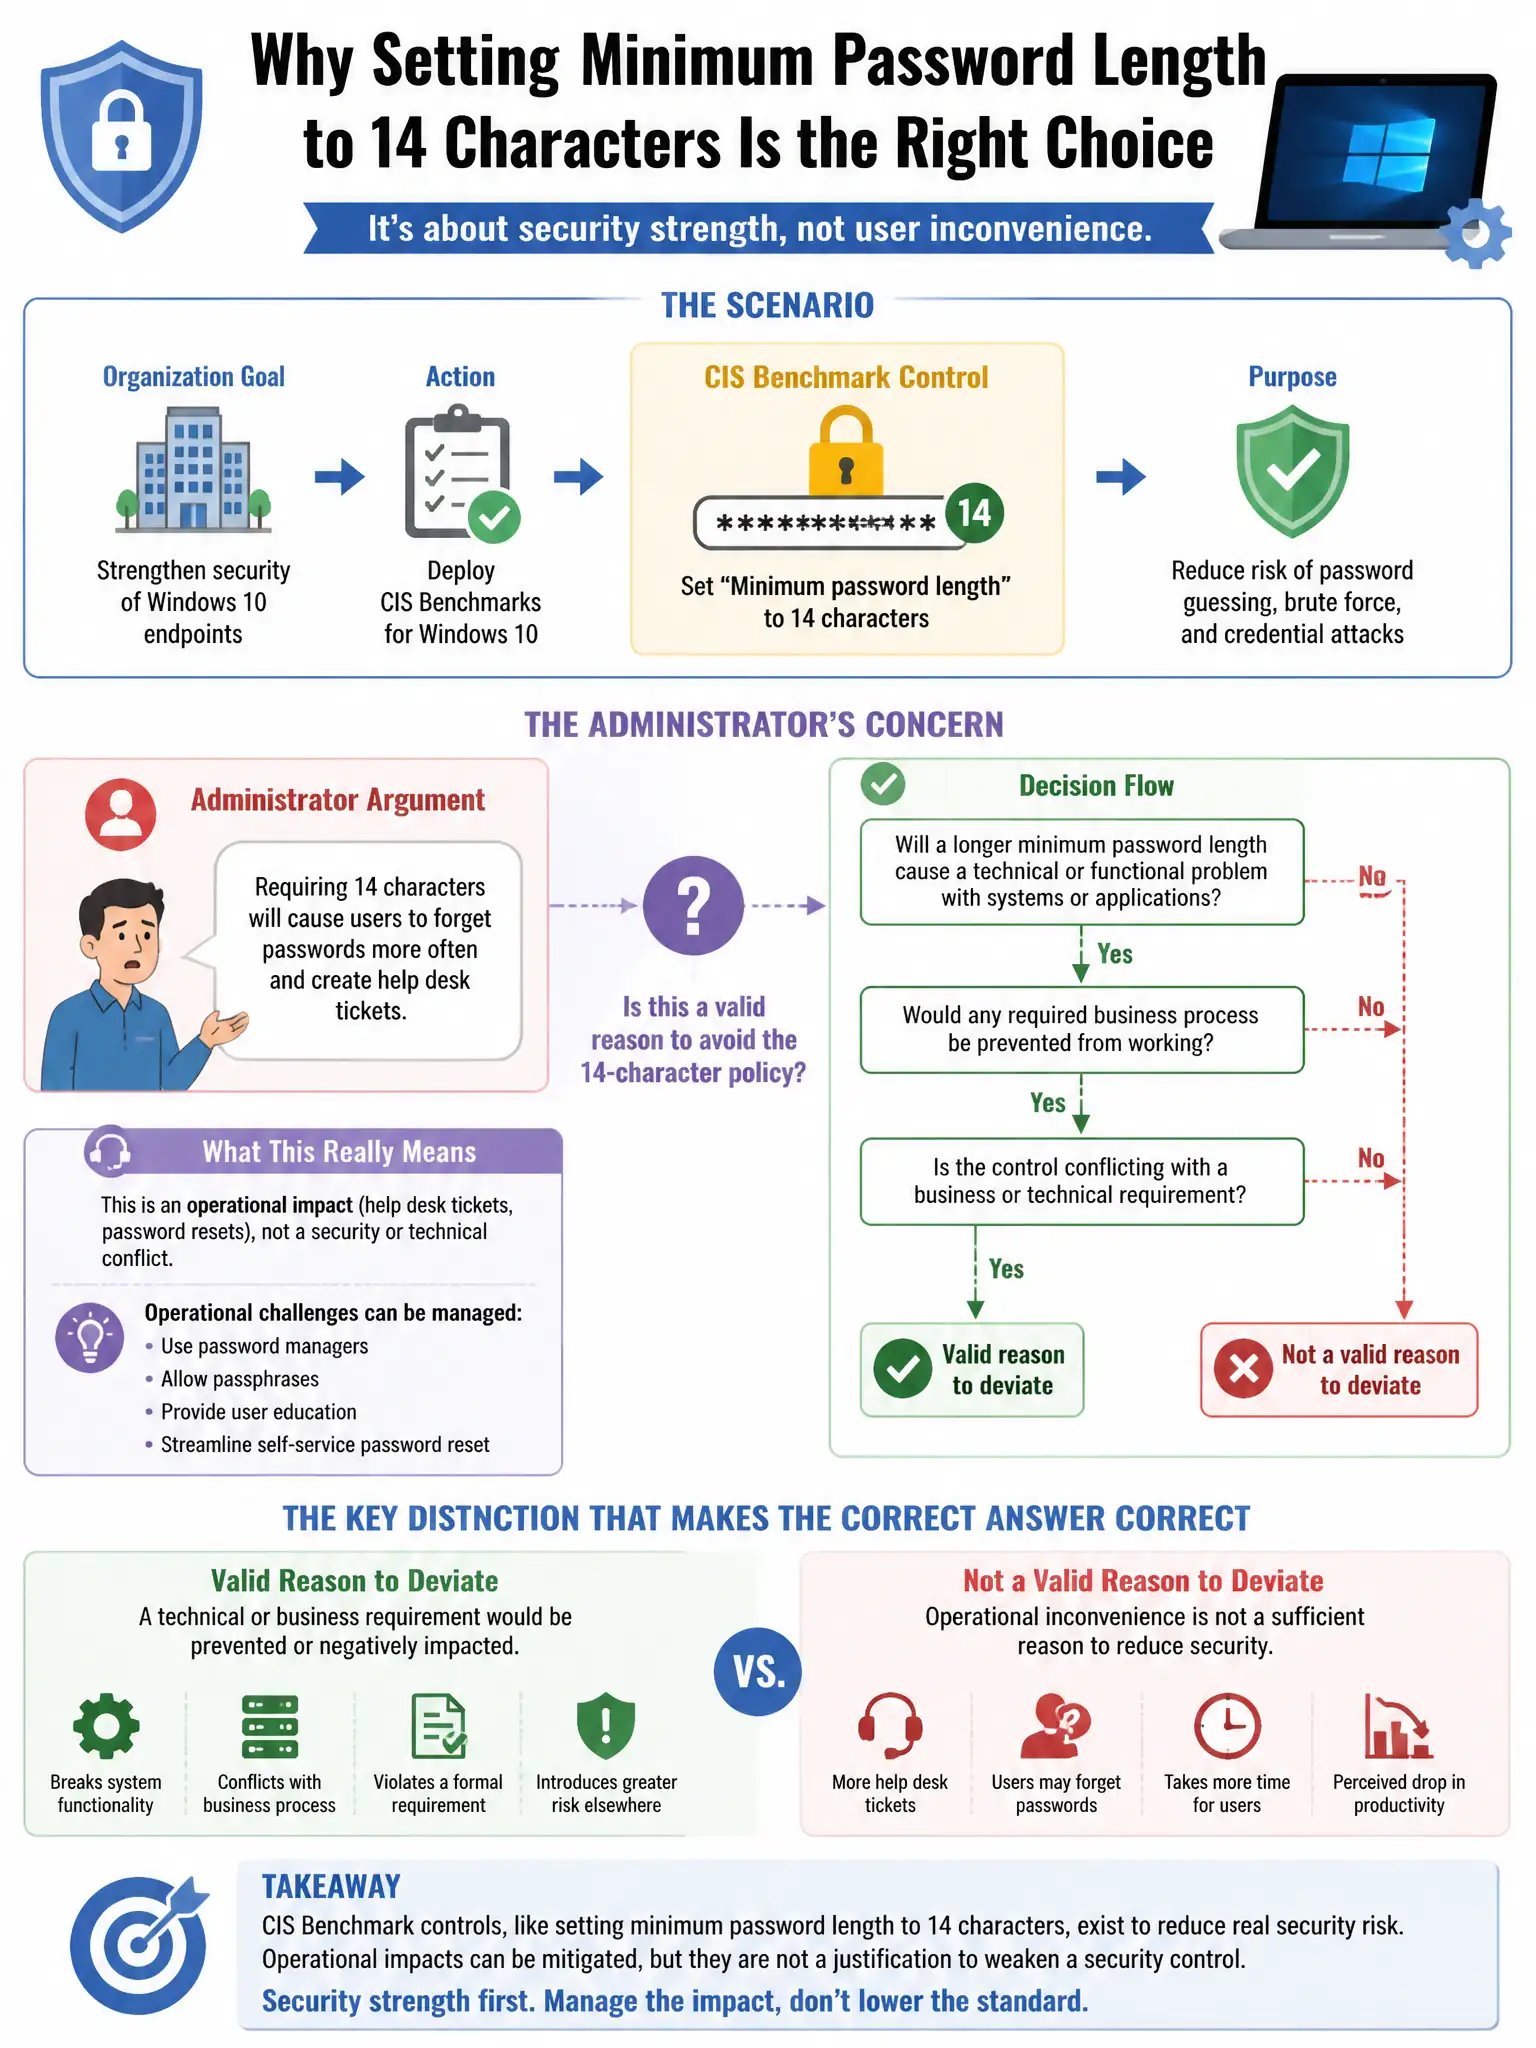
An organization deploys CIS Benchmarks for Windows 10 hardening. One control recommends setting 'Minimum password length' to 14 characters. An administrator argues this will cause user complaints. What is the security justification for this control?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — longer passwords blow up the keyspace an attacker must search in an offline brute-force or dictionary attack, so cracking takes dramatically longer. Password length doesn't stop phishing; MFA does.
Full Explanation
Longer passwords increase the time required for offline brute-force attacks exponentially because password length exponentially increases the keyspace an attacker must search in an offline brute-force or dictionary attack, making longer passwords dramatically more resistant to cracking. The phishing-prevention claim is wrong because password length does not protect against phishing; MFA addresses that threat. The Kerberos requirement claim is wrong because Kerberos authentication works with any valid password; it has no specific length requirement. The NIST claim is wrong because NIST SP 800-63B recommends a minimum of 8 characters for memorized secrets and encourages longer passwords but does not mandate exactly 14 characters.