
A penetration tester is conducting a red team engagement and wants to move laterally using 'Living off the Land' (LotL) techniques. Which tool is most consistent with a LotL approach?
Select an answer to reveal the explanation.
Short Explanation
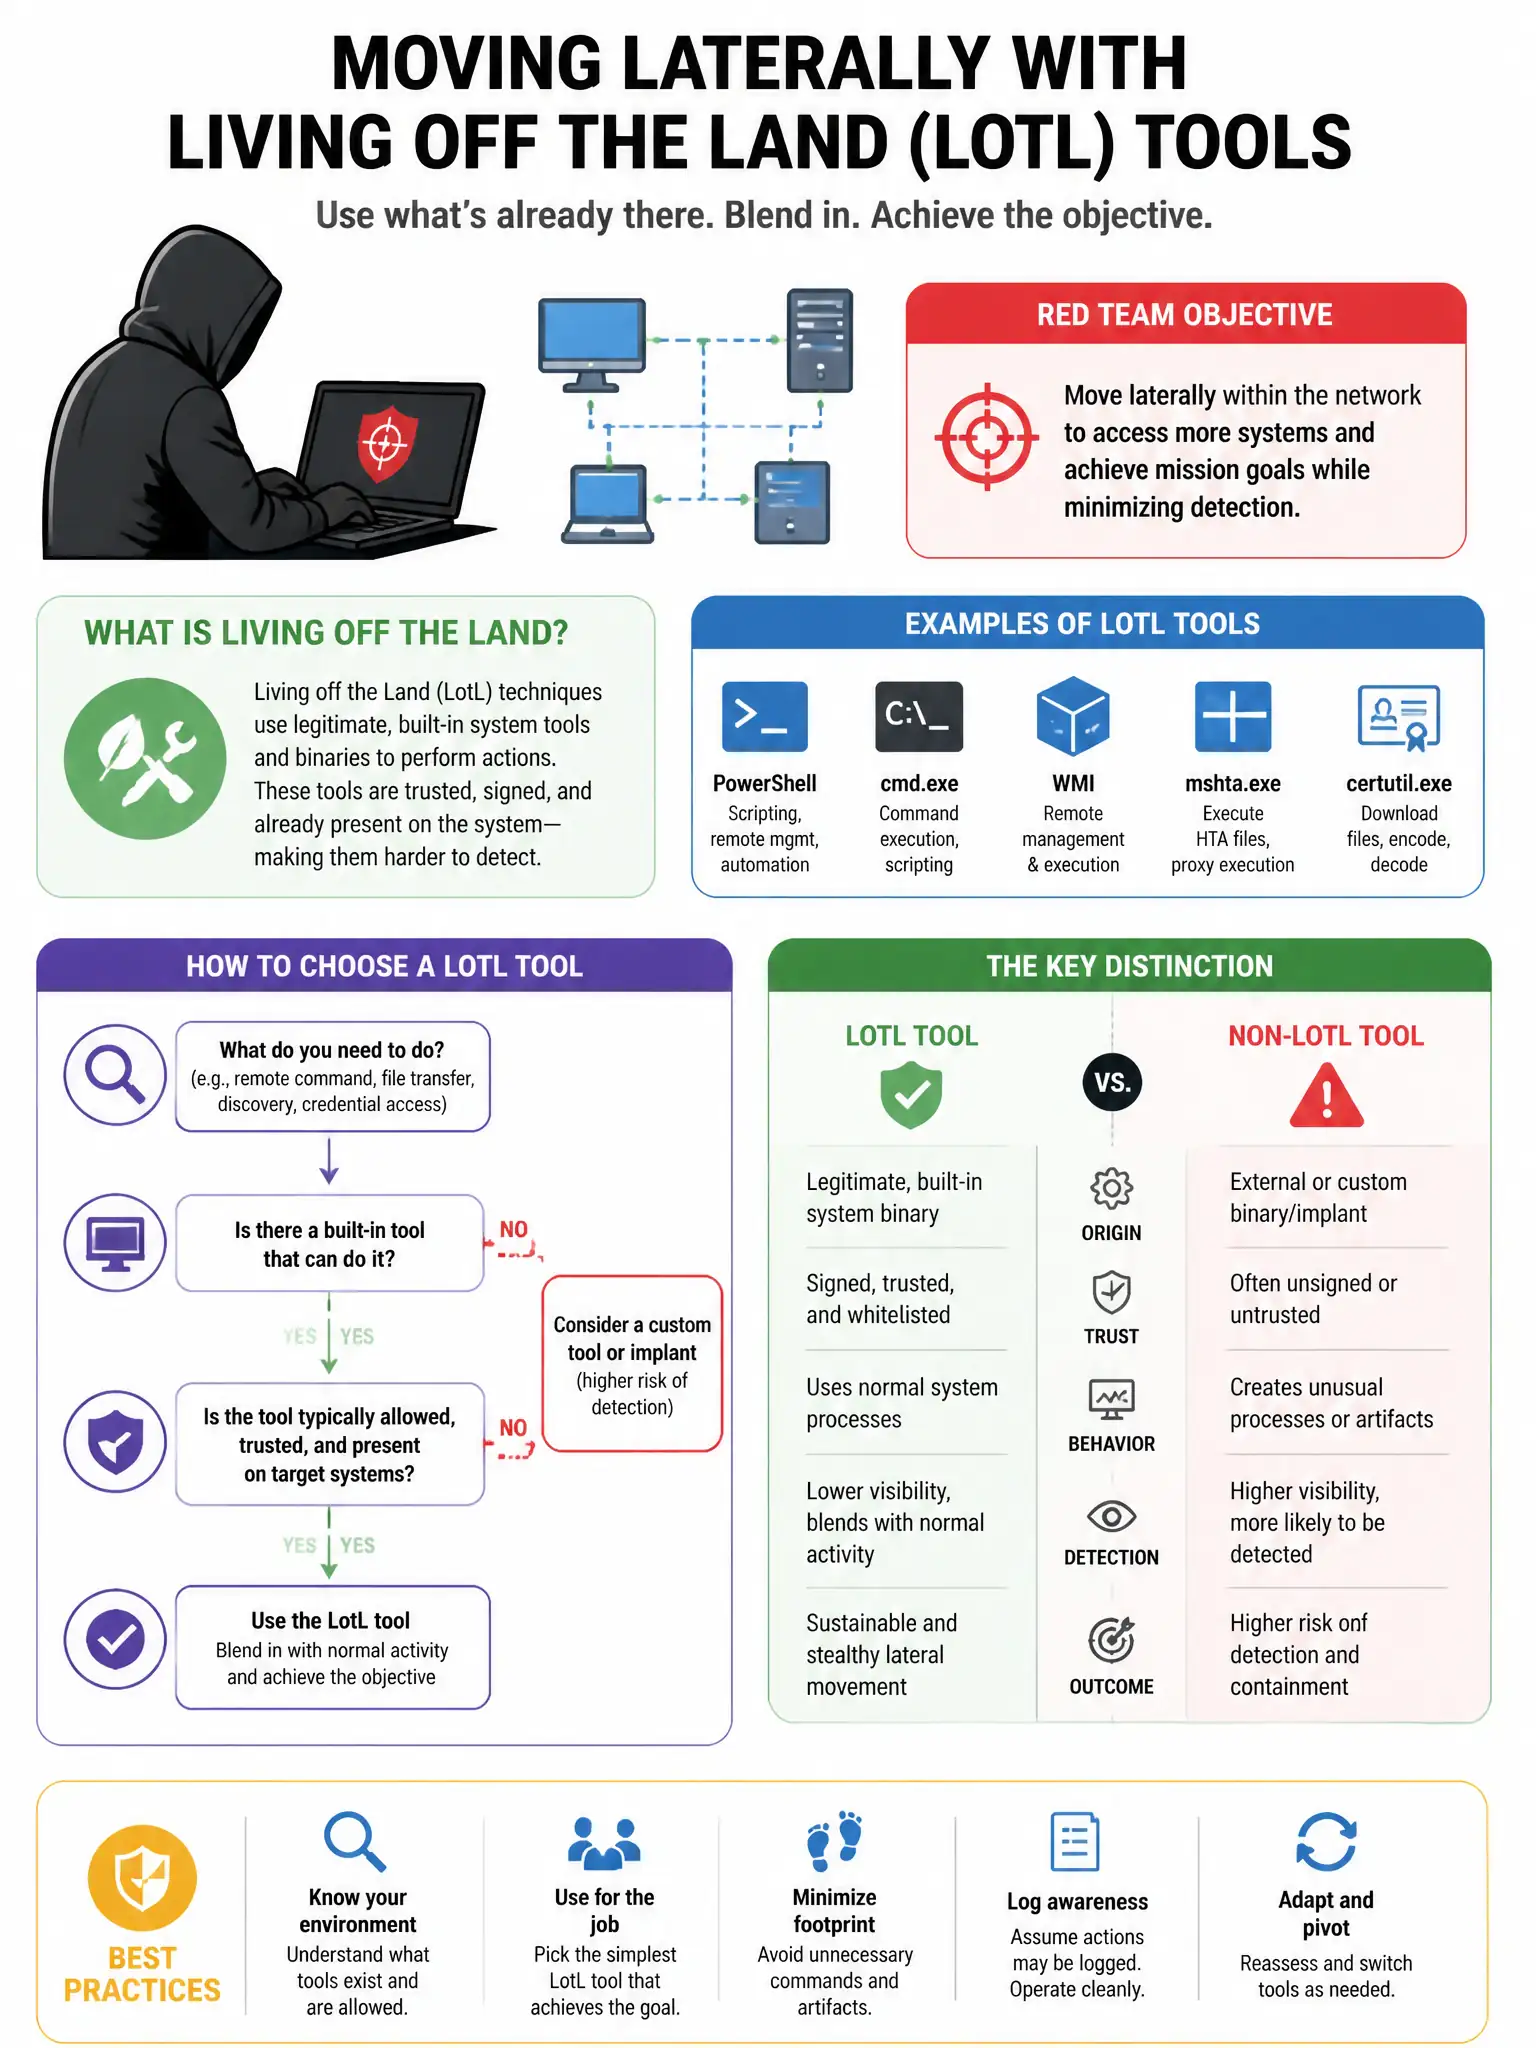
Here's the deal — you want the built-in Windows tools such as WMI, PSExec, or PowerShell remoting because LotL means using what's already on the system. It blends with normal admin activity, so it's harder to spot.
Full Explanation
Using built-in Windows tools such as WMI, PSExec, or PowerShell remoting is correct because Living off the Land techniques use tools and binaries already present on the system, such as WMI, PowerShell, PsExec, and certutil, to perform attacker actions. That makes them harder to detect because they blend with normal administrative activity. Deploying a custom compiled C2 agent is wrong because it is a bespoke tool, not a built-in system utility. Uploading a Metasploit meterpreter payload via a web shell is wrong because Metasploit meterpreter is an attacker-deployed tool, not a system-native binary. Exploiting a zero-day browser vulnerability is wrong because it is a specific initial access technique, not a lateral movement technique based on system-native tools.