
Which standard framework maps attacker techniques and sub-techniques to specific detection data sources and mitigation controls, making it highly useful for continuous security monitoring?
Select an answer to reveal the explanation.
Short Explanation
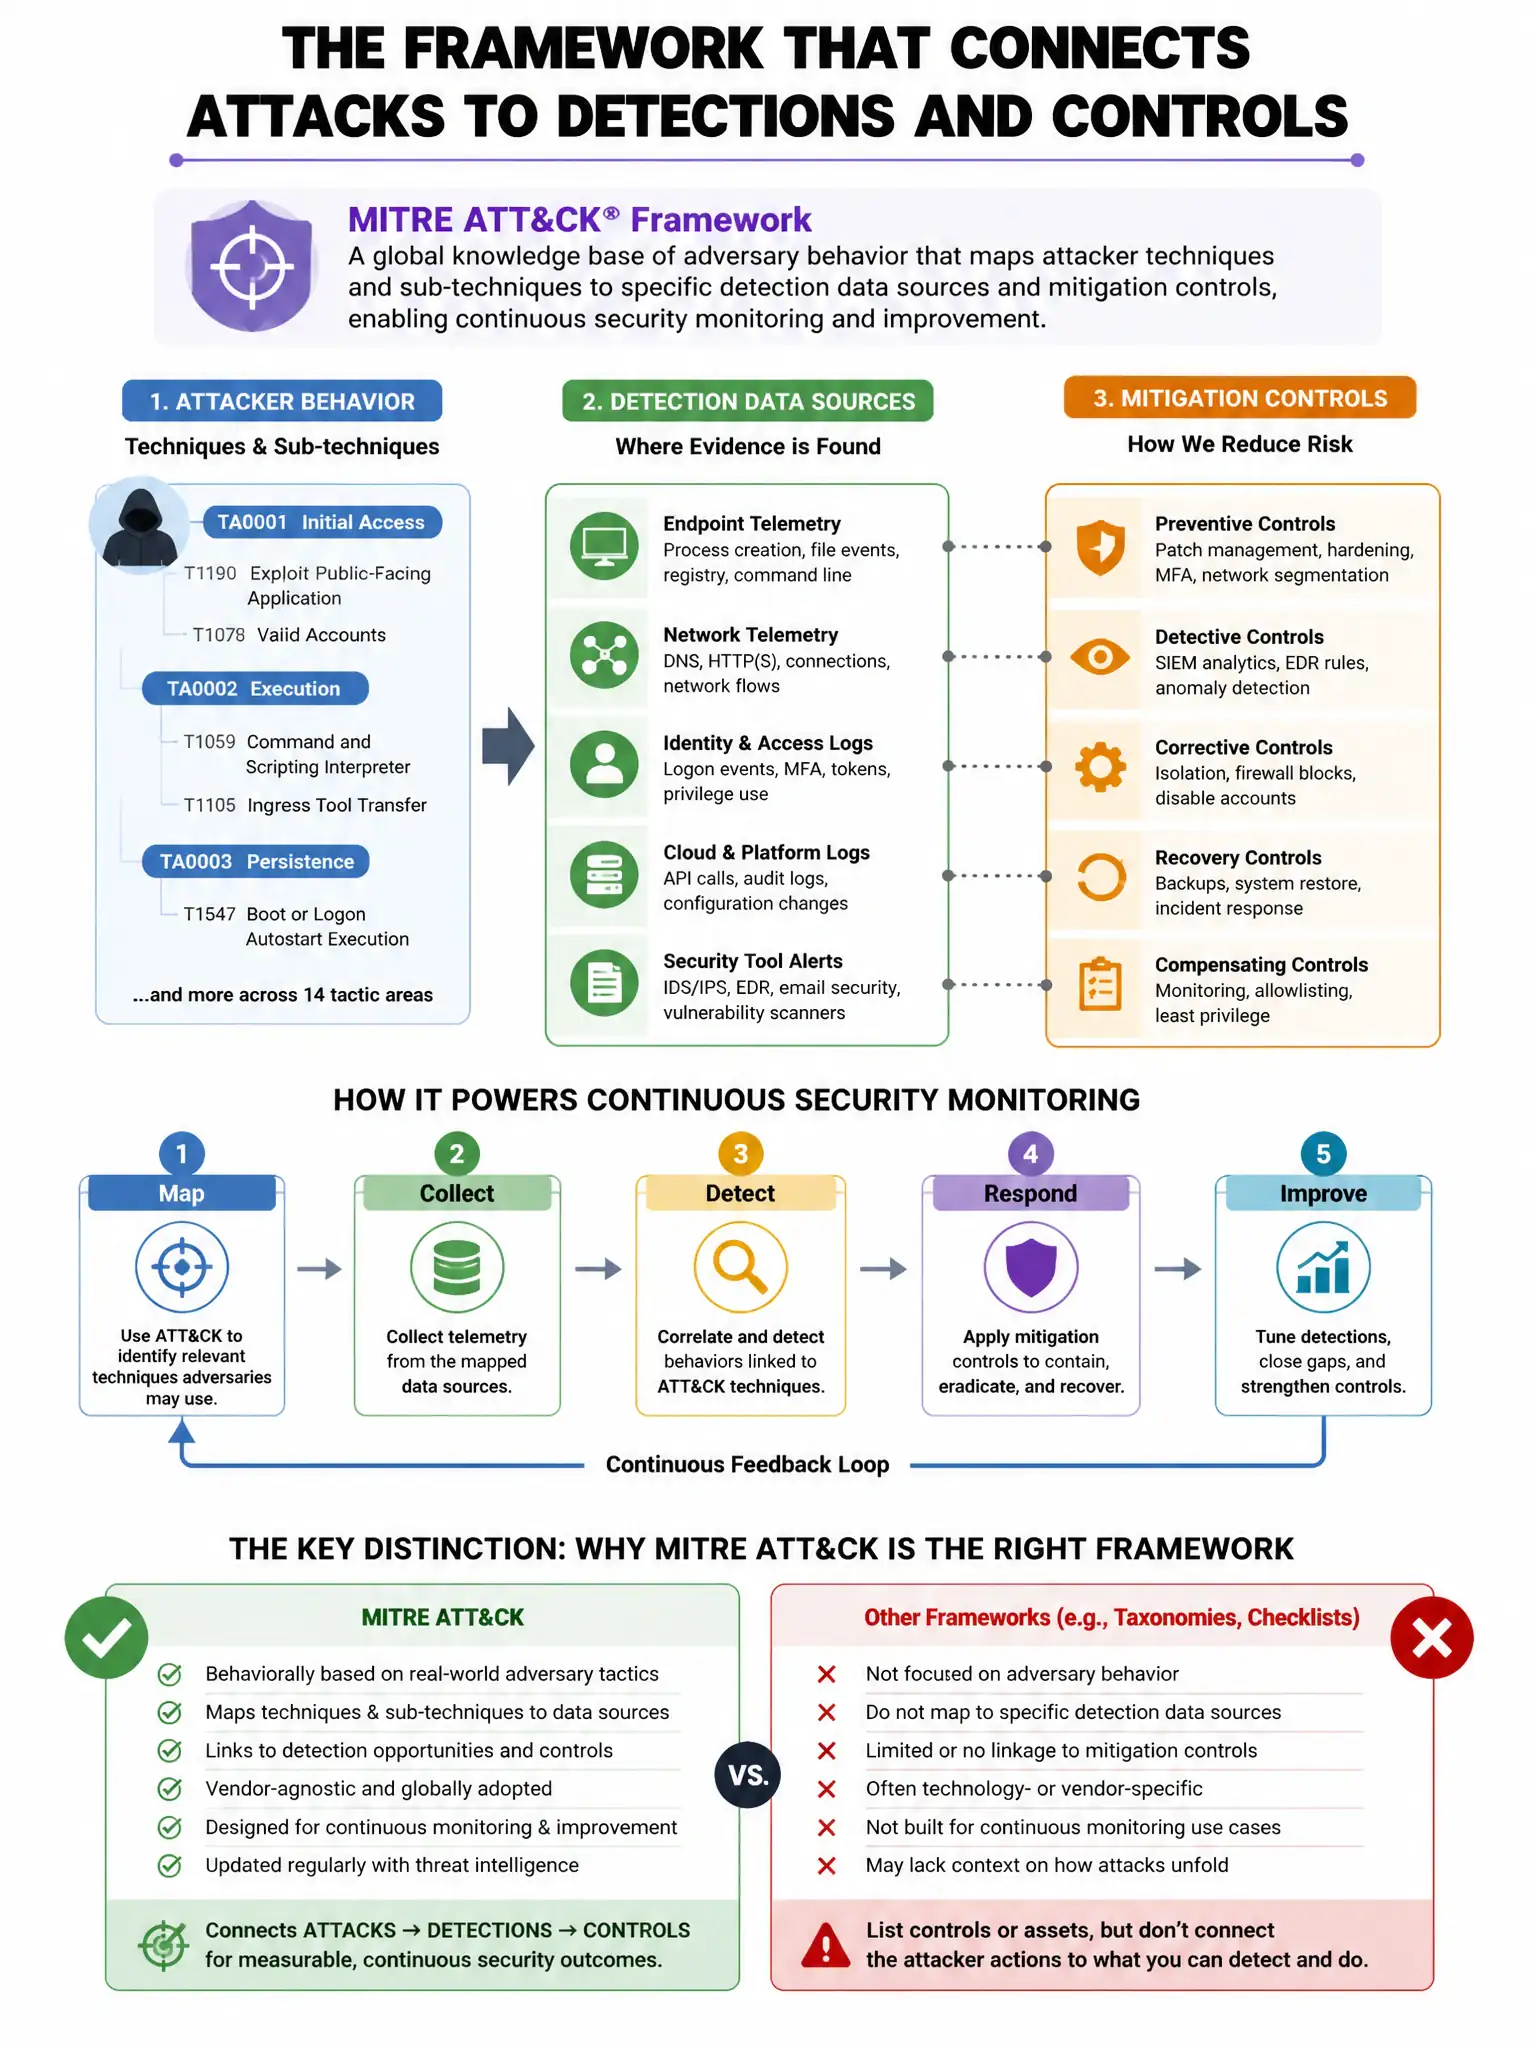
Here's the deal — MITRE ATT&CK is right because it maps adversary tactics, techniques, and procedures to specific data sources, detection opportunities, and mitigations, making it ideal for building and improving detection coverage in a SOC. You use it for continuous security monitoring, not just incident handling.
Full Explanation
MITRE ATT&CK is correct because it maps adversary tactics, techniques, and procedures to specific data sources, detection opportunities, and mitigations, making it ideal for building and improving detection coverage in a SOC. The NIST SP 800-61 Computer Security Incident Handling Guide is wrong because it is an incident response guide, not a detection framework. The CIS Benchmarks are wrong because they provide system hardening guidance, not attacker technique mappings. The OWASP Top 10 is wrong because it focuses on web application vulnerabilities, not enterprise detection.