
A SIEM rule is generating 500 alerts per day but only 2 are confirmed incidents. The SOC team is overwhelmed. What is this situation called and what is the best remediation?
Select an answer to reveal the explanation.
Short Explanation
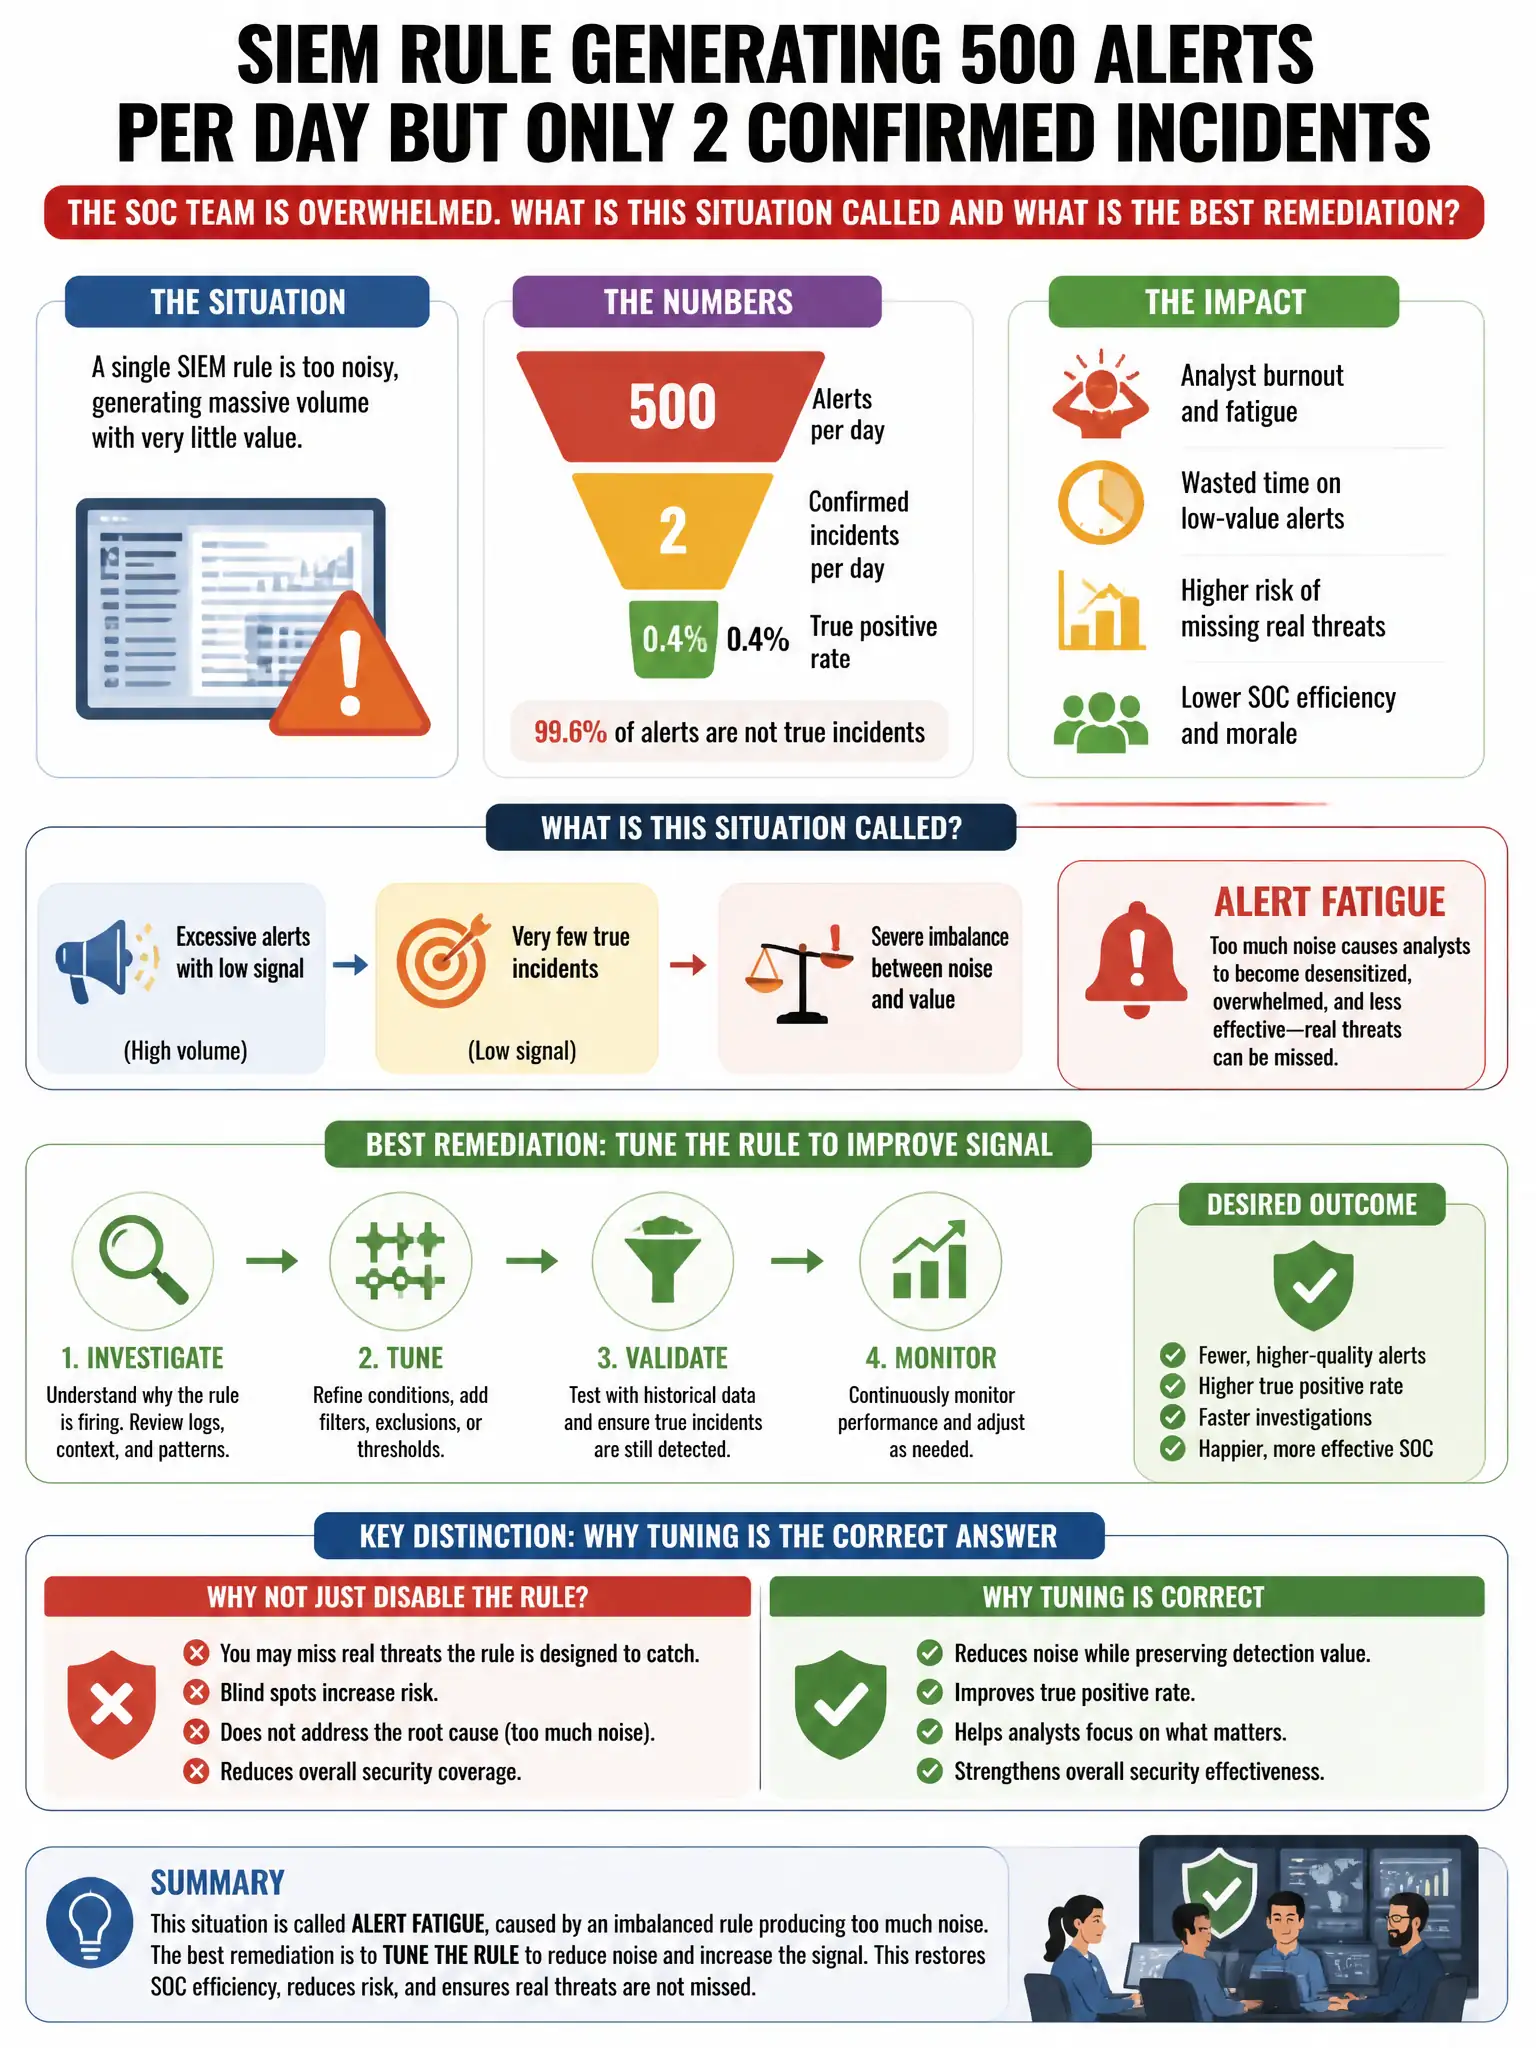
Here's the deal — you're dealing with alert fatigue caused by too many false positives. Tune the rule with extra conditions, context, or whitelisting to cut noise while still catching real threats.
Full Explanation
The correct situation is alert fatigue caused by false positives, remediated by tuning the rule with additional conditions to reduce false positives. A high false positive rate leads to alert fatigue, so the fix is rule tuning: add context, whitelist conditions, or correlated conditions to reduce noise while maintaining detection of real threats. The true positive rate option with more analysts is wrong because adding analysts treats the symptom without addressing the root cause of poor rule specificity. The log ingestion failure option is wrong because the rule is generating many alerts, indicating ingestion is working; the problem is alert quality. The signature update option is wrong because this is a tuning problem, not a signature age problem.