
An organization deploys network-based encryption between all internal hosts using IPsec in tunnel mode. Which security monitoring challenge does this create?
Select an answer to reveal the explanation.
Short Explanation
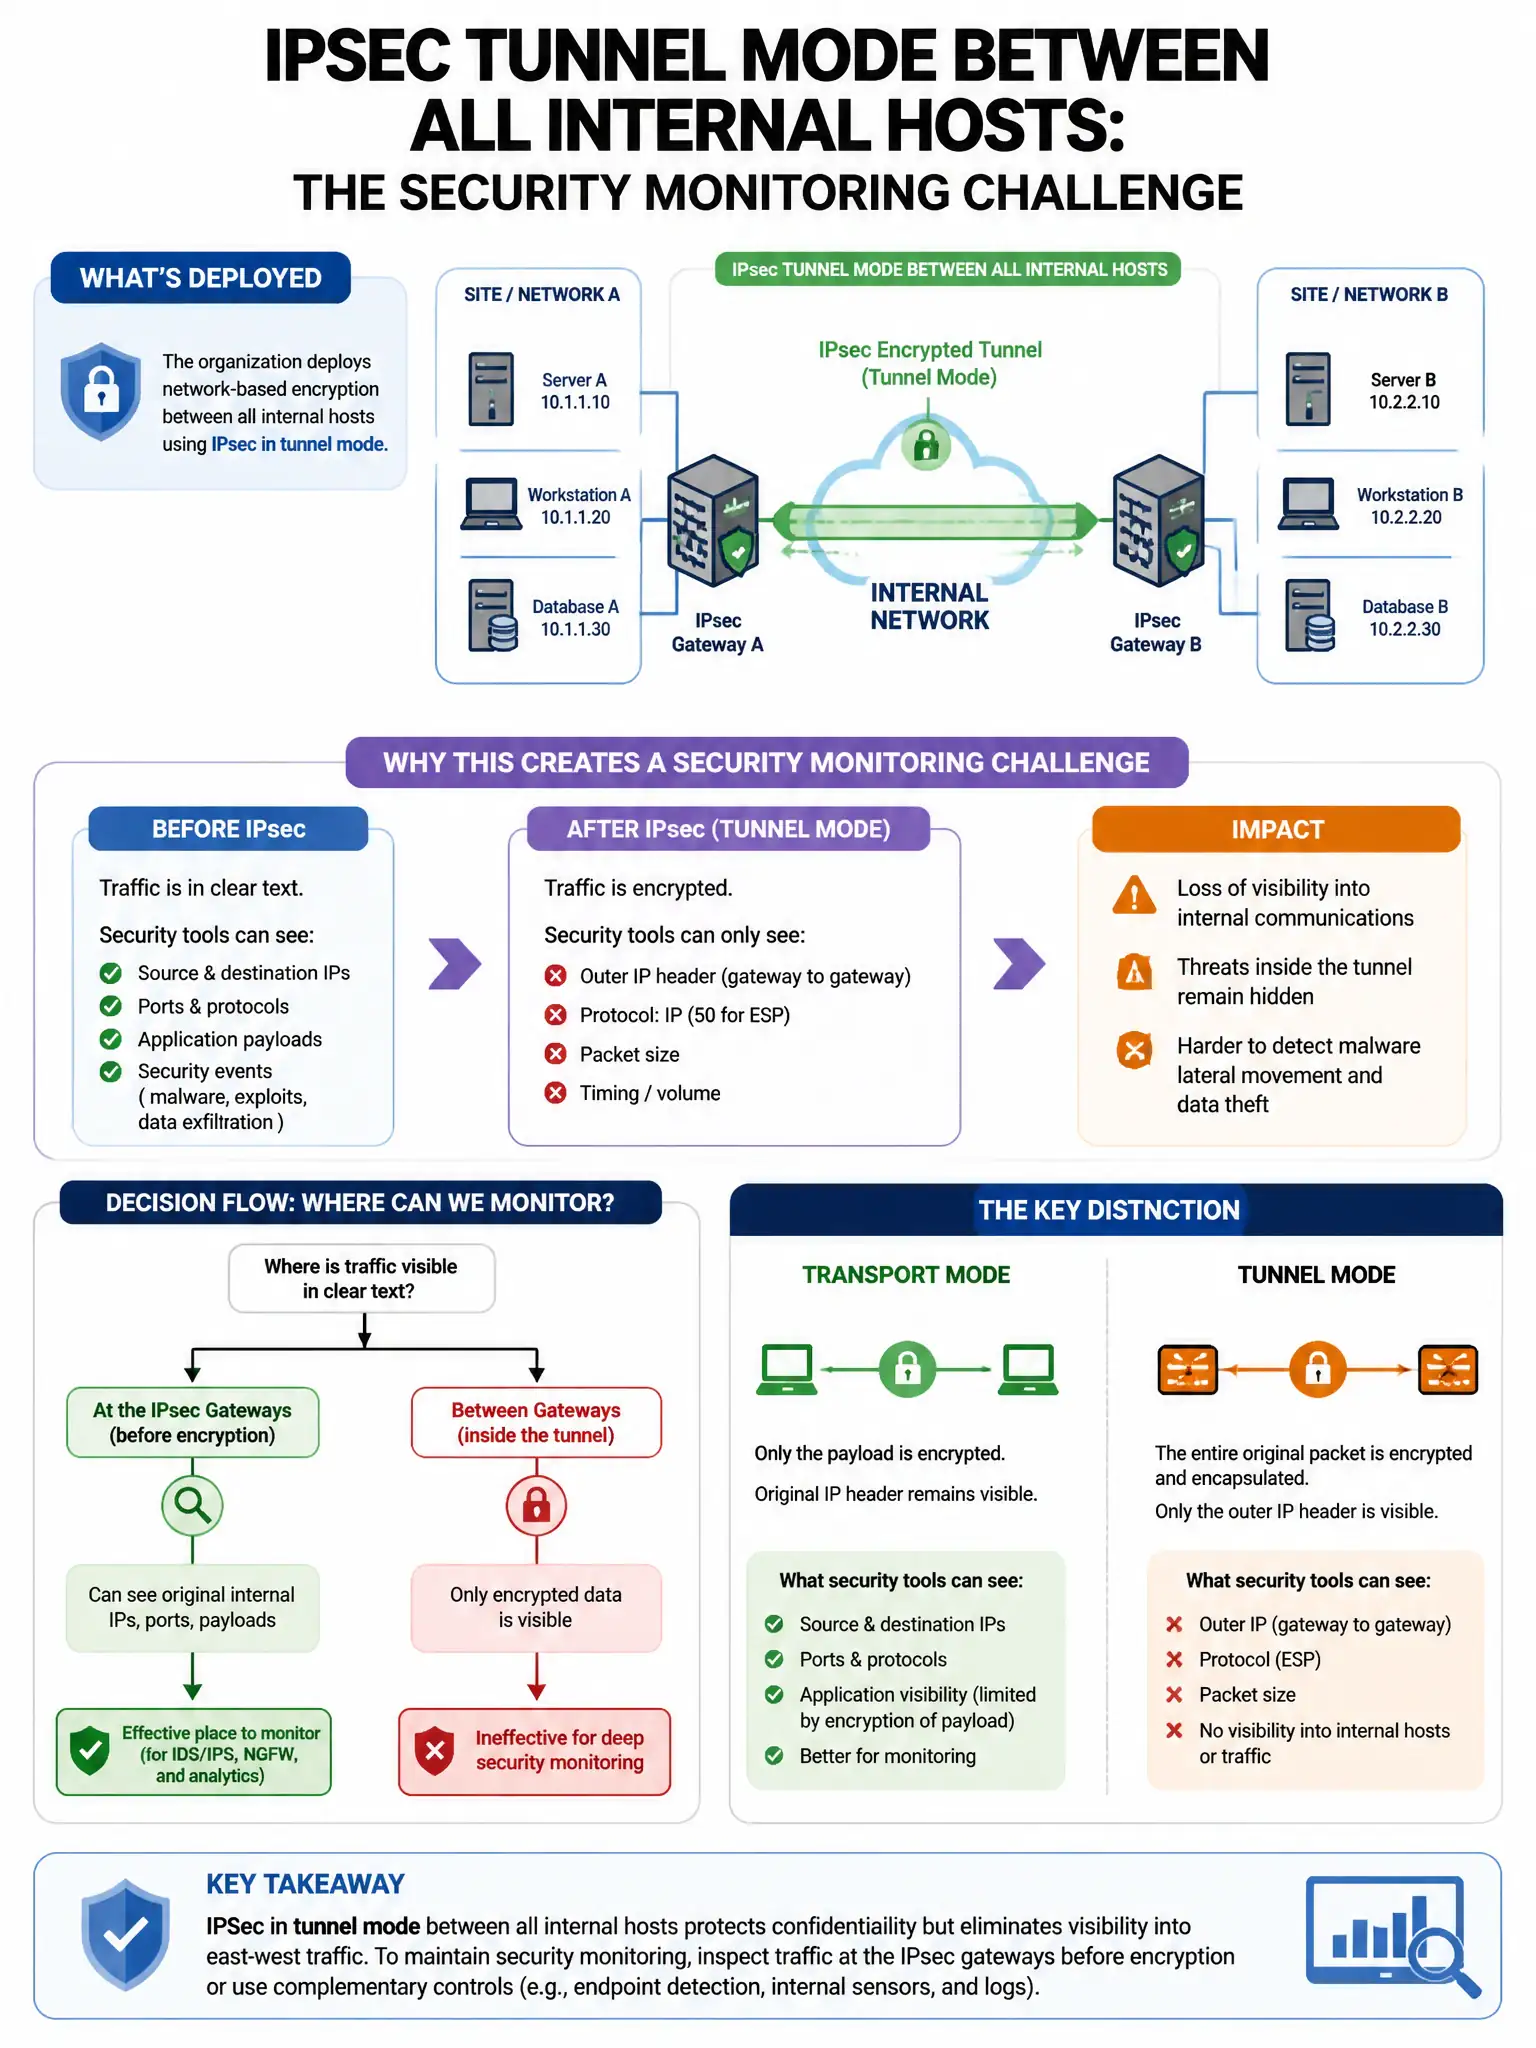
Here's the deal — IPsec tunnel mode encrypts packet payloads, so deep packet inspection and payload-based IDS signatures can't inspect encrypted traffic. You still have some visibility, but you can't match signatures inside the encrypted payload.
Full Explanation
IPsec tunnel mode encrypts packet payloads, so deep packet inspection and payload-based IDS signatures cannot inspect encrypted traffic. The ARP spoofing option is wrong because ARP operates at Layer 2 before IPsec encryption and is still visible. The flow-metadata option is wrong because IPsec does not drop all packets; flow metadata such as source, destination, port, and volume remains visible even with IPsec. The firewall option is wrong because stateful firewalls can track connection state using visible IP headers, and in IPsec transport mode the original IP header remains visible.