
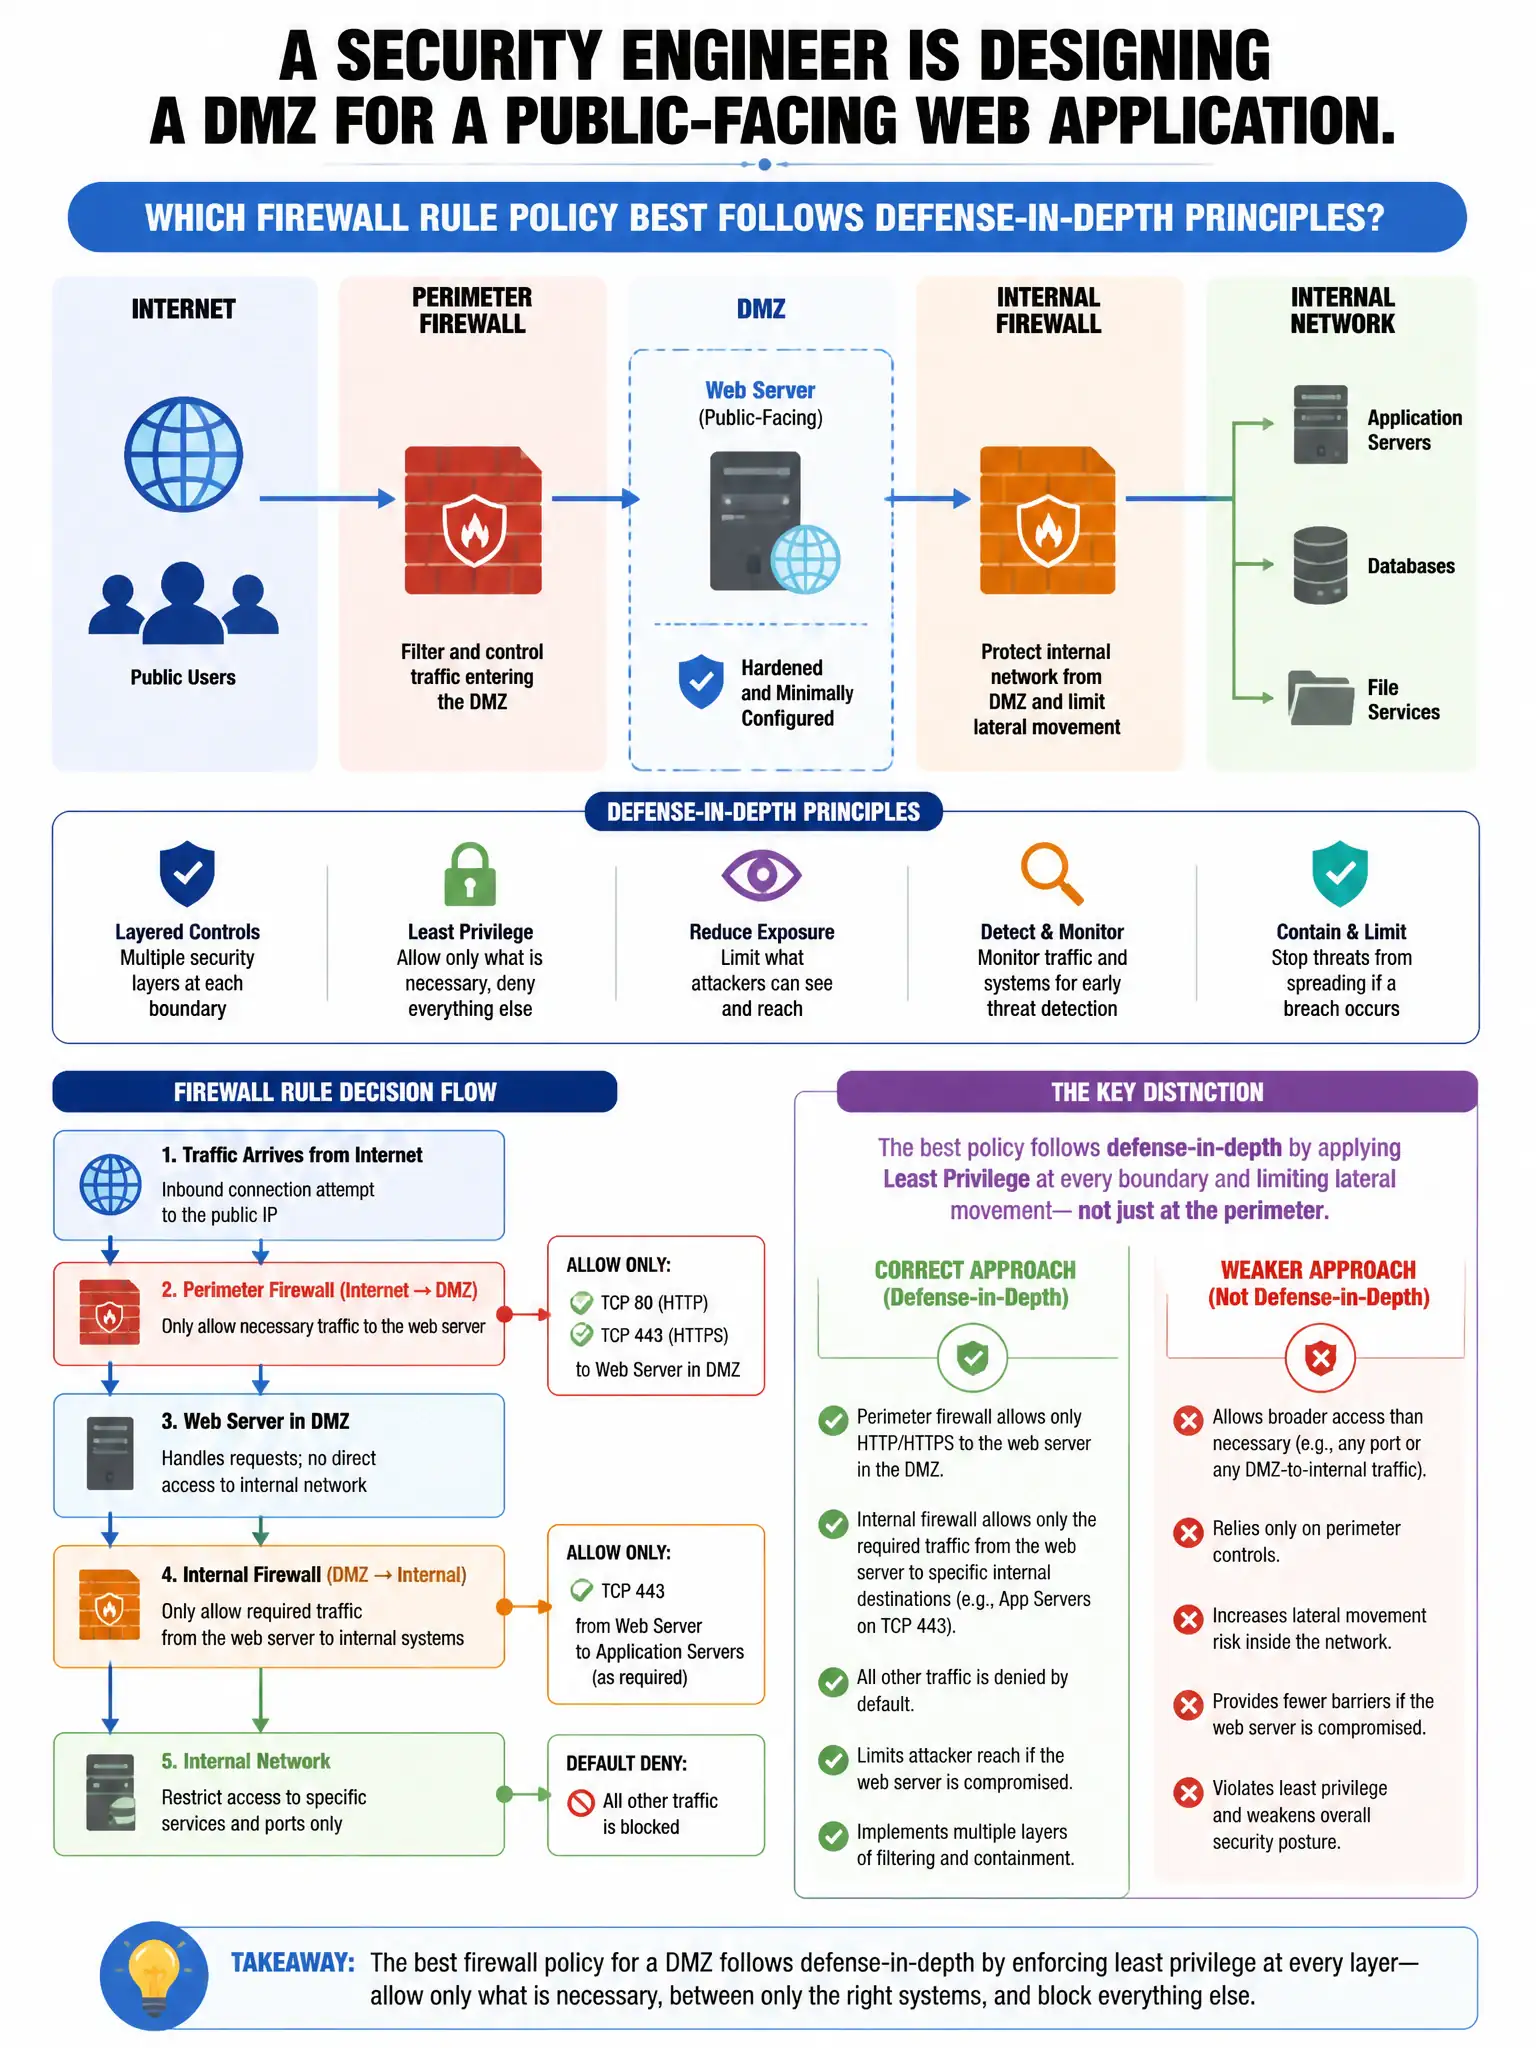
A security engineer is designing a DMZ for a public-facing web application. Which firewall rule policy best follows defense-in-depth principles?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want to block direct DMZ-to-internal traffic and route database calls through an application proxy. That limits the blast radius if the DMZ is compromised.
Full Explanation
Blocking all traffic between the DMZ and internal network and using an application proxy for database calls is correct because it limits the blast radius if the DMZ is compromised. Allowing all outbound traffic from the DMZ to the internal network to support application queries is wrong because it defeats the purpose of the DMZ architecture. Permitting DMZ-to-internal access only on TCP 1433 without stateful inspection is wrong because it gives attackers a direct path to sensitive data. Placing the database server in the DMZ alongside the web server is wrong because it exposes the database directly to the internet.