
A network architect is designing a new enterprise segment and wants to enforce the principle of least privilege at the network layer. Which approach best achieves this goal?
Select an answer to reveal the explanation.
Short Explanation
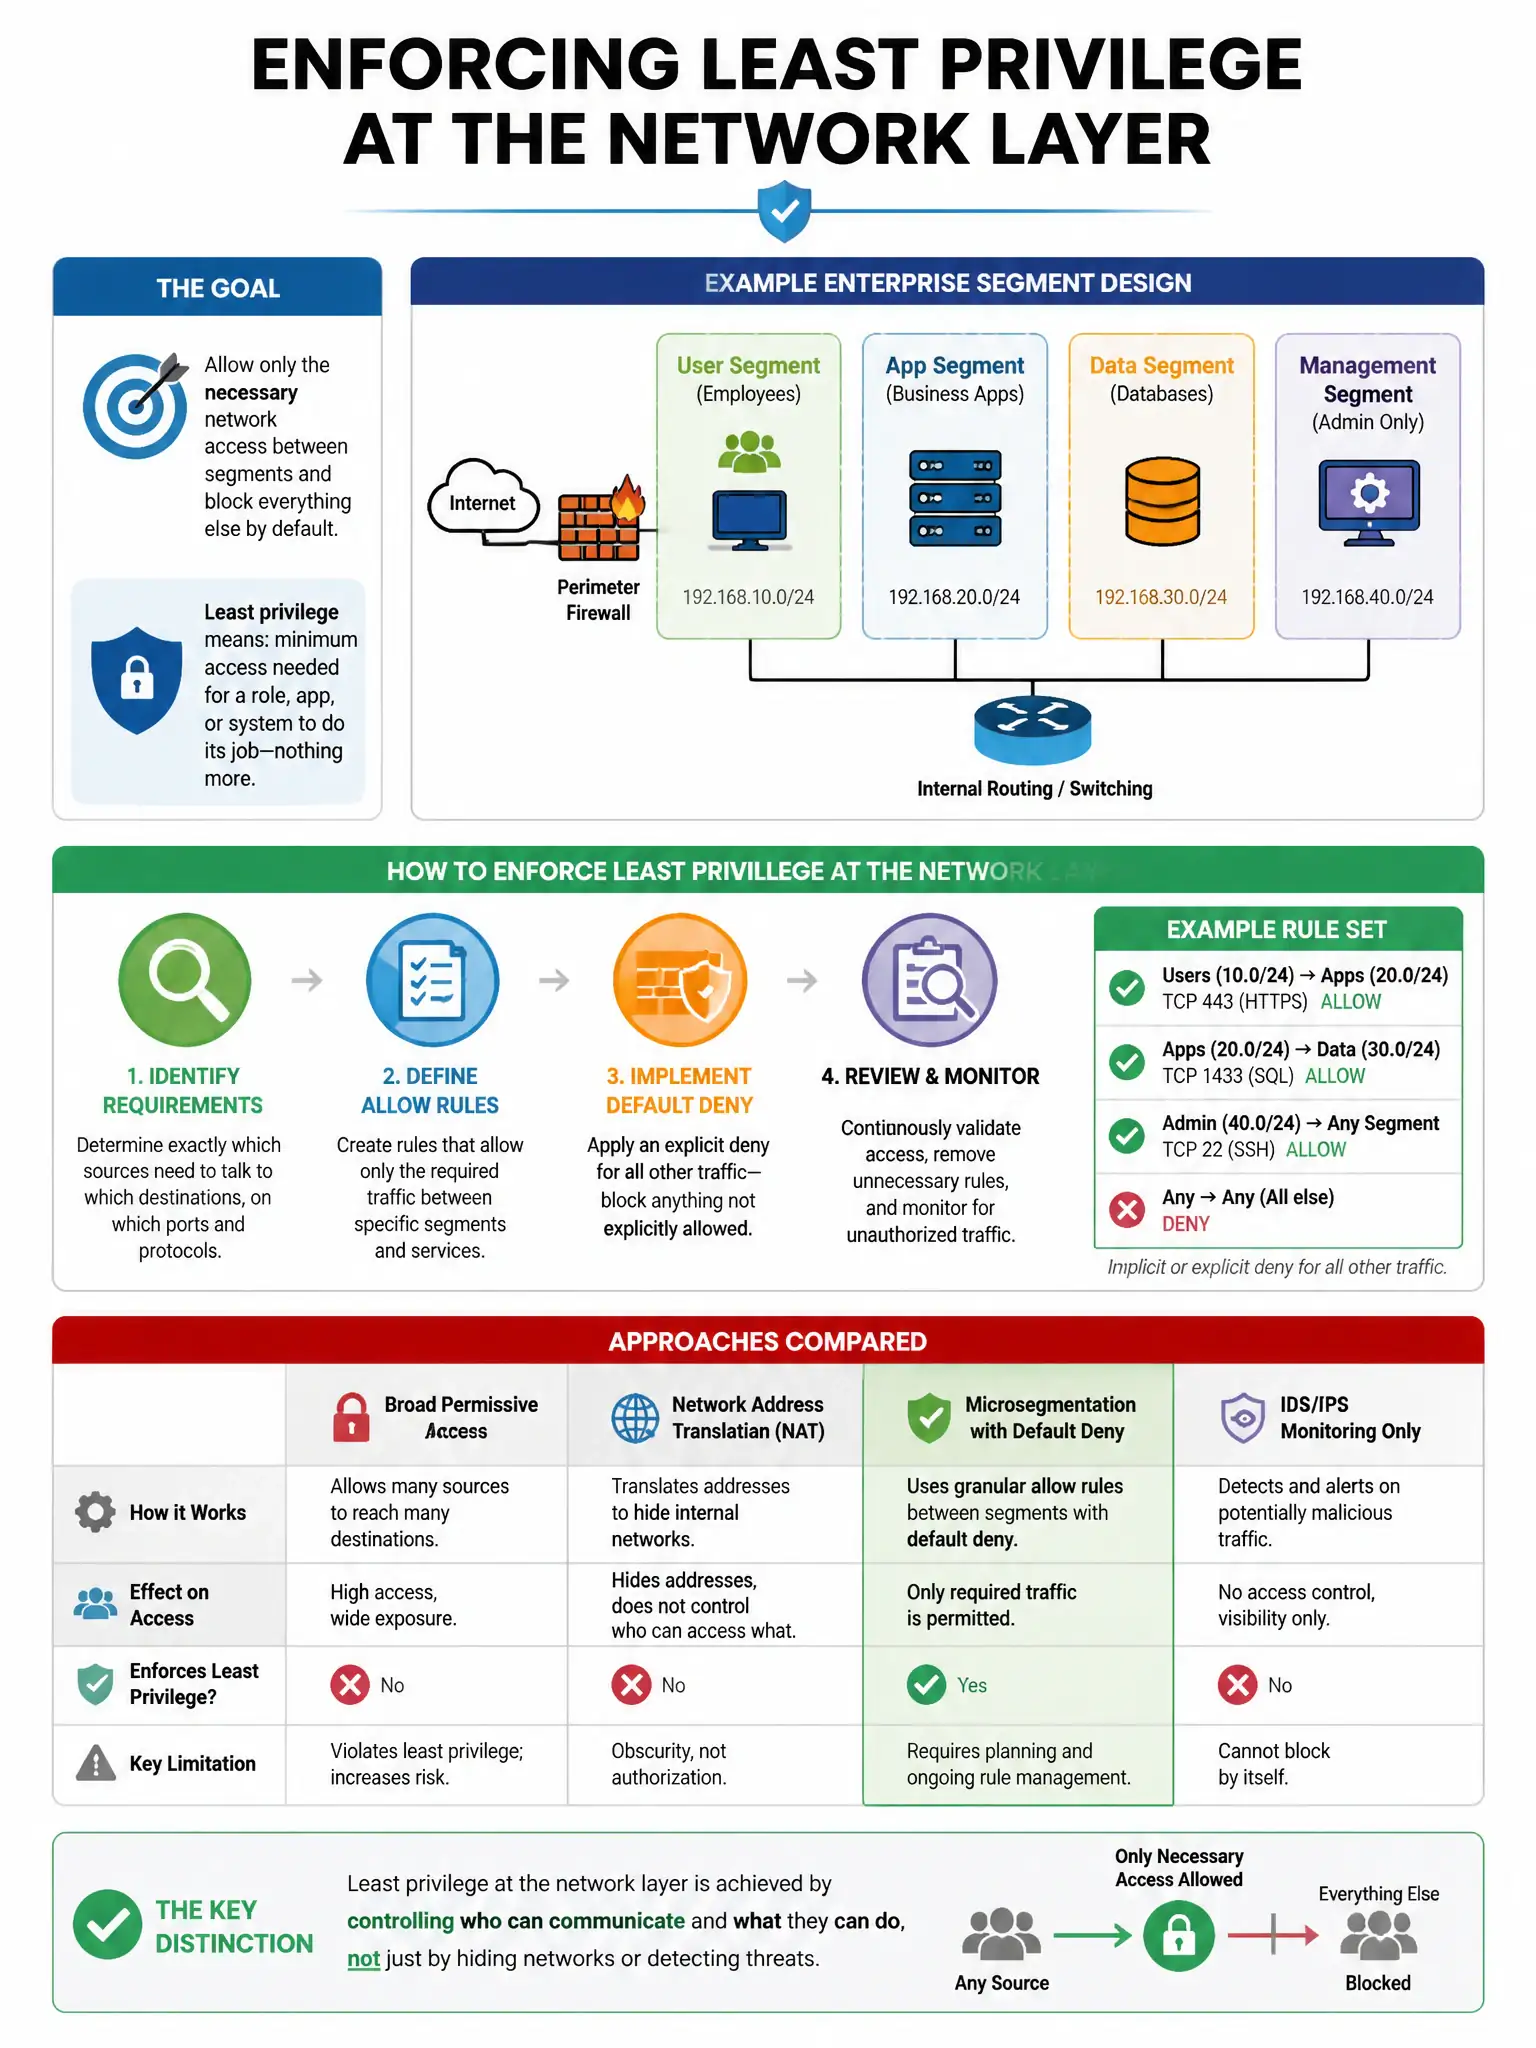
Here's the deal — you want micro-segmentation with host-based firewall rules enforcing per-flow allow lists because it lets only explicitly approved flows between hosts and limits lateral movement. The flat /16 with a perimeter firewall lets east-west traffic run wild once an attacker gets inside. VLAN tagging without inter-VLAN routing controls and a single core IDS sensor don't enforce least privilege.
Full Explanation
Micro-segmentation with host-based firewall rules enforcing per-flow allow lists is correct because it enforces least privilege by permitting only explicitly approved flows between hosts and limiting lateral movement. The flat /16 network with a perimeter firewall is wrong because east-west traffic can move freely once the perimeter is bypassed. VLAN tagging without inter-VLAN routing controls is wrong because VLANs alone do not restrict traffic between segments. The single IDS sensor on the core switch uplink is wrong because it provides visibility but does not enforce network access controls.