
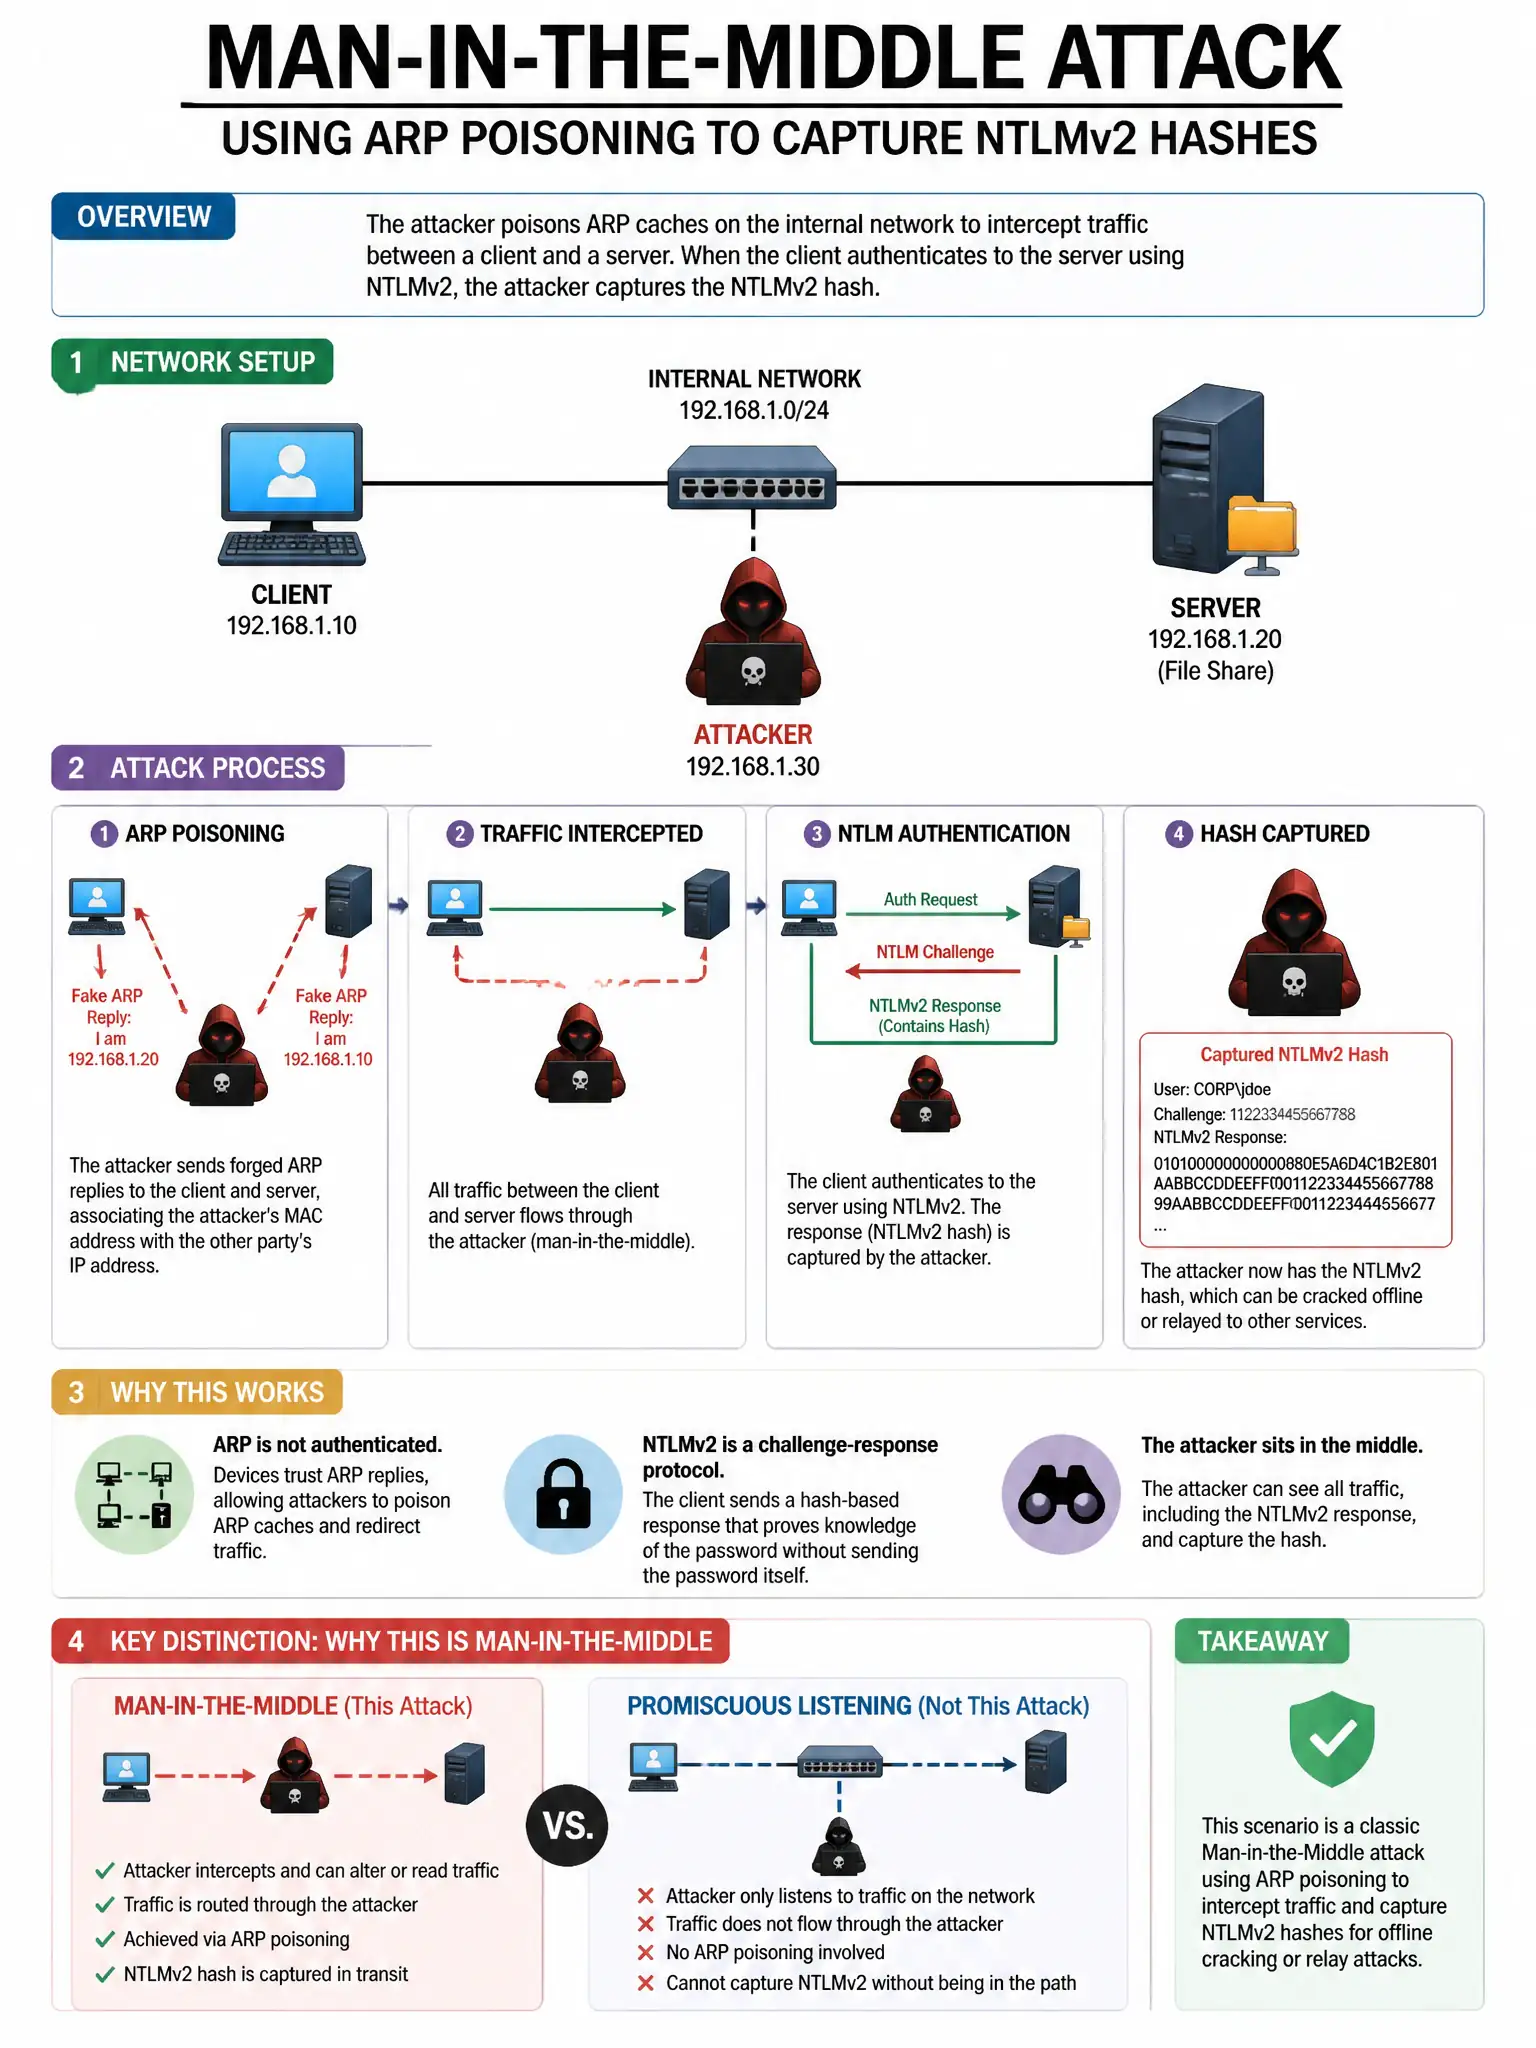
A network penetration tester successfully performs a man-in-the-middle attack on an internal network using ARP poisoning and captures NTLMv2 hashes. Which technique represents the correct next step to leverage this access?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you crack those NTLMv2 hashes offline with hashcat, or you relay them to services that accept NTLM auth. That's how you turn the captured hashes into access without dumping them on someone else.
Full Explanation
The correct next step is to crack the captured NTLMv2 hashes offline with hashcat and a wordlist, or to use NTLM relay to authenticate against other services that accept NTLM authentication, such as with Responder and ntlmrelayx. Offline cracking uses only the tester's own hardware, while relay can leverage the captured challenge-response without first recovering the password. The option to forward the hashes to the client's IT team immediately is wrong because it is premature during the assessment and the hashes must be handled securely under the engagement rules. The option to use the hashes directly to log into Windows systems via Pass-the-Hash with NTLMv2 is wrong because NTLMv2 challenge-response hashes are not directly usable for Pass-the-Hash, which requires NT hashes rather than NTLMv2 responses. The option to submit the hashes to an online cracking service using the client's credentials as input is wrong because it sends client data to an external service and violates data handling obligations and confidentiality.