
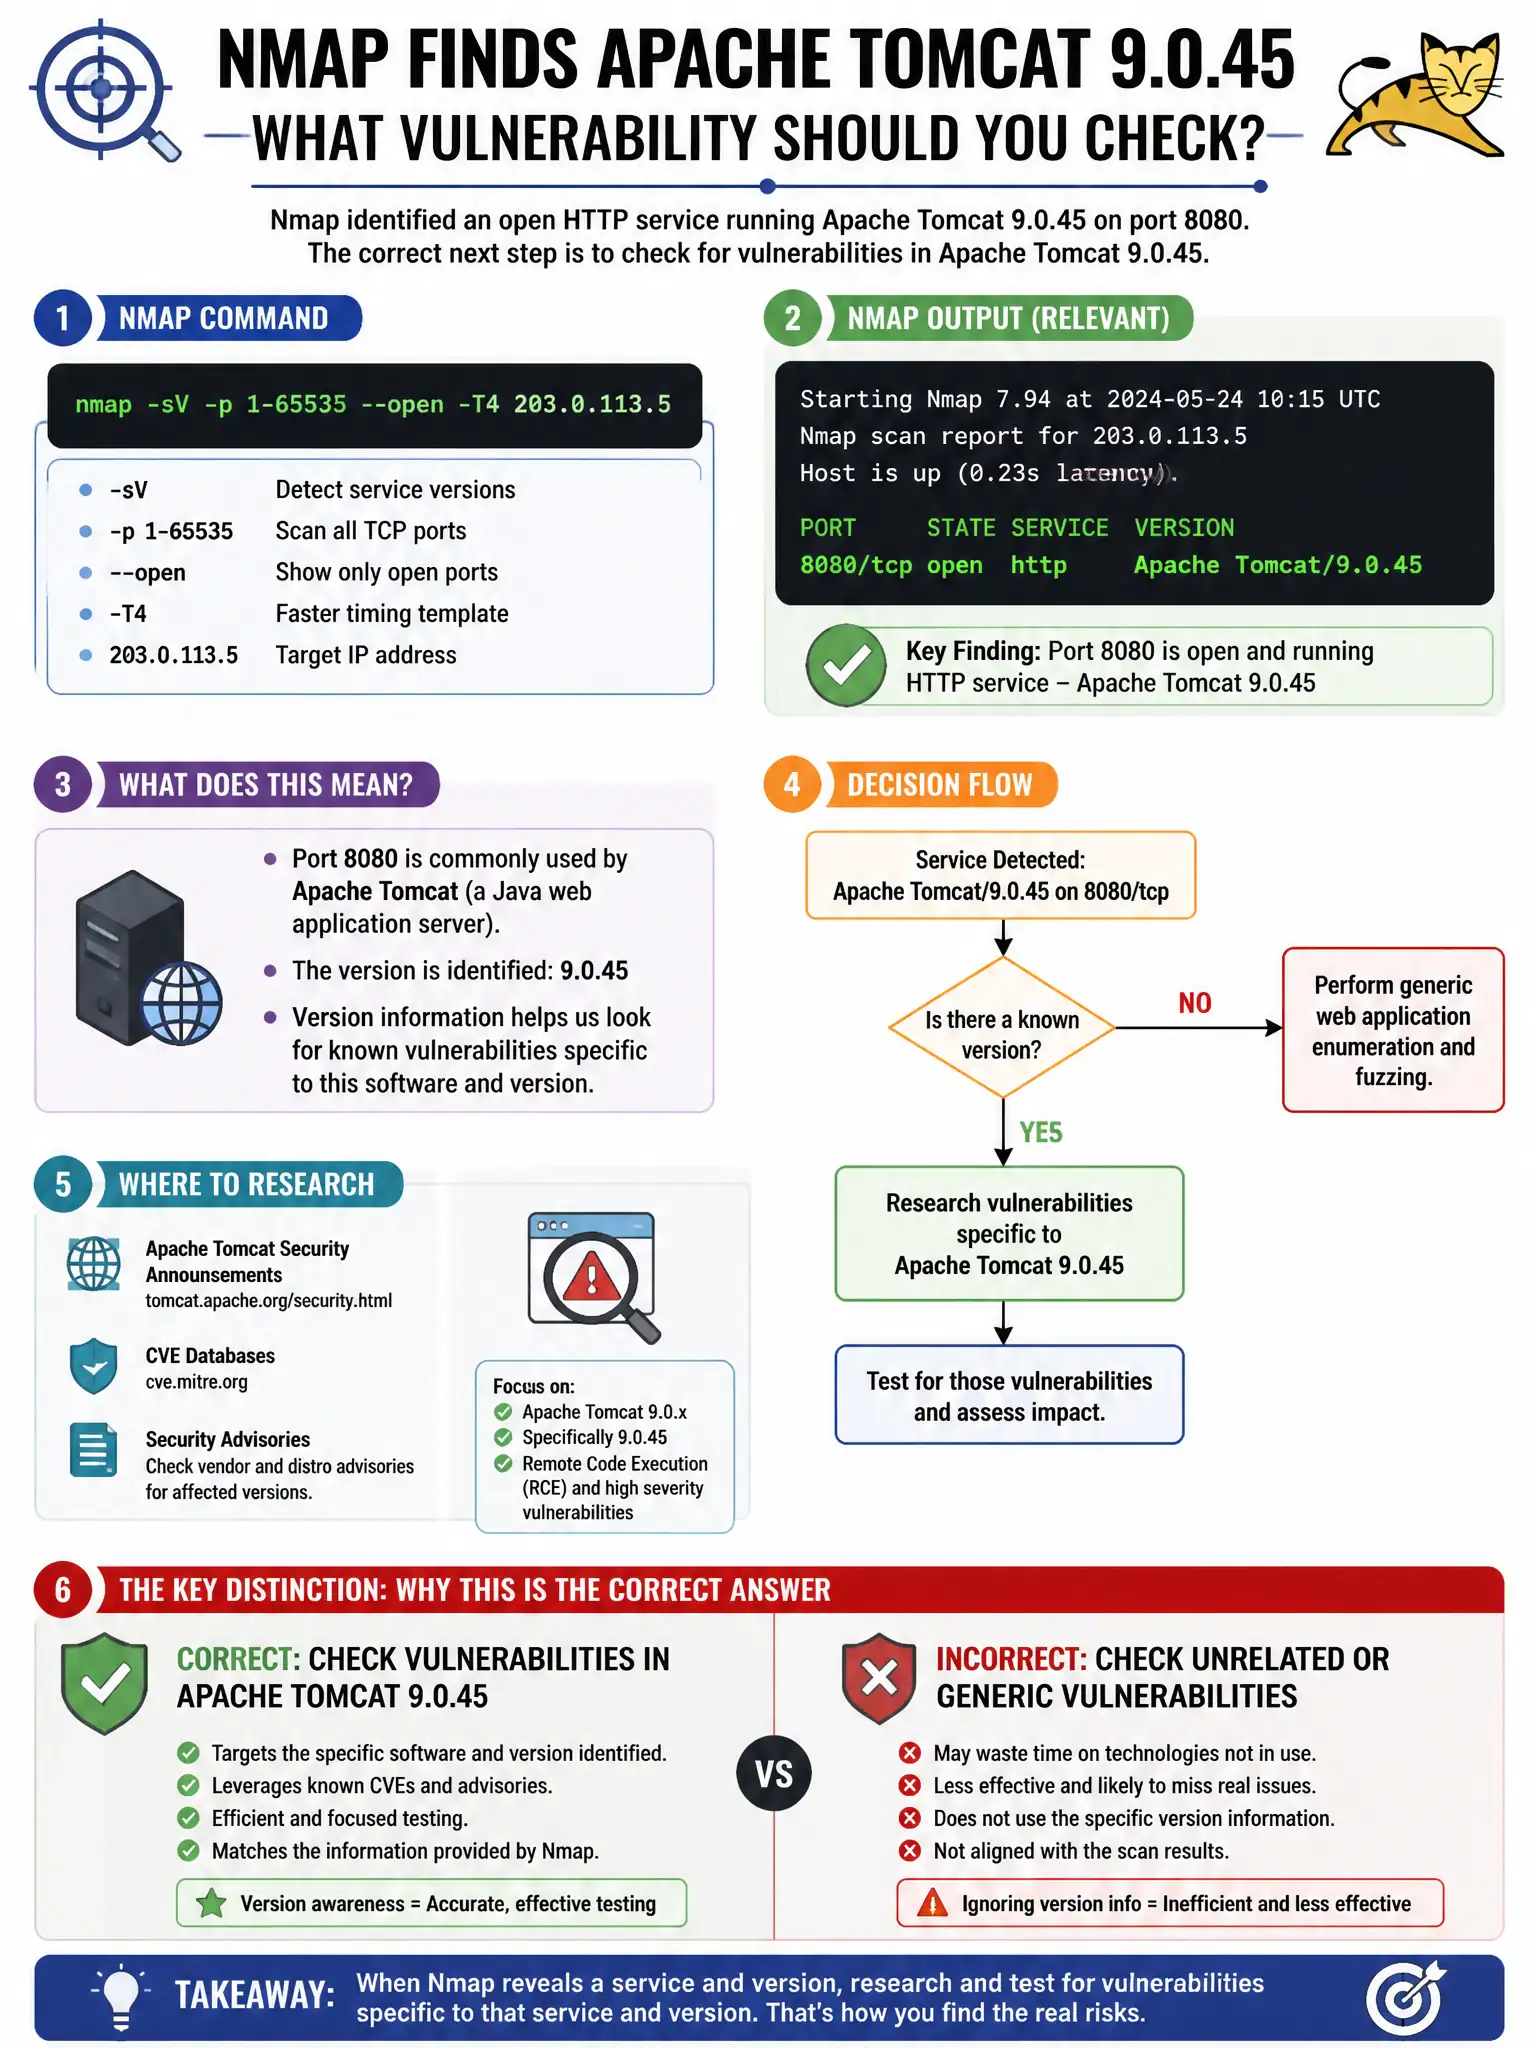
During an nmap scan, a tester runs: nmap -sV -p 1-65535 --open -T4 203.0.113.5. The output shows port 8080/tcp open http Apache Tomcat/9.0.45. What vulnerability should the tester prioritize investigating based on this result?
Select an answer to reveal the explanation.
Short Explanation
You've got a specific Tomcat version on a non-standard port, so you should research CVEs for Apache Tomcat 9.0.45 and test common high-risk issues like Ghostcat, deserialization, and Tomcat Manager default credentials. Don't dismiss the banner or assume it's just a proxy.
Full Explanation
The result shows a specific Apache Tomcat version, 9.0.45, exposed on port 8080, which gives you a precise attack surface to research. Tomcat has had critical remote code execution issues, including Ghostcat CVE-2020-1938, CVE-2019-0232, AJP connector misconfigurations, and deserialization-related problems, and the Tomcat Manager application with default credentials such as tomcat/tomcat is a common high-severity finding. The claim that Apache Tomcat 9.0.45 has no known vulnerabilities is wrong because all software versions should be checked for CVEs. The claim that port 8080 indicates a proxy and should be tested for SSRF is wrong because port 8080 hosting Tomcat indicates a Java web application, not necessarily a proxy. The claim that the service banner is a false positive and should be dismissed pending a manual curl request is wrong because version banners are typically accurate and should be verified by research rather than dismissed.