
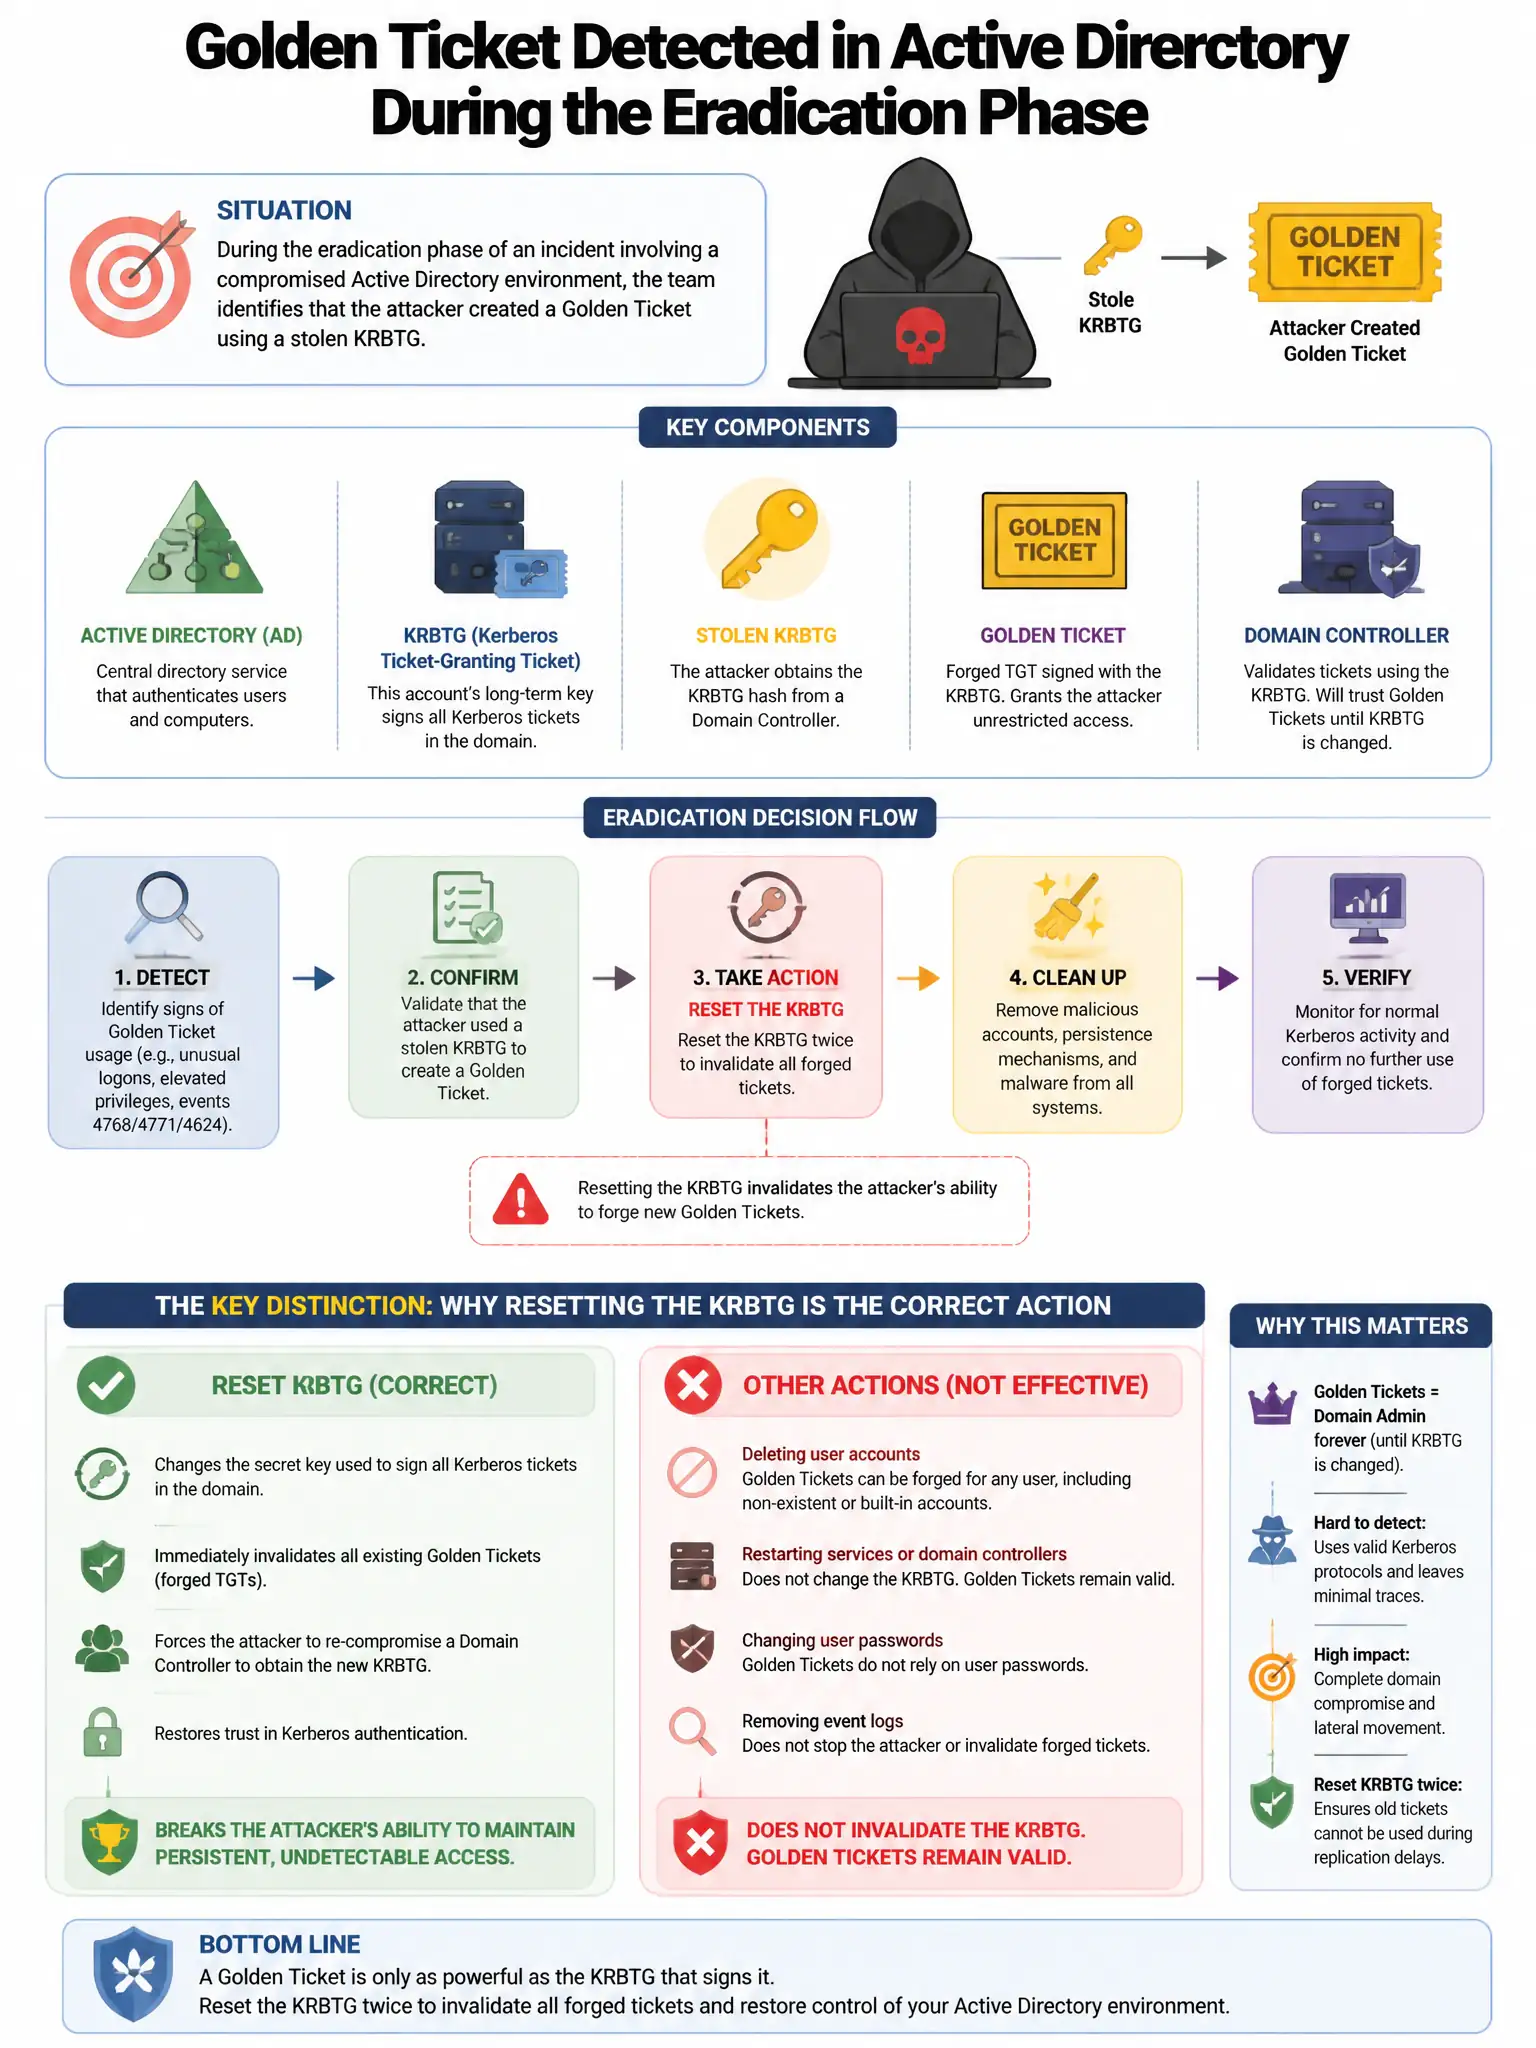
During the eradication phase of an incident involving a compromised Active Directory environment, the team identifies that the attacker created a Golden Ticket using a stolen KRBTGT hash. Which eradication action is specifically required to invalidate all existing Golden Tickets?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — Golden Tickets are signed with the KRBTGT password hash, so you must reset that account's password twice to kill all existing tickets. The second reset clears the old hash from the password history used for backward compatibility.
Full Explanation
Resetting the KRBTGT account password twice, with a delay between resets to allow replication, is required because Golden Tickets are signed using the KRBTGT password hash. The second reset removes the lingering old hash from the password history used for backward compatibility, invalidating all previously issued tickets. Resetting the password of all compromised user accounts is wrong because it does not affect Kerberos tickets already issued with the KRBTGT hash. Revoking all SSL certificates on domain controllers is wrong because SSL certificates are unrelated to Kerberos ticket validation. Rebuilding all domain-joined workstations is wrong because workstation rebuilds do not invalidate tickets already held by the attacker.