
An organization is implementing a SIEM platform. Which log source combination should be prioritized for initial ingestion to maximize threat detection capability?
Select an answer to reveal the explanation.
Short Explanation
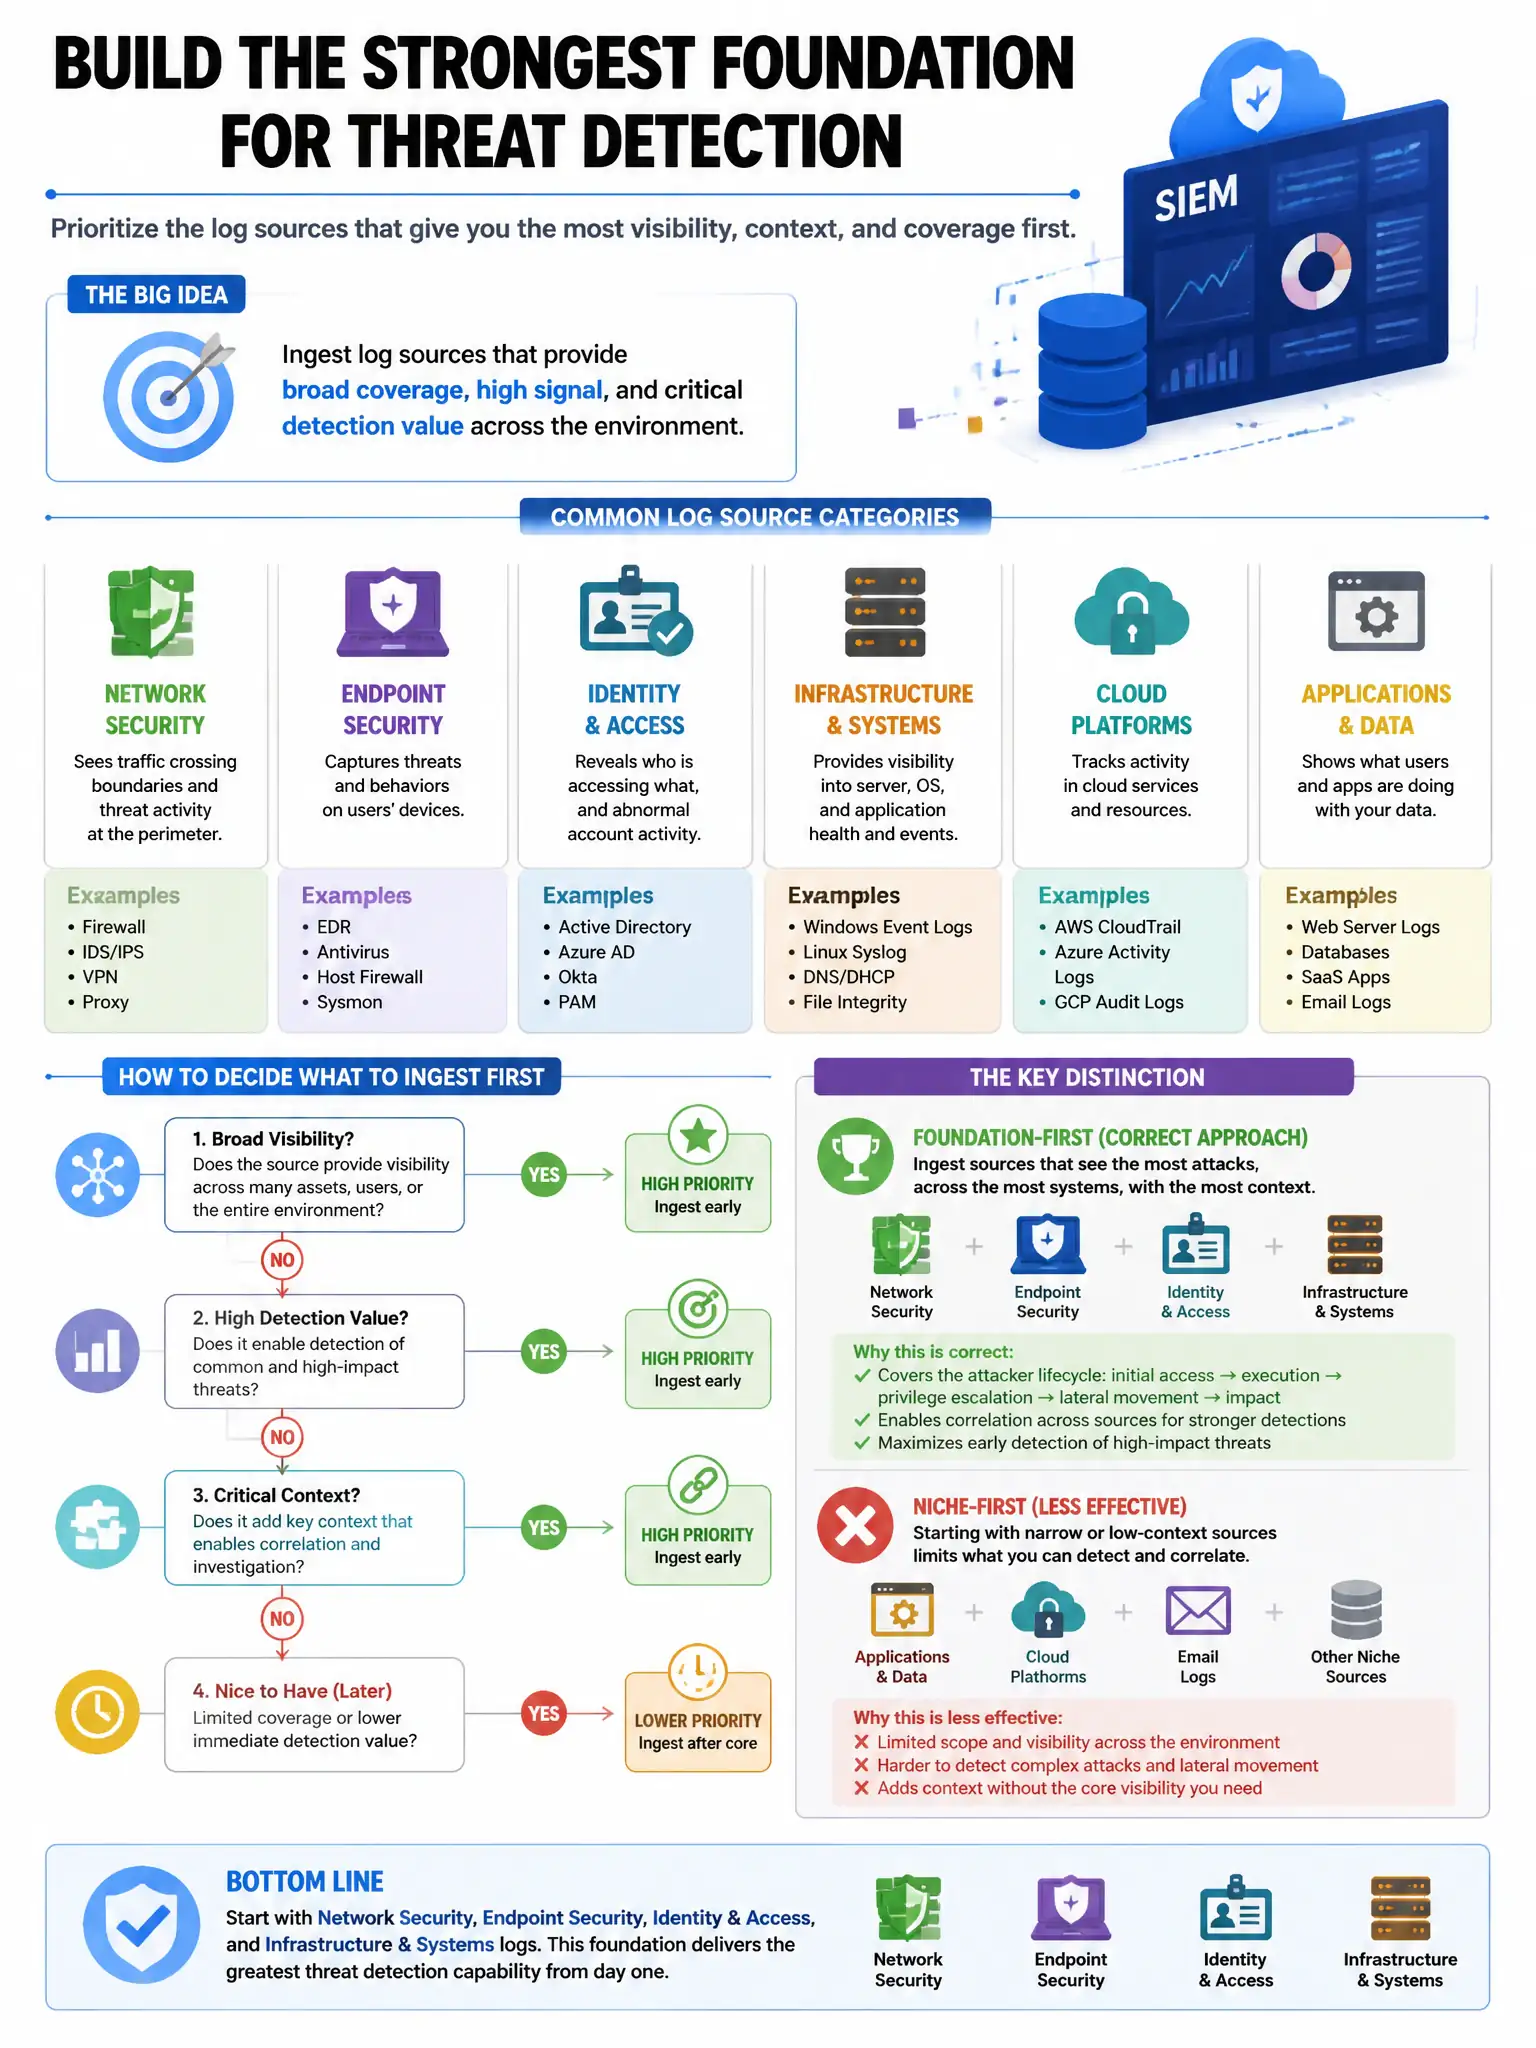
You want the combination that covers the network edge, identity, DNS, and endpoints. Firewall logs show connection attempts and policy violations, Active Directory logs catch credential abuse and lateral movement, DNS logs reveal C2 and DGA activity, and endpoint security logs capture malware. That gives you the strongest initial SIEM threat detection coverage.
Full Explanation
The correct combination is perimeter firewall logs, Active Directory authentication logs, DNS query logs, and endpoint security logs. Firewall logs reveal connection attempts and policy violations; Active Directory logs detect credential abuse and lateral movement; DNS logs expose C2 communication and DGA activity; endpoint security logs capture malware activity. These sources cover the most critical attack vectors for initial SIEM coverage. Physical access control system logs and cafeteria badge swipe logs are wrong because physical access logs are useful but not the highest priority for cyber threat detection. Network printer logs and HVAC environmental monitoring system logs are wrong because printer and HVAC logs have minimal value for detecting cyber attacks. Application performance monitoring metrics and database query execution time logs are wrong because application performance metrics are operational, not security-focused.