
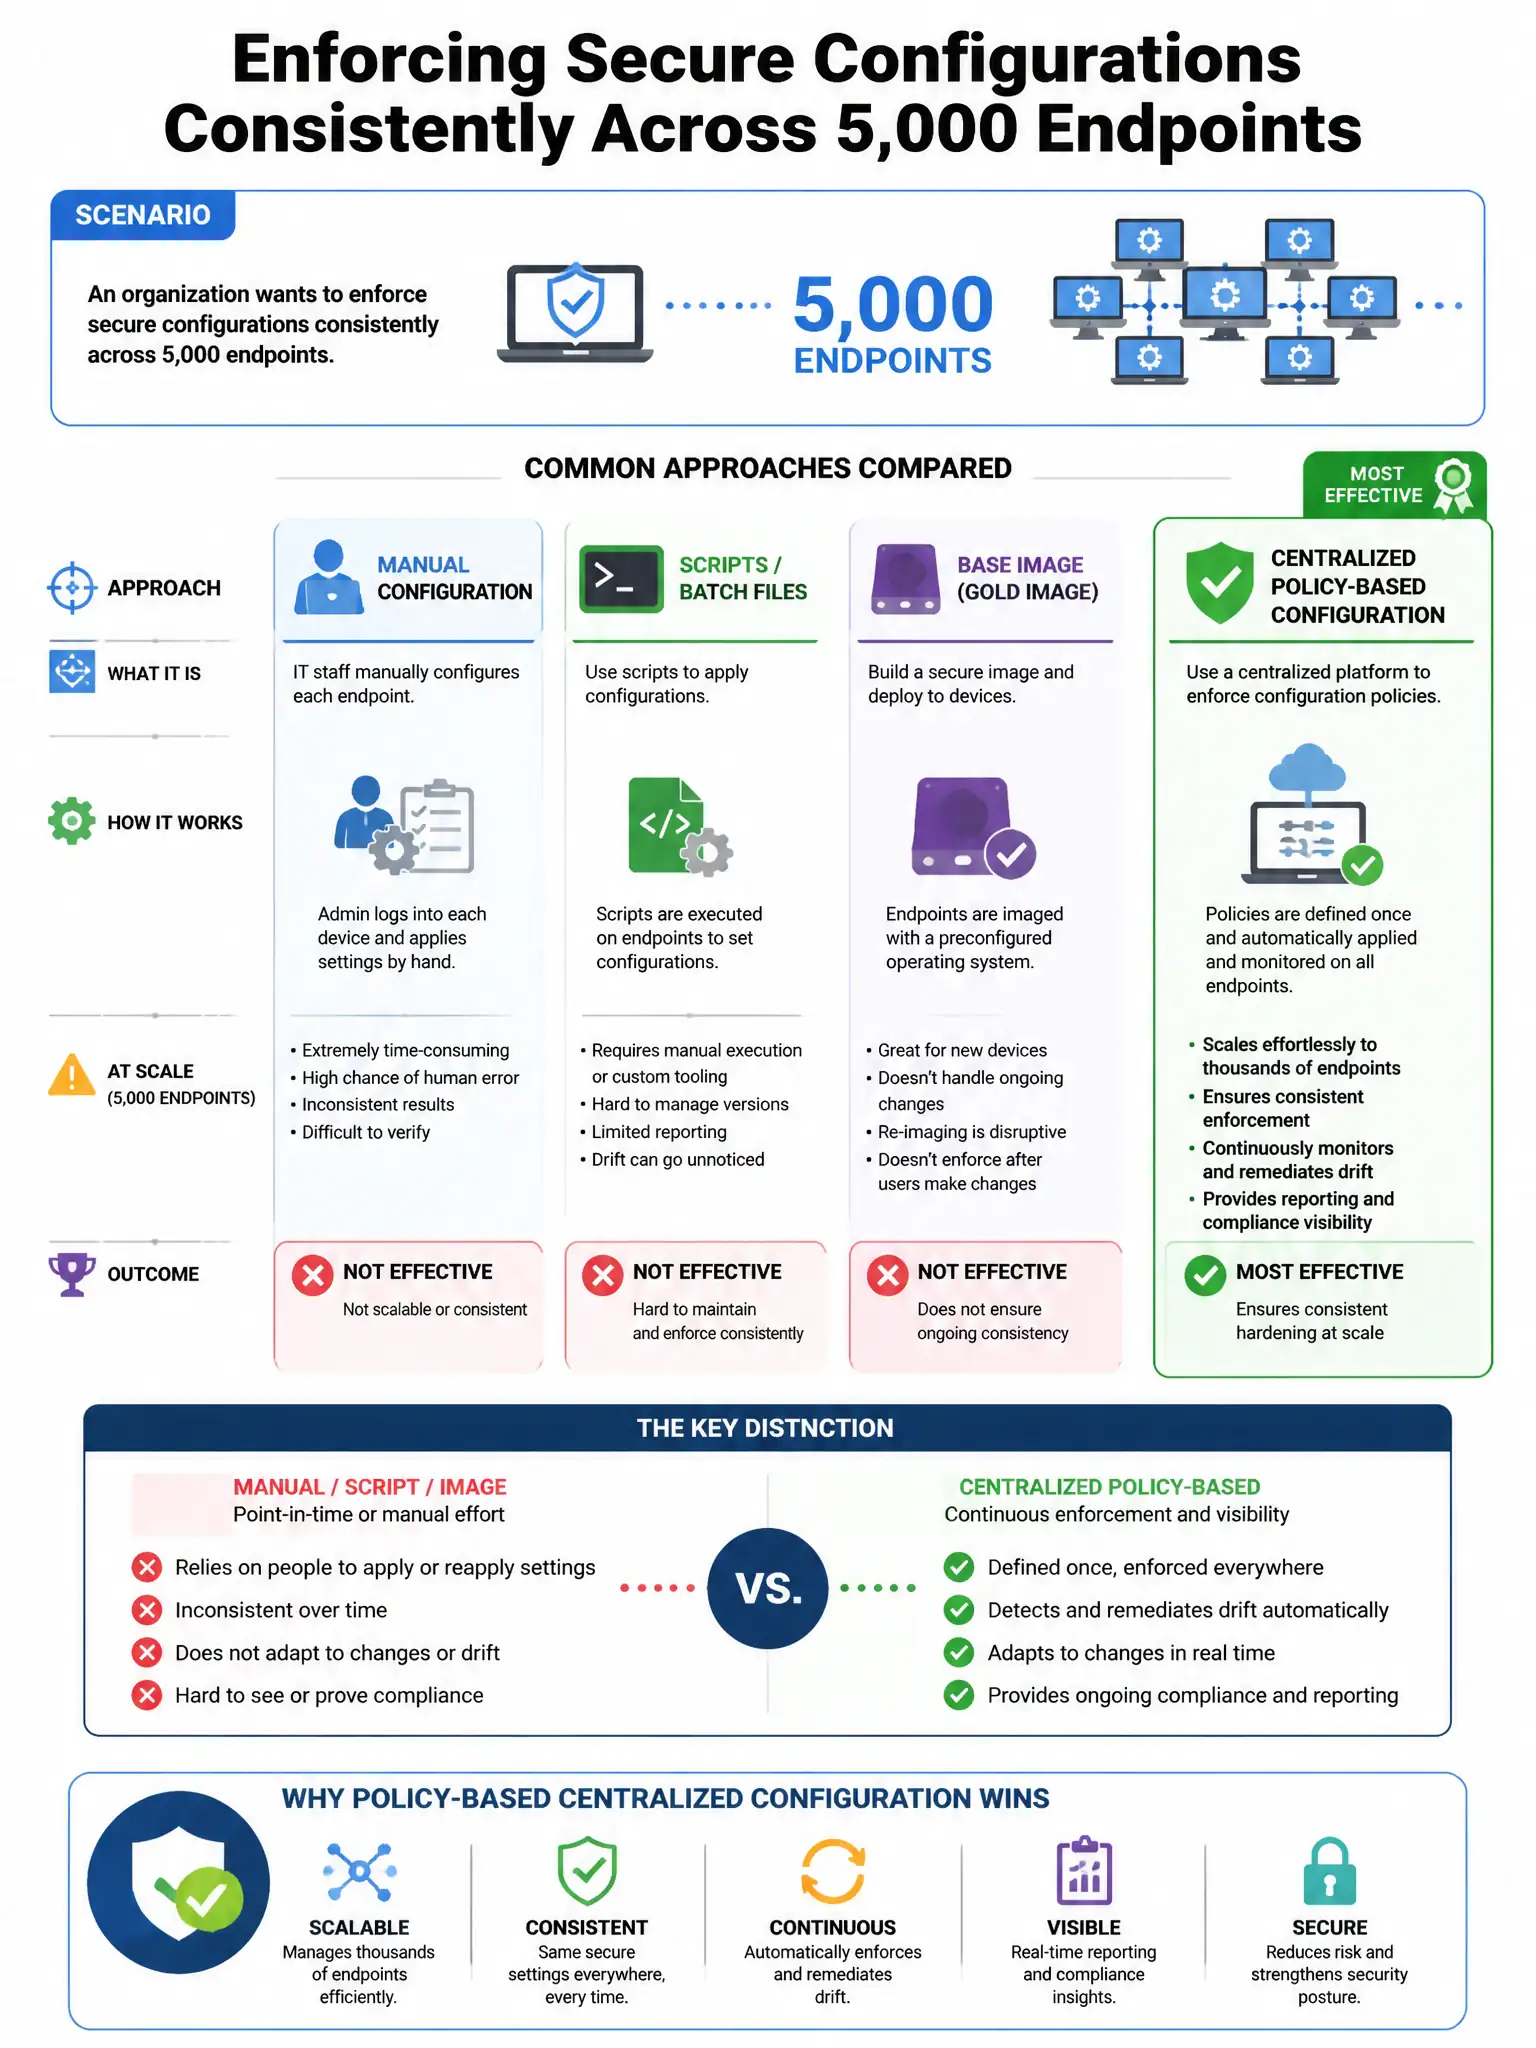
An organization wants to enforce secure configurations consistently across 5,000 endpoints. Which approach MOST effectively ensures consistent hardening at scale?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need configuration management tools such as SCCM, Ansible, or Puppet because they apply CIS benchmark hardening consistently at scale, reduce human error, and continuously verify that settings haven't drifted from the baseline. Manually configuring each endpoint according to a checklist is wrong because it's impractical for 5,000 endpoints, error-prone, and provides no ongoing enforcement against configuration drift.
Full Explanation
The approach that uses configuration management tools such as SCCM, Ansible, or Puppet to automate CIS benchmark application with continuous compliance verification is correct because automated configuration management applies hardening consistently at scale, reduces human error, and enables continuous verification that configurations have not drifted from the baseline. The manual configuration approach is wrong because manually configuring 5,000 endpoints according to a CIS benchmark checklist is impractical, error-prone, and provides no ongoing enforcement against configuration drift. The default OS configuration approach is wrong because default OS configurations include unnecessary services and permissive settings that are not hardened to security baselines. The staff-training approach is wrong because voluntary application of hardening at IT staff convenience does not ensure consistency across the environment.