
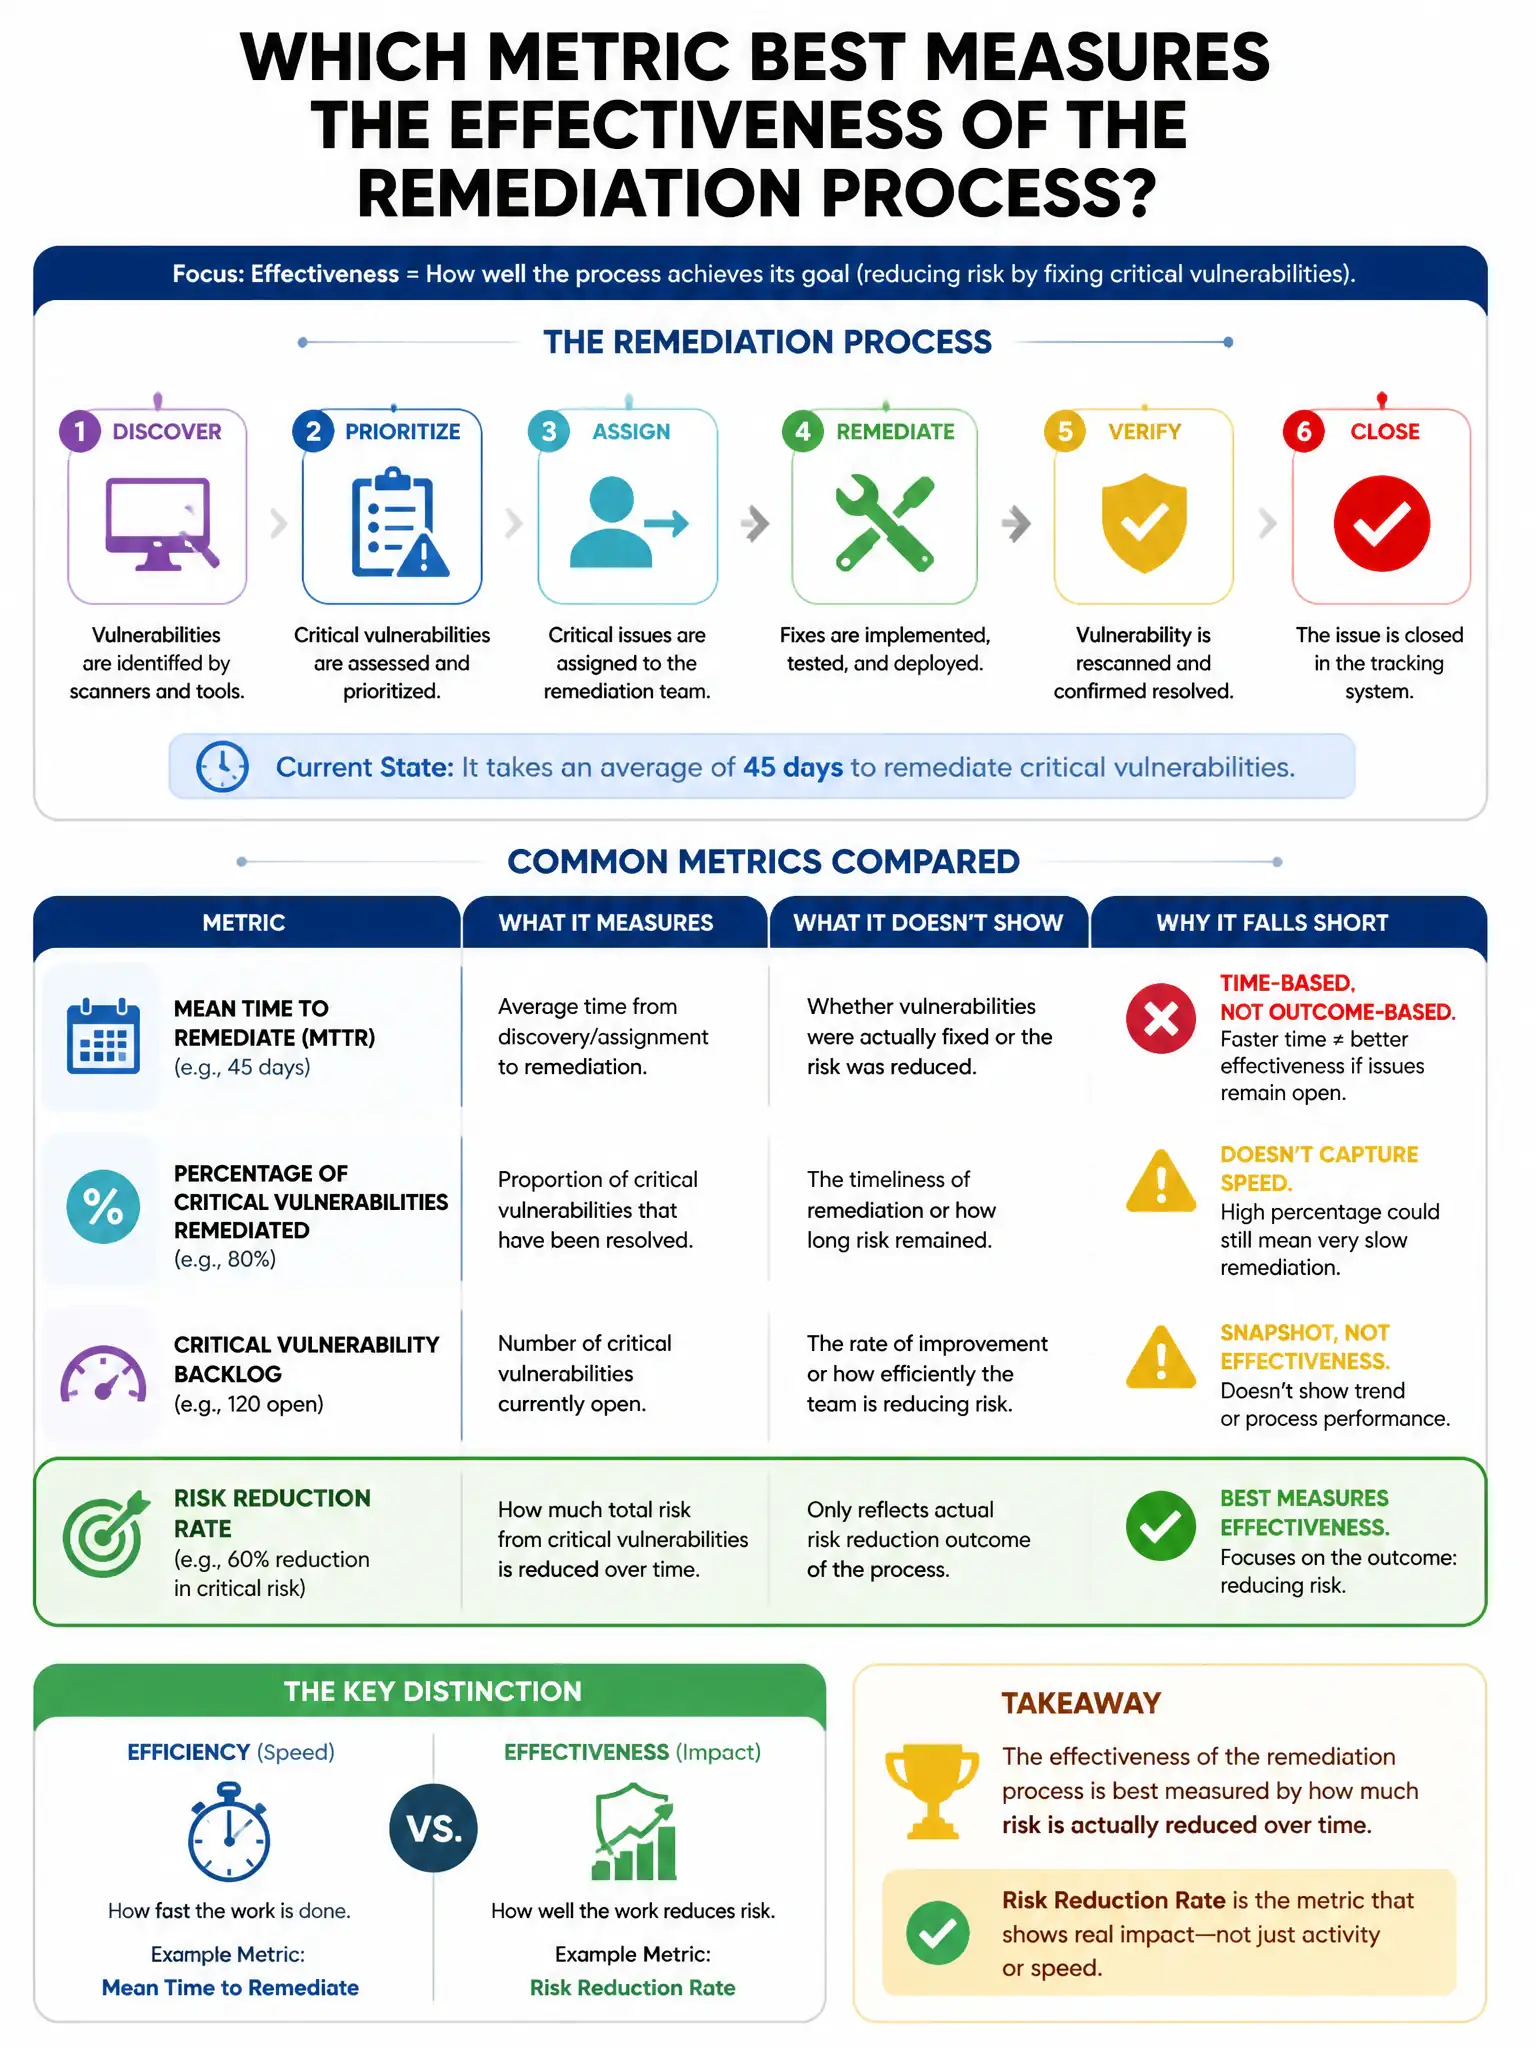
An organization's vulnerability management team takes an average of 45 days to remediate critical vulnerabilities. Which metric BEST measures the effectiveness of the remediation program?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the metric that shows how long critical risks stay open. Mean time to remediate critical vulnerabilities, checked against SLAs and industry benchmarks, tells you whether the remediation program is actually working.
Full Explanation
Mean time to remediate critical vulnerabilities compared against organizational SLAs and industry benchmarks is correct because it directly measures remediation program effectiveness by showing how long the organization remains exposed to critical risks. Comparing against SLAs shows compliance; comparing against benchmarks shows relative program maturity. The total number of vulnerabilities discovered per scan cycle is wrong because it measures discovery capability, not remediation effectiveness. The total number of vulnerability scanners deployed across the environment is wrong because scanner count is an input metric, not an outcome metric. The percentage of scheduled vulnerability scans completed on time is wrong because scan completion measures program execution, not remediation outcomes.