
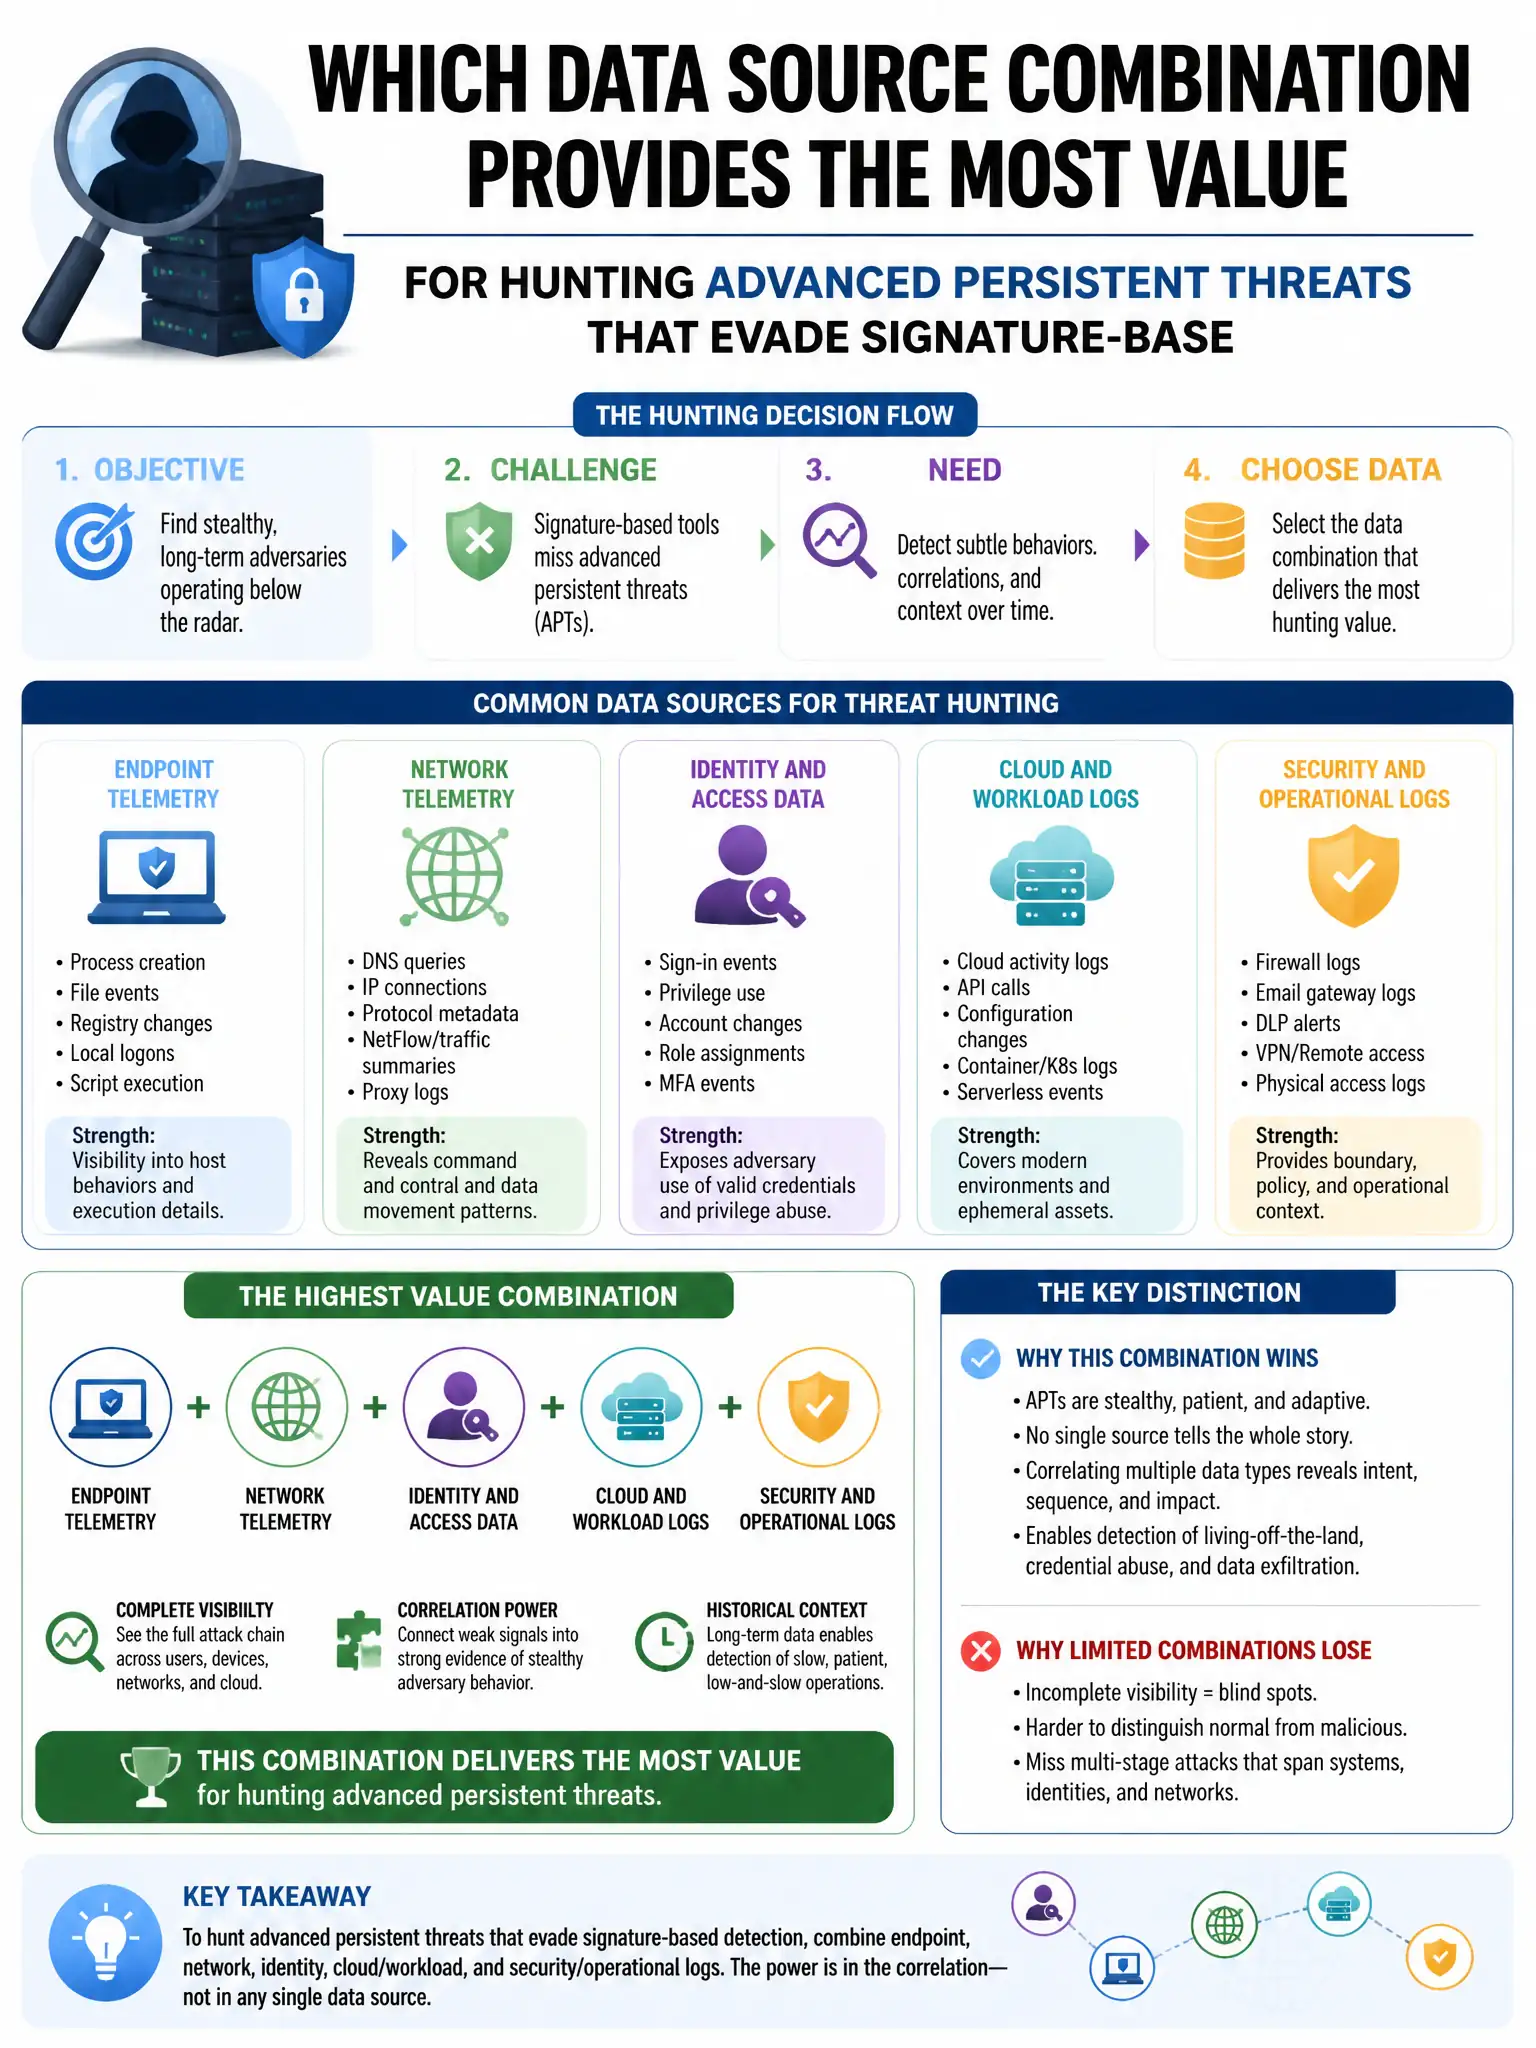
An organization wants to implement a threat hunting program. Which data source combination provides the MOST value for hunting advanced persistent threats that evade signature-based detection?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need network flow data plus endpoint process telemetry because flow shows weird connections and data volumes, while Sysmon or EDR shows what processes are doing. That combo lets you hunt behaviors that signatures miss.
Full Explanation
The correct combination is network flow data (NetFlow/IPFIX) paired with endpoint process telemetry from Sysmon or an EDR platform. Network flow data reveals anomalous connection patterns and data volumes, while endpoint telemetry captures attacker behavior — process creation, network connections, file writes — that bypasses signatures. Together they enable behavioral hunting. Firewall deny logs only are wrong because deny logs only show blocked traffic; advanced persistent threats use allowed channels like HTTPS and DNS. Email gateway spam statistics showing phishing volume trends are wrong because spam statistics reveal phishing volume but not post-compromise behavior. Physical access control system logs for badge entry and exit events are wrong because physical access logs are useful for insider threat investigations but not advanced persistent threat behavioral hunting.