
After containing an incident involving compromised administrative credentials, the IR team is in the recovery phase. Which action is MOST critical before returning affected systems to production?
Select an answer to reveal the explanation.
Short Explanation
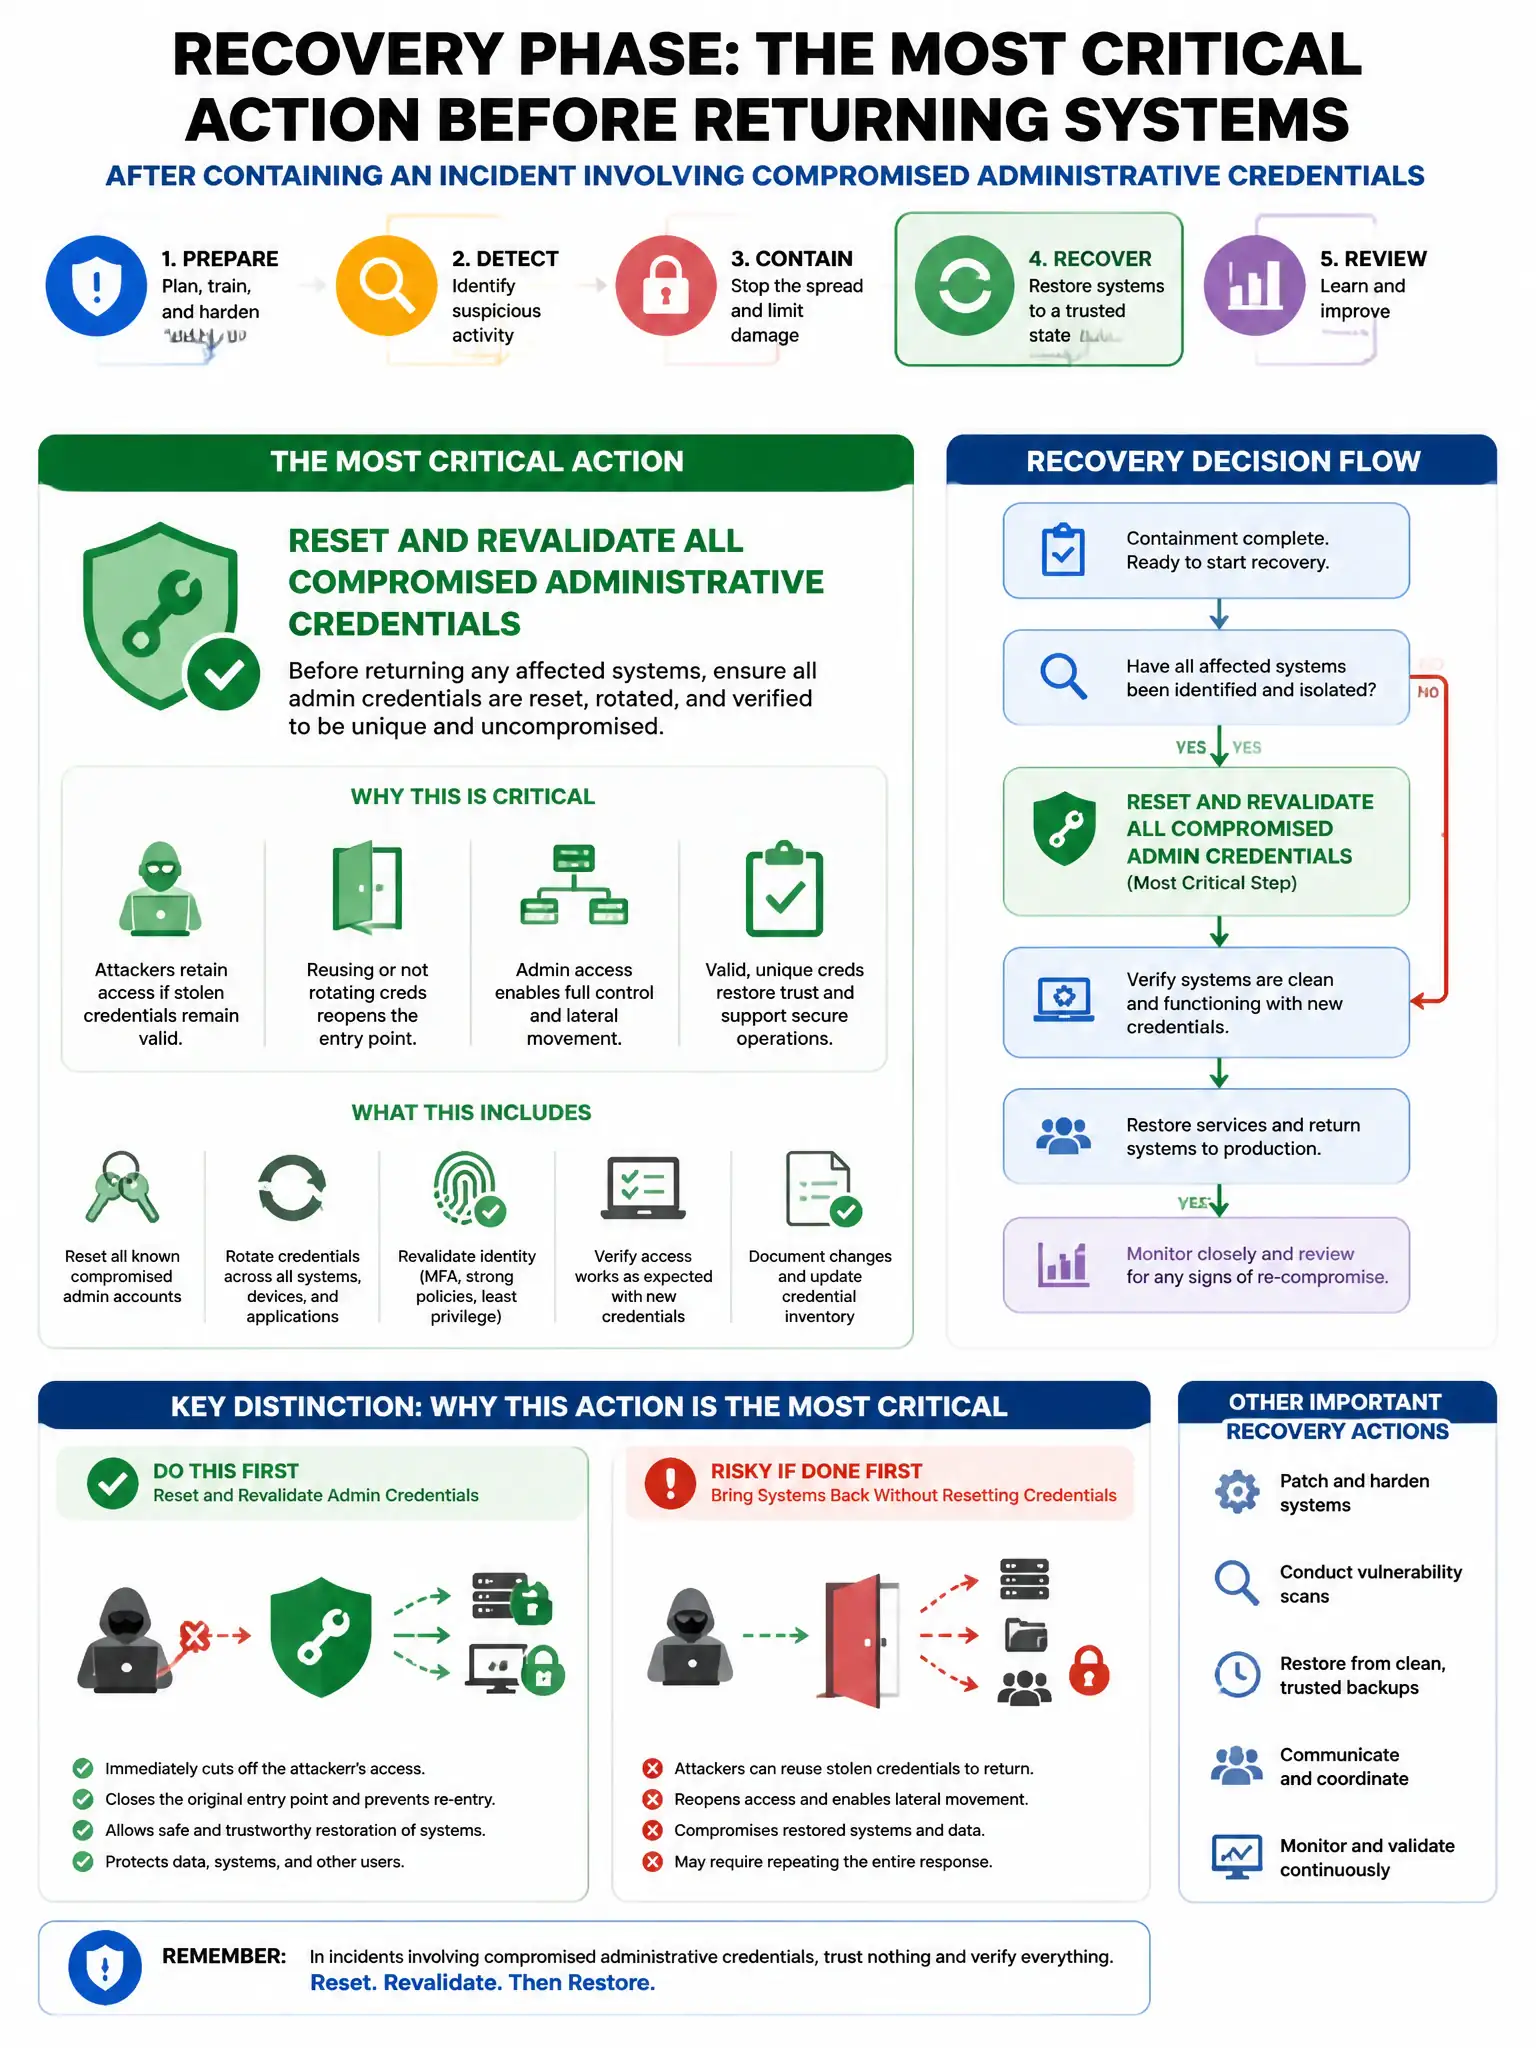
Here's the deal — you've got to reset all potentially compromised credentials, remove persistence mechanisms, and deploy enhanced monitoring before putting systems back in production. If you don't, the attacker can walk right back in.
Full Explanation
Resetting all potentially compromised credentials, verifying all persistence mechanisms have been removed, and deploying enhanced monitoring before returning systems to production is correct. Returning systems without resetting compromised credentials lets the attacker regain access immediately. All backdoors must be removed, and enhanced monitoring must be deployed to detect return activity. Installing the latest version of all software packages is wrong because updates are good practice but do not address compromised credentials. Notifying all company employees via a company-wide email announcement is wrong because notification may be required but is not the most critical technical step before production. Restoring from the most recent backup regardless of when it was taken is wrong because restoring from backup without knowing the initial infection date may restore already-compromised systems.