
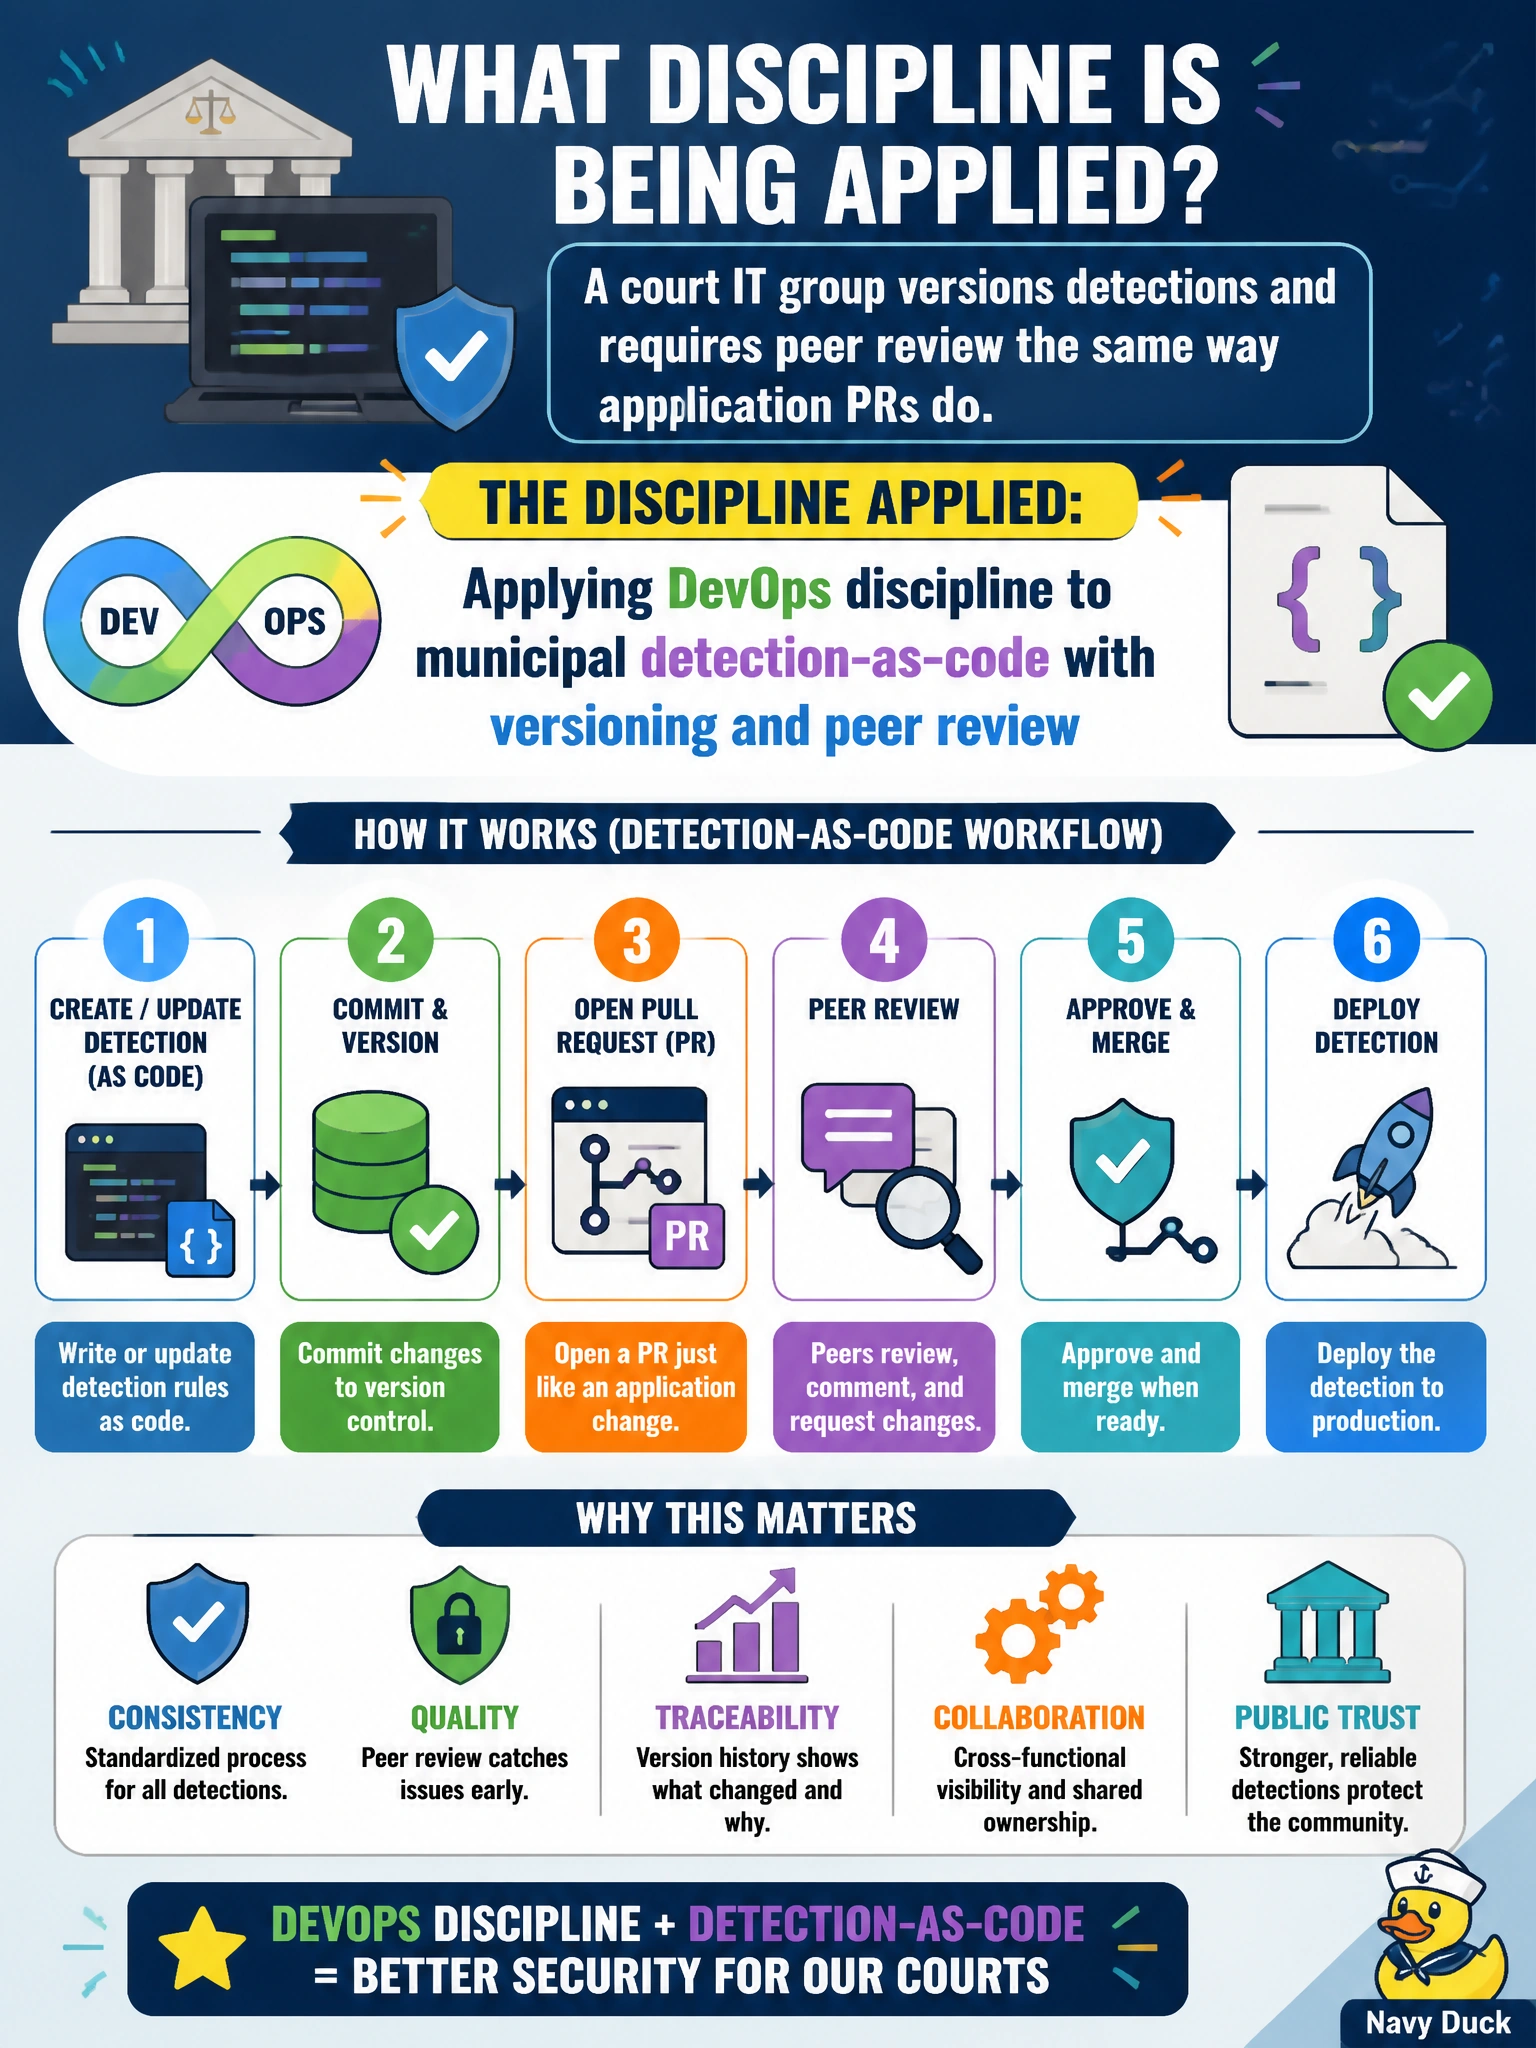
A court IT group versions detections and requires peer review the same way application PRs do. What discipline is that applying?
Select an answer to reveal the explanation.
Short Explanation
Detections are code—version them and peer-review them like any civic app PR. An ITIL change ticket, a threat-intel exchange share, or a SOAR playbook run won't give you DevOps PR discipline even when they're versioned, as they're about approvals, distribution, and response. That's what detection-as-code brings to the SIEM.
Full Explanation
A court IT group that versions detections and requires peer review the same way application PRs do is applying DevOps discipline to municipal detection-as-code with versioning and peer review. Detections are production logic with outage and miss risk; version history, diffs, reviewers, and CI attach accountability and rollback to every change. Courts benefit especially because auditability and separation of duties are cultural expectations—live silent edits in the SIEM console fight that culture. Why the other options fail by concept: Coordinating municipal detection-as-code via ITIL change control with versioning and peer review mislabels the discipline — ITIL change control is ticketed approvals and CAB gating, not DevOps PR-based versioning and peer review of the detection logic itself. Sharing municipal detection-as-code via threat intel exchange with versioning and peer review describes distributing detections to outside peers, not the internal DevOps discipline of versioning and peer-reviewing the court's own detection logic via PRs, which is what the stem is testing. Executing municipal detection-as-code via SOAR playbooks with versioning and peer review describes automating what happens after a detection fires, not the DevOps discipline for how the detection rule itself is written, versioned, and reviewed before it ever runs. Exam caveat: peer review should include detection content experts, not only generic code reviewers who cannot judge false-positive risk on court case-management telemetry. Operational check: store detections in version control, mandate dual review for production promotions, and periodically reconcile the live SIEM rule set to the repository to catch out-of-band console edits.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.