
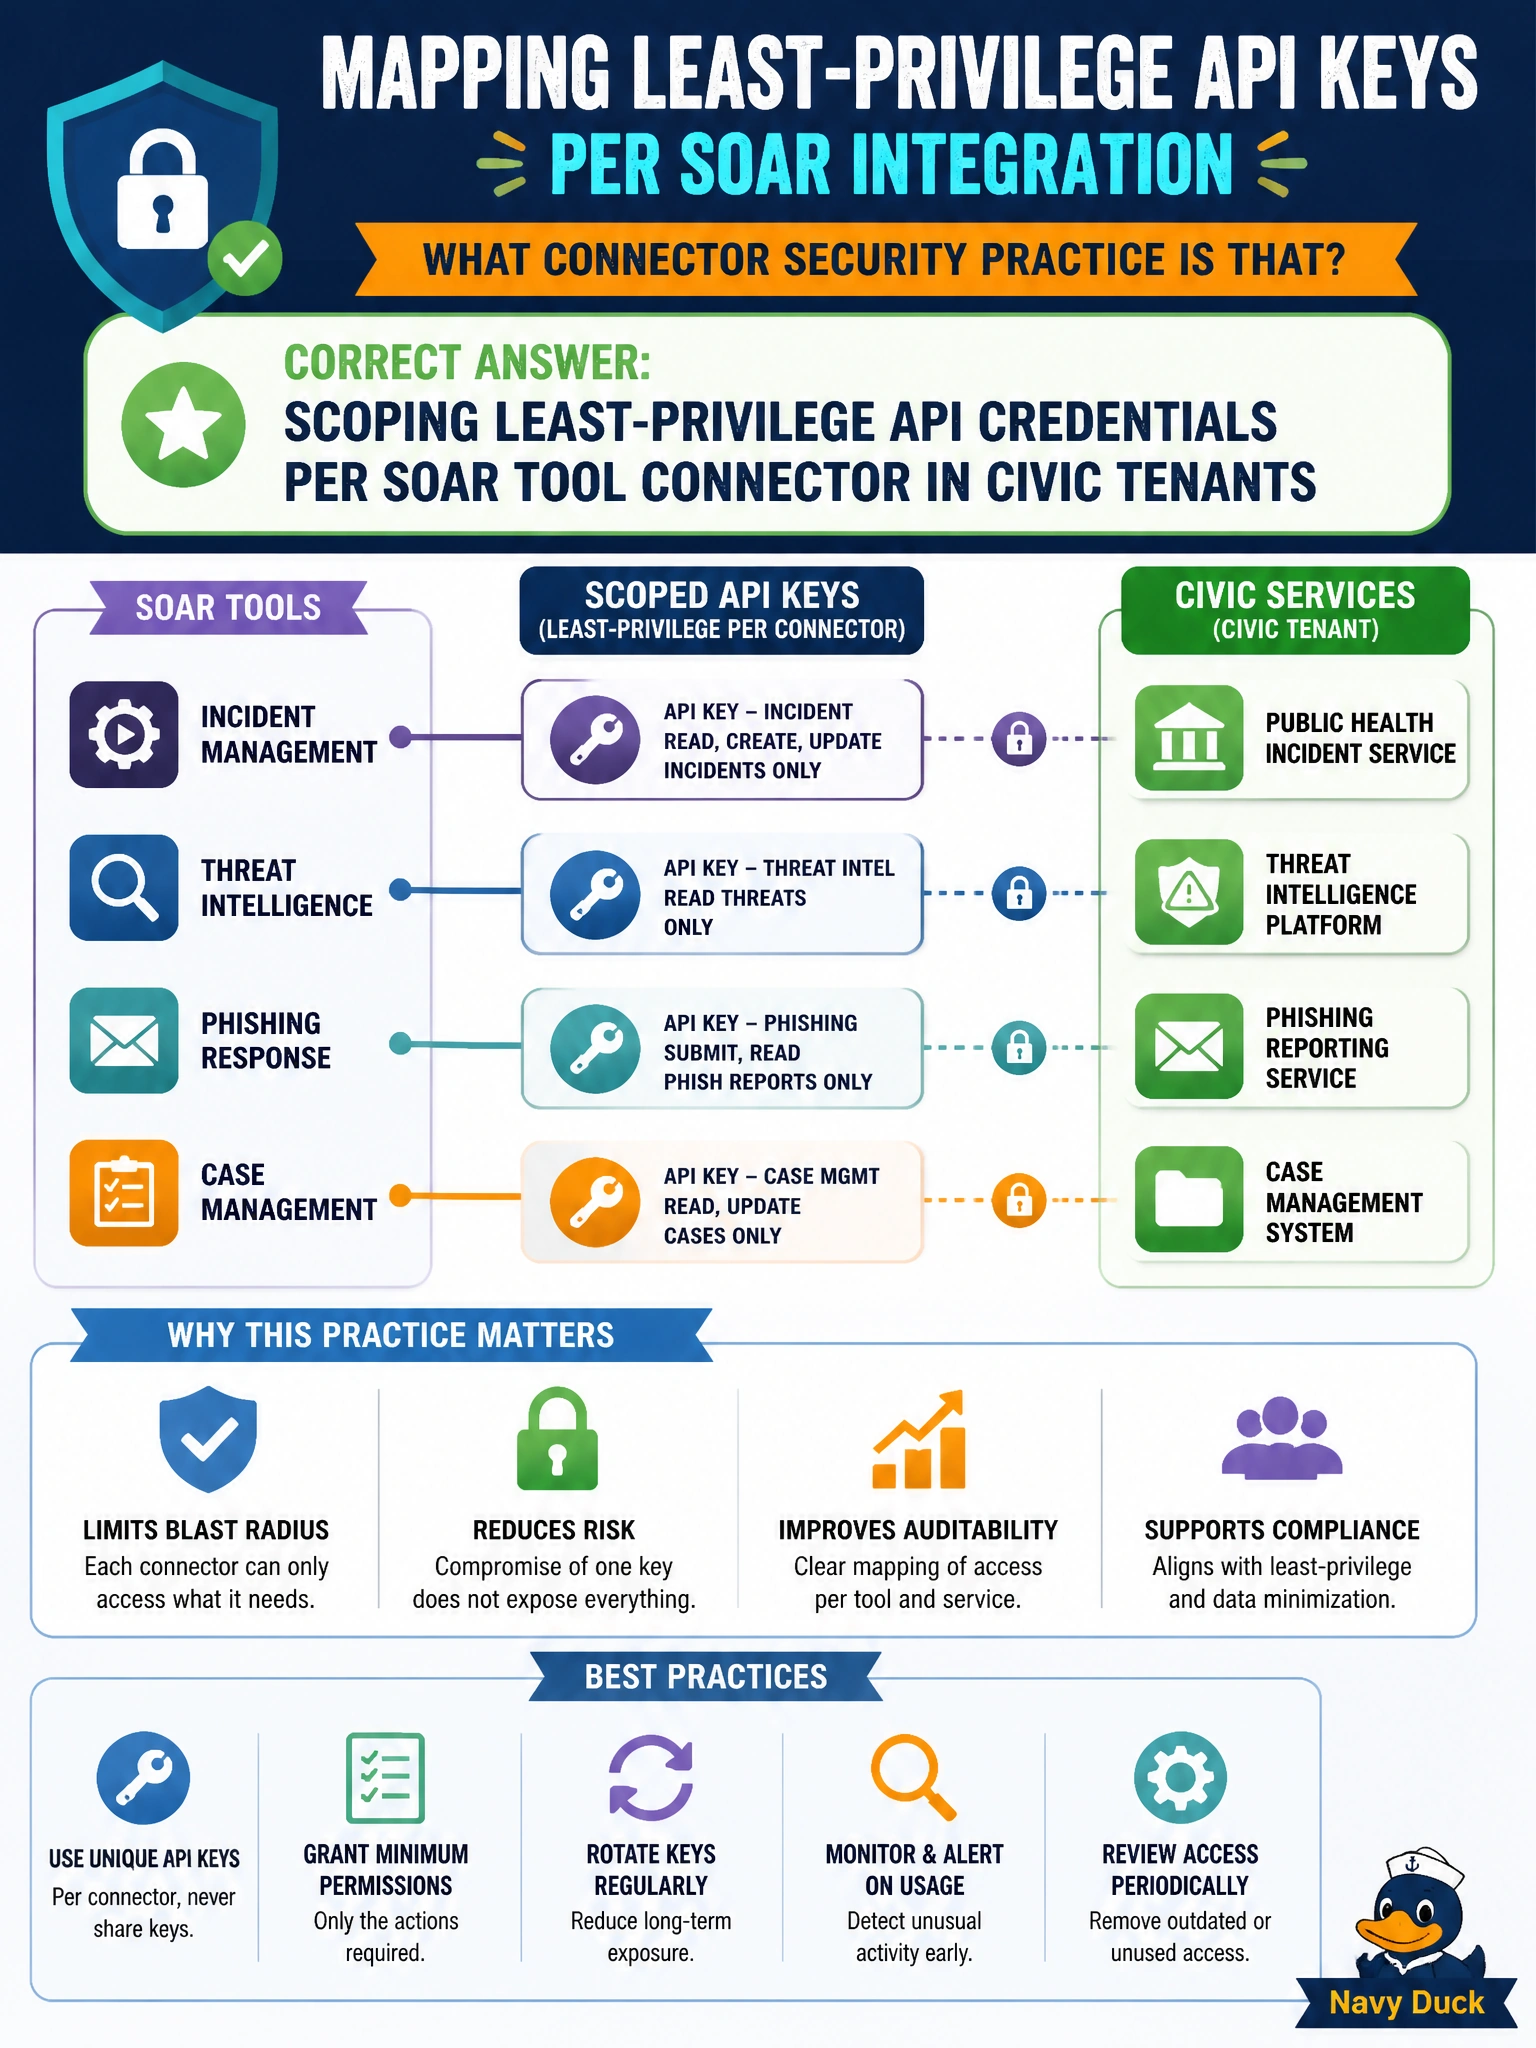
A public-health team maps least-privilege API keys per SOAR integration. What connector security practice is that?
Select an answer to reveal the explanation.
Short Explanation
Giving each playbook its own key still leaves you without per-connector limits, so one workflow calling several tools can reach more than each integration needs. Scoping keys to the central data lake means you'll miss per-connector limits, and tying keys to workstation logins doesn't scope what each integration can do. Least privilege keeps public-health tenants safer.
Full Explanation
A public-health team that maps least-privilege API keys per SOAR integration is hardening connector security in civic tenants. Each tool—EDR, mail, lab systems, ITSM—gets credentials scoped only to the actions that integration needs. Compromising one key then limits blast radius instead of handing an attacker tenant-wide admin through a single stolen secret. Per-connector scoping also clarifies ownership and rotation for health-department compliance reviews. Why the other options fail by concept: Scoping least-privilege API credentials per SOAR automation playbook in civic tenants ties credentials to the workflow rather than to each tool connector, so one playbook calling multiple integrations would carry combined access instead of limiting each EDR, mail, lab, or ITSM integration to only its needed actions. Scoping least-privilege API credentials per central data lake in civic tenants scopes keys to lake storage access rather than to each SOAR tool connector's required API actions, so it does not limit or isolate what each EDR, mail, lab, or ITSM integration is allowed to do. Scoping least-privilege API credentials per analyst workstation login in civic tenants ties credentials to human sign-in rather than to each SOAR connector's required API actions, so it does not restrict what each integration is allowed to do. Exam caveat: Least privilege must be revisited when playbooks add write actions; starting narrow is correct, but undocumented scope creep re-creates overprivilege. Operational check: inventory each SOAR connector's required API scopes, issue dedicated credentials, deny admin-by-default, rotate on a schedule, and alert on use of break-glass elevated keys.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.