
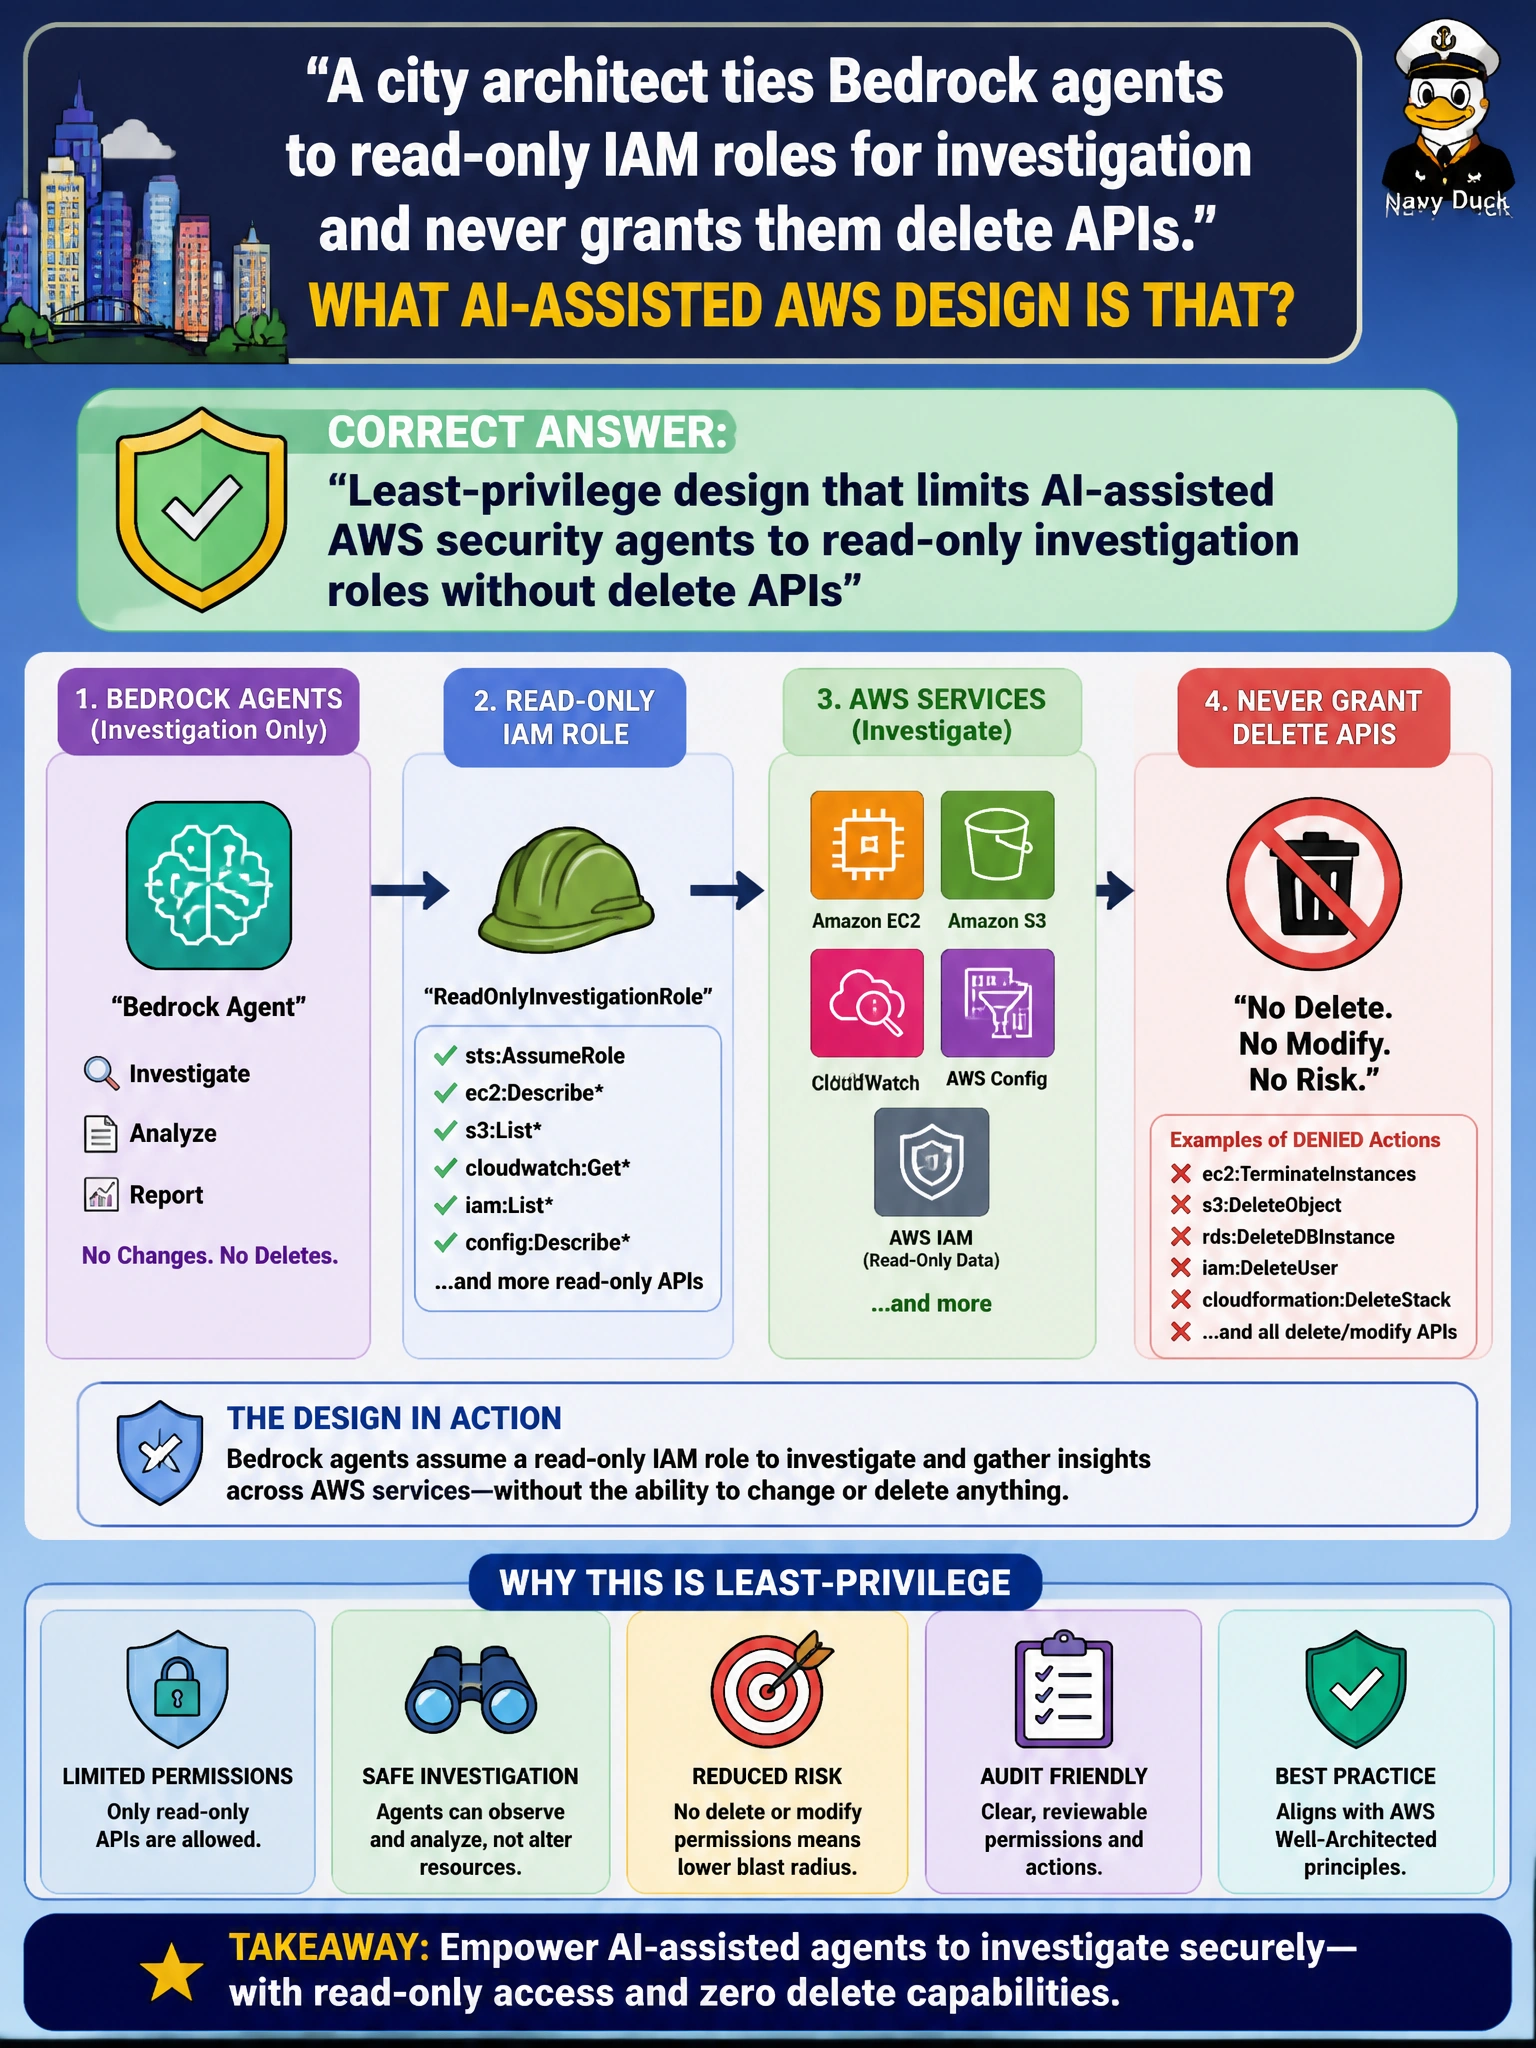
A city architect ties Bedrock agents to read-only IAM roles for investigation and never grants them delete APIs. What AI-assisted AWS design is that?
Select an answer to reveal the explanation.
Short Explanation
Investigation agents get reading glasses, not a wrecking ball—read-only IAM, no delete APIs. You'll be too narrow with just read-only GuardDuty findings, read-only CloudTrail Lake queries, or read-only session roles — you won't have the broad investigation roles this question's testing. Least privilege still wins.
Full Explanation
Least-privilege design that limits AI-assisted AWS security agents to read-only investigation roles without delete APIs constrains Bedrock-class agents to observation and analysis—listing, describing, and querying—while denying destructive actions such as object delete or instance terminate. City architects separate investigation identities from remediation identities so generative agents cannot become an accidental wrecking ball across municipal accounts. Read-only investigation roles still accelerate triage; destructive change remains behind stronger human-gated automation or break-glass processes.
Detective control design that limits AI-assisted AWS security agents to read-only GuardDuty findings without delete APIs fails by concept because it scopes read-only to a single detective signal rather than the least-privilege IAM boundary; it does not establish broad read-only investigation roles. Centralized logging design that limits AI-assisted AWS security agents to read-only CloudTrail Lake queries without delete APIs fails because it scopes read-only to a single logging source for historical context rather than broad investigation roles; it does not establish the least-privilege IAM boundary. Temporary elevation design that limits AI-assisted AWS security agents to read-only session roles without delete APIs fails because it describes a temporary session mechanism rather than persistent least-privilege investigation roles; temporary elevation is for short-lived access patterns, not the steady-state read-only IAM boundary tested here.
Exam caveat: AI-assisted investigation agents should use read-only IAM without delete APIs. Read-only GuardDuty findings only, read-only CloudTrail Lake queries only, and read-only session roles via temporary elevation are not the least-privilege IAM boundary tested here on GASAE-style AWS AI design questions.
Operational check for a city cloud architect: attach a managed or custom read-only investigation policy to the Bedrock agent role, explicitly deny delete and terminate actions, run an investigation scenario confirming describe/list/query succeed and delete/terminate fail, and ensure agents never reuse long-lived human console sessions for municipal AWS access.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.