
A housing authority revokes suspicious IAM access keys through automation when GuardDuty flags them. What AWS IR action is that?
Select an answer to reveal the explanation.
Short Explanation
When GuardDuty waves a red flag on an IAM key, you should yank it—merely enabling GuardDuty for civic workload visibility won't revoke anything. Rotating your long-lived IAM keys on a fixed schedule with Secrets Manager won't revoke the flagged key either; that's hygiene, not response. Isolating EC2 workloads with security groups doesn't touch IAM credentials, so revoke the key fast.
Full Explanation
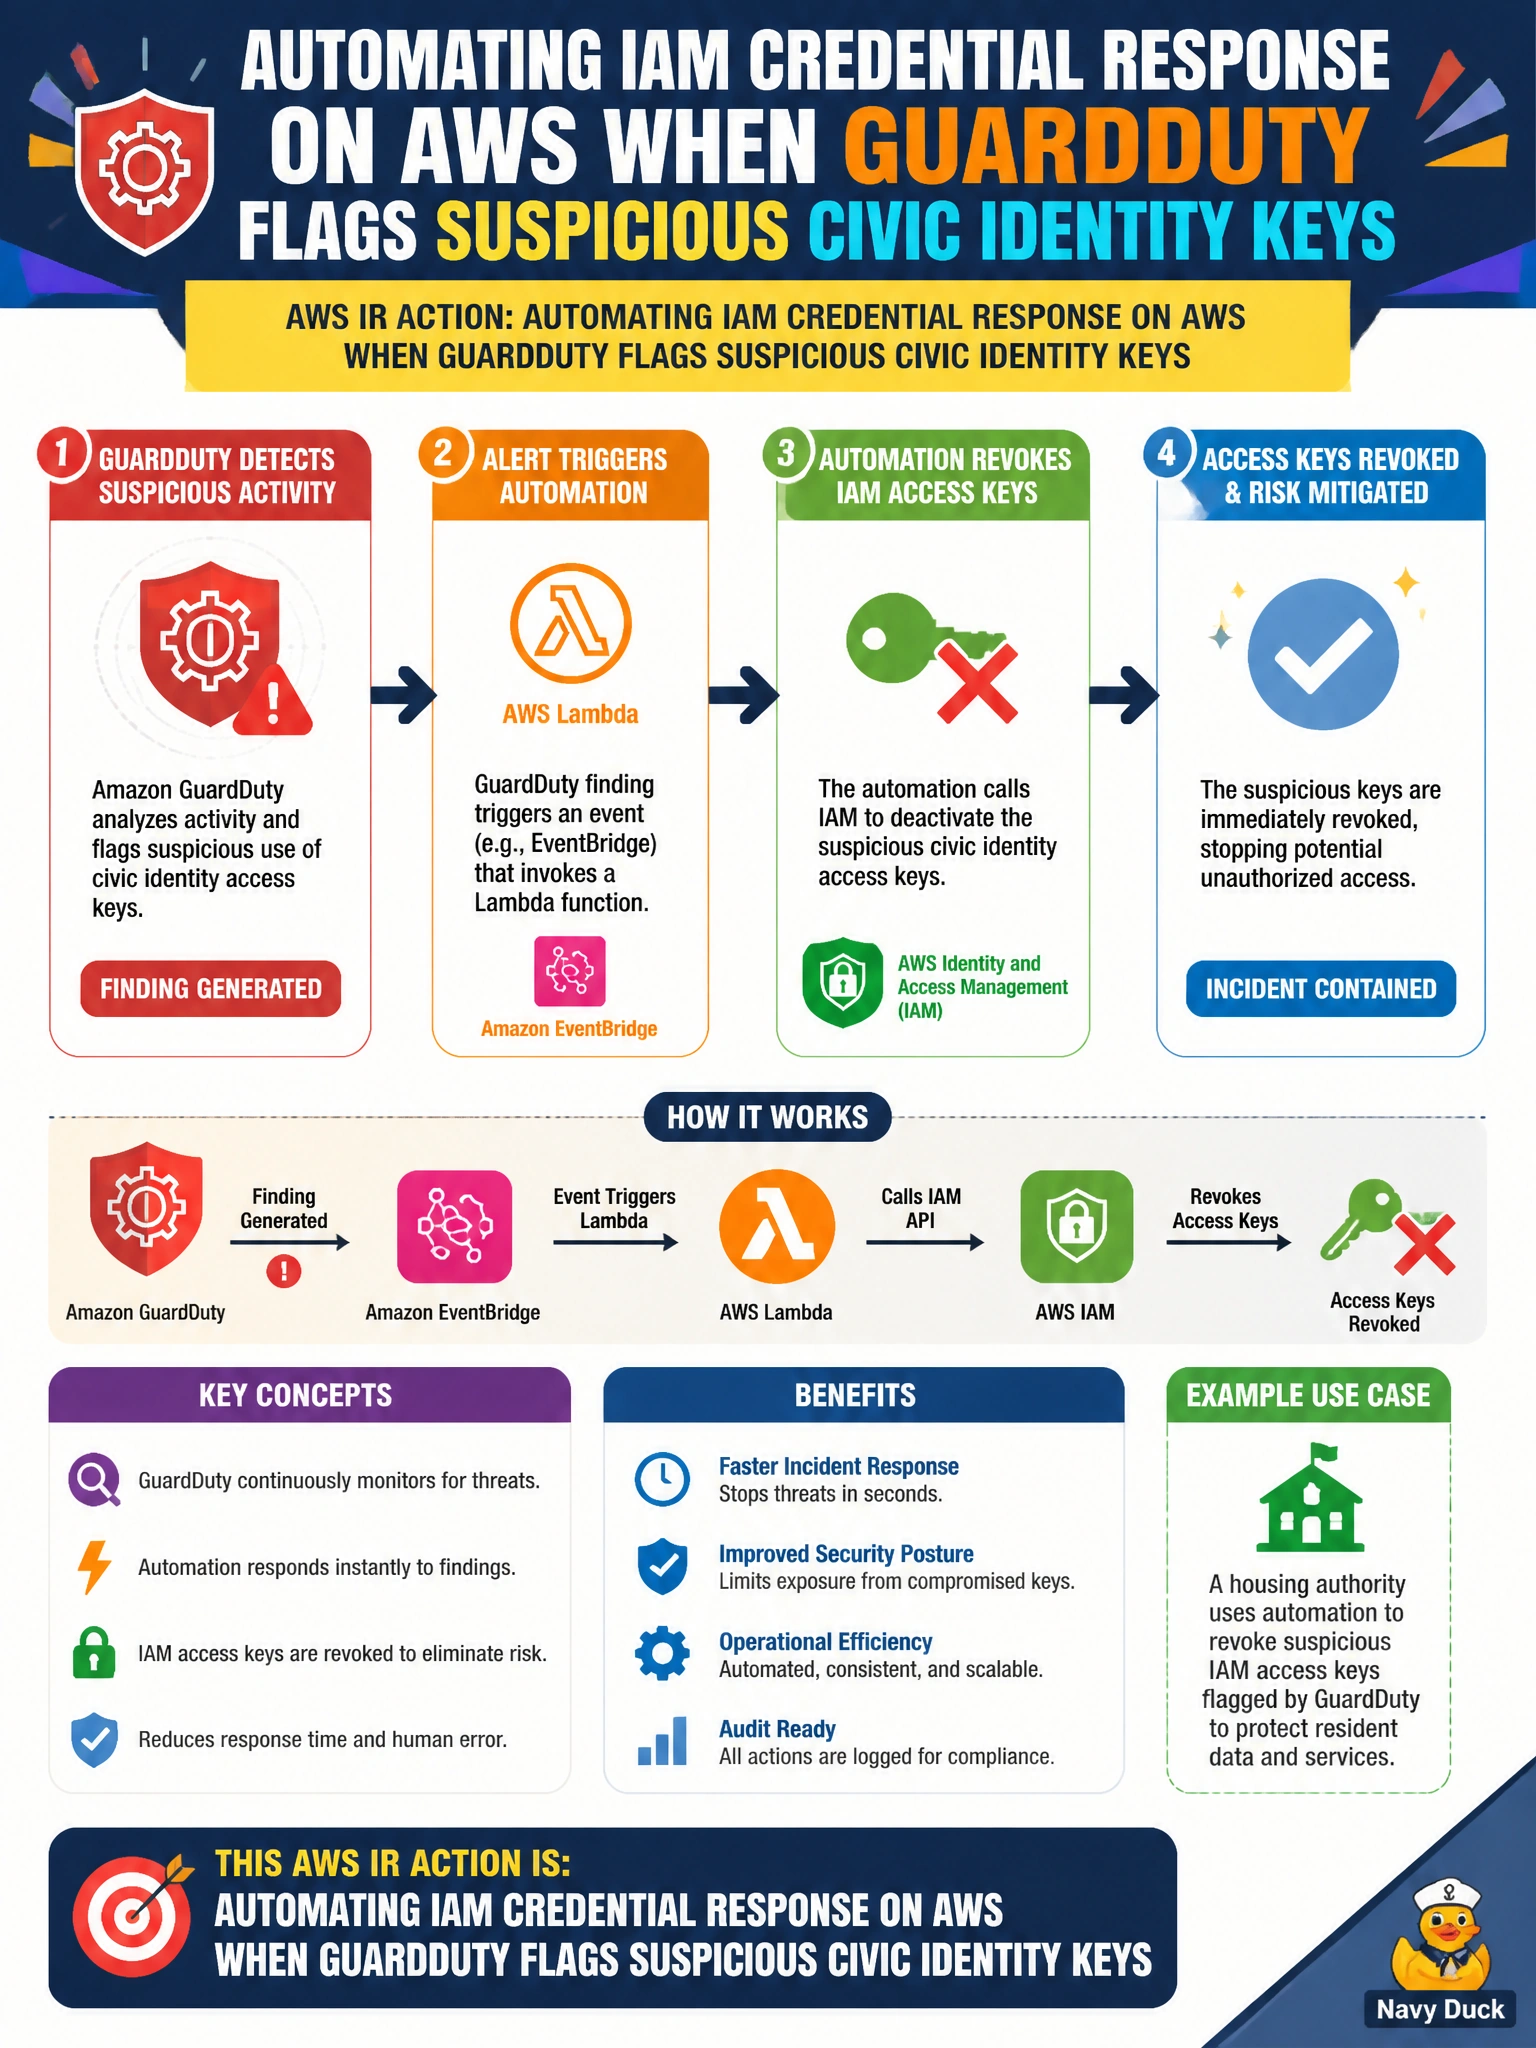
Automating IAM credential response on AWS when GuardDuty flags suspicious civic identity keys lets a housing authority revoke or disable compromised access keys quickly, limiting abuse of identities that may reach housing applications and citizen data stores. GuardDuty IAM findings become the trigger; automation performs the credential containment step and opens or updates IR tickets so humans can continue investigation. Speed matters because long-lived keys flagged as suspicious remain a live risk until revoked.
Enabling GuardDuty threat detection for civic workloads for improved visibility into IAM activity fails by concept because visibility alone does not contain or revoke the flagged credentials; it only observes them while abuse against municipal housing systems continues. Rotating long-lived IAM access keys on a fixed schedule using Secrets Manager for operational hygiene fails because scheduled rotation is not incident response; it does not act on the specific GuardDuty finding or immediately revoke the already-flagged key, leaving it live until the next scheduled cycle. Isolating flagged EC2 workloads with automated Security Group changes upon GuardDuty network findings fails because the scenario concerns IAM access keys, not EC2 network workloads; security group isolation does not revoke or disable the compromised IAM credentials.
Exam caveat: Automated revocation of GuardDuty-flagged IAM keys is the expected AWS IR credential response. Do not confuse visibility or scheduled rotation with credential containment, and do not accept EC2 network isolation as a substitute for revoking IAM keys.
Operational check for a housing authority cloud team: simulate or use a test finding for a non-production access key, confirm automation disables or deletes the key and records a ticket, verify that GuardDuty visibility alone is not treated as the production response path, and ensure GuardDuty IAM finding types remain enabled for civic accounts.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.