
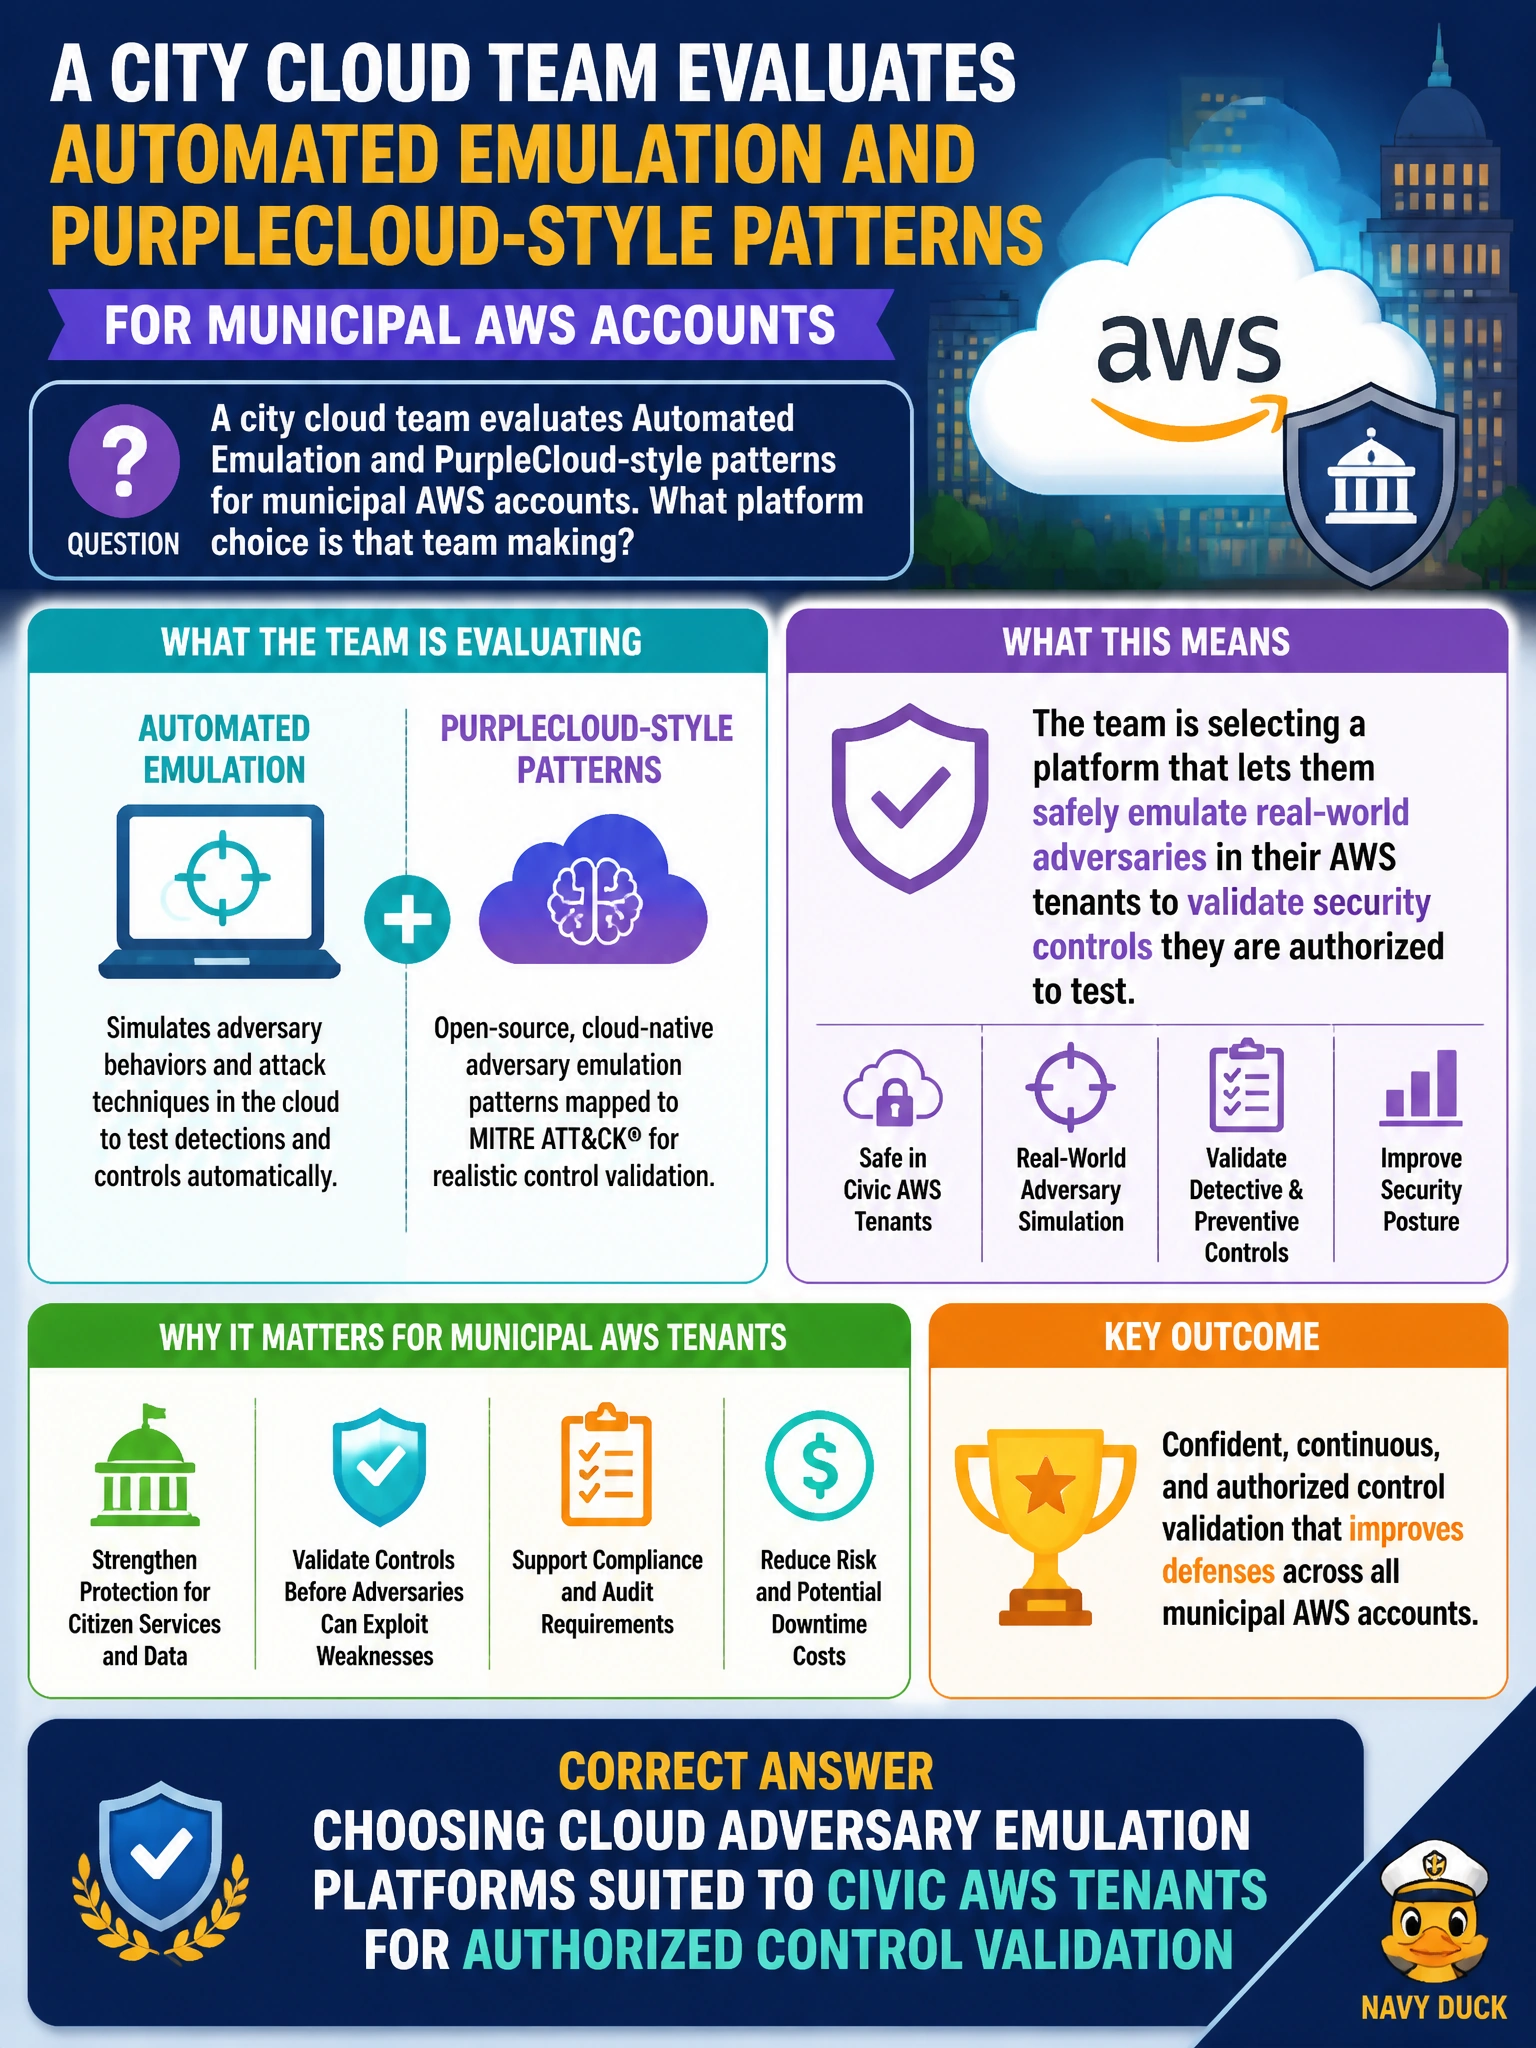
A city cloud team evaluates Automated Emulation and PurpleCloud-style patterns for municipal AWS accounts. What platform choice is that team making?
Select an answer to reveal the explanation.
Short Explanation
Think of picking a gym that already has city-account memberships—you'll want cloud emulation platforms that speak AWS, not vulnerability scanning services with emulation playbooks for civic AWS tenants just for authorized reporting. It's about authorized control validation, so reviewing emulation insights on a dashboard or discussing emulation scenarios in a workshop won't validate controls for you. Match the platform to the municipal cloud you actually run.
Full Explanation
Selecting cloud adversary emulation platforms suited to civic AWS tenants is the right platform choice because municipal cloud control validation must run inside the same account, identity, and network model the city actually operates. Automated Emulation and PurpleCloud-style patterns are designed for authorized purple-team work against cloud control planes, IAM paths, and internet-facing services without forcing the team to invent one-off attack infrastructure for every exercise. That alignment lets the city prove detections and preventions where citizen services live, under change windows and scopes the CISO already approved. Selecting vulnerability scanning services with emulation playbooks for civic AWS tenants for authorized reporting fails by concept: adding playbooks to a scanner still produces vulnerability findings for reporting, but it does not provide an adversary emulation platform that executes authorized techniques against AWS tenant controls, managed identities, and cloud-native detections. Adopting posture dashboards with emulation insights for civic AWS tenants for authorized control review fails by concept for the same reason: reviewing insights on a dashboard is not the same as validating controls; authorized emulation proves detections and preventions with reversible, non-destructive scenarios against accounts and environments scoped for testing. Coordinating tabletop workshops using emulation scenarios for civic AWS tenants for authorized control discussion fails by concept because discussing scenarios improves procedural discussion rather than matching the purple-team platform to the municipal AWS tenant model the team is actually choosing between; tabletop discussion is not the platform decision the stem describes. Exam caveat: cloud emulation platforms are not a license for unrestricted red activity; scope, authorization, and non-production-first staging still govern what may run. Operational check: confirm the chosen platform can authenticate into approved municipal AWS accounts, map techniques to GuardDuty/CloudTrail/Security Hub signals, and support abort and evidence export before any citizen-facing VPC is touched.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.