
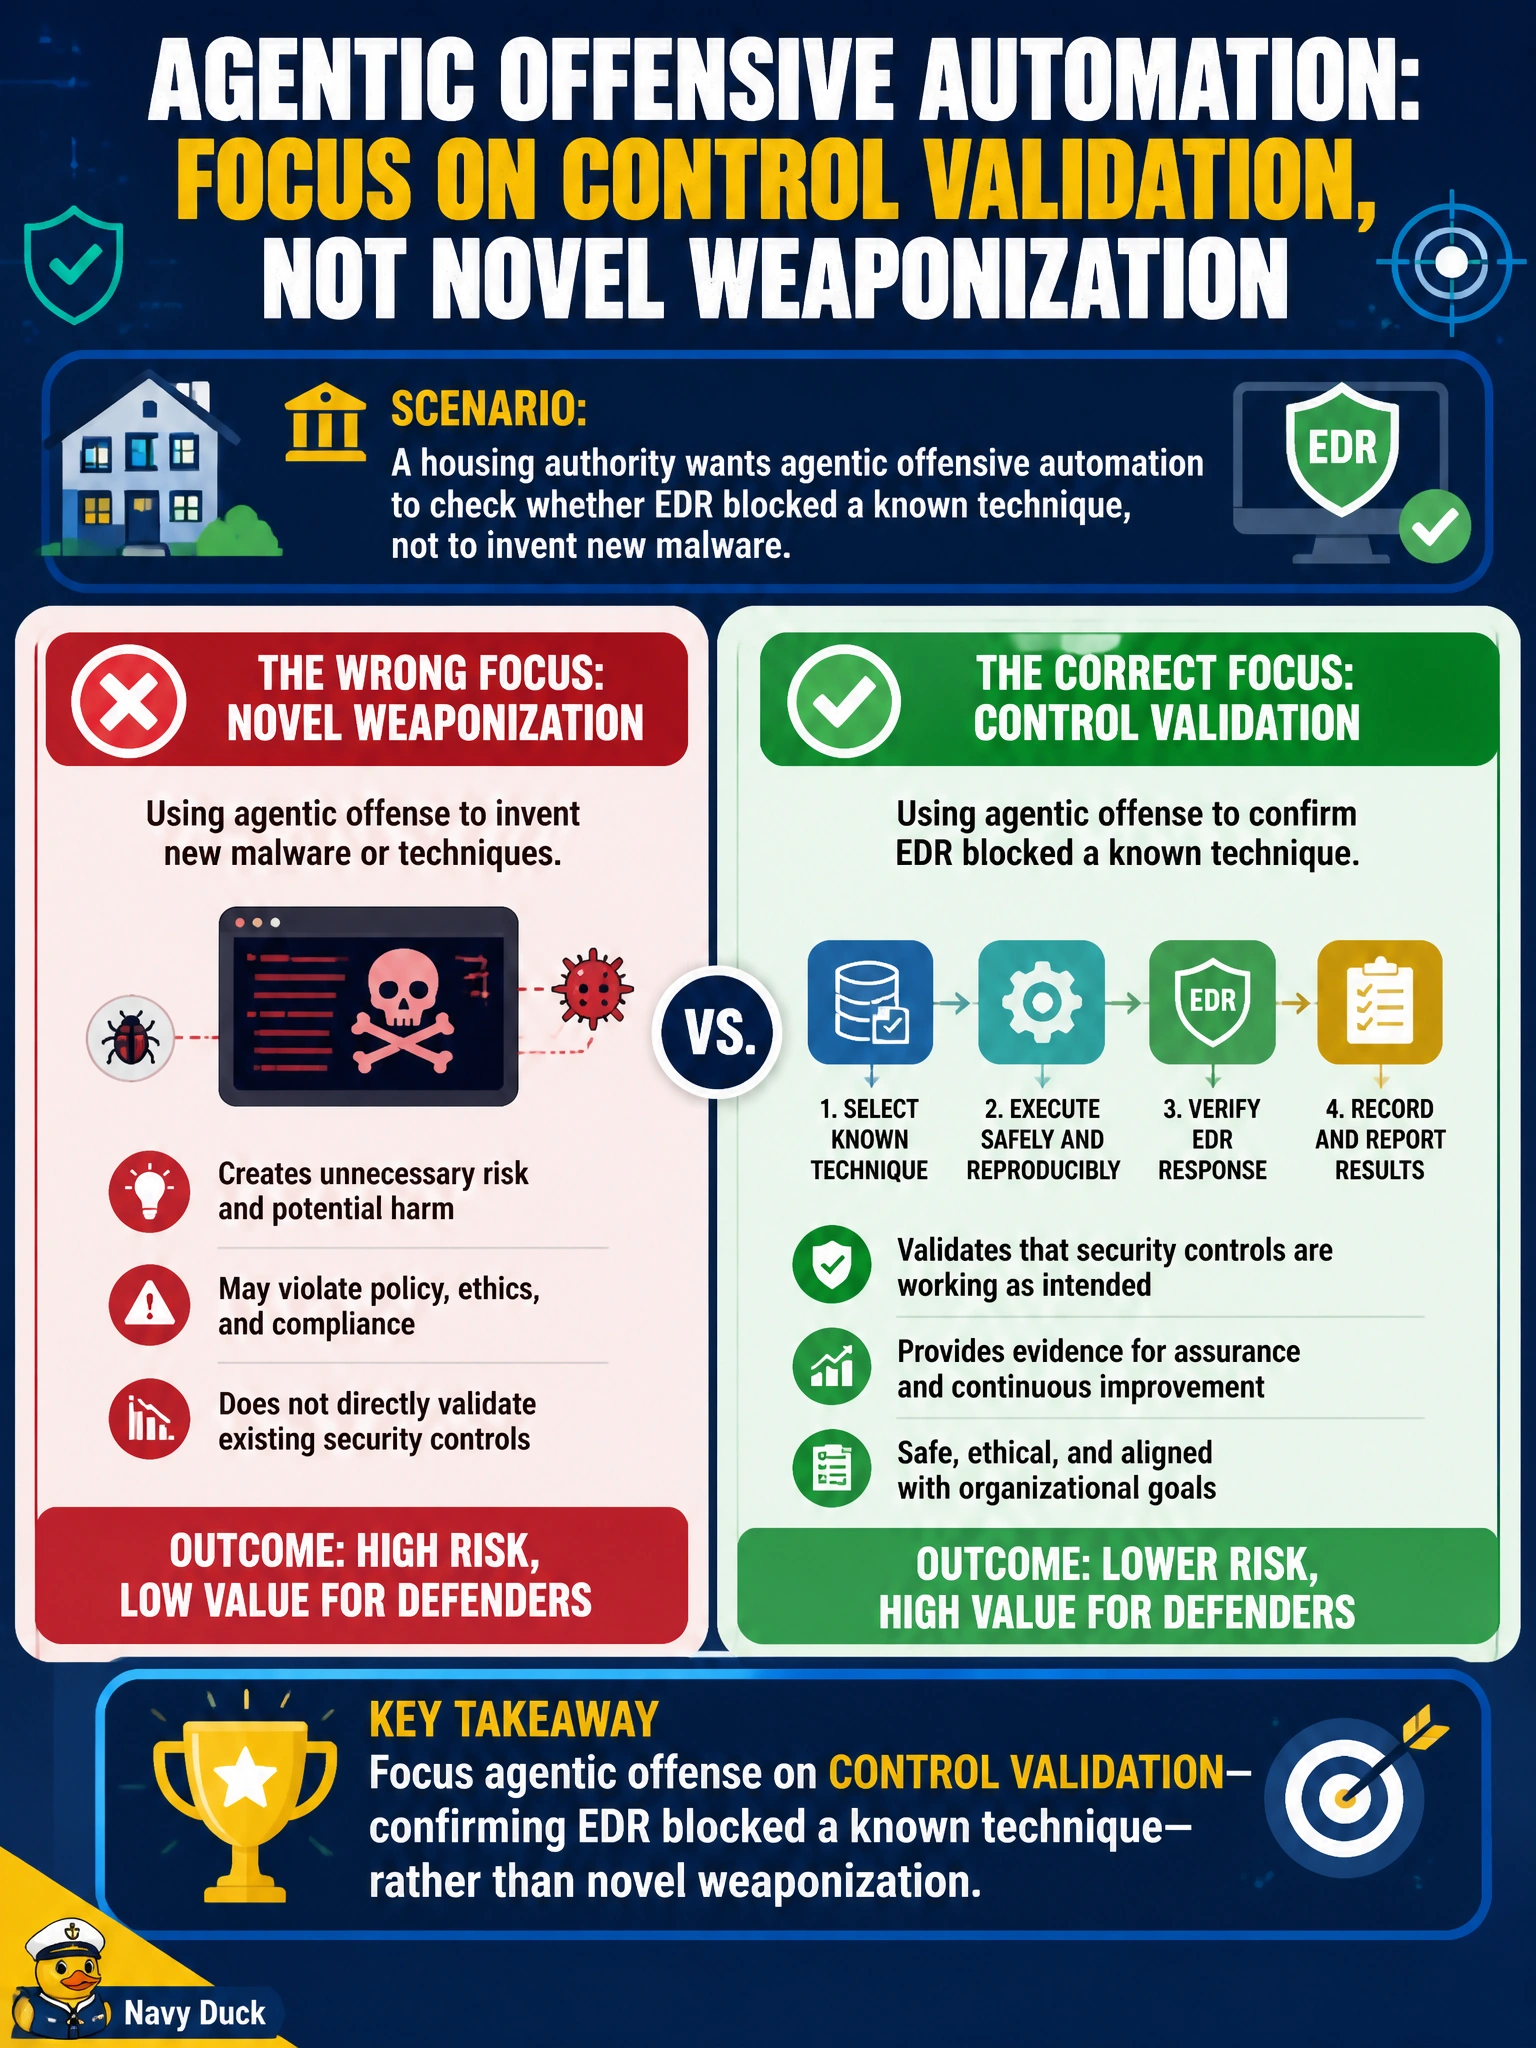
A housing authority wants agentic offensive automation to check whether EDR blocked a known technique, not to invent new malware. What focus is correct?
Select an answer to reveal the explanation.
Short Explanation
You're checking whether EDR blocked the known move, not just whether it logged it. This is control validation, like making sure the lock still catches. You'll miss the point if you're settling for the EICAR test file or a simulation when it's proof the EDR actually blocked that known technique you need.
Full Explanation
Housing authorities that want agentic offensive automation to check whether EDR blocked a known technique—not invent new malware—are correctly focusing on control validation. Purple-team value in municipal environments comes from proving detections and preventions work against known ATT&CK-relevant behaviors, then remediating gaps. Novel weaponization shifts the program toward malware authoring, which is rarely the authorized civic objective and raises stewardship and legal risk.
The correct focus works because success is defined as measurable defensive outcomes: block, detect, alert, or miss—with telemetry. Known techniques provide repeatable baselines for EDR efficacy over time.
Focusing agentic offense on control validation—confirming EDR logged a known technique—rather than novel weaponization fails as the wrong outcome: a log proves detection telemetry only, not that EDR actually blocked execution as the housing authority asked to confirm.
Focusing agentic offense on control validation—confirming EDR blocked an EICAR file—rather than novel weaponization fails as the wrong artifact: blocking the benign EICAR test string proves basic antimalware function only, not that EDR blocked the specific known technique the housing authority asked to confirm.
Focusing agentic offense on control validation—confirming EDR simulated a known technique—rather than novel weaponization fails as the wrong method: a simulation models the technique without live execution, so it does not prove the EDR actually blocked the known technique as the housing authority requested.
Exam caveat: Agentic offense in civic purple teams ≈ control validation of known techniques, not novel malware factories.
Operational check: Codify test cases as known technique IDs, keep EDR on, score block/detect results in the SIEM, and prohibit public publication of new exploit variants from the automation program.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.