
A city CISO requires an AI SBOM listing models, embeddings, frameworks, and tool plugins for the civic GenAI platform. What does that inventory primarily enable?
Select an answer to reveal the explanation.
Short Explanation
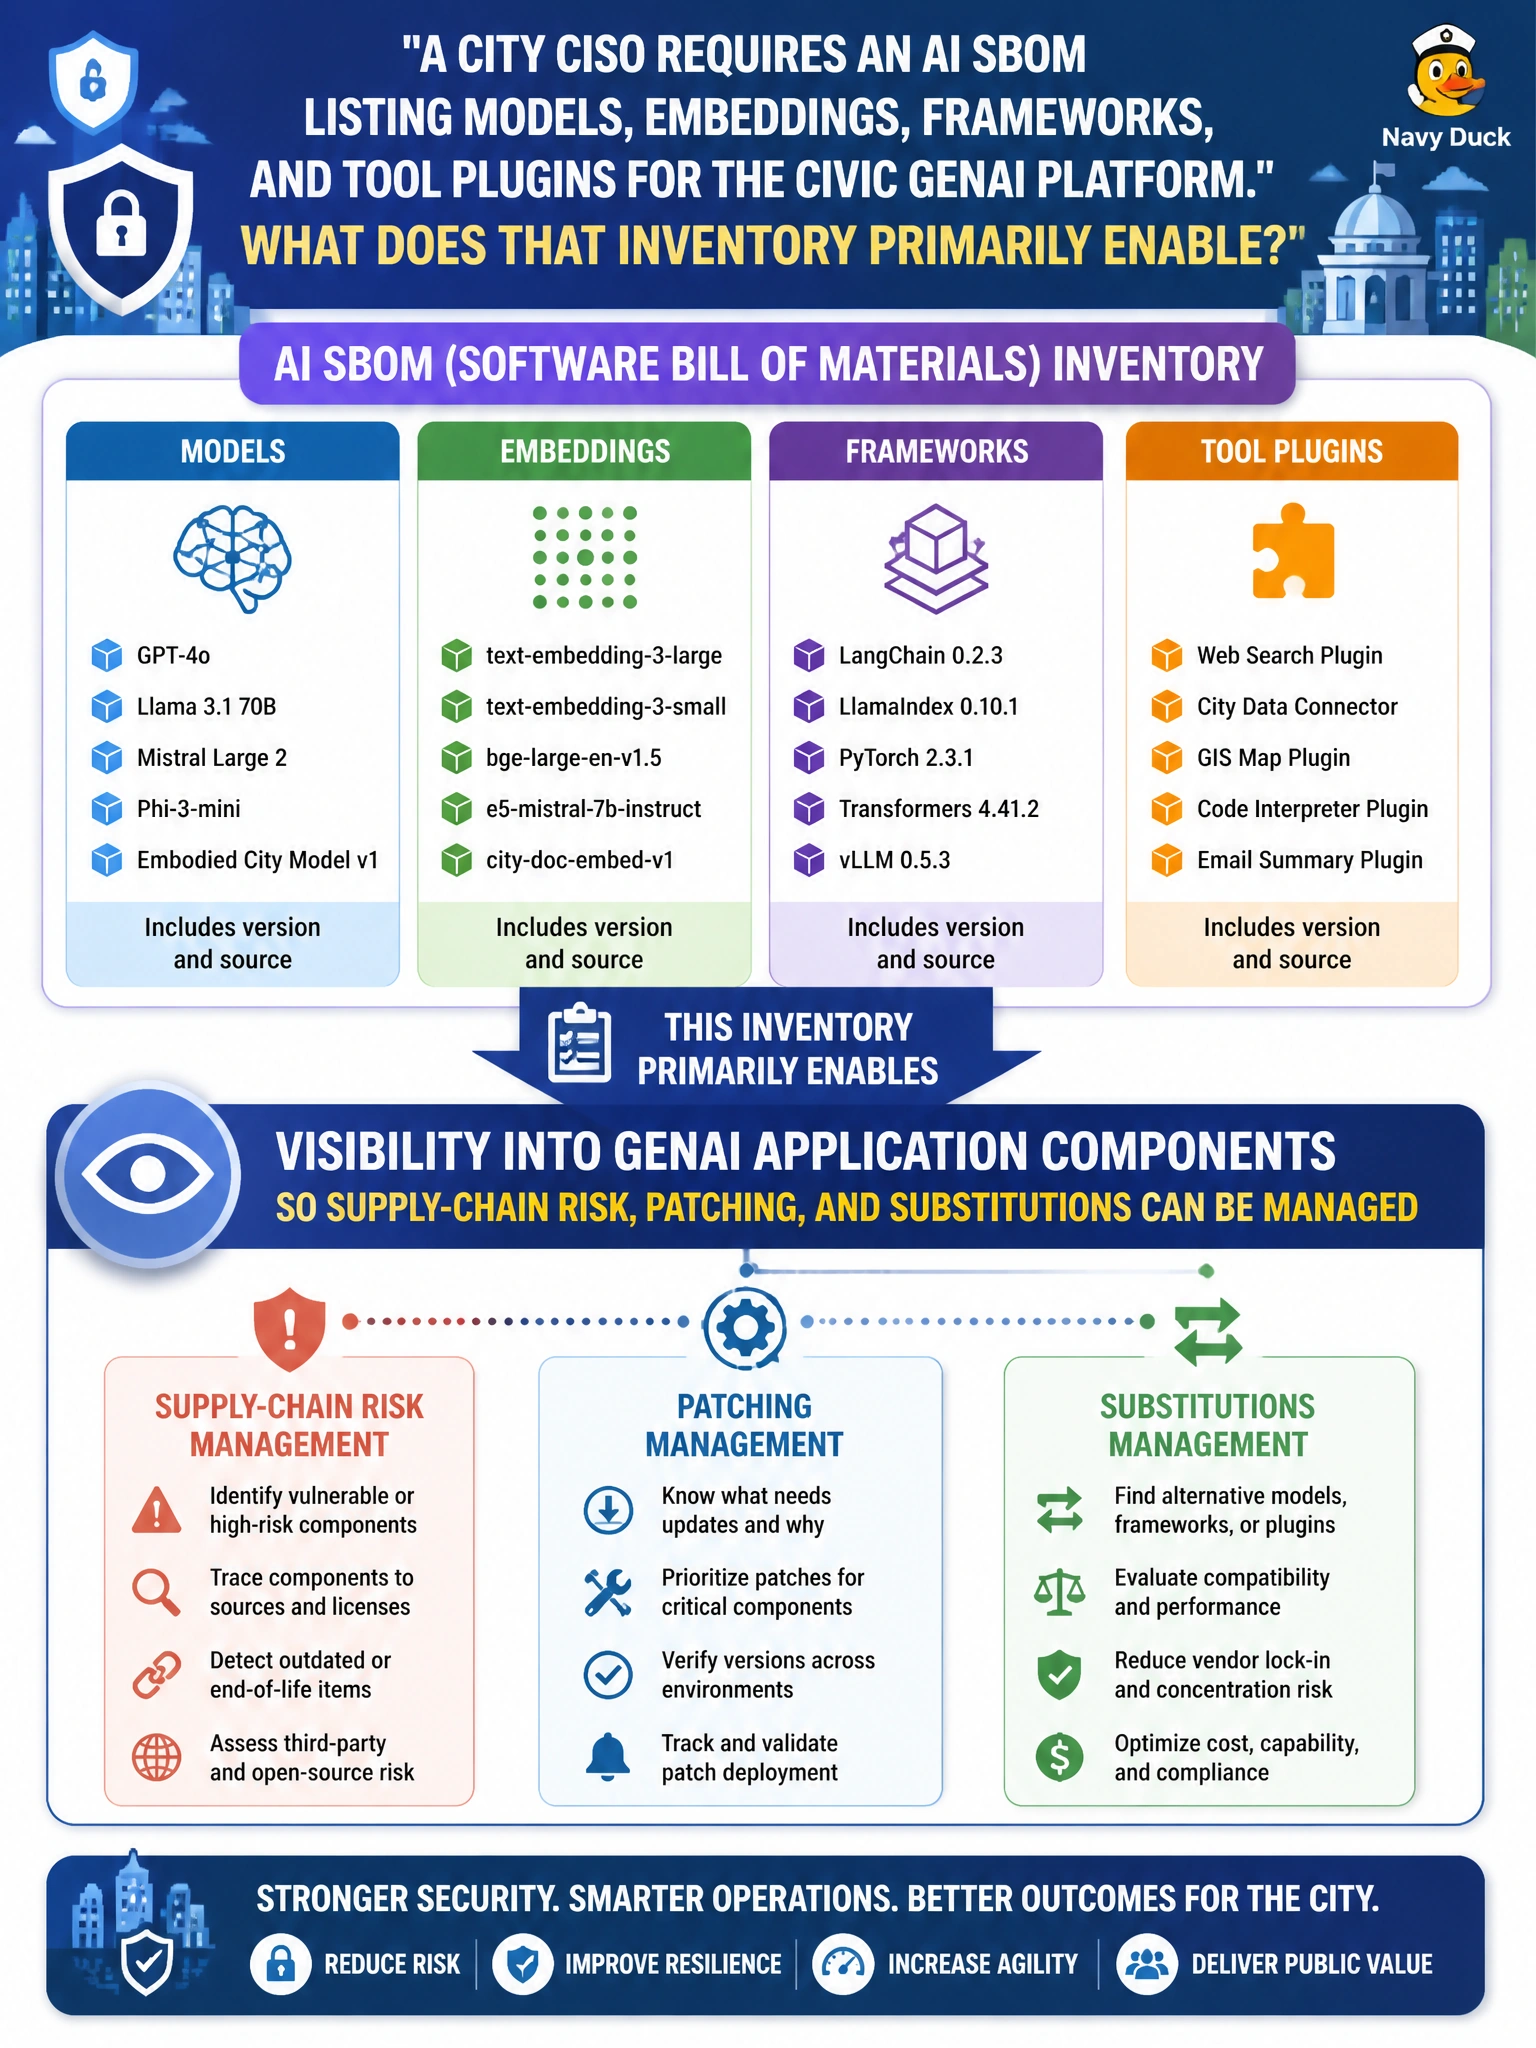
An AI SBOM is the packing list for your city’s GenAI stack — models, embeddings, frameworks, plugins. You cannot patch or replace what you cannot name. The list enables management; it is not a free pass to skip scanning or diligence.
Full Explanation
A software bill of materials tailored to GenAI applications inventories models, embedding components, frameworks, and tool plugins that traditional SBOMs may miss. For a civic GenAI platform, that inventory primarily enables visibility so supply-chain risk, patching, substitutions, and license obligations can be managed deliberately by the CISO and platform owners. The AI SBOM is a living management instrument, not a one-time spreadsheet ritual that excuses further diligence.
Automatic deletion of all resident conversations after one minute is a retention control, not what an SBOM enables. Exemption from vulnerability scanning for listed packages inverts the purpose of inventory—listed components still need scanning and patching. Permission to skip vendor due diligence once the spreadsheet exists confuses inventory with assurance; listing a component documents it but does not approve it for municipal use.
Exam caveat: AI SBOMs must stay current as models, embeddings, and plugins change; a stale inventory creates false confidence during incidents and audits. Operational check: maintain an AI SBOM for the civic platform covering models, embeddings, frameworks, and plugins; map owners and patch SLAs; feed the inventory into vulnerability and substitution reviews; and update it on each material change.