
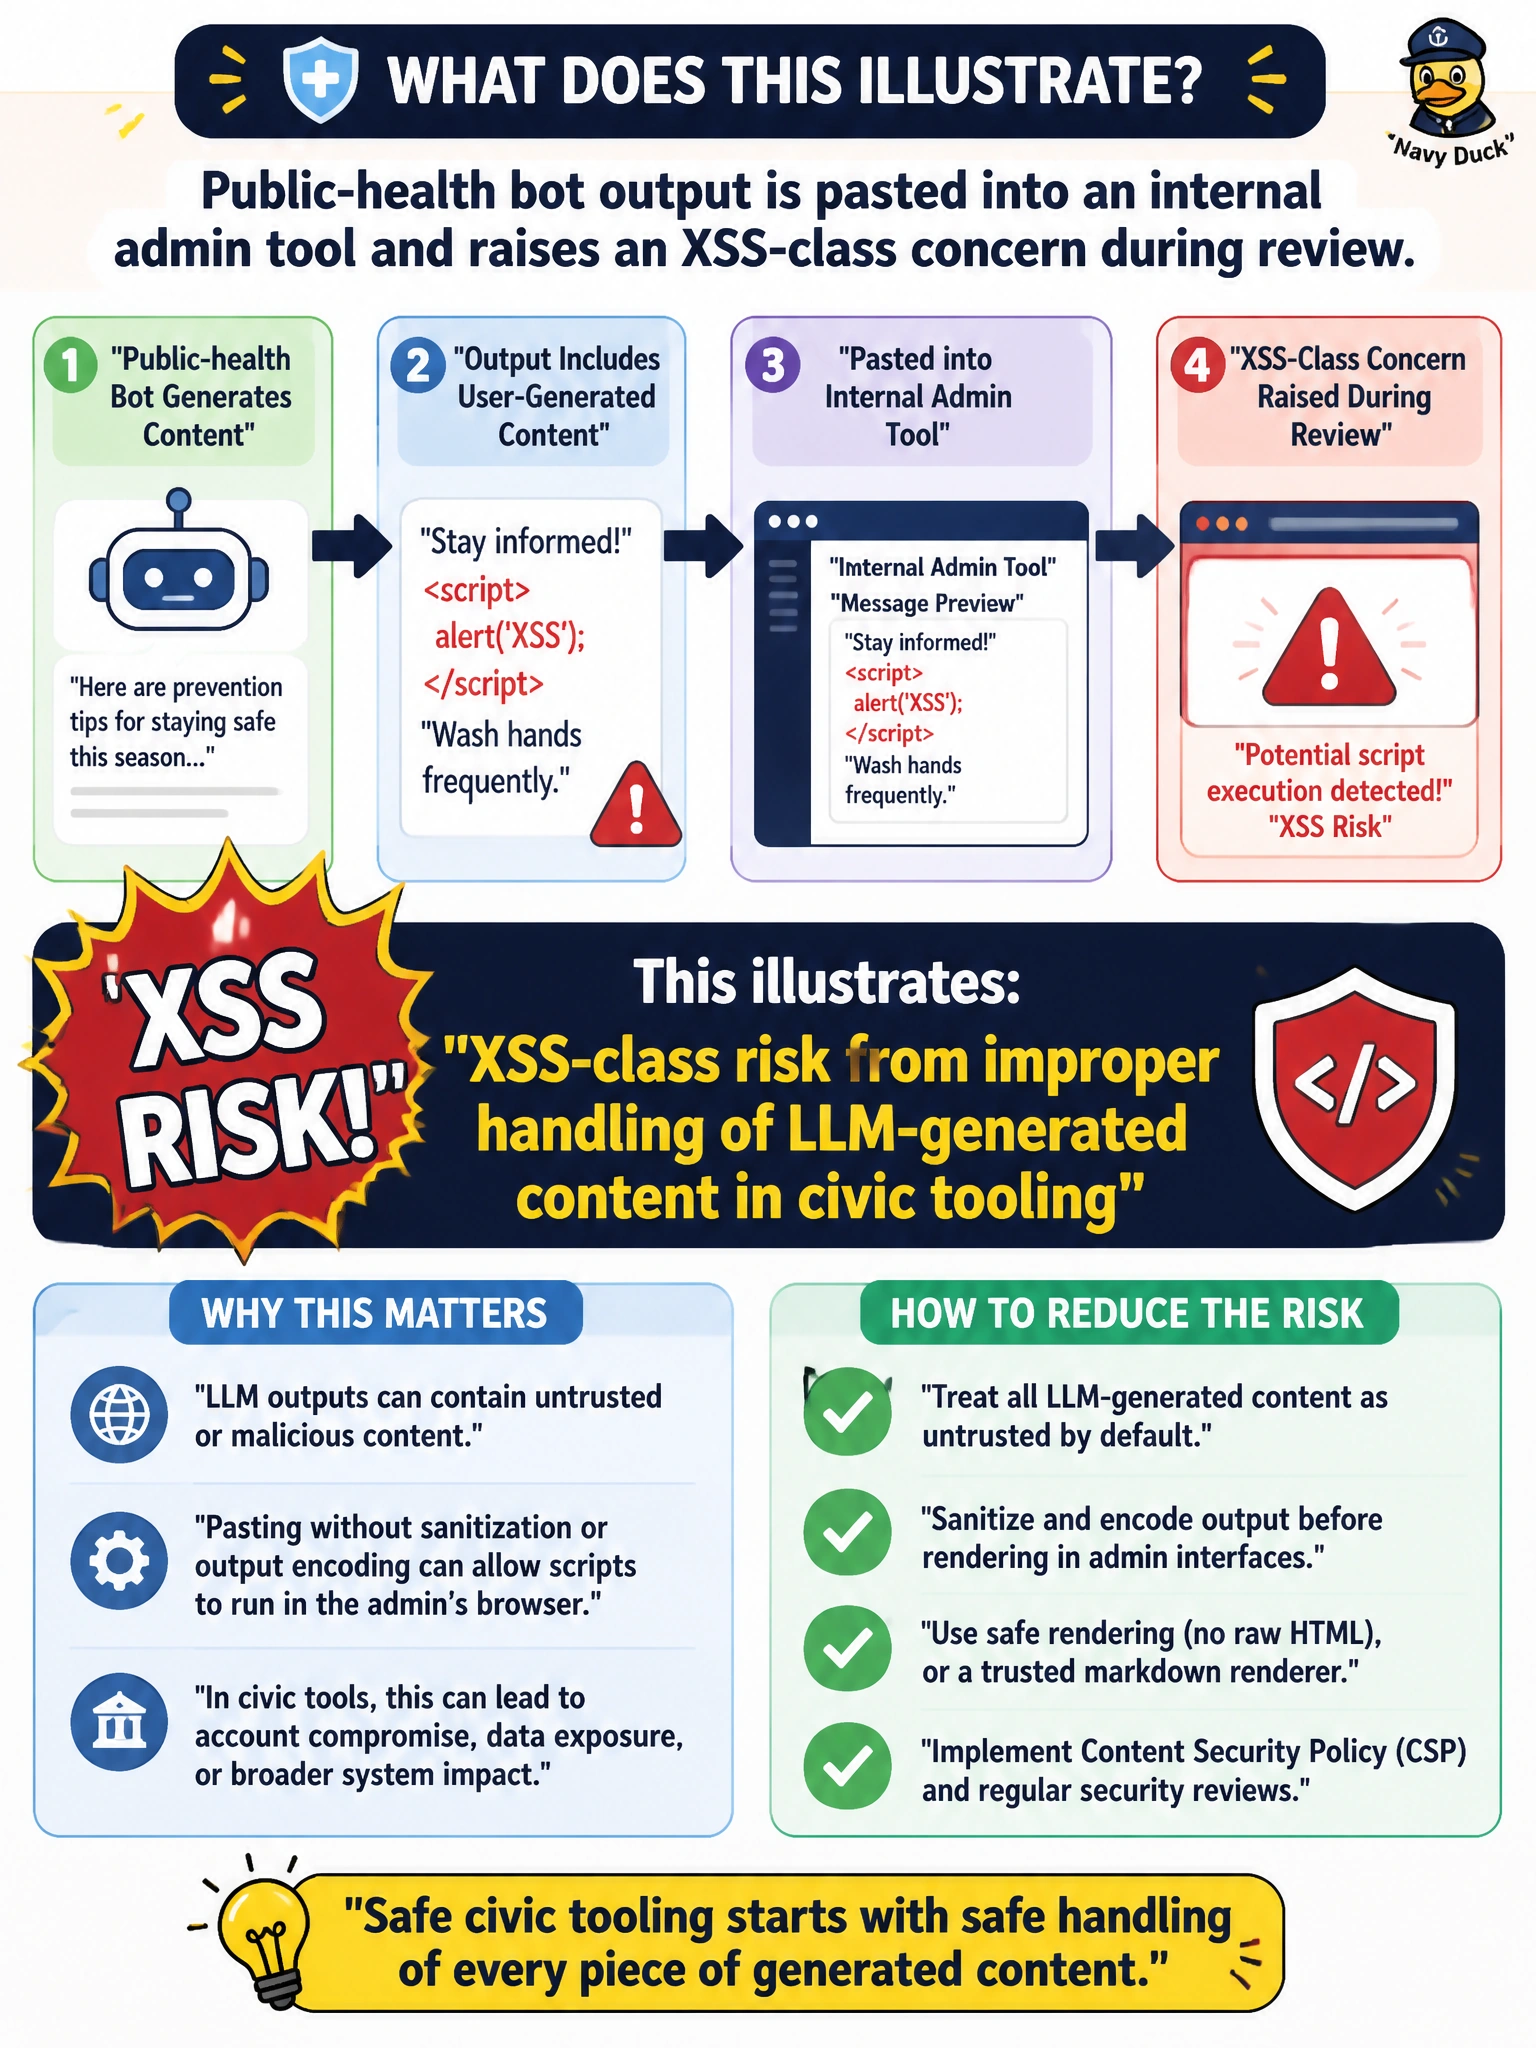
Public-health bot output is pasted into an internal admin tool and raises an XSS-class concern during review. What does this illustrate?
Select an answer to reveal the explanation.
Short Explanation
Copy-paste from a bot into an admin screen can turn model text into a script problem—XSS-class risk from sloppy output handling. Escaping input before inference, tuning CSP for public pages, and logging answers aren't the finding here.
Full Explanation
Public-health bot output pasted into an internal admin tool that raises an XSS-class concern illustrates XSS-class risk from improper handling of LLM-generated content in civic tooling. Even if the original chat UI was safer, downstream tools that interpret model text as markup inherit active-content risk and can expose staff sessions or administrative actions. Correct illustration ties generative output to classic web injection classes inside municipal admin workflows, driving sanitization wherever LLM text is consumed or copied. Focusing on HTML escaping applied to citizen input before public-health model inference processing addresses a different pipeline stage—input sanitization before inference—not the markup-rendering issue created when LLM text is pasted into a screen that interprets it as active content. Tuning Content Security Policy for cached public guidance pages on the portal is a separate control for cached public pages and misses the point: the XSS-class risk here comes from how the internal admin tool renders pasted LLM text, not from CSP on public guidance pages. Relying on conversation logging for public-health bot answers to support quality review addresses auditability, not the active-content risk: the XSS-class concern comes from how downstream tooling renders model text, not from whether answers are logged. Exam caveat: treat this as a risk category and control gap in content handling across the full staff workflow; assessments should not distribute working XSS payloads against production public-health systems. Operational check: inventory admin screens that accept pasted bot output, enforce encoding and sanitization on those inputs, add automated checks for script patterns in LLM text pipelines, train staff not to paste raw HTML from assistants into privileged consoles, and retest public-health assistant outputs through the same admin paste paths used by clinicians and clerks.